ExfilSquad Targets New Victims, Shares Data via Torrents
Extortion group ExfilSquad lists 13 new US, UK and Swedish victims and now distributes stolen data via peer-to-peer torrents.
ExfilSquad, a data-theft extortion collective that emerged in mid-2026, announced 13 new victims in the US, UK and Sweden with an August 5, 2026 negotiation deadline. The group skips ransomware, instead stealing data and threatening publication on a dark web leak site. Resecurity says its TTPs center on exploiting misconfigured Microsoft Dataverse, Power Pages, case management and CRM portals. The group now distributes stolen data through per-victim torrent trackers and web seeds, making leaks hard to contain.
- Extortion without ransomware: ExfilSquad steals data, threatens publication, and set an August 5, 2026 negotiation deadline.
- TTPs include exploiting misconfigured Microsoft Dataverse, Power Pages, case management and CRM portals for large-scale theft.
- Each victim gets a unique torrent tracker and web seed, spreading stolen data across P2P networks.
- Active torrent seed hosts in China and Russia suggest prior knowledge or deliberate involvement in distribution.
- Previously breached the UK Police National Legal Database, exposing contacts of over 100,000 officers and justice professionals.
Full article479 words · extracted from securityaffairs.com · click to collapse

ExfilSquad targets 13 organizations, exploiting cloud portals for data theft and using torrents to spread stolen information and amplify damage.
Resecurity is tracking the activity of ExfilSquad – the group announced new victims this week. ExfilSquad is a new cybercrime group that emerged in mid-2026. Instead of using ransomware, it steals data and threatens to publish it on a dark web leak site unless victims pay a ransom.
The list includes 13 organizations from the U.S., the UK, and Sweden. Notably, in July, the group also targeted a major financial institution in Nigeria.
“ExfilSquad announced new victims this week and set a firm deadline – August 5, 2026 – to complete all required negotiations. Otherwise, the stolen data will be released. This time, the list of victims includes 13 organizations from the U.S., the UK, and Sweden.” reads the report published by Resecurity. “Notably, in July, the group was also targeting a major financial institution in Nigeria.”
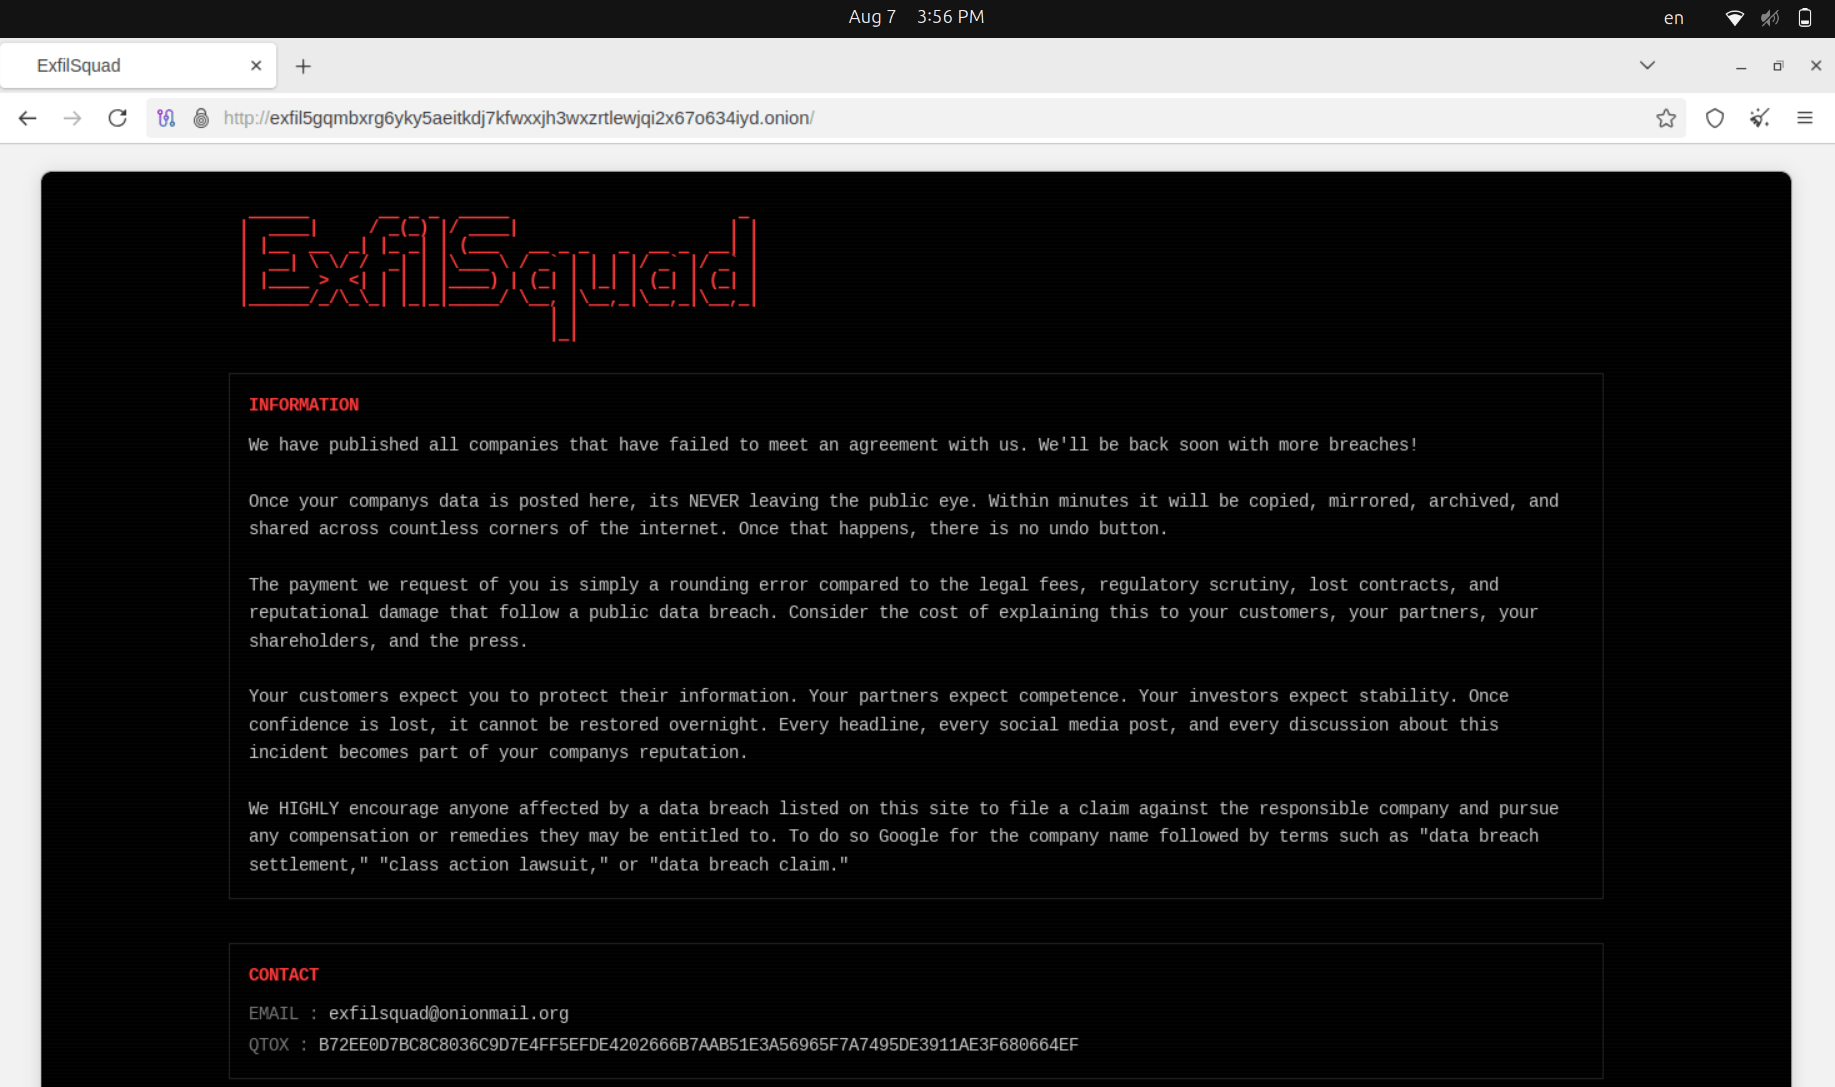
Their TTPs revolve around exploiting cloud/SaaS portals for large-scale data theft, including misconfigured Microsoft Dataverse, Power Pages sites, Case Management and Customer Relationship Management Systems (CRMs).
The collective attracted significant attention after the cyberattack on the U.K.’s Police National Legal Database (PNLD), which compromised contact data of more than 100,000 police officers and criminal justice professionals.
ExfilSquad is leveraging P2P networks to distribute stolen data by using torrent files. Such an approach has already been used by LockBit 3.0 and Cl0p ransomware. Each victim is assigned a unique torrent tracker and an initial web seed, which is a notable tactic employed by the hacking collective.
Resecurity views this tactic as a trend leveraged by sophisticated adversaries involved in ‘hack-and-leak’ operations. By using torrents, the leaked data is easily accessible to a broader audience, including other malicious actors. Due to the decentralized nature of P2P, it is complicated to prevent further data circulating. This amplifies the reputational and financial damage to victim organizations in times, as the data becomes widely available and impossible to remove.
“Once stolen data has been released, it is not possible to stop its sharing via the P2P network or remove the torrent file, because other participants involved in seeding can easily resume downloads. Resecurity views this tactic as a trend leveraged by multiple sophisticated actors involved in hack-and-leak operations.” concludes the report. “Resecurity analyzed the nodes involved in torrent sharing, as well as seeds that participated in the circulation of stolen data. Interestingly, hosts from China and Russia were among the most active during August 7, 2026, which may suggest that the operators behind them had prior knowledge of the data publication or were involved in its distribution at a later stage once it became available. In any case, such hosts indicate an interest in this type of data.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, ExfilSquad)
Text extracted automatically; images, tables and formatting may be missing. Original: https://securityaffairs.com/197025/security/exfilsquad-targets-new-victims-shares-data-via-torrents.html