More than half of public vulnerabilities bypass leading WAFs
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2025-55182 | Unauthenticated RCE in React Server Components (React2Shell) CVE-2025-55182 is a critical (CVSS 10.0) pre-authentication remote code execution flaw (CWE-502, deserialization of untrusted data) in React Server Components, specifically the react-server-dom-parcel, react-server-dom-turbopack, and react-server-dom-webpack packages in versions 19.0.0, 19.1.0, 19.1.1, and 19.2.0. It is triggered when the vulnerable code unsafely deserializes payloads from HTTP requests sent to Server Function endpoints, requiring no authentication or user interaction. An attacker gains arbitrary code execution on the affected server (CVSS scope changed, with high impact to confidentiality, integrity, and availability), and reporting notes a campaign in which hackers used the flaw to breach 766 Next.js hosts and steal credentials. Any React/Next.js application exposing Server Functions with the affected React versions is in scope, which given the ubiquity of React and Next.js is a very large deployed base. Exploitation is confirmed in the wild: the flaw was added to CISA's Known Exploited Vulnerabilities catalog on 2025-12-05 with known ransomware use, EPSS puts the 30-day exploitation probability at 99.8%, multiple public PoC/scanner repositories are available, and coverage has dubbed the flaw React2Shell. Do: Upgrade the react-server-dom-webpack, react-server-dom-parcel, and react-server-dom-turbopack packages to the vendor-patched releases (any version later than the vulnerable 19.0.0, 19.1.0, 19.1.1, and 19.2.0 line) and update Next.js per Vercel's advisory; as a KEV entry, U.S. federal agencies must apply vendor mitigations per BOD 22-01 or discontinue use. Audit internet-exposed Server Function endpoints for the vulnerable React versions and review logs for exploitation activity, including the reported campaign that breached 766 Next.js hosts and stole credentials, then rotate any exposed credentials. | 10.0 | 100% | KEV ransomware PoC ×7 |
| mass≈1M+ internet-facing Next.js/React Server Components deployments (order-of-magnitude estimate) |
Full article467 words · extracted from helpnetsecurity.com · click to collapse
Miggo Security has released a new report that examines how web application firewalls are used across real-world security programs. The research outlines the role WAFs play as foundational infrastructure and evaluates their effectiveness against critical vulnerabilities, CVEs, and AI-driven threats.
The report also explores how the WAF’s edge placement, combined with runtime intelligence, can support a more reliable and AI-ready mitigation layer for modern defense strategies.
“This study clarifies that WAFs are currently an underutilized asset because the manual, generic signature model erodes trust. Security teams cannot afford the risk of false positives or waiting 41 days for vendors to test CVE-specific rule changes. We see massive untapped potential here: runtime augmentation provides the necessary intelligence and automation to finally transform the WAF into a reliable, high-confidence defense layer for all critical CVEs, not just reactive, one-off fixes,” said Andy Ellis, CISO at Duha.
The study comes on the heels of the discovery of “React2Shell” (CVE-2025-55182), a critical vulnerability in React and Next.js. This unfolding crisis serves as a stark, real-world validation of the study’s conclusion: the exposure window between exploit discovery and effective WAF protection is where the damage can happen.
“WAFs are necessary, but they cannot win the AI-enabled zero-day race alone,” asserts Daniel Shechter, CEO of Miggo Security. “The ‘React2Shell’ vulnerabilities are the textbook example of why the old model fails. We have a CVSS 10.0 threat where the exploit lives in the complex deserialization logic of the ‘Flight’ protocol – a place standard WAF signatures rarely look. The only way to close this 41-day gap is shifting from slow, generic signatures to fast, exploit-aware rules generated by runtime intelligence.”
Miggo’s study analyzed a representative set of more than 360 CVEs to evaluate WAF effectiveness across leading vendors. The curated dataset mirrors real-world attacker priorities, including the availability of exploit tooling, the prevalence of affected components, and the potential impact of exploitation, while also examining how AI augmentation can strengthen protection.
Key findings:
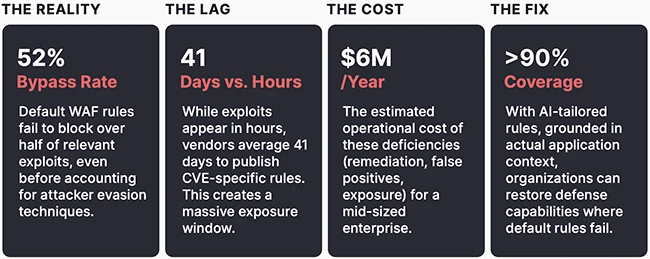
- Most publicly relevant vulnerabilities bypass leading WAFs: 52% of exploits bypass default rules even under favorable conditions. Real attacker payloads’ variability only pushes that number higher.
- AI-powered tailored rules push coverage above 91%: +91% of bypassed vulnerabilities can be mitigated when rules are tailored with AI for the actual vulnerability and application context instead of generic attack patterns.
- WAF rule releases are 41x slower than AI-native attackers: It takes 41 days on average for a CVE-specific WAF rule to be published by leading WAF vendors, while exploit code appears within hours. This mismatch defines the modern exposure window.
- $6 million in potential enterprise losses are estimated due to operational WAF deficiencies, annually for a mid-sized enterprise, because of the exposure window, unnecessary remediation costs, and false positives’ impact. An augmented approach can reduce these significant losses.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.helpnetsecurity.com/2025/12/18/miggo-research-waf-vulnerability-bypass/