Three Million Affected in Pentagon Personnel Agency Data Breach
Pentagon's DMDC says unauthorized users accessed a file-sharing server for nine months, exposing unencrypted PII of about 3 million people.
The U.S. Defense Manpower Data Center (DMDC) is notifying 2.76 million living and 294,000 deceased individuals that a small number of unauthorized users accessed a file-sharing server between October 2025 and July 16, 2026, when a vulnerability was discovered and patched. The files held unencrypted PII including Social Security numbers plus names, dates of birth, contact details, sex, race, and military occupational data. DMDC, which held at least 60 million records in fiscal 2024, is offering 12 months of IDX credit monitoring with an enrollment deadline of August 19, 2027. No cybercrime group has claimed responsibility.
- 2.76 million living and 294,000 deceased individuals affected
- Unauthorized access to unencrypted PII persisted roughly nine months
- Vulnerability discovered July 16, 2026 and promptly patched
- Exposed data includes SSNs and military personnel information
- 12 months of IDX credit monitoring offered, deadline August 19, 2027
Full article563 words · extracted from securityaffairs.com · click to collapse
 Pierluigi Paganini
 September 29, 2026

Pentagon personnel agency breach exposed data of 3 million people after attackers accessed a file-sharing server for about nine months.
The U.S. Defense Manpower Data Center (DMDC), which maintains personnel records for the Department of Defense, is notifying people that their personal information was exposed in a data breach. According to the agency, unauthorized users accessed one of its file-sharing servers for roughly nine months.
The breach affects 2.76 million living people and 294,000 deceased individuals, according to a Department of War official. DMDC held at least 60 million records in fiscal year 2024, covering military and civilian personnel, contractors, family members, retirees and veterans.
“The Pentagon has confirmed that the breach affects 2.76 million “living individuals,” a category that potentially includes current and former defense personnel or their dependents, and 294,000 “deceased individuals,” a Defense Department official told CNN on Monday, three days after this story was published.” CNN states.
The Defense Manpower Data Center (DMDC) has notified individuals that a security vulnerability exposed personal information stored on one of its file-sharing systems.
The vulnerability was discovered on July 16, 2026, and the US office quickly patched the system and restored it. An investigation found that a small number of unauthorized users had accessed files between October 2025 and the discovery date. The files contained unencrypted personal information.
“On July 16, 2026, a security vulnerability in a DMDC file sharing system was discovered, which allowed unauthorized users to access files. DMDC immediately updated the file sharing system to patch the vulnerability and the system was restored.” reads a data breach notification letter sent to impacted individuals. “Analysis identified that between October 2025 and the date of discovery, a small number of unauthorized users accessed files on a server containing unencrypted PII. The types of PII involved vary by individual; however, in your case, they include social security number (SSN) and at least one additional identifier such as name, date of birth, contact information, sex, race, and military personnel information (such as occupational specialty).”
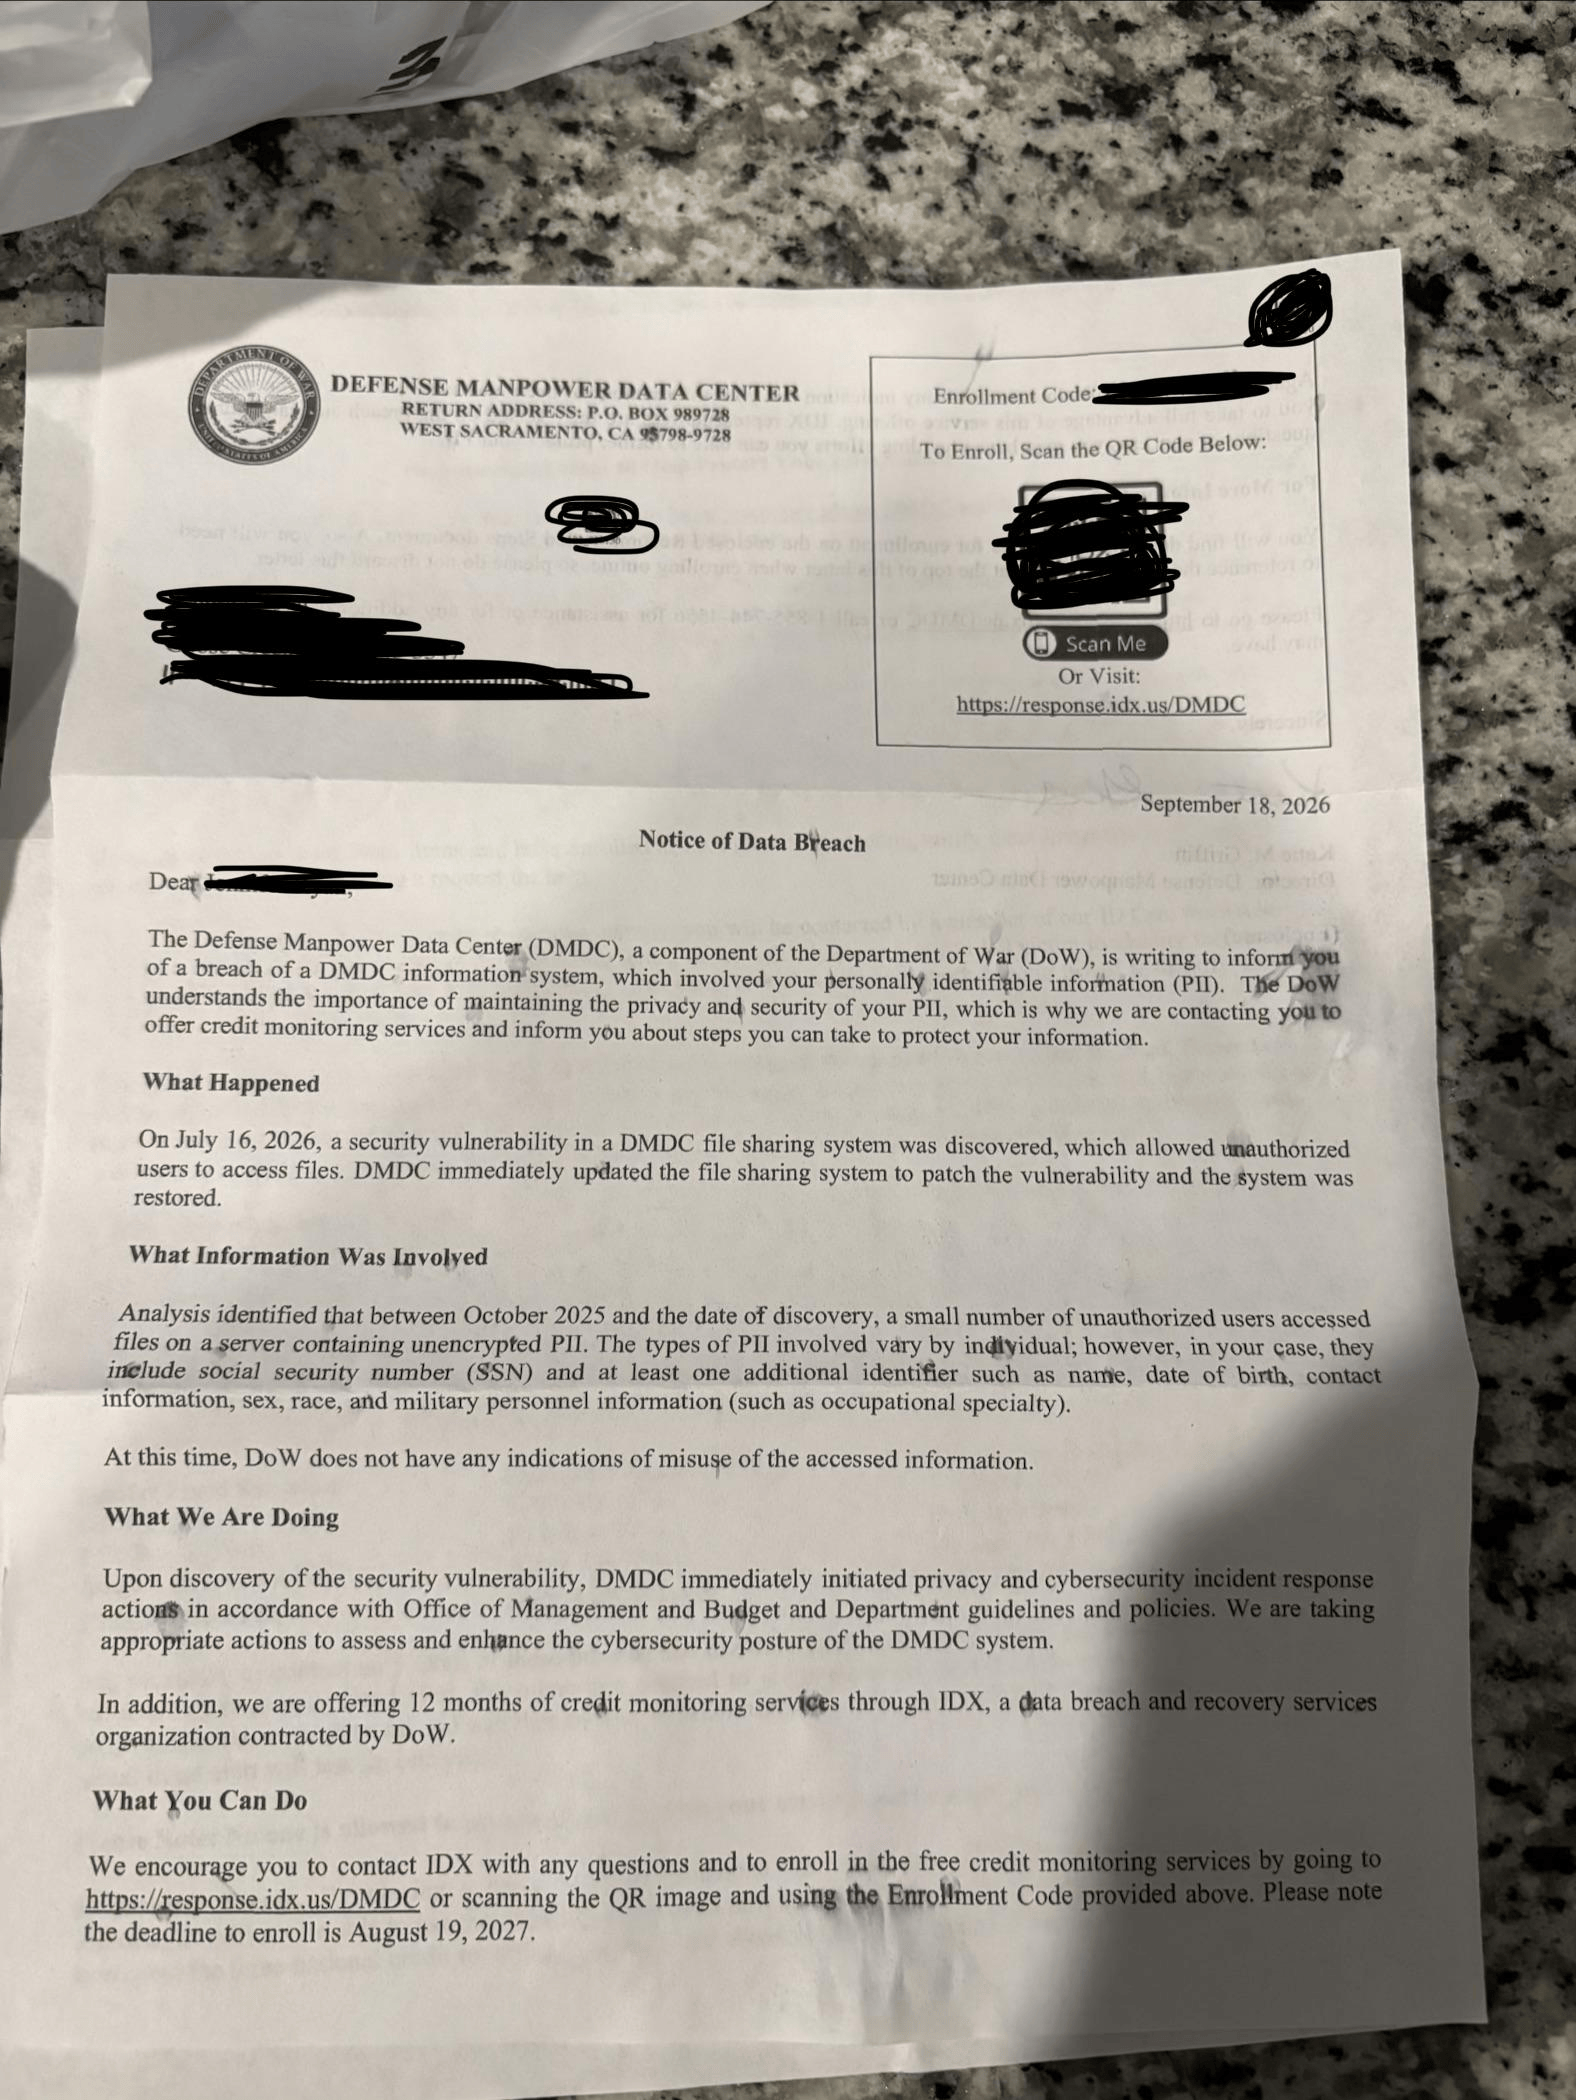
The data exposed varies by person, but in this case included Social Security numbers (SSNs) and at least one other identifier, such as name, date of birth, contact details, sex, race or military personnel information, including occupational specialty.
After discovering the vulnerability, the Defense Manpower Data Center (DMDC) launched its privacy and cybersecurity incident response process in line with U.S. government policies and guidelines. The agency says it is assessing the affected system and taking steps to improve its security.
DMDC is also offering 12 months of free credit monitoring through IDX, a company specializing in data breach and recovery services. Individuals affected by the breach are encouraged to contact IDX with any questions and enroll in the service. Enrollment is available through the dedicated IDX website using the enrollment code provided in the notification. The deadline to enroll is August 19, 2027. The credit monitoring is intended to help affected individuals identify potential misuse of their personal information following the breach.
At this time, no known cybercrime group claimed responsibilty for the attack.
DMDC says it launched privacy and cybersecurity incident response actions after finding the vulnerability.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, US Defense Manpower Data Center)