Criminals turn placeholder domain into ClickFix trap
Attackers registered documentation placeholder domain third-party.com and used it to serve Windows users a ClickFix fake-CAPTCHA page pushing a PowerShell downloader.
Manifold Security researchers found that third-party[.]com, an ordinary domain long hardcoded in software documentation and code examples as a placeholder, was registered by attackers and served a fake Cloudflare-style verification page to Windows visitors. The ClickFix page copied a command to visitors' clipboards and persuaded them to paste it into the Windows Run box, downloading and executing a PowerShell script; the script-hosting domain was not resolving at time of writing. Unlike example.com, which is reserved for documentation, third-party[.]com is registrable, so any docs or tests referencing it now point to attacker infrastructure.
- third-party[.]com, long used as a docs placeholder, was registered and weaponized by attackers.
- Fake Cloudflare CAPTCHA page tricks Windows users into pasting a PowerShell downloader via the Run box.
- example.com is reserved; third-party[.]com is an ordinary registrable domain anyone could own.
- Script-hosting domain was not resolving at time of writing.
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | third-party.com | example. The best-known is probably example.com . Another, third-party[.]com , has often been used in documentation to represent an ex |
Full article564 words · extracted from malwarebytes.com · click to collapse
A domain that has long appeared in software documentation, code examples, and developer test material is now being used to push a ClickFix attack against Windows users.
A placeholder domain stands in for a website in an example. The best-known is probably example.com. Another, third-party[.]com, has often been used in documentation to represent an external website, API, or service.
However, there is a very important difference between the two: example.com is reserved for documentation, while third-party[.]com is an ordinary domain. Anyone could register it, and someone did. Every document, test, and skill that hardcoded it now points readers and users to the attacker’s infrastructure.
Researchers at Manifold Security found that third-party[.]com was serving a fake Cloudflare-style verification page to Windows visitors. The page tries to persuade them to open the Windows Run box and paste a command it has copied to their clipboard.This command is designed to download and execute a PowerShell script. At the time of writing the domain hosting the script is not resolving.
ClickFix is a social-engineering technique that turns the victim into the malware installer.
Instead of relying on a malicious attachment or an obvious executable download, the attacker convinces someone to run a command themselves. Common lures include:
- A fake CAPTCHA or Cloudflare Turnstile check.
- A browser error that claims it needs a “manual fix.”
- A bogus video-player, document-viewer, or popular software download.
- A support scam page that tells the visitor to paste a command into Run, Command Prompt, Terminal, or PowerShell.
ClickFix works because the command often uses legitimate Windows or Mac tools to download and execute the next stage. It also runs with the permissions of the person who has been convinced to enter it.
The consequences can range from information theft to more serious compromise of a company network. In a recent campaign called TerminalFix, a fake Cloudflare CAPTCHA led victims to paste a PowerShell command into Windows Terminal or PowerShell.
How to stay safe
With ClickFix running rampant—and it doesn’t look like it’s going away anytime soon—it’s important to be aware, careful, and protected.
- Slow down. Be wary of a webpage that urges you to run commands on your device, especially if it uses a countdown or other pressure tactic.
- Don’t run commands or scripts from untrusted sources. Never run code or commands copied from websites, emails, or messages unless you trust the source and understand the action’s purpose. Verify instructions independently. If a website tells you to execute a command or perform a technical action, check through official documentation or contact support before proceeding.
- Check what you’re pasting. A website may copy a command to your clipboard without showing you the full text. Don’t paste it into a command window.
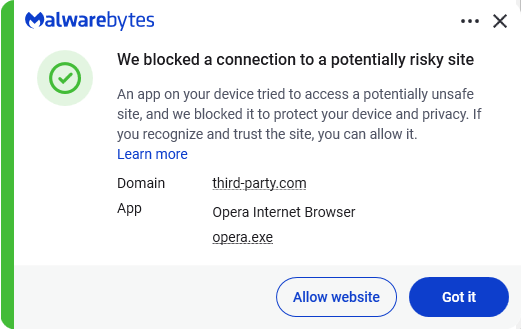
- Secure your device. Use an up-to-date, real-time anti-malware solution with a web protection component.
- Educate yourself on evolving attack techniques. Understanding that attacks may come from unexpected vectors and evolve helps maintain vigilance. Keep reading our blog!
Pro tip: The free Malwarebytes Browser Guard extension warns you when a website tries to copy something to your clipboard.
Stop threats before they can do any harm.
Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →
About the author
Was a Microsoft MVP in consumer security for 12 years running. Can speak four languages. Smells of rich mahogany and leather-bound books.