Palo Alto Networks and NVIDIA want tighter control over AI agents
Palo Alto Networks and NVIDIA are integrating controls that limit what AI agents can access and do.
Palo Alto Networks is expanding its NVIDIA collaboration so organizations can control AI agent activity, network access, and identity. Prisma AIRS AI Gateway on NVIDIA Vera CPUs is described as a future design for inspecting agent interactions, limiting approved tools, and stripping sensitive data. OpenShell is already broadly available and runs agents in isolated environments with file and network policy. Runtime controls on BlueField DPUs are generally available, using DOCA Argus to monitor tool calls and forward telemetry to Cortex XSIAM; an OpenShell integration with Idira for agent secrets is still planned.
- Prisma AIRS AI Gateway on NVIDIA Vera CPUs is described as future architecture.
- OpenShell already isolates agents and enforces file, network, and resource policies.
- Prisma AIRS runtime security on BlueField DPUs is generally available.
- DOCA Argus monitors execution and tool calls, sending telemetry to Cortex XSIAM.
- A planned OpenShell and Idira integration would manage agent identities and secrets.
Full article328 words · extracted from helpnetsecurity.com · click to collapse
Palo Alto Networks is expanding its work with NVIDIA to help companies control what AI agents can access and do. The collaboration covers agent activity, network traffic and identity management through NVIDIA’s Open Agent Safety Platform reference design.
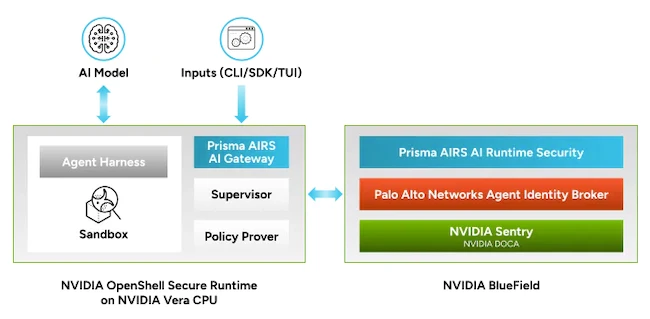
Palo Alto Networks Securing Agents within NVIDIA Open Agent Safety Platform (Source: Palo Alto Networks)
AI agents can write code, retrieve company data and use software tools to complete tasks with limited human input. “Security must control what an agent can do,” wrote Anand Oswal, Palo Alto Networks’ EVP of AI and network security, in the company’s announcement.
Checking agent activity and network traffic
Palo Alto plans to run its Prisma AIRS AI Gateway on systems powered by NVIDIA Vera CPUs. The gateway would let companies manage how their AI agents connect to models and tools from one place. It can inspect interactions, limit access to approved tools, remove sensitive data and track usage and costs. The Vera deployment is described as part of a future architecture.
The company describes the Vera deployment as forward-looking. NVIDIA’s OpenShell software, by comparison, is already broadly available. It runs agents in isolated environments and enforces policies governing their access to files, networks and other resources while they work.
Managing what agents can access
The company also describes Prisma AIRS AI Runtime Security running on NVIDIA BlueField data processing units. The BlueField deployment is generally available. By running security controls on a processor separate from the host, the design can enforce network policy independently of the application running the agent.
The integration can use NVIDIA DOCA Argus to monitor agent execution paths and tool calls, enforce access rules for networks and external APIs, and send telemetry to Cortex XSIAM for analysis and response.
A planned integration between OpenShell and Palo Alto Networks’ Idira platform would add identity and secrets management for agent sandboxes. The companies aim to give agents access appropriate to their tasks without depending on persistent credentials assigned to people.