Microsoft releases Windows 10 KB5122878 extended security update
Microsoft shipped Windows 10 ESU update KB5122878, delivering the record September 2026 Patch Tuesday fixes, including patches for two actively exploited zero-days.
Microsoft released KB5122878 for Windows 10 Enterprise LTSC and ESU customers, moving builds 19045/19044 to .7725 with security and bug fixes. The update carries this month's record September 2026 Patch Tuesday set, which fixed 966 Microsoft vulnerabilities including two actively exploited zero-day flaws. It also fixes BitLocker recovery-key prompts and Remote Desktop audio redirection, and updates Secure Boot certificate rollout and Morocco time zone data. Microsoft reports no known issues with the update.
- Includes September 2026 Patch Tuesday fixes for 966 vulnerabilities, two actively exploited
- Applies to Windows 10 Enterprise LTSC and ESU program enrollees
- Fixes BitLocker recovery key prompt issue and Remote Desktop audio redirection
- No known issues reported; installs via Windows Update
Full article403 words · extracted from bleepingcomputer.com · click to collapse
Microsoft has released the Windows 10 KB5122878 extended security update, which includes this month's record-breaking September 2026 Patch Tuesday fixes, along with a few bug fixes.
If you are running Windows 10 Enterprise LTSC or are enrolled in the ESU program, you can install this update like normal by going into Settings, clicking on Windows Update, and manually performing a 'Check for Updates.'
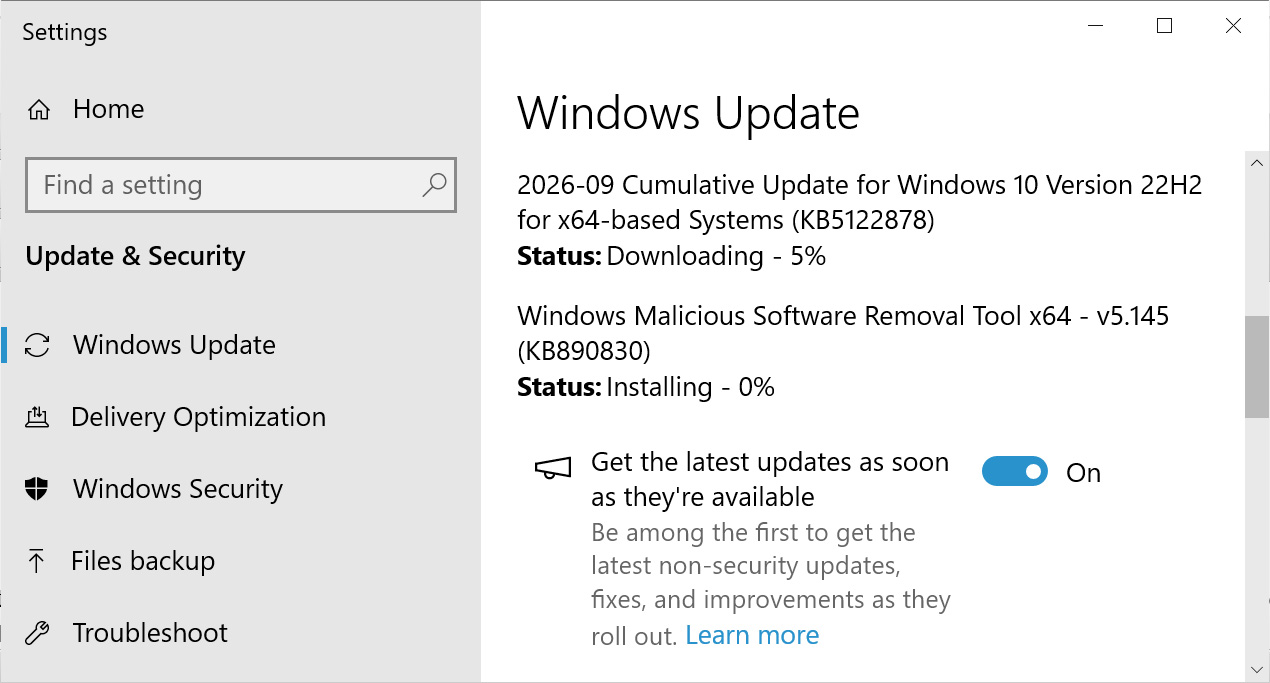
Source: BleepingComputer
After installing this update, Windows 10 will be updated to build 19045.7725, and Windows 10 Enterprise LTSC 2021 will be updated to build 19044.7725.
What's new in Windows 10 KB5122878
Microsoft is no longer releasing new features for Windows 10, and the KB5122878 update primarily contains security updates and bug fixes.
The update also includes fixes released as part of today's record-breaking September 2026 Patch Tuesday, which fixed a massive 966 vulnerabilities across Microsoft's products, including two actively exploited zero-day flaws.
The complete list of fixes in KB5122878 is listed below:
-
[Secure Boot] This update includes additional high confidence device targeting data, increasing coverage of devices eligible to automatically receive new Secure Boot certificates. Certificate deployment via Windows updates continues across supported PCs and non-managed business devices in the coming months.
-
[Date and Time] This update adjusts Morocco Standard Time to reflect Morocco's transition to permanent UTC+00:00 effective September 20, 2026. This change ensures that the correct local time is displayed after the transition.
-
[OMA DM protocol] This update improves the logging features of the OMA DM Client (omadmclient.exe) component. More debug information is now saved when connecting to a server.
-
[Windows Code Integrity policies] Improves application compatibility during Windows certificate-authority rotation by recognizing Microsoft Windows Production PCA 2026 RSA2048-SHA256 as equivalent to PCA 2011.
-
[Remote Desktop] This update addresses an issue that affects Remote Desktop audio redirection. Audio from the remote session might not play on the local computer in certain configurations.
-
[BitLocker Group Policy] This update addresses the "Devices with an unrecommended BitLocker Group Policy configuration might be required to enter their BitLocker recovery key" known issue.
Microsoft says there are no known issues with this update.
Once attackers have valid credentials, only 37% of their actions are blocked
Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.bleepingcomputer.com/news/microsoft/microsoft-releases-windows-10-kb5122878-extended-security-update/