Talos release protection against zero-day vulnerability (CVE-2021
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2021-40444 | Remote Code Execution via MSHTML Rendering Engine in Microsoft Windows/Office (CVE-2021-40444) CVE-2021-40444 is a remote code execution vulnerability in the Microsoft MSHTML browser rendering engine, which Microsoft Office documents can load on Windows systems. It is triggered when a user is convinced to open a specially crafted Office document containing a malicious ActiveX control hosted by the MSHTML engine (tracked as a path-traversal-class issue, CWE-22). A successful attacker gains the ability to run arbitrary code in the context of the logged-on user, with greater impact when that user has administrative rights. Any Windows system that can open Office documents is exposed, spanning Windows 7, 8.1, RT 8.1, Windows 10 (1507 through 21H1) and Windows Server 2004/2008. Exploitation is confirmed in the wild: Microsoft observed targeted attacks at disclosure, the flaw is in CISA's KEV with known ransomware use, and Microsoft released security updates on September 14, 2021. Do: Apply Microsoft's security updates released September 14, 2021 for your Windows version immediately; this is a CISA KEV item with known ransomware use, so patching is treated as mandatory. As interim protection, keep Microsoft Defender Antivirus/Defender for Endpoint signatures current (enterprise detection build 1.349.22.0 or newer, with alerts appearing as 'Suspicious Cpl File Execution') and avoid opening untrusted Office documents, since exploitation requires user interaction with a crafted file. | 8.8 | 97% | KEV ransomware PoC ×2 |
| masshundreds of millions of Windows PCs and servers (nearly all Windows desktop/laptop installs on affected versions at disclosure) |
Full article515 words · extracted from blog.talosintelligence.com · click to collapse
Thursday, September 9, 2021 11:38
Cisco Talos released new SNORT® rules Thursday to protect against the exploitation of a zero-day vulnerability in Microsoft MSHTML that the company warns is being actively exploited in the wild.
Users are encouraged to deploy SIDs 58120 – 58129, Snort 3 SID 300049 and ClamAV signature ID: 9891528 (Doc.Exploit.CVE_2021_40444-9891528-0) to detect and prevent the exploitation of CVE-2021-40444. Cisco Secure Endpoint users can use Orbital Advanced Search to run complex OSqueries to see if their endpoints are vulnerable to this specific threat. An OSquery (CVE-2021-40444_vulnerability status) has been added for this threat.
If an adversary were to successfully exploit this vulnerability, they could remotely execute code on the victim machine or gain complete control. The Microsoft advisory also stated that proof-of-concept code for this vulnerability is available in the wild.While no official Microsoft patch is available at this time, the company advised users to disable Internet Explorer ActiveX controls by updating the system registry. Additionally, Office documents opened from the internet should open in Protected View by default. Users should verify the documents they are opening are in protected view or enable Application Guard for Office to mitigate this vulnerability.
Microsoft disclosed this vulnerability earlier this week, warning of “targeted attacks that attempt to exploit this vulnerability by using specially crafted Microsoft Office documents.”
Cisco Talos has observed malware samples attempting to exploit this vulnerability being uploaded to public repositories dating back to mid-August. We have also observed activity indicating that this vulnerability is being actively used in malware campaigns and will likely continue to be leveraged by additional threat actors moving forward.
The ease with which this vulnerability can be weaponized and the widespread reliance on malicious Office documents to initiate malware infections will likely cause this vulnerability to quickly gain more widespread popularity across the threat landscape.
MSHTML is the Internet Explorer web browser’s rendering engine, though many Office documents also use this engine.
The U.S. Cybersecurity and Infrastructure Security Agency warned users Tuesday of the vulnerability, advising users to follow the workarounds Microsoft outlined. Microsoft is actively researching the issue and plans to either release an out-of-band update or deploy a patch as part of the company’s regularly scheduled monthly security update on Sept. 14.
This is just the latest in the line of zero-day vulnerabilities in Microsoft products. Attackers actively exploited the so-called “PrintNightmare” vulnerability in the PrintSpooler service that could allow authenticated users to achieve escalated privileges, including admin rights. Multiple zero-day vulnerabilities in Microsoft Exchange Server were also a part of attacks from the Hafnium threat actor.
CoverageWays our customers can detect and block this threat are listed below.
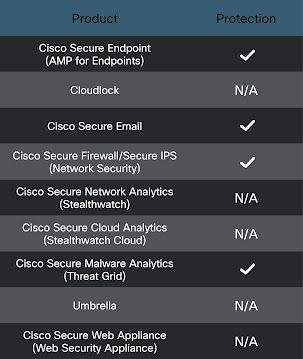
Cisco Secure Endpoint is ideally suited to prevent the execution of the malware detailed in this post. New users can try Cisco Secure Endpoint for free here.
Additional protections with context to your specific environment and threat data are available from the Cisco Secure Firewall Management Center.
Open Source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org.
Text extracted automatically; images, tables and formatting may be missing. Original: https://blog.talosintelligence.com/talos-release-protection-against-zero/