Anthropic’s Claude AI Uncovers Origins of NSA-Provided Cryptographic Keys After 25 Years
Anthropic says Claude reconstructed NIST curve seeds as 1990s lrand48 outputs from Unix timestamps, with no cryptographic break.
Anthropic reported that an internal Claude research model reconstructed how the NSA generated seeds for five NIST elliptic curves in under 30 minutes. The seeds match a 1990s C lrand48 generator initialized with Unix timestamps between May 1997 and April 1998, reproducing P-192, P-224, P-256, P-384, and P-521, plus five ANSI X9.62 example seeds. Anthropic calls this historical reconstruction of public parameters, not private keys, and reports no cryptographic break, new attack, or deployment change. The B-163 seed and some base points remain unexplained.
- Claude linked five NIST curve seeds to lrand48 and 1997–1998 Unix timestamps.
- Reconstruction covered P-192 through P-521 but not the B-163 seed.
- Anthropic reports no ECDSA break and no reason to change deployments.
- The $36,864 bounty will be donated to the Internet Security Research Group.
Full article497 words · extracted from gbhackers.com · click to collapse
Anthropic says an internal Claude research model reconstructed how the National Security Agency generated seeds for five NIST elliptic curves in under 30 minutes, addressing a cryptographic mystery spanning roughly 25 years.
Its October 16 report attributes the seeds to a standard C pseudorandom number generator initialized with Unix timestamps, rather than secret passphrases.
Despite references to cryptographic keys, the discovery concerns public curve parameters, not private keys or signature secrets. Anthropic describes the work as historical reconstruction, reporting no cryptographic break, new attack, or reason to change deployments.
Claude AI Solves 25-Year-Old NSA Cryptography Mystery
NIST adopted ECDSA and recommended elliptic curves in its FIPS 186-2 Digital Signature Standard in 2000. Published seeds supported verification of curve parameter derivation, but their unexplained origins led researchers to question whether the NSA deliberately influenced curve selection.
A bounty organized by cryptographer Filippo Valsorda encouraged efforts to explain those seeds. Earlier accounts suggested they originated from humorous phrases associated with NSA mathematician Jerry Solinas.
Claude instead examined programming patterns typical of 1990s C libraries and identified lrand48, a linear congruential generator with a 48-bit internal state.
The model scanned published seeds across 34 generator-and-output-slice combinations. Four binary-curve seeds contained five 32-bit words whose highest bits were consistently zero, matching lrand48’s 31-bit output.
Enumerating the 17 hidden state bits and checking subsequent outputs recovered candidate generator states. The prime-curve seeds exposed fewer bits from each generator call.
Claude applied the Lenstra–Lenstra–Lovász lattice basis reduction algorithm to reconstruct internal states from these truncated outputs. Five NIST seeds and five ANSI X9.62 example seeds matched a construction collecting bytes from lrand48() >> 23.
Reversing the generator revealed initialization values corresponding to Unix timestamps between May 1997 and April 1998. The recovered construction reproduced P-192, P-224, P-256, P-384, and P-521. For P-256, the standardized seed appeared as candidate 1,842 in a sequence initialized on August 16, 1997.
Claude also reconstructed base-point generation for P-192 and five ANSI example curves using the generator from FreeLIP, Arjen Lenstra’s arithmetic package. These base points differ from the curve seeds and serve as fixed points for cryptographic operations.
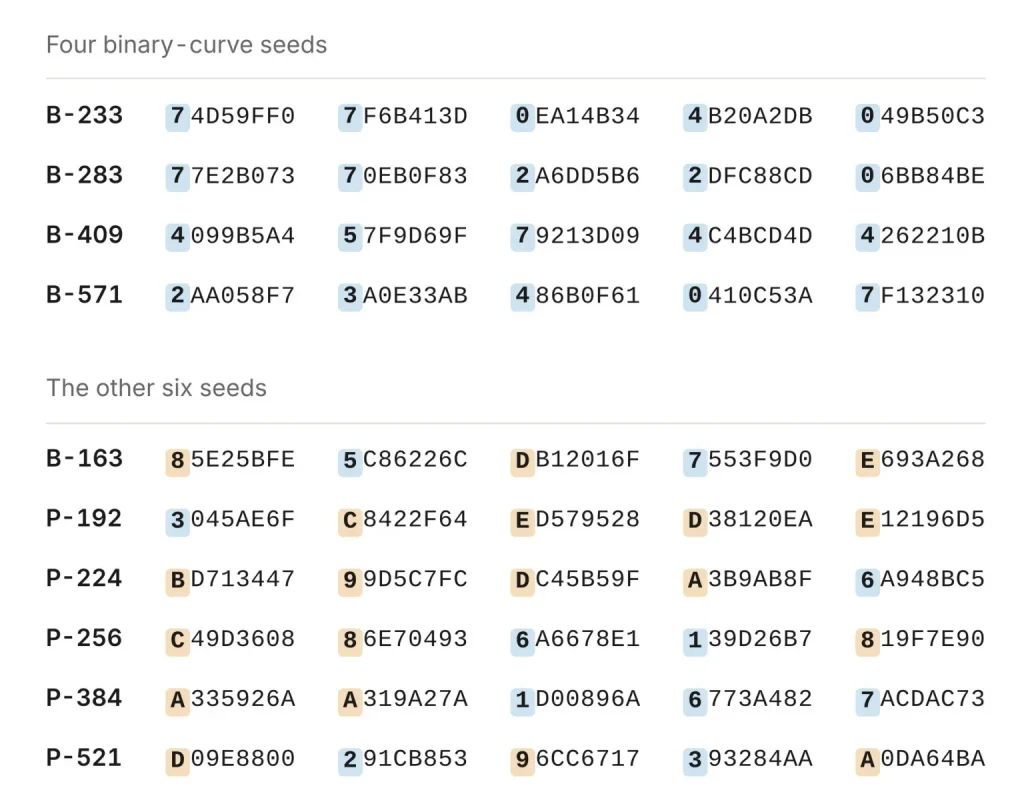
The reconstruction remains incomplete. Anthropic could not explain the B-163 seed or several base points. Researchers also found skipped candidates that apparently produced suitable curves, leaving the original selection criteria unresolved.
Anthropic argues that the reproducible timestamp-based construction reduces concerns about intentional manipulation, although it does not establish every historical decision or prove that no alternative generation runs occurred.
The $36,864 bounty will be donated to the Internet Security Research Group. For defenders, the outcome is greater transparency into public cryptographic parameters, not recovered secrets or demonstrated ECDSA weakness.
Join 16,000+ SOC teams using ANY.RUN to streamline threat investigations and reduce manual effort. Explore for your team
Eswar is a Cyber security content editor with a passion for creating captivating and informative content. With years of experience under his belt in Cyber Security, he is covering Cyber Security News, technology and other news.