2,000 Leaked Documents Reveal How Russia Turns Engineering Students Into GRU Cyber Operators
Leaked Bauman Moscow State Technical University files reveal a hidden GRU training pipeline feeding APT28 and Sandworm units.
More than 2,000 leaked Bauman Moscow State Technical University documents show that Department No. 4, a hidden program inside the Military Training Center, trained roughly 250 career and reserve students for GRU cyber and intelligence roles across six academic years. Graduates were linked to Military Unit 26165 (APT28), Unit 74455 (Sandworm/APT44) and Unit 29155, and former Unit 26165 commander Viktor Netyksho was involved in department oversight. Reporting by The Insider, The Guardian, Le Monde, Der Spiegel and other outlets, with independent analysis by DomainTools, estimates 10-15 students annually were selected for GRU-related assignments before graduating.
- Bauman's unlisted Department No. 4 trained about 250 students in special intelligence, cyber operations and IT protection.
- Graduates were assigned to Military Unit 26165 (APT28) and Unit 74455 (Sandworm/APT44).
- Former Unit 26165 commander Major General Viktor Netyksho was part of the department's oversight structure.
- Coursework covered cryptography, steganography, intrusion detection, hardware implant discovery and propaganda production.
- Reporting establishes unit placements, not confirmed participation in specific operations.
Full article932 words · extracted from securityaffairs.com · click to collapse
 Pierluigi Paganini
 September 03, 2026

2,000 leaked files expose Bauman University’s hidden Department No. 4, which trained GRU-linked hackers and propagandists linked to APT28 and Sandworm.
Leaked Documents Expose Bauman University’s Hidden Department That Trained Hackers, Propagandists, and Malware Developers for the GRU
More than 2,000 internal documents from Bauman Moscow State Technical University have been reviewed by an international media consortium, and the picture they describe is not a conventional cybersecurity program. The files span academic and administrative records through 2025.
“Recently leaked records show that Bauman Moscow State Technical University’s Department No. 4 operated as a long-term training pipeline for Russian military intelligence and cyber operations.” reads the report published by DomainTools. “The department served several elements of the Russian General Staff and trained roughly 250 career and reserve students across three specialties: special intelligence (“Служба специальной разведки”), operational information-technical effects (“Применение сил и средств информационно-технического воздействия и защиты от информационно-технического воздействия”), and information-technology protection (”3ащита информационных технологий”). “
Department No. 4, also called “Special Training,” operated inside Bauman’s Military Training Center and doesn’t appear anywhere on the university’s public organizational chart. The GRU’s talent pipeline tends not to announce itself.
The investigation was carried out by a group of media outlets including The Insider, The Guardian, Le Monde, Der Spiegel, Delfi, VSquare, and FRONTSTORY.PL. DomainTools researchers also analyzed the leaked files independently. A DarkForums user known as “Losyash” may have shared the data, but it has not been confirmed that the account originally obtained the records.
The department trained students in three military specialties. These covered special intelligence, information and cyber operations, and the protection of IT systems. In practice, the courses included espionage, offensive cyber operations, electronic reconnaissance, secure systems, and influence operations.
Around 250 career and reserve students went through the program over six academic years. Researchers estimate that 10 to 15 students each year were selected for GRU-related assignments before graduating.
“Technical protection training covered cryptography and steganography, as well as code analysis and intrusion detection. Students were also trained in hardware inspection, the discovery of physical implants, and the identification of undocumented device functions. These subjects point to possible assignments in technical counterintelligence and supply chain security, as well as firmware analysis and embedded system inspection. Other likely functions include secure procurement and the protection of specialized military platforms.” continues the report. “The files also reveal an underreported malware-analysis and cyber threat intelligence program.”
One advanced practical assignment required the creation of a social-media video built around what the course materials called “manipulation, pressure, and hidden propaganda.” This counted as coursework.
Course materials defined “information-technical weapons” as tools and methods designed to alter, destroy, copy, block, or manipulate information. Red-team and blue-team functions were treated as a single discipline, not separate tracks, which mirrors how Russian military doctrine actually deploys cyber operators.
The personnel links are what make this more than a training curiosity. The leaked records identify Major General Viktor Netyksho as involved in Department No. 4’s oversight. Netyksho was the former commander of Military Unit 26165, the GRU formation publicly associated with APT28, also tracked as Fancy Bear, Sofacy, and STRONTIUM. He was among the 12 GRU officers indicted by the United States in 2018 for interference in the 2016 presidential election.
“Reporting identified graduates assigned to GRU Military Unit 26165 (associated with APT28) and Military Unit 74455 (associated with Sandworm), and linked senior officers, including former Unit 26165 commander Viktor Netyksho, to student oversight.” continues the report. “The data also connected senior GRU officers to the supervision and evaluation of Bauman students. Viktor Netyksho, the former commander of Unit 26165 and the 85th Main Special Service Center, is part of the department’s teaching and oversight structure.”
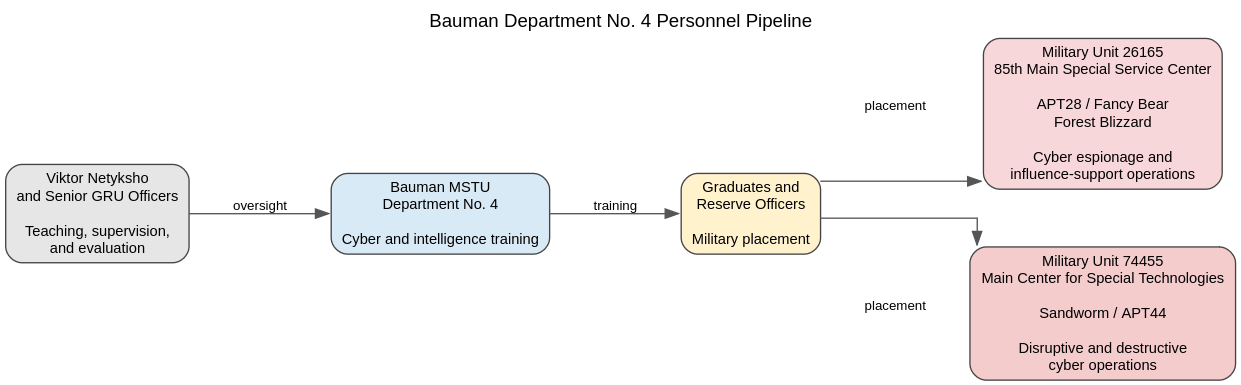
The reporting also identifies Aleksei Kondrashov, a 2024 Department No. 4 graduate, as linked to Military Unit 74455: the GRU’s Main Center for Special Technologies, known publicly as Sandworm, or APT44. That unit has been associated with the 2017 NotPetya attack and ongoing destructive operations against Ukraine. DomainTools also connected graduates and senior staff to Military Unit 29155, a GRU formation linked to sabotage and assassination operations in Europe.
A necessary precision: the reports establish unit placements, not individual operational involvement. A documented assignment to Military Unit 74455 doesn’t establish that a specific person participated in a specific attack. That distinction matters for both attribution work and legal proceedings.
What the leak does establish is the factory behind the names. APT28 and Sandworm are the threat groups that security teams track, attribute, and brief about. Department No. 4 is where some of the people running those operations were systematically trained, assessed, and selected.
For defenders, DomainTools summarizes the implication precisely: Russian operations should be tracked as a combined threat in which espionage, destructive attacks, military reconnaissance, technical surveillance, and influence campaigns draw on the same personnel pipelines and the same underlying doctrine. The Bauman material makes that pipeline visible for the first time at this level of institutional detail.
“The documents show that Department No. 4 is a small part of a larger long-term military training system, not a single hacking unit. The program prepared personnel for espionage and offensive cyber operations within a larger Russian technical university system.” concludes the report. “Its doctrine treated cyber warfare as more than network intrusion. Students were taught not only adversarial cyber warfare, but also a larger holistic doctrine of cyber war using both defense and attack to be better able to carry out successful campaigns.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Russia)
Text extracted automatically; images, tables and formatting may be missing. Original: https://securityaffairs.com/198332/intelligence/2000-leaked-documents-reveal-how-russia-turns-engineering-students-into-gru-cyber-operators.html