ToolHive: The open-source way to run any MCP server securely
Stacklok's open-source ToolHive runs Model Context Protocol servers in isolated containers with per-request identity enforcement, audit logging and a signed registry.
ToolHive, shipped under Apache 2.0, containersizes MCP servers locally via Docker or Podman or in clusters through a Kubernetes operator, applying permissions, network filtering, and secrets management. The platform includes a Registry Server implementing the official MCP Registry API with signing and provenance verification, a Virtual MCP Server gateway with OIDC/OAuth single sign-on and OpenTelemetry traces, and a desktop Portal for one-click installs. The browser-based cloud UI is retired, so the desktop app and CLI are the supported rollout paths.
- Runs MCP servers in per-container isolation with minimal permissions and no local credentials
- Registry Server signs and verifies provenance via the official MCP Registry API
- Gateway unifies backends behind one endpoint with OIDC/OAuth SSO and OpenTelemetry
- Browser cloud UI retired; build on desktop app and CLI
Full article433 words · extracted from helpnetsecurity.com · click to collapse
ToolHive is an open-source platform that runs Model Context Protocol servers inside containers. An MCP server is the connector that lets an AI client like Cursor or Claude Code reach an outside tool, and Stacklok ships ToolHive under Apache 2.0, so the runtime, the Kubernetes operator, and the registry cost nothing to self-host.
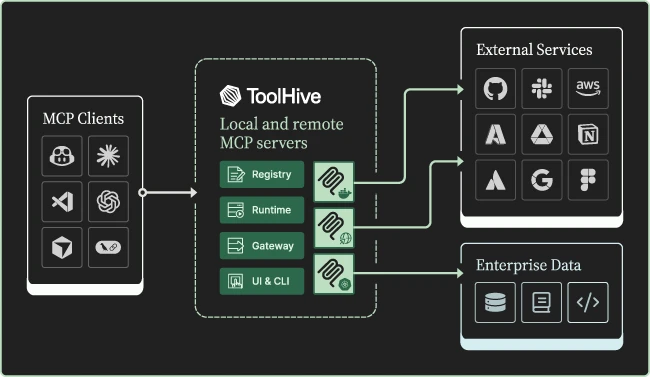
A server you install by hand sits on the machine with the machine’s credentials and the machine’s network access. ToolHive drops each one into its own container with a minimal permission file and no local credentials attached. Point it at an authentication source and it starts enforcing identity and access policy per request, with audit logs to match. Don’t, and you have a sandbox and not much else.
What the pieces do
Four parts make up the platform. The Runtime is the one most people meet first: it runs MCP servers in containers, locally through Docker or Podman, or in a cluster through the Kubernetes operator, with permissions, network filtering, and secrets management applied on the way in. It will also containerize a server whose authors never shipped an image, pulling it straight from a package manager.
The Registry Server is where an admin curates the catalog a team is allowed to use. It implements the official MCP Registry API, signs servers, and verifies provenance. The Gateway, which Stacklok calls Virtual MCP Server, collapses several backends behind one endpoint with OIDC or OAuth single sign-on, OpenTelemetry traces, and Prometheus metrics. The Portal is the friendly end: a desktop app, a catalog to browse, one-click installs.
One piece is in motion. The browser-based cloud UI is marked retired, so build a rollout around the desktop app and the CLI rather than the web surface.
What this changes for you
Building an MCP server is the easy half, and plenty of tools already do it. The operational half is knowing which servers are running on which machines and what each one can touch, and that is the gap ToolHive goes after.
The container boundary holds without much work from you. Everything past it, the identity enforcement, the audit trail, the policy filtering, means wiring ToolHive into an identity provider and a telemetry stack you already run. Install it on a laptop and you get isolation. Governance is a second project.
ToolHive is available for free on GitHub.

Must read:
- 20 open-source cybersecurity tools to keep your team ready for anything
- GitHub CISO on security strategy and collaborating with the open-source community

Subscribe to the Help Net Security ad-free monthly newsletter to stay informed on the essential open-source cybersecurity tools. Subscribe here!
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.helpnetsecurity.com/2026/09/07/toolhive-open-source-mcp-server-security/