Twitch extension with 30K installs exposes users’ OAuth tokens
Twitch extension with 30,000+ installs exfiltrates users' OAuth session tokens to Russian-run JeetBot proxy servers.
Socket analysis shows the "Twitch Enhanced Viewer | JeetBot" browser extension, with over 30,000 installs on the official Chrome and Firefox stores, captures the Twitch web client's authorization header and extracts the user's OAuth token. The token is appended as an auth= URL parameter to video playlist requests routed through JeetBot proxy servers, landing in cleartext request logs retrievable by the Russian-language bot service vendor; ten hardcoded Russian-language channels are exempted. Earlier versions used more explicit token exfiltration, and the extension remained live in both stores at publication. Socket recommends removing the extension, disconnecting all Twitch sessions, and re-authenticating.
- 30,000+ installs across official Chrome Web Store and Firefox Add-ons
- Extension extracts Twitch OAuth tokens from web client authorization headers
- Tokens appended as auth= URL params, written in cleartext to proxy server logs
- Ten hardcoded Russian-language Twitch channels exempted from token capture
- Users should remove extension, revoke sessions, and re-authenticate
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | ttvnw.net | tension redirects Twitch’s video playlist request (to usher.ttvnw[.]net ) through that proxy, it appends the token as an &auth= q |
Full article497 words · extracted from bleepingcomputer.com · click to collapse
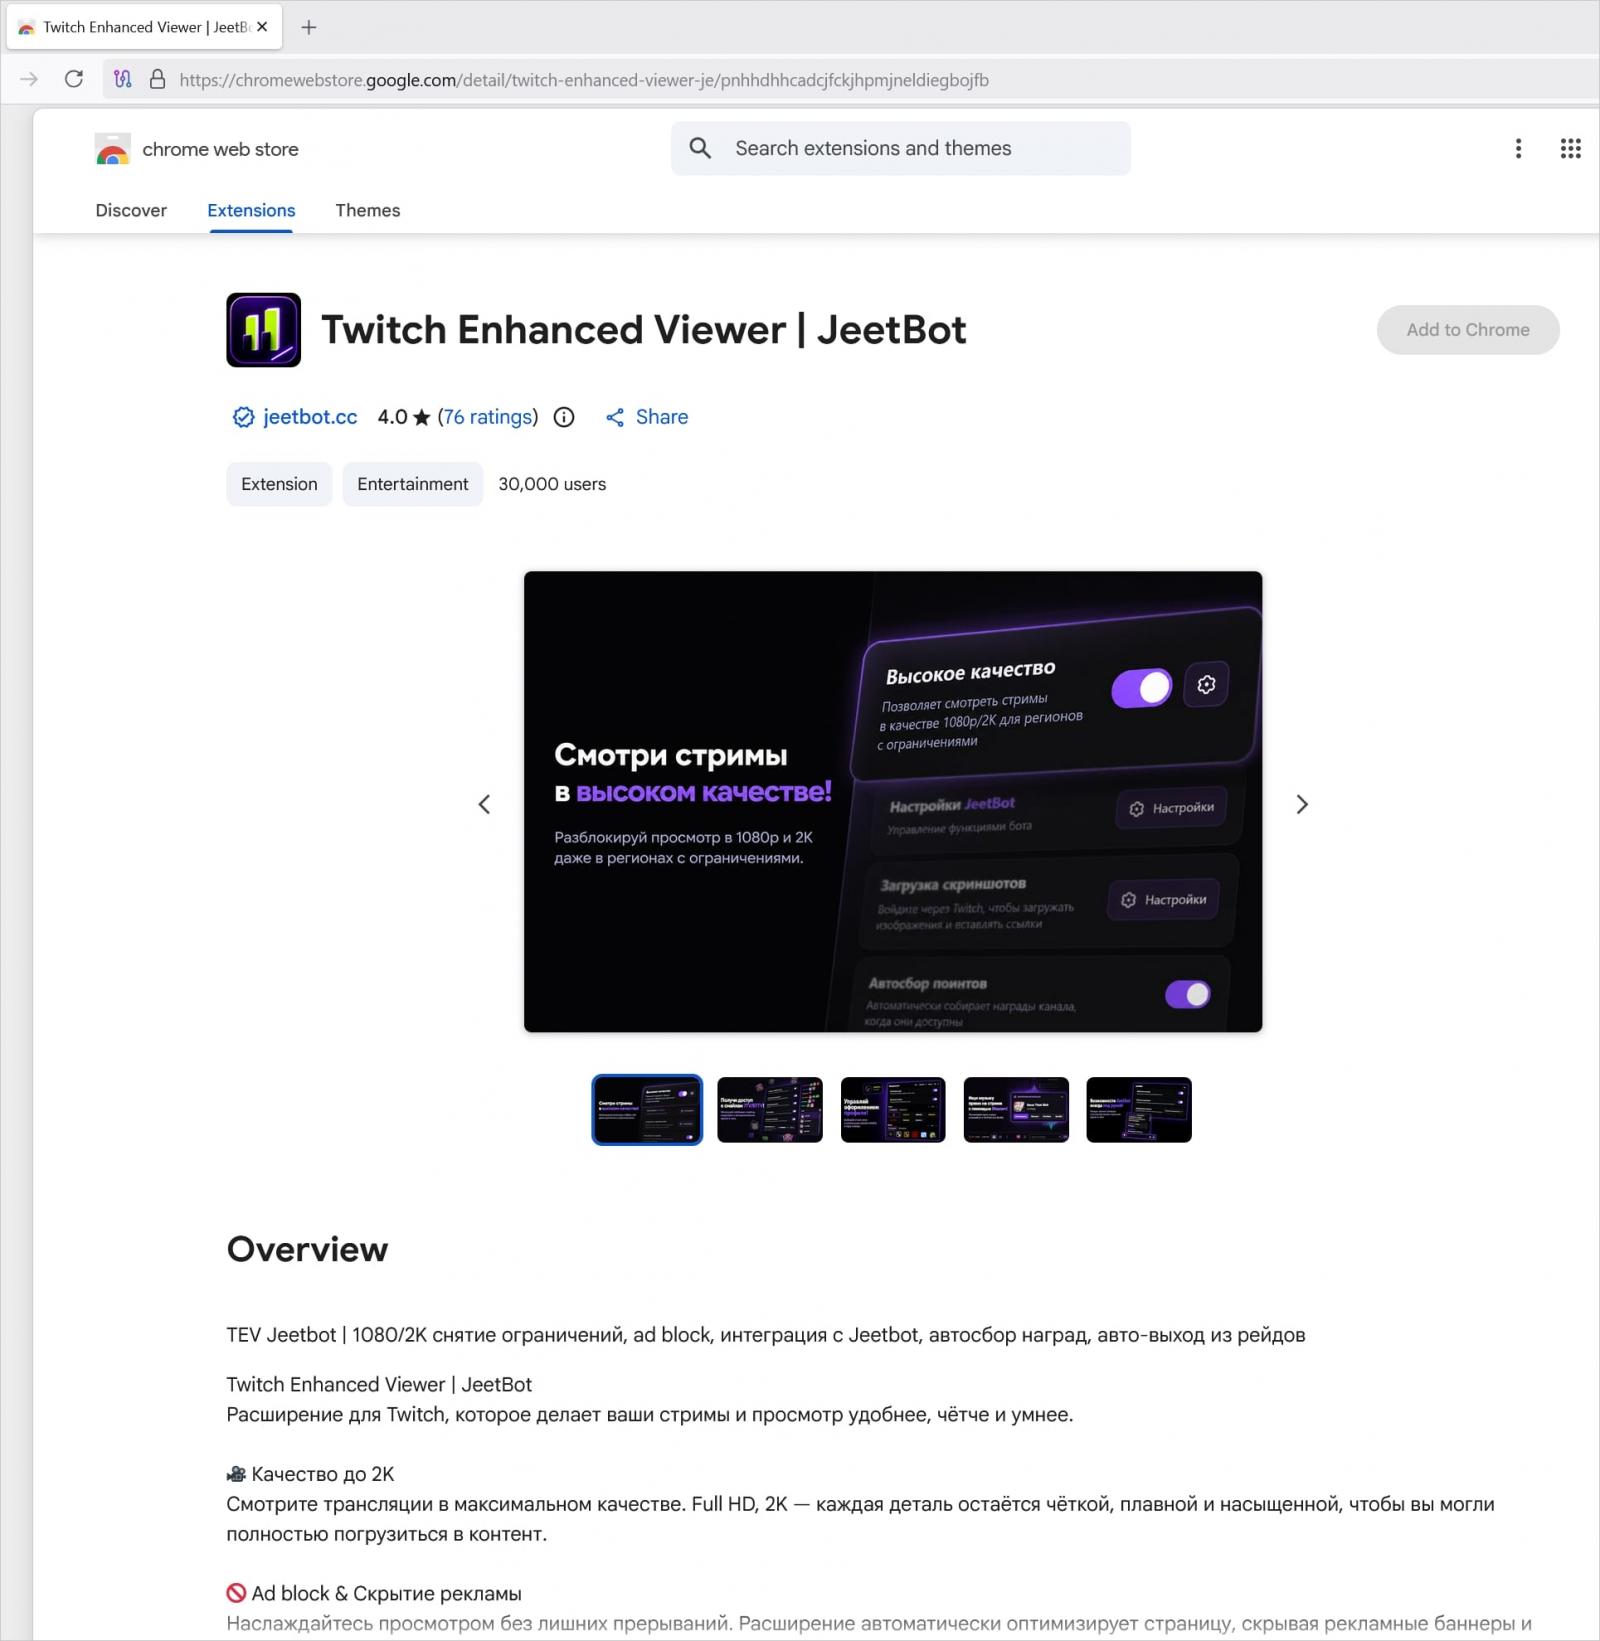
A browser extension called Twitch Enhanced Viewer | JeetBot, available in the official Chrome and Firefox stores, sends users’ Twitch OAuth session tokens to a commercial bot service.
The extension has more than 30,000 installs and is advertised as a legitimate third-party tool for Twitch that can block ads, force 1080p (full HD) playback, bypass region restrictions, and enable channel-point collection.
However, an analysis from application security company Socket shows that the extension captures the authorization header used by the Twitch web client, extracts the user OAuth token, and sends the credentials through proxy servers.
The servers are operated by JeetBot, a commercial Russian-language streaming and chatbot service that offers tools for Twitch, Kick, and VK Live.
In current versions of the extension, the token is appended directly to redirected proxy requests as an auth= URL parameter, ending up in the proxy server’s request logs, where the software vendor can easily retrieve it.
“When the extension redirects Twitch’s video playlist request (to usher.ttvnw[.]net) through that proxy, it appends the token as an &auth= query parameter,” Socket says.
“Because the token is placed in the URL query string, it is written in cleartext into the proxy server’s request logs.”
This process occurs for every Twitch channel the user watches, except for a set of ten Russian-language channels hardcoded into the extension’s code.
Source: BleepingComputer.com
Socket highlights that earlier versions of the extension included more explicit credential-theft mechanisms.
In the description of the product in the Firefox Add-ons store, the developer provided a disclaimer about the previously used mechanism, saying:
“Previous versions of the extension transmit your OAuth-twitch token to our server. This is necessary for the stream to run in 1080/1440p.” [machine translated]
The data privacy disclosure for the Chrome variant of Twitch Enhanced Viewer | JeetBot says that its developer “disclosed that it will not collect or use your data.”
The declaration covers selling user data to third parties except for approved cases, transferring it for reasons outside the product’s “core functionality,” or “to determine creditworthiness or for lending purposes.”
At the time of publishing, the extension was still present in both the Chrome Web Store and the Firefox Add-Ons store.
BleepingComputer has sent JeetBot a request for additional information at the email address indicated in the Chrome Web Store, but we have not received a response by publication.
Socket researchers believe the extension represents a security risk and recommend that users remove it from their browsers, disconnect all sessions in Twitch, and then re-authenticate, to invalidate any token that may have been forwarded.
Developers are advised to avoid routing requests with authentication headers or tokens through third-party servers.
Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.bleepingcomputer.com/news/security/twitch-extension-with-30k-installs-exposes-users-oauth-tokens/