Rejetto HFS servers now actively scanned for critical RCE flaw
Hackers are scanning Rejetto HFS for CVE-2026-61500, a critical flaw enabling admin session forgery and RCE.
Attackers are scanning for CVE-2026-61500 in Rejetto HTTP File Server versions 3.0.0 through 3.2.0, a session-cookie signing flaw that can lead to administrator takeover and remote code execution. The server derives its signing key from Math.random() and leaks generator outputs to unauthenticated clients, letting an attacker reconstruct the key and forge an admin cookie, then run custom server-side JavaScript via server_code. VulnCheck Canary honeypots saw small-scale probes from a single China Telecom IP against deployments in Japan and the United States, with no confirmed successful exploitation reported. Horizon3 published a proof-of-concept on September 30, 2026, after Anthropic's Mythos model helped find the bug; the fix is in 3.2.1, and 3.3.4 is the latest stable release.
- CVE-2026-61500 lets remote attackers recover a Math.random session signing key.
- Forged administrator cookies can run server-side JavaScript for remote code execution.
- VulnCheck honeypots saw limited probes from a single China Telecom IP.
- No confirmed successful exploitation or post-exploitation activity has been reported.
- Upgrade Rejetto HFS to 3.2.1 or preferably stable release 3.3.4.
Vulnerabilities mentionedAll →
- CVE-2026-615009.3<1%Rejetto HFS 3.0.0 through 3.2.0 derives its session-cookie signing key from the non-cryptographic Math.random() generator and discloses outputs of the same…published PoC
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2026-61500 | Rejetto HFS 3.0.0 through 3.2.0 derives its session-cookie signing key from the non-cryptographic Math.random() generator and discloses outputs of the same… |
Full article434 words · extracted from bleepingcomputer.com · click to collapse

Hackers are actively scanning for a Rejetto HFS weak signing key vulnerability, tracked as CVE-2026-61500, that allows session forgery, account takeover, and remote code execution (RCE).
VulnCheck VP of Security Research Caitlin Condon posted on LinkedIn over the weekend that the company's Canary Intelligence honeypots had observed probes targeting CVE-2026-61500.
Condon said the observed activity appears to be small-scale reconnaissance from a single China Telecom IP address probing deployments in Japan and the United States.
Rejetto HFS (HTTP File Server) is a free and open-source file-sharing server tool used for self-hosted file sharing on Windows, Linux, and macOS.
CVE-2026-61500, first published on July 13, 2026, is a session-cookie signing weakness and leakage issue fixed in Rejetto HFS version 3.2.1.
"Rejetto HFS 3.0.0 through 3.2.0 derives its session-cookie signing key from the non-cryptographic Math.random() generator and discloses outputs of the same generator to unauthenticated clients during login," reads the flaw description on the NIST NVD.
"A remote attacker can collect a small number of login responses, reconstruct the generator's state, recover the signing key, and forge a valid administrator session cookie, leading to full administrative access and remote code execution via the server_code configuration feature."
Horizon3 researchers discovered the flaw using Anthropic's Mythos model, which identified both the weak signing-key generation and the leak that enabled key recovery.
Horizon3 published more details about the flaw and a proof-of-concept (PoC) exploit in a write-up on September 30, 2026.
"Mythos didn't just flag the insecure PRNG in isolation – it simultaneously identified that the application leaked raw Math.random() outputs through a separate code path, recognized those two facts as a chain, and determined the leak produced exactly the observations needed to make state recovery feasible," explained Horizon3.
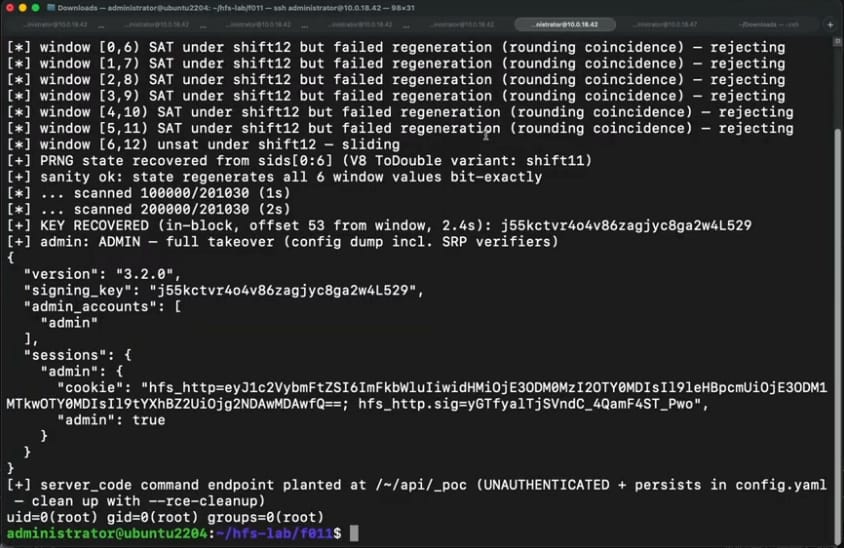
Source: Horizon3
The researchers' exploit demonstrates the chain to abuse HFS's built-in ability to execute custom server-side JavaScript to achieve remote code execution.
The release of these technical details may have prompted the probing activity targeting CVE-2026-61500.
Possible attack scenarios include accessing, stealing, or deleting HFS files, installing malware on the server, or using the compromised host to access internal systems.
However, VulnCheck has not shared details on successful exploitation or any post-exploitation activity.
Users of Rejetto HFS are recommended to upgrade to version 3.2.1 or, ideally, the latest stable release, 3.3.4, as soon as possible.
Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.