Threat Advisory: Apache HTTP Server zero-day vulnerability opens door for attackers
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2021-41733 | Oppia 3.1.4 does not verify that certain URLs are valid before navigating to them. Oppia 3.1.4 does not verify that certain URLs are valid before navigating to them. NVD description · AI analysis pending | 6.1 | <1% |
| — | ||
| CVE-2021-42013 | Path Traversal and RCE in Apache HTTP Server (follow-up to CVE-2021-41773) Apache HTTP Server contains a path traversal flaw (CWE-22) that can lead to remote code execution; CVE-2021-42013 resolves an incomplete patch previously issued for CVE-2021-41773. The flaw is triggered when files outside directories mapped by Alias-like directives are not protected by the default 'require all denied' configuration, or when CGI scripts are enabled, allowing an attacker to traverse outside the intended directory roots. An attacker can read files outside the configured paths, and where CGI script execution is enabled, achieve remote code execution on the server. The affected product per CISA is Apache HTTP Server; the source data does not specify exact version ranges, so defenders should consult the vendor advisory for fixed releases. Exploitation is confirmed in the wild: the vulnerability was added to CISA KEV on 2021-11-03 with known ransomware use, EPSS estimates a 100% probability of exploitation within 30 days, and no public PoC is listed. Do: Apply the Apache HTTP Server update per vendor instructions immediately, since this is a CISA KEV item with known ransomware use and near-certain near-term exploitation. Until patched, ensure directories targeted by Alias-like directives are covered by 'require all denied' defaults and disable CGI script execution where it is not required. Review access logs for path traversal probes and confirm no replaced version retains the incomplete earlier patch. | 9.8 | 100% | KEV ransomware PoC ×6 |
| massorder of 100,000+ internet-exposed Apache HTTP Server instances at disclosure time |
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| ipv4 | 134.122.112.12 | this threat. Indicators of compromise (IoCs) IP Addresses: 134.122.112.12 143.198.136.88 161.35.188.242 161.35.86.181 167.99.133.28 1 |
| ipv4 | 137.184.69.137 | 55 161.35.215.189 143.198.62.76 174.138.42.66 46.101.59.235 137.184.69.137 165.227.125.18 |
| ipv4 | 141.101.146.162 | 46.210.169 94.46.15.22 69.49.228.92 69.49.235.93 3.83.56.46 141.101.146.162 156.146.50.105 156.146.50.98 185.254.96.162 185.56.80.11 19 |
| ipv4 | 14.161.74.29 | 40.67 47.106.92.240 45.77.138.50 45.86.203.97 27.102.114.78 14.161.74.29 149.28.140.81 185.98.87.200 217.138.216.4 142.93.153.4 178. |
| ipv4 | 142.93.153.4 | 4.78 14.161.74.29 149.28.140.81 185.98.87.200 217.138.216.4 142.93.153.4 178.128.172.249 79.165.90.196 51.79.142.118 59.12.193.82 64 |
| ipv4 | 143.198.136.88 | ndicators of compromise (IoCs) IP Addresses: 134.122.112.12 143.198.136.88 161.35.188.242 161.35.86.181 167.99.133.28 162.241.114.189 |
| ipv4 | 143.198.62.76 | 45.146.164.110 145.220.25.28 165.227.79.155 161.35.215.189 143.198.62.76 174.138.42.66 46.101.59.235 137.184.69.137 165.227.125.18 |
| ipv4 | 145.220.25.28 | 22 35.82.51.168 37.237.230.28 44.242.181.147 45.146.164.110 145.220.25.28 165.227.79.155 161.35.215.189 143.198.62.76 174.138.42.66 4 |
| ipv4 | 149.28.140.81 | 92.240 45.77.138.50 45.86.203.97 27.102.114.78 14.161.74.29 149.28.140.81 185.98.87.200 217.138.216.4 142.93.153.4 178.128.172.249 79 |
| ipv4 | 156.146.50.105 | .15.22 69.49.228.92 69.49.235.93 3.83.56.46 141.101.146.162 156.146.50.105 156.146.50.98 185.254.96.162 185.56.80.11 194.126.177.17 19 |
| ipv4 | 156.146.50.98 | 8.92 69.49.235.93 3.83.56.46 141.101.146.162 156.146.50.105 156.146.50.98 185.254.96.162 185.56.80.11 194.126.177.17 192.3.194.202 89 |
| ipv4 | 161.35.188.242 | mpromise (IoCs) IP Addresses: 134.122.112.12 143.198.136.88 161.35.188.242 161.35.86.181 167.99.133.28 162.241.114.189 162.241.69.182 |
| ipv4 | 161.35.215.189 | 44.242.181.147 45.146.164.110 145.220.25.28 165.227.79.155 161.35.215.189 143.198.62.76 174.138.42.66 46.101.59.235 137.184.69.137 16 |
| ipv4 | 161.35.86.181 | IP Addresses: 134.122.112.12 143.198.136.88 161.35.188.242 161.35.86.181 167.99.133.28 162.241.114.189 162.241.69.182 185.246.210.16 |
| ipv4 | 162.241.114.189 | 2 143.198.136.88 161.35.188.242 161.35.86.181 167.99.133.28 162.241.114.189 162.241.69.182 185.246.210.169 94.46.15.22 69.49.228.92 69. |
| ipv4 | 162.241.69.182 | 161.35.188.242 161.35.86.181 167.99.133.28 162.241.114.189 162.241.69.182 185.246.210.169 94.46.15.22 69.49.228.92 69.49.235.93 3.83. |
| ipv4 | 165.227.125.18 | 89 143.198.62.76 174.138.42.66 46.101.59.235 137.184.69.137 165.227.125.18 |
| ipv4 | 165.227.79.155 | 8 37.237.230.28 44.242.181.147 45.146.164.110 145.220.25.28 165.227.79.155 161.35.215.189 143.198.62.76 174.138.42.66 46.101.59.235 13 |
| ipv4 | 167.99.133.28 | 134.122.112.12 143.198.136.88 161.35.188.242 161.35.86.181 167.99.133.28 162.241.114.189 162.241.69.182 185.246.210.169 94.46.15.22 |
| ipv4 | 174.138.42.66 | 0 145.220.25.28 165.227.79.155 161.35.215.189 143.198.62.76 174.138.42.66 46.101.59.235 137.184.69.137 165.227.125.18 |
| ipv4 | 178.128.172.249 | 4.29 149.28.140.81 185.98.87.200 217.138.216.4 142.93.153.4 178.128.172.249 79.165.90.196 51.79.142.118 59.12.193.82 64.39.106.120 64.3 |
| ipv4 | 185.246.210.169 | 161.35.86.181 167.99.133.28 162.241.114.189 162.241.69.182 185.246.210.169 94.46.15.22 69.49.228.92 69.49.235.93 3.83.56.46 141.101.14 |
| ipv4 | 185.254.96.162 | .93 3.83.56.46 141.101.146.162 156.146.50.105 156.146.50.98 185.254.96.162 185.56.80.11 194.126.177.17 192.3.194.202 89.248.173.143 80 |
| ipv4 | 185.56.80.11 | 141.101.146.162 156.146.50.105 156.146.50.98 185.254.96.162 185.56.80.11 194.126.177.17 192.3.194.202 89.248.173.143 80.239.140.67 4 |
| ipv4 | 185.98.87.200 | 38.50 45.86.203.97 27.102.114.78 14.161.74.29 149.28.140.81 185.98.87.200 217.138.216.4 142.93.153.4 178.128.172.249 79.165.90.196 51 |
| ipv4 | 192.3.194.202 | 05 156.146.50.98 185.254.96.162 185.56.80.11 194.126.177.17 192.3.194.202 89.248.173.143 80.239.140.67 47.106.92.240 45.77.138.50 45. |
| ipv4 | 194.126.177.17 | 62 156.146.50.105 156.146.50.98 185.254.96.162 185.56.80.11 194.126.177.17 192.3.194.202 89.248.173.143 80.239.140.67 47.106.92.240 45 |
| ipv4 | 217.138.216.4 | 3.97 27.102.114.78 14.161.74.29 149.28.140.81 185.98.87.200 217.138.216.4 142.93.153.4 178.128.172.249 79.165.90.196 51.79.142.118 59 |
| ipv4 | 27.102.114.78 | 3.143 80.239.140.67 47.106.92.240 45.77.138.50 45.86.203.97 27.102.114.78 14.161.74.29 149.28.140.81 185.98.87.200 217.138.216.4 142. |
| ipv4 | 34.223.64.22 | 2.118 59.12.193.82 64.39.106.120 64.39.98.36 45.155.204.183 34.223.64.22 35.82.51.168 37.237.230.28 44.242.181.147 45.146.164.110 14 |
| ipv4 | 35.82.51.168 | 93.82 64.39.106.120 64.39.98.36 45.155.204.183 34.223.64.22 35.82.51.168 37.237.230.28 44.242.181.147 45.146.164.110 145.220.25.28 1 |
| ipv4 | 37.237.230.28 | 06.120 64.39.98.36 45.155.204.183 34.223.64.22 35.82.51.168 37.237.230.28 44.242.181.147 45.146.164.110 145.220.25.28 165.227.79.155 |
| ipv4 | 3.83.56.46 | 9.182 185.246.210.169 94.46.15.22 69.49.228.92 69.49.235.93 3.83.56.46 141.101.146.162 156.146.50.105 156.146.50.98 185.254.96.162 |
| ipv4 | 44.242.181.147 | 8.36 45.155.204.183 34.223.64.22 35.82.51.168 37.237.230.28 44.242.181.147 45.146.164.110 145.220.25.28 165.227.79.155 161.35.215.189 |
| ipv4 | 45.146.164.110 | .183 34.223.64.22 35.82.51.168 37.237.230.28 44.242.181.147 45.146.164.110 145.220.25.28 165.227.79.155 161.35.215.189 143.198.62.76 1 |
| ipv4 | 45.155.204.183 | 90.196 51.79.142.118 59.12.193.82 64.39.106.120 64.39.98.36 45.155.204.183 34.223.64.22 35.82.51.168 37.237.230.28 44.242.181.147 45.1 |
| ipv4 | 45.77.138.50 | 17 192.3.194.202 89.248.173.143 80.239.140.67 47.106.92.240 45.77.138.50 45.86.203.97 27.102.114.78 14.161.74.29 149.28.140.81 185.9 |
| ipv4 | 45.86.203.97 | 202 89.248.173.143 80.239.140.67 47.106.92.240 45.77.138.50 45.86.203.97 27.102.114.78 14.161.74.29 149.28.140.81 185.98.87.200 217. |
| ipv4 | 46.101.59.235 | 8 165.227.79.155 161.35.215.189 143.198.62.76 174.138.42.66 46.101.59.235 137.184.69.137 165.227.125.18 |
| ipv4 | 47.106.92.240 | 1 194.126.177.17 192.3.194.202 89.248.173.143 80.239.140.67 47.106.92.240 45.77.138.50 45.86.203.97 27.102.114.78 14.161.74.29 149.28 |
| ipv4 | 51.79.142.118 | 00 217.138.216.4 142.93.153.4 178.128.172.249 79.165.90.196 51.79.142.118 59.12.193.82 64.39.106.120 64.39.98.36 45.155.204.183 34.22 |
| ipv4 | 59.12.193.82 | .4 142.93.153.4 178.128.172.249 79.165.90.196 51.79.142.118 59.12.193.82 64.39.106.120 64.39.98.36 45.155.204.183 34.223.64.22 35.82 |
| ipv4 | 64.39.106.120 | .4 178.128.172.249 79.165.90.196 51.79.142.118 59.12.193.82 64.39.106.120 64.39.98.36 45.155.204.183 34.223.64.22 35.82.51.168 37.237 |
| ipv4 | 64.39.98.36 | .249 79.165.90.196 51.79.142.118 59.12.193.82 64.39.106.120 64.39.98.36 45.155.204.183 34.223.64.22 35.82.51.168 37.237.230.28 44.2 |
| ipv4 | 69.49.228.92 | 162.241.114.189 162.241.69.182 185.246.210.169 94.46.15.22 69.49.228.92 69.49.235.93 3.83.56.46 141.101.146.162 156.146.50.105 156. |
| ipv4 | 69.49.235.93 | 189 162.241.69.182 185.246.210.169 94.46.15.22 69.49.228.92 69.49.235.93 3.83.56.46 141.101.146.162 156.146.50.105 156.146.50.98 185 |
| ipv4 | 79.165.90.196 | 81 185.98.87.200 217.138.216.4 142.93.153.4 178.128.172.249 79.165.90.196 51.79.142.118 59.12.193.82 64.39.106.120 64.39.98.36 45.155 |
| ipv4 | 80.239.140.67 | 62 185.56.80.11 194.126.177.17 192.3.194.202 89.248.173.143 80.239.140.67 47.106.92.240 45.77.138.50 45.86.203.97 27.102.114.78 14.16 |
| ipv4 | 89.248.173.143 | 98 185.254.96.162 185.56.80.11 194.126.177.17 192.3.194.202 89.248.173.143 80.239.140.67 47.106.92.240 45.77.138.50 45.86.203.97 27.10 |
| ipv4 | 94.46.15.22 | 67.99.133.28 162.241.114.189 162.241.69.182 185.246.210.169 94.46.15.22 69.49.228.92 69.49.235.93 3.83.56.46 141.101.146.162 156.14 |
Full article694 words · extracted from blog.talosintelligence.com · click to collapse
Thursday, October 7, 2021 15:36
A recently discovered vulnerability in Apache HTTP Server (CVE-2021-41733) is being actively exploited in the wild.
This vulnerability is a path traversal and file disclosure vulnerability that could allow an attacker to map URLs outside of the document root. It could also result in the exposure of the source of interpreted files like CGI scripts. The exploitation of this vulnerability is of very low complexity and poses a critical threat to all users of this open-source software.
This particular vulnerability was introduced in a recent version of Apache (2.4.49). Users running older versions of Apache are not currently affected. The fix for CVE-2021-41733 in 2.4.50 was found to be insufficient, leading to a second, new vulnerability (CVE-2021-42013) that Apache is now reporting. As a result, version 2.4.51 was released to fully address the issue. Users are recommended to upgrade to 2.4.51 as soon as possible. According to data available on Shodan, only a small number of Apache installations are actually running 2.4.49 or 2.4.50, meaning less than 1 percent of the overall Apache install base could be affected.
Active Exploitation
In response to this vulnerability, Cisco Talos released coverage for Cisco Secure products, including Cisco Secure Firewall with Snort rule 58276 (Snort 3 SID 300053). Upon deploying the signature, we immediately saw exploitation activity coming from a variety of addresses. Since this is primarily a path traversal bug, the majority of the exploitation we see is focused on two specific paths: /etc/passwd and /bin/sh. These would make sense, as attackers are going to try and leverage this for access by accessing credentials or obtaining direct access to a shell. Below are a few examples of common requests we are seeing:
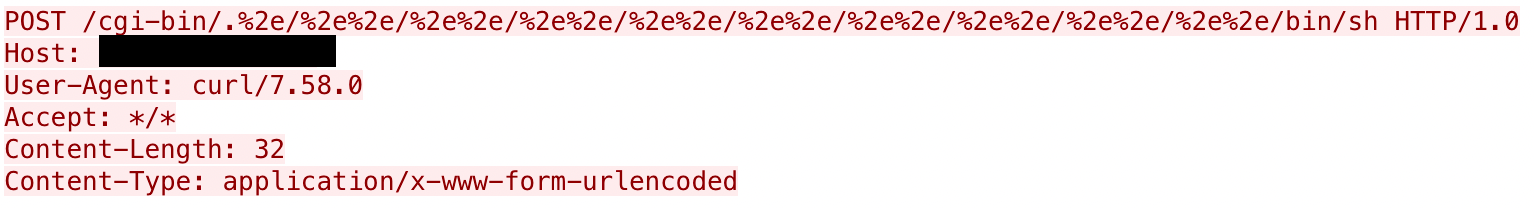
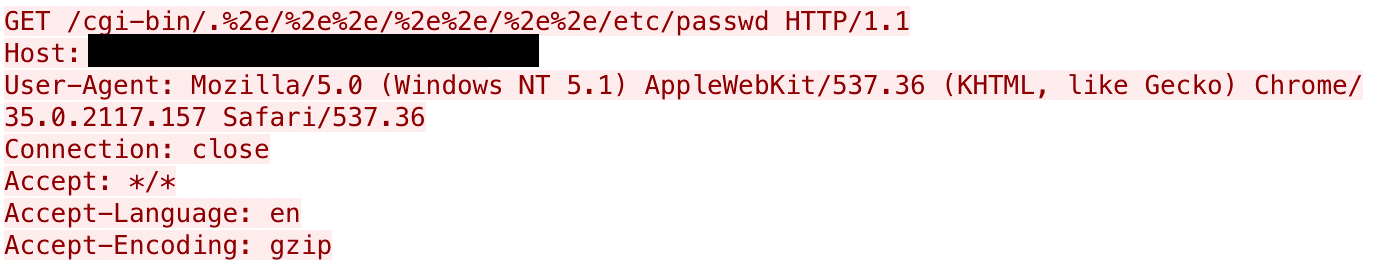
These two pcaps show the most common targets we've seen of the path traversal vulnerability and the most common approaches to user agents for the activity. The majority of the activity is using cURL as the user agent, but we have seen other activity that is focused on using various common user agents, including the one shown above.
However, this is not an exhaustive list of paths being targeted. We have seen other paths being probed by attackers including /etc/services and /etc/hosts, examples of which are shown below.


There appear to be several different groups of actors exploiting this vulnerability. Some are just scanners that appear to be scanning for potentially vulnerable hosts. Others appear to be iterating through a large list of domains with varying generic HTTP scanning leveraging this vulnerability. And there's another group operating at a much lower volume that are keenly interested in this specific vulnerability.
Conclusion
Internet-facing servers are always at increased risk of exploitation and web servers are historically a popular target. Apache is a popular web server that has a large install base. This vulnerability was only recently disclosed and the amount of exploitation in the wild points to it being a popular target for adversaries despite having a potentially small attack surface. As such, affected customers should apply the 2.4.51 patch as soon as possible to mitigate any potential issues.
The activity seems to include those that are performing wide scale scanning as well as others experimenting and working to implement mechanisms to exploit it. The low complexity of this exploit allows for automated exploitation to be easily implemented by an attacker.
Coverage
Ways our customers can detect and block this threat are listed below.

Open-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org. Snort SID 58276 (Snort 3 SID 300053) has been released to address this vulnerability.
Cisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.
Indicators of compromise (IoCs)
IP Addresses:
134.122.112.12
143.198.136.88
161.35.188.242
161.35.86.181
167.99.133.28
162.241.114.189
162.241.69.182
185.246.210.169
94.46.15.22
69.49.228.92
69.49.235.93
3.83.56.46
141.101.146.162
156.146.50.105
156.146.50.98
185.254.96.162
185.56.80.11
194.126.177.17
192.3.194.202
89.248.173.143
80.239.140.67
47.106.92.240
45.77.138.50
45.86.203.97
27.102.114.78
14.161.74.29
149.28.140.81
185.98.87.200
217.138.216.4
142.93.153.4
178.128.172.249
79.165.90.196
51.79.142.118
59.12.193.82
64.39.106.120
64.39.98.36
45.155.204.183
34.223.64.22
35.82.51.168
37.237.230.28
44.242.181.147
45.146.164.110
145.220.25.28
165.227.79.155
161.35.215.189
143.198.62.76
174.138.42.66
46.101.59.235
137.184.69.137
165.227.125.18
Text extracted automatically; images, tables and formatting may be missing. Original: https://blog.talosintelligence.com/apache-vuln-threat-advisory/