Wyden seeks upgraded NSA security guidance on commercial VPN use
Senator Ron Wyden asked the NSA to update public guidance on commercial VPN security risks and answer questions about foreign surveillance threats against single-hop VPNs.
Sen. Ron Wyden sent a letter to NSA Director Gen. Joshua Rudd urging the agency to revise public guidance on commercial VPNs, following earlier letters to federal agencies in March and July. He argues single-hop VPNs offer little protection against sophisticated adversaries able to compel or compromise the single provider, citing a Congressional Research Service paper favoring multi-hop and mixnet architectures. The letter references a September NSA advisory on a China-sponsored campaign against telecom, government and military networks and asks unclassified questions about multi-hop systems such as Apple Private Relay, Tor and Nym versus mixnets.
- Wyden says consumer VPNs are marketed as privacy shields but insufficient against state adversaries
- Letter cites CRS findings that multi-hop and mixnet architectures mitigate single-provider compromise
- NSA asked to update VPN configuration guidance issued after China-linked telecom intrusions
- Questions posed on effectiveness of Apple Private Relay, Tor and Nym
Full article799 words · extracted from cyberscoop.com · click to collapse
Skip to main content
Get our latest cybersecurity news first on Google.
Click here!
it’s the latest in a sequence of letters to feds from Sen. Ron Wyden, D-Ore., on commercial VPNs.
Listen to this article
0:00
Learn more.
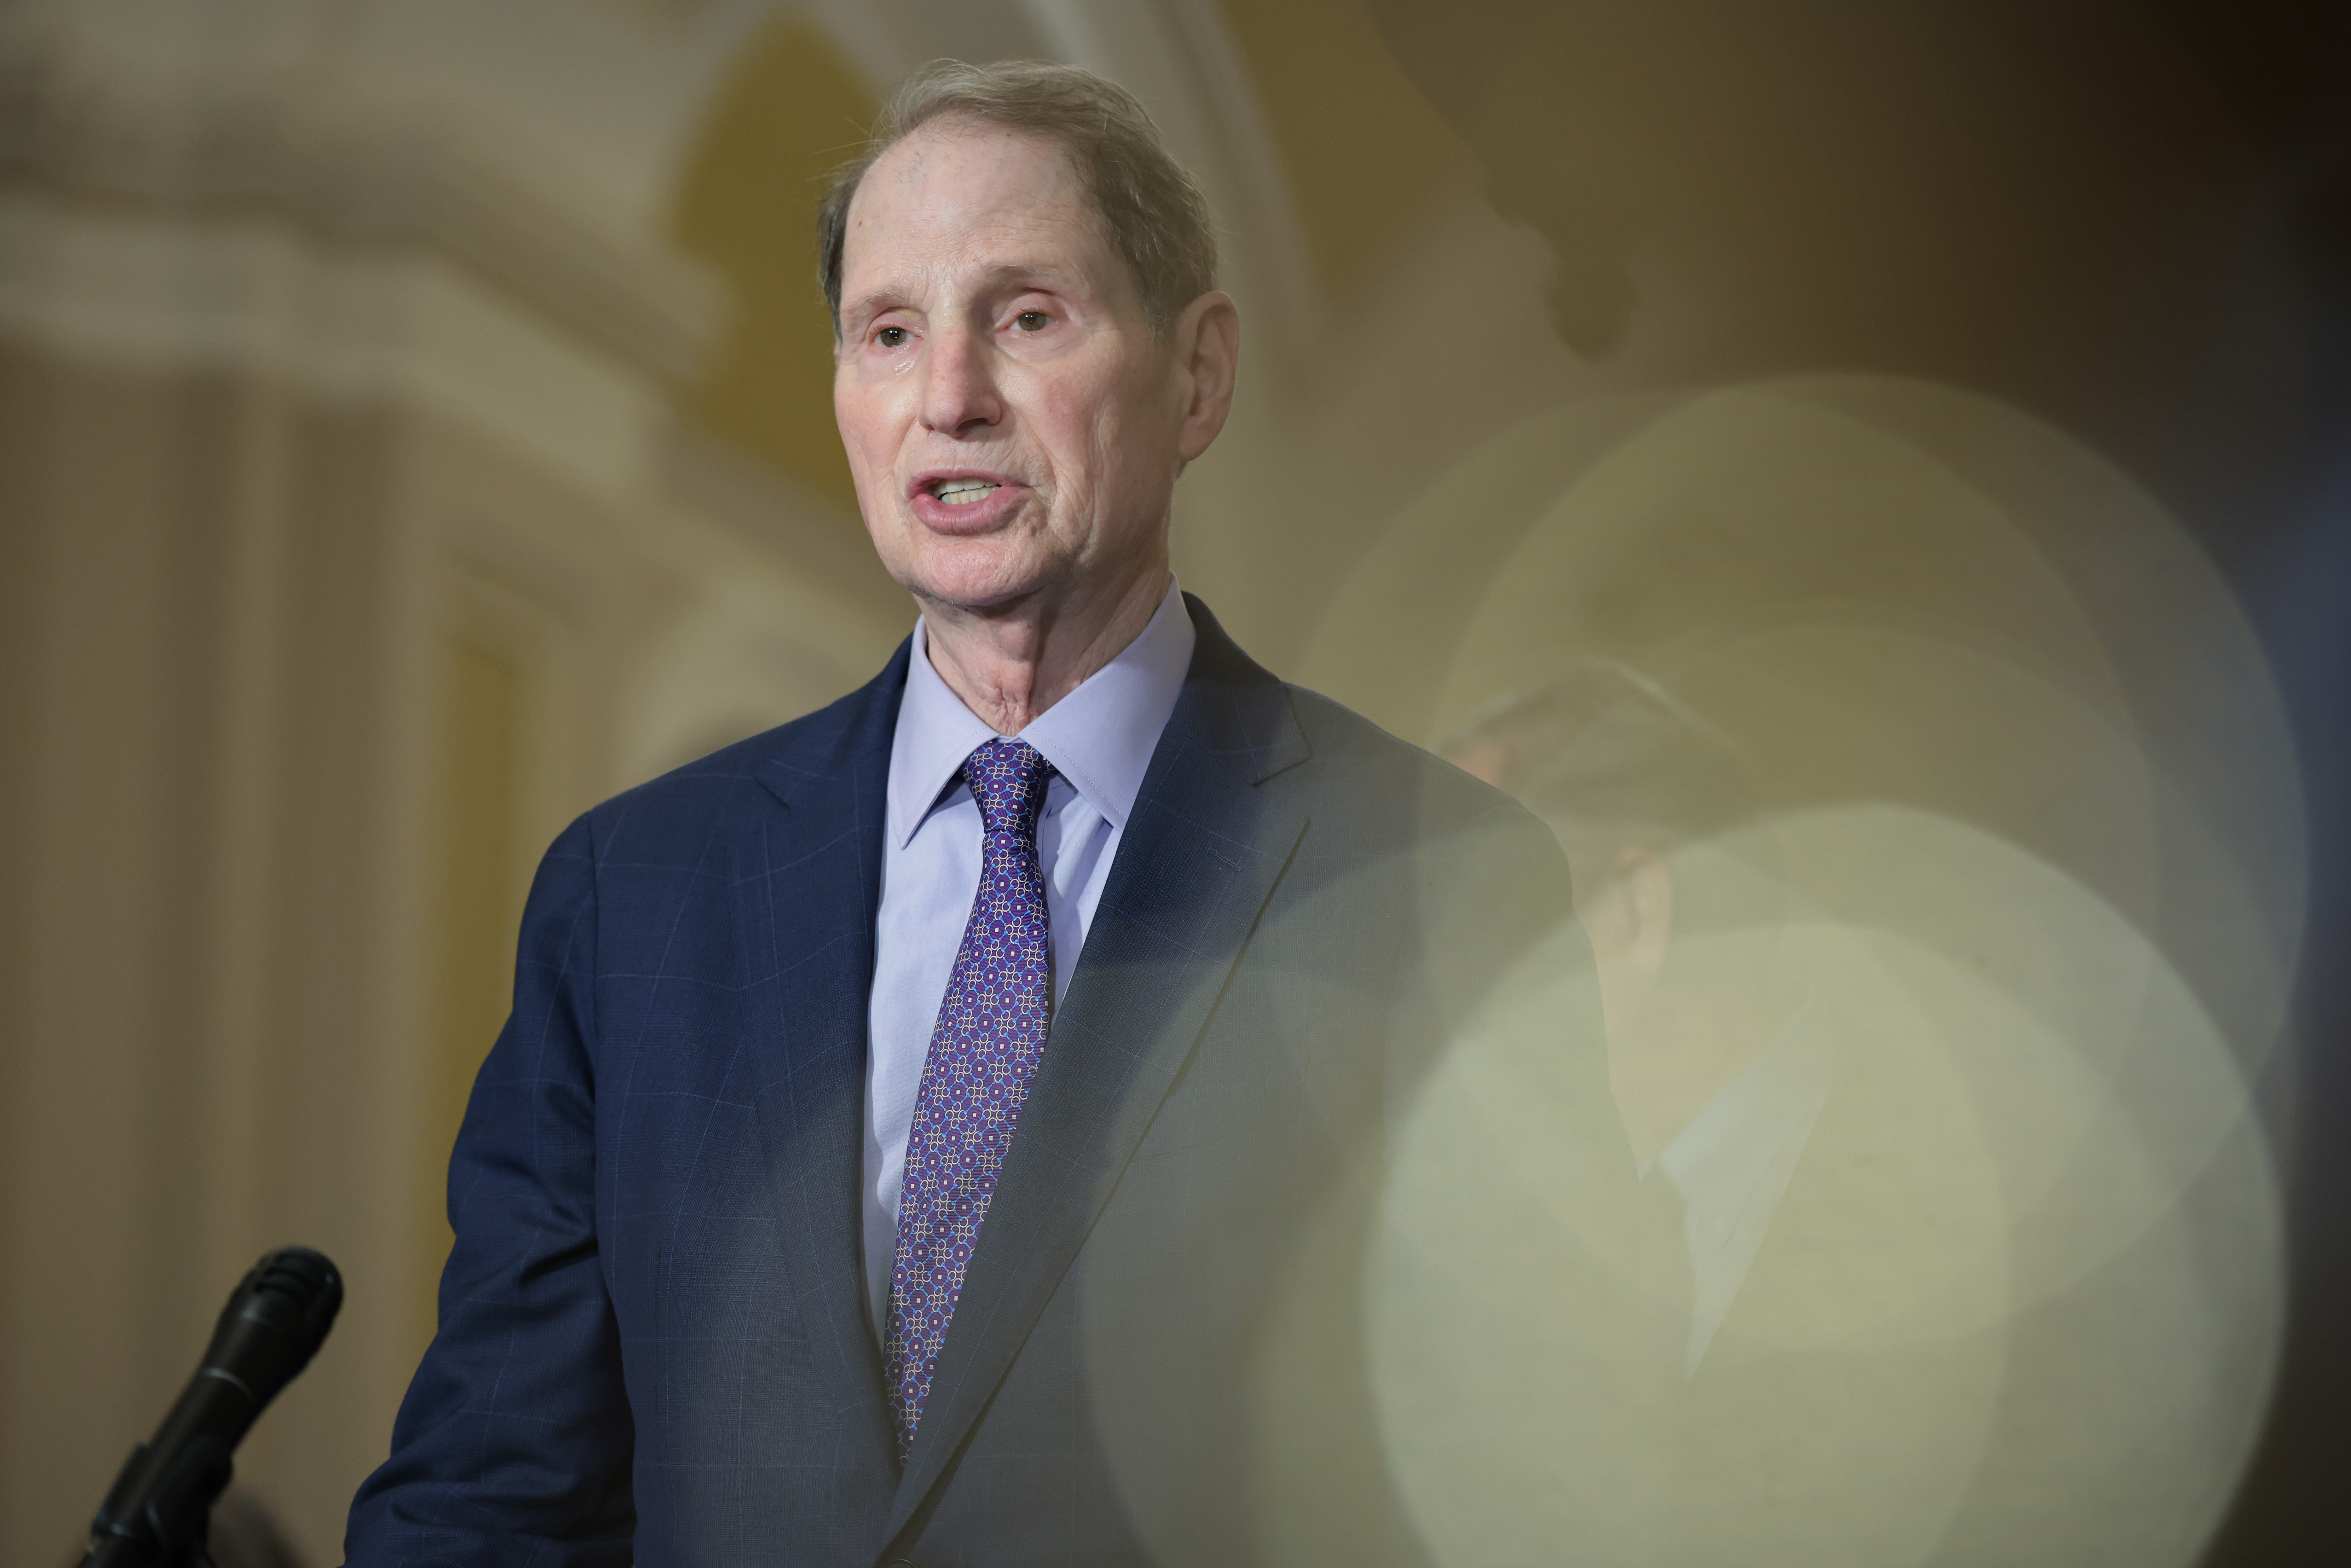
Sen. Ron Wyden, D-Ore., speaks to reporters following the weekly Democrat Senate policy luncheon at the U.S. Capitol on May 6, 2025. (Photo by Kayla Bartkowski/Getty Images)
Sen. Ron Wyden, D-Ore., is asking the National Security Agency to update public guidance on the security risks associated with commercial virtual private networks, and to answer questions about foreign surveillance threats against standard VPNs.
In a letter to NSA Director Gen. Joshua Rudd that Wyden sent Wednesday, the senator continued his push to warn about standard, commercial VPNs, following letters to federal agency leaders in March and July .
“While commercial Virtual Private Networks (VPNs) are recommended by federal agencies and widely marketed as shields against online spying, standard consumer VPNs do not sufficiently protect users from sophisticated adversaries,” Wyden wrote in the letter, first reported by CyberScoop. “Other, more secure alternatives are widely available.”
Wyden took aim at “single-hop” VPNs that routes data through one server before arriving at the destination.
He cited a Congressional Research Service paper from last month that said “a single-hop VPN, however strongly encrypted, offers essentially no protection against an adversary who can compel… or infiltrate that one provider,” compared to “multi-hop and mixnet architectures [that] directly target and mitigate this weakness” since a second server only knows the IP address of the first server.
He also cited a letter responding to an earlier missive that Wyden signed with other lawmakers in an exchange with the Office of the Director of National Intelligence. The office offered a note of caution about scrutinizing VPN providers’ privacy and security policies, but Wyden said “it overlooked the importance of the VPN service’s architecture against sophisticated foreign threats.”
Wyden referenced an advisory from the NSA and allied foreign governments last September about a China-sponsored campaign to target telecommunications, government and military networks.
He said that the NSA should update its public guidance on VPN configuration.
“Americans facing advanced foreign threats — including government personnel, defense contractors, journalists, and human rights defenders — deserve clear, honest advice about how best to protect their communications from surveillance by foreign adversaries.
He also asked Rudd to answer a series of questions in an unclassified reply. Some view single-hop commercial VPNs as sufficient for average internet users , and Wyden asked whether they were strong enough to protect “Americans’ sensitive digital footprints against foreign adversaries capable of monitoring internet backbones.”
And Wyden wants Rudd to weigh in on the importance and effectiveness of multi-hop anti-surveillance systems, like Apple Private Relay, Tor and Nym, as well as how multi-hop proxy systems fare against mixnet architectures.
You can read the full letter below.
More Scoops
Sen. Ron Wyden, D-Ore., leaves a Senate Democratic meeting at the U.S. Capitol Building on Oct. 3, 2025. (Photo by Kevin Dietsch/Getty Images)
Sen. Wyden urges feds to discard older, insecure, public-facing VPNs
In a letter first reported by CyberScoop, Ron Wyden, D-Ore., said ‘devastating’ attacks on the federal government have accumulated due to the tech.
U.S. Sen. Ron Wyden, D-Ore., walks to the Senate Chambers in the U.S. Capitol Building on July 28, 2025. (Photo by Anna Moneymaker/Getty Images)
Blistering Wyden letter seeks review of federal court cybersecurity, citing ‘incompetence,’ ‘negligence’
Sen. Ron Wyden, D-Ore., talks with reporters as he leaves the U.S. Capitol following the first vote of the week on June 17. (Photo by Chip Somodevilla/Getty Images)
Wyden legislation would mandate FCC cybersecurity rules for telecoms
Latest Podcasts
Government
Jail time for Maine child in 764 marks turning point in federal law enforcement
FCC proposes public scorecard to rate telecoms on anti-robocall efforts
Dogged Russia-based botnet dismantled after 23-year run
FBI raises alarm over deceptive phishing campaign targeting prominent people
Technology
Pegasus, NoviSpy variant spyware found on devices of Serbian activists
The Collective Cyber Defense letter wrote your next vendor questionnaire
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
The GTA VI leaks are breaking the internet. Security researchers have seen this before.
Threats
McKesson copes with fallout from data theft extortion attack
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
ATF confirms cyberattack hit system containing info on its investigation targets
Unit 42 warns AI has shifted balance of power from defenders to attackers
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Election official says Tina Peters would be consultant, won’t have access to election systems
Bipartisan Senate bill aims to prepare energy sector for Q-Day
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/wyden-nsa-commercial-vpn-security-guidance/