New RomCom Backdoor Targets Female Political Leaders
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2023-36884 | Race Condition RCE in Microsoft Windows Search CVE-2023-36884 is a race condition (TOCTOU) vulnerability in Microsoft Windows Search that permits remote code execution, rated 7.5 (high) on CVSS 3.1. It is triggered over the network with user interaction — for example, when a user opens or interacts with a specially crafted document that causes the vulnerable search code path to race, allowing arbitrary code execution in the context of the current user. An attacker gains code execution on the victim's Windows system, which the RomCom threat actor chained with Firefox flaws to deploy backdoors against political targets, and CISA notes known ransomware use. Virtually every supported Windows client and server release at the time is affected, spanning Windows 10 1507 through 22H2, Windows 11 21H2/22H2, and Windows Server 2008 through 2022. The flaw was actively exploited as a zero-day before being fixed in the July 2023 Patch Tuesday; it was added to the CISA KEV catalog on 2023-07-17 and carries a 98.9% EPSS score (100th percentile). Do: Apply the July 2023 Patch Tuesday Windows security updates to all Windows 10, Windows 11, and Windows Server systems, prioritizing high-value and frequently attacked endpoints since the bug was exploited as a zero-day by RomCom and carries a KEV deadline (US civilian agencies were directed to remediate by August 1, 2023). Because exploitation requires user interaction, caution users against opening untrusted documents, and verify patch status via your patch management or vulnerability scanner against the KEV requirement. If patching is not possible, follow vendor mitigations per CISA's required action or discontinue use. | 7.5 | 99% | KEV ransomware |
| mass≈1 billion+ Windows devices (Windows 10/11 installed base) plus the enterprise Windows Server estate |
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | wplsummit.com | gle Drive folder containing photographs from the event, the wplsummit[.]com fake website directed visitors to a OneDrive folder conta |
Full article490 words · extracted from infosecurity-magazine.com · click to collapse
Japanese cybersecurity provider Trend Micro has uncovered a new malicious campaign targeting female political leaders and attendees of the Women Political Leaders (WPL) Summit held in Brussels in June 2023.
The treat actors, Void Rabisu, started deploying a new version of its RomCom backdoor – which Trend Micro tracks as RomCom 4.0 and Microsoft as Peapod – in early August 2023, Trend Micro reported in a malware analysis published on October 13.
The backdoor payload was hidden in a malicious copy of the official website of the WPL Summit, which aims to improve gender equality in politics.
“While the ‘Videos & photos’ link of the legitimate domain redirects visitors to a Google Drive folder containing photographs from the event, the wplsummit[.]com fake website directed visitors to a OneDrive folder containing two compressed files and an executable called Unpublished Pictures 1-20230802T122531-002-sfx.exe. The latter file appears to be a piece of malware,” reads the Trend Micro report.
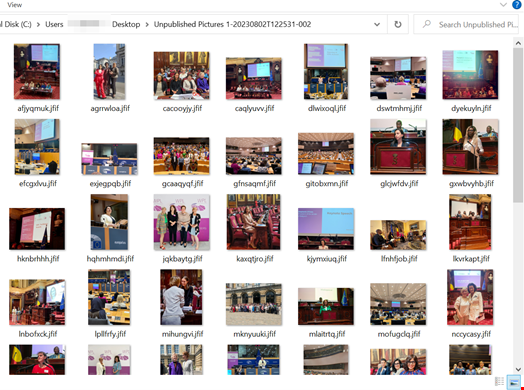
This tactic is similar to a previous Void Rabisu campaign in June, where the group used the Ukrainian World Congress and the July 2023 NATO summit as lures to deploy a zero-day exploit based on the CVE-2023-36884 vulnerability, a remote code execution flaw in Office and Windows HTML. This campaign was reported by Microsoft in July.
Additionally, Trend Micro noted that Void Rabisu is using a new technique in its latest campaigns that has not previously been reported on.
The technique involves a TLS-enforcing technique by the RomCon command-and-control (C2) servers that can render the automated discovery of RomCom infrastructure more difficult.
“We observed Void Rabisu using this technique in a May 2023 RomCom campaign that spread a malicious copy of the legitimate PaperCut software, in which the C2 server ignored requests that were not conformant,” reads the Trend Micro analysis.
Who Is Void Rabisu?
Void Rabisu, also known as Storm-0978, Tropical Scorpius, and UNC2596, is a hybrid threat actor conducting financially motivated and espionage attacks.
The group was first identified in early 2022 but is believed to have been active for longer than that.
It was initially considered a financially motivated threat actor because of its associated Cuba ransomware.
However, in August 2022, Cuba ransomware was involved in an attack targeting the parliament of Montenegro. This led security researchers to assume the group was pursuing a geopolitical agenda.
This hypothesis was later confirmed as Void Rabisu started targeting the Ukrainian government and military, their energy and water utility sectors as well as EU politicians and government spokespersons.
"Void Rabisu is one of the clearest examples where we see a mix of the typical tactics, techniques, and procedures (TTPs) used by cybercriminal threat actors and TTPs used by nation-state-sponsored threat actors motivated primarily by espionage goals," Trend Micro said.
Read more: Void Rabisu's RomCom Backdoor Reveals Shifting Threat Actor Goals
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.infosecurity-magazine.com/news/romcom-backdoor-female-political/