Exposed DarkSword iOS Servers Reveal Crypto Wallet Theft From Compromised iPhones
Censys-exposed DarkSword/Coruna servers reveal an iOS exploitation-as-a-service platform stealing crypto wallet secrets, including 11 victim recovery phrases.
Censys uncovered five exposed servers running a DarkSword/Coruna iOS exploitation platform, including exploit_server.py, the darksword.db database, wallet injection modules, and reseller/agent controls. A production-server capture contained 11 victim BIP39 recovery phrases, 179 device loot directories, and 75 control-plane accounts, with telemetry showing iPhones running iOS 16.1 and 16.3.1 polling a watering-hole beacon every three seconds. Eighteen modules inject into wallet apps including MetaMask, Phantom, Trust Wallet, Coinbase, Exodus, and imToken to steal secrets; development files reference CVE-2026-31001, a JavaScriptCore type-confusion flaw targeting iOS 26, though no deployed iOS 26 chain was demonstrated.
- Five exposed servers revealed a full DarkSword/Coruna iOS exploitation and C2 platform.
- 18 wallet-theft modules inject into MetaMask, Phantom, Trust Wallet, Coinbase and more.
- Production capture held 11 victim recovery phrases; infrastructure active during September.
- Operation runs as commercial exploitation-as-a-service; no named actor attribution.
- CVE-2026-31001 referenced, but no deployed iOS 26 exploit chain demonstrated.
Vulnerabilities mentionedAll →
- published —
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2026-31001 | NVD description · AI analysis pending | — | — | — | — | — |
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | 66ds.lol | esearchers also identified 22 samples from infections using 66ds[.]lol, a separate Cloudflare-fronted C2 . These builds preserve |
Full article632 words · extracted from gbhackers.com · click to collapse
Exposed directories on five servers have revealed an operational DarkSword/Coruna exploitation platform built to compromise iPhones and harvest cryptocurrency wallet secrets.
Censys researchers uncovered delivery infrastructure, implants, wallet injection modules, and reseller controls.
At the same time, a separate production-server capture contained 11 victim recovery phrases, 179 device loot directories, and 75 control-plane accounts. The infrastructure remained active during September triage.
The five hosts surfaced between September 15 and 17, exposing a packaged DS-Fusion release, operational telemetry, an analysis workspace, Coruna staging files, and a complete command-and-control platform.
At 156.239.230[.]120:8080, researchers recovered exploit_server.py, a FastAPI administration application, and the darksword.db database.
The platform automatically registers devices, distributes exploit stages, queues commands, and organizes exfiltrated content.
Its agent model includes commission rates, device quotas, and separate delivery channels, while an integrated parser searches harvested files for BIP39 recovery phrases and cryptocurrency addresses.
These features expose the business machinery behind the attacks.
Censys investigation connects the exposed systems, through identical Coruna payloads, Chinese-language administration panels, and shared harvesting components.
Censys Researchers said that, the operation as commercial exploitation-as-a-service, although they cannot attribute the cluster to a named actor.
Exposed DarkSword iOS Servers
Telemetry from 166.88.95[.]90 showed two iPhones running iOS 16.1 and 16.3.1 polling a watering-hole beacon every three seconds for hours on September 6.
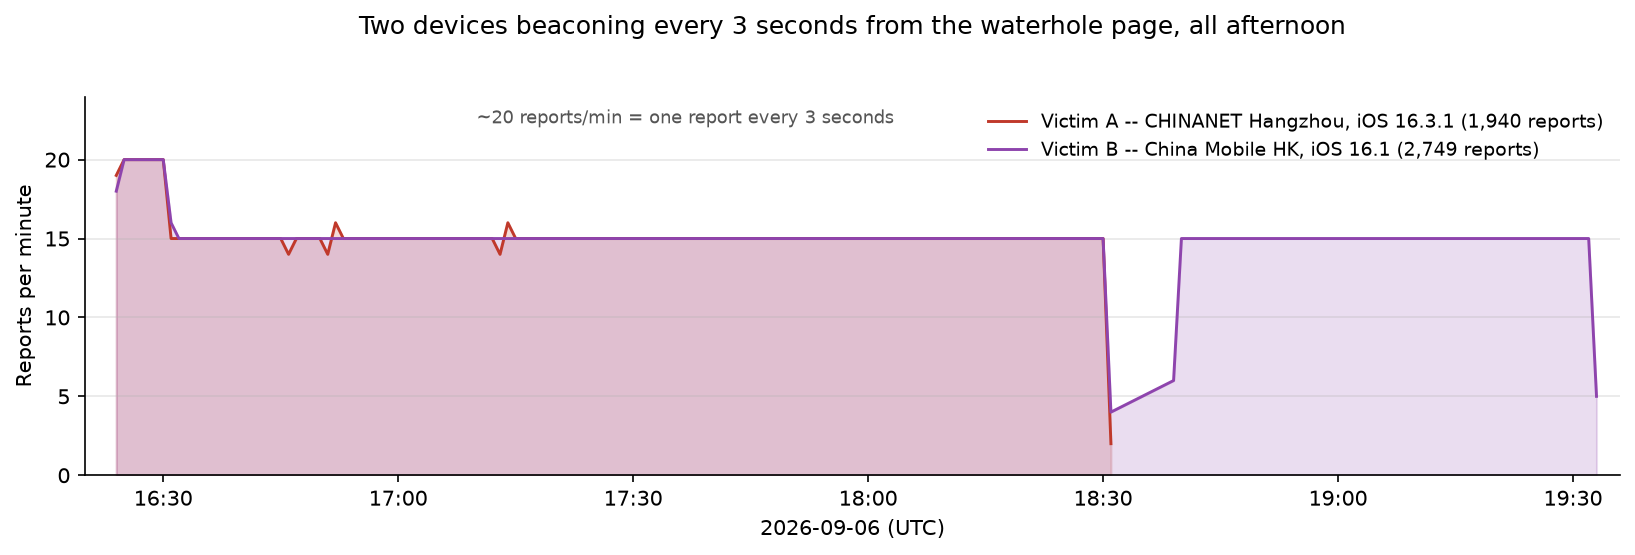
However, two initially suspicious exfiltration files on another host were only test-device reports, not stolen victim content.
After exploitation obtains kernel memory access, the recovered platform loads bootstrap.dylib, stage2.dylib, and the core_v6.dylib implant.
A SpringBoard coordinator disguised as future-destroy.htm watches wallet applications launch and injects matching theft modules into their running processes.
Eighteen modules target applications including MetaMask, Phantom, Trust Wallet, Coinbase, Exodus, and imToken.
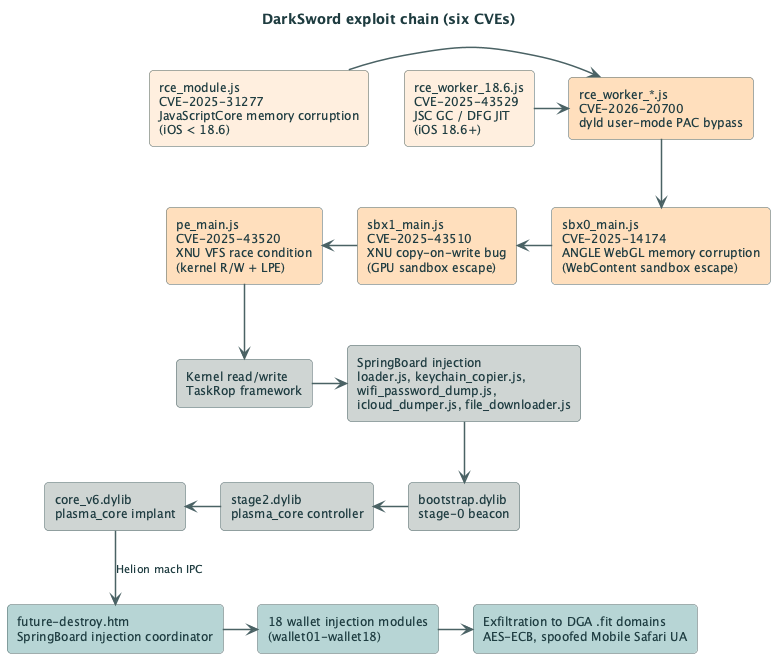
The implant also searches photos and Notes for BIP39 mnemonics, transmitting only phrases that pass checksum validation.
Shared module infrastructure includes an embedded AES key, domain-generation fallbacks, separate exfiltration endpoints, and disabled TLS certificate validation.
The production capture provides evidence of theft, including 12-word recovery phrases associated with six wallet brands.
Nevertheless, its provenance remains unexplained, and the 179 loot directories should not be treated as a verified count of unique victims.
Researchers also identified 22 samples from infections using 66ds[.]lol, a separate Cloudflare-fronted C2. These builds preserve the shared wallet framework but substitute their own fallback address.
BitKeep modules expand the observed targeting to a nineteenth wallet application; certificate pivots connect this operator to Tencent and Shenyang infrastructure.
The exposed development files reference CVE-2026-31001, described by Censys as a JavaScriptCore type-confusion vulnerability targeting iOS 26.
However, companion sandbox-escape and kernel-privilege stages remain placeholders. The findings do not demonstrate a deployed iOS 26 exploit chain or active zero-day exploitation.
Google’s March analysis documented DarkSword’s six-vulnerability chain targeting iOS 18.4–18.7, distinct from older Coruna coverage.
Censys’s July panel-sprawl investigation demonstrated why stable panel fingerprints outperform rapidly changing domains for infrastructure tracking.
Google recommends updating to the latest iOS release and enabling Lockdown Mode when updates are unavailable.
Censys reports its detection coverage matched all 347 unique Mach-O binaries in the recovered sample set, supporting broader signature-based hunting beyond individual payload hashes.
IOCs
| IP | Port | Hosting | First seen |
43.134.165[.]205 | 9999 | Tencent Cloud | 2026-09-15 |
166.88.95[.]90 | 9999 | Evoxt (Japan) | 2026-09-15 |
23.148.212[.]237 | 8888 | (unknown) | 2026-09-15 |
47.102.192[.]23 | 9876 | Alibaba Cloud | 2026-09-15 |
156.239.230[.]120 | 8080, 80 | (unknown) | 2026-09-16 |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.