Check Point warns of Management Server zero-day exploited in attacks
Check Point patched CVE-2026-93616, an exploited unauthenticated Management Server zero-day.
Check Point released emergency hotfixes for CVE-2026-93616, a path-traversal flaw in Security Management Server that lets unauthenticated attackers upload and execute arbitrary scripts. The company said the vulnerability is exploited in the wild and that a handful of customers were attacked. Affected products include Security Management, Multi-Domain Management, Log Server, Multi-Domain Log Server, and SmartEvent; customers who cannot patch immediately should limit access to trusted IPs. The article also recounts other Check Point bugs, including CVE-2024-24919, CVE-2026-50751, CVE-2026-16232, CVE-2026-85102, and CVE-2026-85103.
- CVE-2026-93616 allows unauthenticated script upload and execution.
- Check Point says a handful of customers were attacked.
- Hotfix covers R82.20 management, log, and SmartEvent products.
- Trusted-client IP restrictions are advised if patching is delayed.
- The report also cites other exploited Check Point flaws.
Vulnerabilities mentionedAll →
- CVE-2024-249198.6100%Information Disclosure in Internet-Facing Check Point Quantum Security Gatewayspublished · Check Point Quantum Security Gateways KEV ransomware
Full article501 words · extracted from bleepingcomputer.com · click to collapse
Check Point Software released emergency hotfixes to address a critical Security Management Server vulnerability that could let attackers run arbitrary scripts.
The Security Management Server is a central repository that stores and manages security policies, processes administrator changes, and collects system logs across enterprise networks.
Tracked as CVE-2026-93616, this path traversal flaw lets unauthenticated threat actors upload arbitrary scripts on vulnerable Check Point Management Servers and execute them in low-complexity attacks.
The Cybersecurity and Infrastructure Security Agency (CISA) and the FBI have urged software companies since May 2024 to remove path traversal weaknesses from their products before shipping, saying such security issues "have been called 'unforgivable' since at least 2007."
Check Point has addressed the vulnerability in R82.20 Security Hotfix and said that the complete list of affected products includes Security Management Server, Multi-Domain Security Management Server, Log Server, Multi-Domain Log Server, and SmartEvent.
"This vulnerability is exploited in the wild. Check Point is aware of a handful of customers who have been attacked," the company warned, while advising security teams to check their networks for evidence of successful exploitation using the indicators of compromise shared in this security advisory.
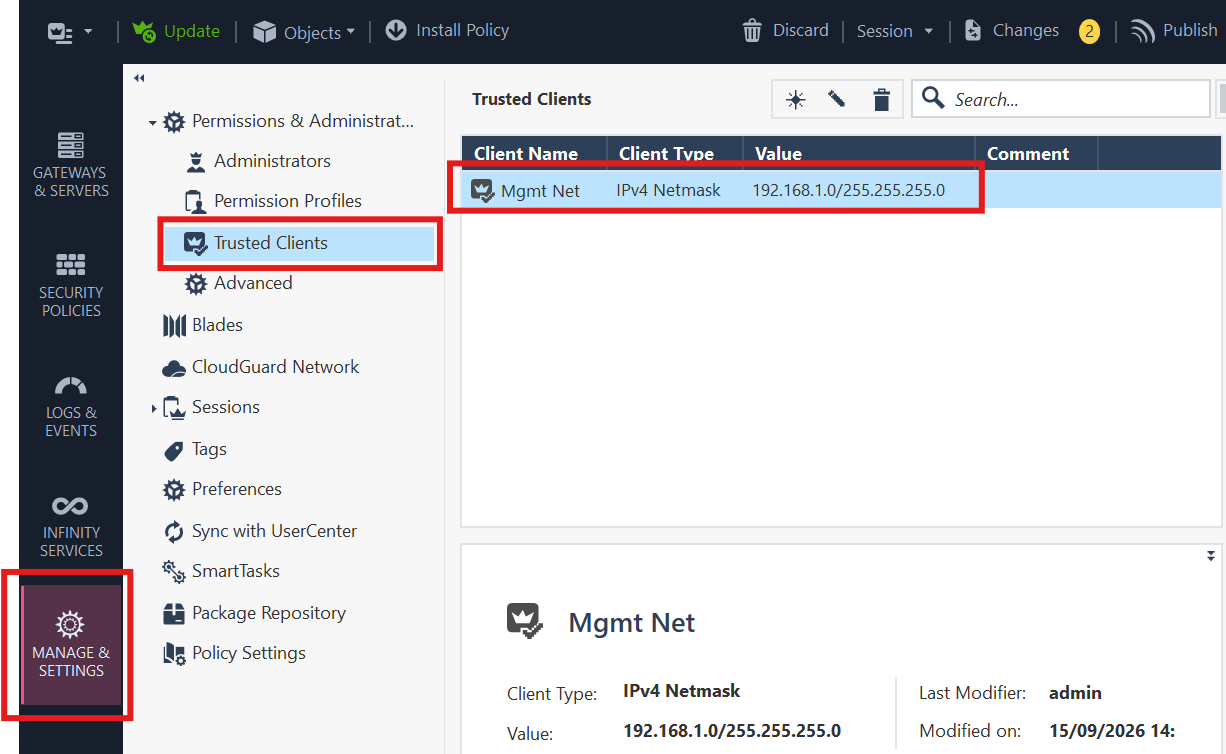
Check Point also provides temporary mitigation measures for customers who can't immediately deploy the hotfix on vulnerable systems, including hardening vulnerable systems against attacks by placing them behind a firewall and limiting access to trusted IP addresses from Manage & Settings > Permissions & Administrators > Trusted Clients in the SmartConsole dashboard.
In recent months, Check Point has warned customers that other flaws were being actively exploited in the wild.
For instance, two years ago, CISA flagged a flaw (CVE-2024-24919) in Check Point's Quantum Security Gateways as actively exploited by ransomware gangs, confirming an Orange Cyberdefense CERT report linking these attacks to NailaoLocker ransomware.
Qilin ransomware affiliate has also exploited an authentication bypass (CVE-2026-50751) zero-day since June, while a second auth bypass zero-day (CVE-2026-16232) has been exploited since at least July to authenticate with administrator privileges to SmartConsole admin panels.
Two weeks ago, the Dutch National Cyber Security Centre (NCSC-NL) also warned organizations to urgently patch two critical Check Point VPN flaws (CVE-2026-85102 and CVE-2026-85103) because it "expects exploitation attempts to occur soon."
More recently, on Friday, Check Point released security updates to address another critical authentication bypass (CVE-2026-16232) in the login process for Security Management Server and Security Gateways that lets attackers execute code with root privileges on management systems.
While the company has not yet flagged CVE-2026-16232 as actively exploited, it said security teams can identify attacks by looking for "Administrator failed to log in: Username too long" alerts in the Audit and Admin login logs.
Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.