PoeLLM Malware Hijacks 3,400+ Servers for Crypto Mining and Botnet Expansion
PoeLLM has compromised over 3,400 servers, mining cryptocurrency and spreading through exposed AI and web apps.
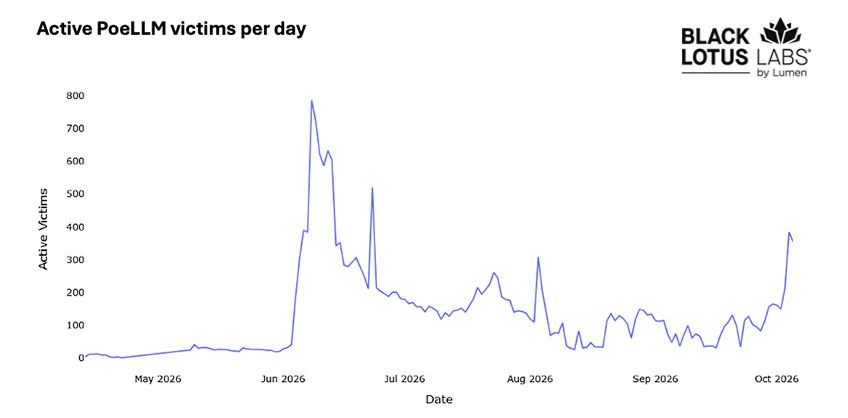
PoeLLM, active since April 2026, has compromised more than 3,400 servers, mainly in the United States and Western Europe, by abusing exposed LiteLLM, Ollama, Gotenberg, Gitea, and possibly Ivanti Sentry systems. Operators derive command-and-control addresses from a poem hosted on GitHub, and infected hosts run XMRig and Iron miners while scanning and exploiting further machines. One sample used LiteLLM authenticated command-execution flaw CVE-2026-42271, which version 1.83.7 fixes. Peak activity exceeded 800 servers a day, and Lumen said it blocked traffic to identified command servers.
- More than 3,400 servers compromised since April 2026, peaking above 800 daily.
- Command servers are decoded from words in a GitHub-hosted poem.
- CVE-2026-42271 allows authenticated command execution in LiteLLM before 1.83.7.
- Payloads add remote shells, scanners, and XMRig and Iron miners.
- Lumen blocked traffic to identified PoeLLM command servers.
Vulnerabilities mentionedAll →
- CVE-2026-422718.793%Command Injection in BerriAI LiteLLM AI Gateway Exploited in the Wildpublished · BerriAI LiteLLM (proxy server / AI Gateway) KEV
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2026-42271 | Command Injection in BerriAI LiteLLM AI Gateway Exploited in the Wild CVE-2026-42271 is a command injection (CWE-77/CWE-78) in BerriAI LiteLLM's proxy server, a widely used AI gateway for calling LLM APIs. Two MCP preview endpoints (POST /mcp-rest/test/connection and POST /mcp-rest/test/tools/list) accept a full stdio server configuration, including command, args, and env fields, and spawn the supplied command as a subprocess on the proxy host; the endpoints are gated only by any valid proxy API key with no role check, so even low-privilege internal-user keys can trigger it. An attacker with any authenticated key gains arbitrary command execution with the privileges of the proxy process, and reporting indicates attackers are chaining the flaw into broader takeover of AI gateway servers, including reverse shells and crypto miners, in some cases via weak or default keys such as the example 'sk-1234' admin key. Any organization running LiteLLM versions 1.74.2 through before 1.83.7, including LiteLLM distributed with Red Hat OpenShift AI, is affected. The flaw was added to CISA's Known Exploited Vulnerabilities catalog on 2026-06-08 and is under active attack, with a very high EPSS of 83.6% for exploitation within 30 days. |
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| ipv4 | 120.224.114.212 | 2026 May 16, 2026 89.39.253.46 April 14, 2026 June 24, 2026 120.224.114.212 May 9, 2026 September 8, 2026 5.78.73.122 June 8, 2026 Augu |
| ipv4 | 15.204.178.28 | September 8, 2026 5.78.73.122 June 8, 2026 August 22, 2026 15.204.178.28 June 14, 2026 August 17, 2026 92.119.165.74 July 1, 2026 Ju |
| ipv4 | 191.37.28.160 | le conversion services. IOCs IP Address Start Date End Date 191.37.28.160 April 13, 2026 May 16, 2026 89.39.253.46 April 14, 2026 Jun |
| ipv4 | 5.78.73.122 | June 24, 2026 120.224.114.212 May 9, 2026 September 8, 2026 5.78.73.122 June 8, 2026 August 22, 2026 15.204.178.28 June 14, 2026 Au |
| ipv4 | 89.39.253.46 | art Date End Date 191.37.28.160 April 13, 2026 May 16, 2026 89.39.253.46 April 14, 2026 June 24, 2026 120.224.114.212 May 9, 2026 Se |
| ipv4 | 92.119.165.74 | August 22, 2026 15.204.178.28 June 14, 2026 August 17, 2026 92.119.165.74 July 1, 2026 July 23, 2026 Note: IP addresses and domains a |
Full article694 words · extracted from gbhackers.com · click to collapse
A cryptocurrency mining campaign dubbed PoeLLM has compromised more than 3,400 servers by targeting exposed AI infrastructure and other internet-facing applications.
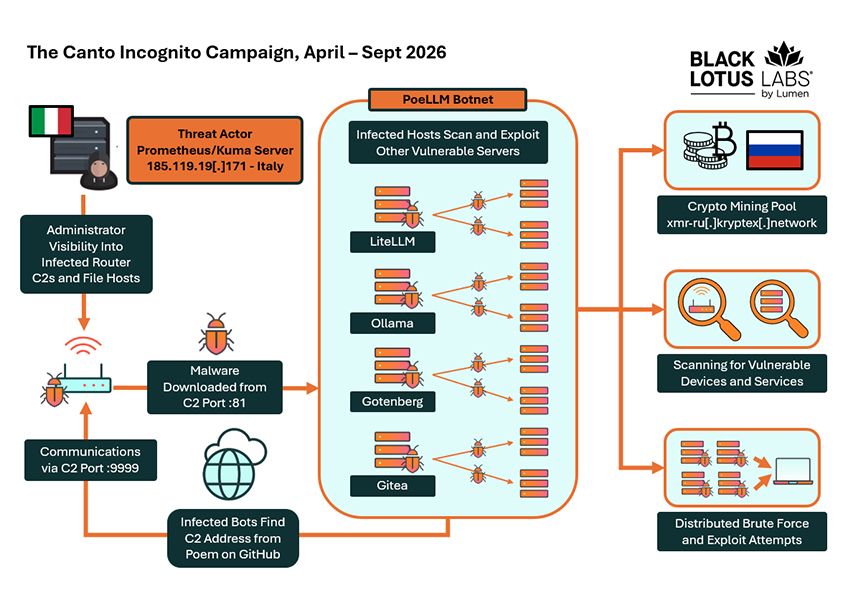
Active since April 2026, the operation combines vulnerability exploitation, cryptocurrency miners and an unusual command-and-control mechanism that derives server addresses from a poem hosted on GitHub.
Victims predominantly run LiteLLM, Ollama, Gotenberg and Gitea, with possible targeting of Ivanti Sentry. Most affected systems are concentrated in the United States and Western Europe.
The research’s headline findings report peak activity exceeding 800 active servers daily, while earlier sections describe approximately 2,200 affected servers, indicating different reporting snapshots.
PoeLLM retrieves its control instructions from “On the Nature of Connection,” a poem embedded in a file named dash.css within a fork of the Node.js website repository.
Researchers found no apparent connection between the malware and legitimate Node.js software.
The malware extracts four words or phrases using fixed textual markers, then maps them through a hardcoded dictionary to numerical values.
These values become the four octets of an IPv4 address identifying the current command-and-control server.
By modifying selected words, the operator can redirect infected machines without replacing their malware. Researchers observed 11 poem updates following the repository’s initial April 13 commit.
The decoding pattern remained unchanged, allowing investigators to reconstruct infrastructure transitions.
Black Lotus Labs said in a report shared with GBhackers, while investigating a compromised Ivanti Sentry system that contacted 5.78.73[.]122 and subsequently began scanning other devices.
Further telemetry exposed widespread scanning against ports 3000 and 4000, associated with Gotenberg and LiteLLM deployments.
PoeLLM Malware
Successful attacks instructed targets to retrieve payloads from command servers on port 81. Infected systems subsequently communicated over ports 3778, 5001, 5002 or 9999.
One analyzed sample referenced LiteLLM’s /mcp-rest/test/connection endpoint, consistent with CVE-2026-42271.
The vulnerability affects versions 1.74.2 through versions preceding 1.83.7 and permits authenticated users, including low-privilege API-key holders, to execute commands through supplied MCP configurations.
Version 1.83.7 fixes the issue. Importantly, this is authenticated command execution, not an unauthenticated flaw.
The ELF payload, named libgcrypt, incorporates remote-shell capabilities, HTTP/S scanning, exploit deployment, and XMRig and Iron miners.
Victims contacted Kryptex mining infrastructure, including 5.180.174[.]162:8029 and 46.21.245[.]211:7029.
The initial C2 decoded from the poem was 191.37.28[.]160 and appears to have been used to test the infection process.
Compromised machines also became scanning and exploitation workers, distributing the campaign’s expansion across victim infrastructure.
Recent traffic toward SSH services and login portals suggests experimentation with distributed brute-force attacks, although researchers considered that capability immature.
Several decoded command servers exposed vulnerable Boa router administration interfaces, suggesting the operator reused compromised network devices.
Researchers did not establish direct exploitation evidence for the vulnerabilities identified on the initial Brazilian router.
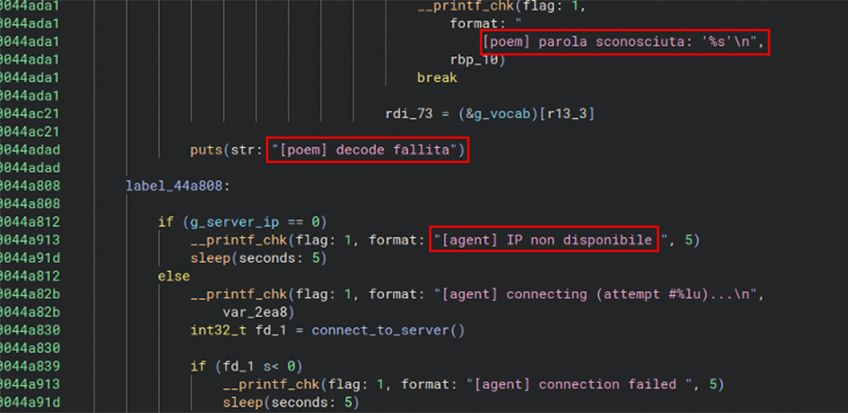
Italian-language comments and infrastructure connections support an Italian-speaking operator assessment, not a confirmed nationality.
Researchers separately assessed an Italy-hosted server as a probable administrative interface with moderate confidence.
Lumen says it blocked traffic to and from identified PoeLLM command servers. Defenders should correlate the reported download paths, mining connections and scanning activity with exposed application inventories.
Gotenberg’s installation guidance explicitly warns against public internet exposure and recommends keeping the service behind a firewall.
The documentation also demonstrates localhost-only port binding, directly addressing the deployment exposure exploited by campaigns targeting publicly reachable conversion services.
IOCs
| IP Address | Start Date | End Date |
|---|---|---|
| 191.37.28.160 | April 13, 2026 | May 16, 2026 |
| 89.39.253.46 | April 14, 2026 | June 24, 2026 |
| 120.224.114.212 | May 9, 2026 | September 8, 2026 |
| 5.78.73.122 | June 8, 2026 | August 22, 2026 |
| 15.204.178.28 | June 14, 2026 | August 17, 2026 |
| 92.119.165.74 | July 1, 2026 | July 23, 2026 |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.