Hackers Abuse Google CAPTCHA, WebDAV and BNB Smart Chain to Deploy Credential-Stealing Malware
Cisco Talos details ClickFix campaigns abusing fake Google CAPTCHA prompts, WebDAV and BNB Smart Chain to deploy the Amatera infostealer.
Cisco Talos identified a multi-stage campaign, first observed in April 2026 when a Ukrainian government organization executed a disguised DLL named verification.google from a WebDAV path. The chain combines ClearFake JavaScript injected via malicious Cloudflare Workers, EtherHiding payloads stored in BNB Smart Chain contracts, ClickFix social engineering, and WebDAV-hosted DLL loaders to deliver the Amatera (ACR Stealer) infostealer. The Amatera configuration contained over 400 collection entries targeting browsers, messengers, crypto wallets, password managers, FTP and VPN tools, hunting for .kdbx, .p12, .pfx and .pem files. The pf.ch branch deploys ZigCryptoStealer, an EDR-terminating vulnerable driver and Go-based reverse TCP proxies, while the verification.google branch installs NetSupport Manager, supporting moderate-confidence attribution of the UAT-10820 activity to a Russian actor.
- Chain uses compromised sites, ClearFake JavaScript, EtherHiding in BNB Smart Chain contracts, ClickFix prompts, and WebDAV DLL loaders
- Amatera configuration holds 400+ collection entries: browsers, wallets, messengers, password managers, FTP and VPN tools
- pf.ch branch deploys ZigCryptoStealer, an EDR-killing vulnerable driver, and Go reverse TCP proxies
- verification.google branch installs unauthorized NetSupport Manager; Russia-based C2 IP supports UAT-10820 attribution
- Hunt rundll32.exe from WebDAV UNC paths invoking pf.ch or verification.google by ordinal
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | leaguejazire.com | opens a WebDAV UNC path hosted on a randomized subdomain of leaguejazire[.]com , then launches the pf.ch loader through rundll32.exe usi |
Full article800 words · extracted from gbhackers.com · click to collapse
A multi-stage malware operation that combines fake Google CAPTCHA prompts, WebDAV-hosted DLL execution, malicious Cloudflare Workers and BNB Smart Chain smart contracts to deploy the Amatera information stealer.
The activity was first identified in April 2026 after a Ukrainian government organization executed a disguised DLL named “verification.google” from a WebDAV path using the 32-bit rundll32.exe utility.
Talos assesses with moderate confidence that the campaign is part of a broader cryptocurrency and credential theft operation rather than a targeted intrusion against the Ukrainian organization.
The researchers track the activity associated with the “verification.google” branch as UAT-10820, and assess with moderate confidence that a Russian threat actor operated that branch based partly on its NetSupport Manager command-and-control infrastructure.
Investigation of the initial WebDAV execution led Talos to a related DLL loader called “pf.ch,” which exposed the full delivery sequence.
The chain begins with compromised websites where a malicious Cloudflare Worker injects ClearFake JavaScript.
Rather than hosting every stage on conventional attacker-controlled servers, the injected code retrieves obfuscated browser-stage payloads from BNB Smart Chain contracts.
This blockchain-backed delivery technique, widely known as EtherHiding, lets operators update malicious JavaScript stored in smart-contract data without modifying the compromised website.
In the observed campaign, the initial script queried BNB Smart Chain testnet contract 0x886d310Ac23e05EA705e24E513D19f53793832A9, then selected a Windows- or macOS-specific contract based on the visitor’s operating system.
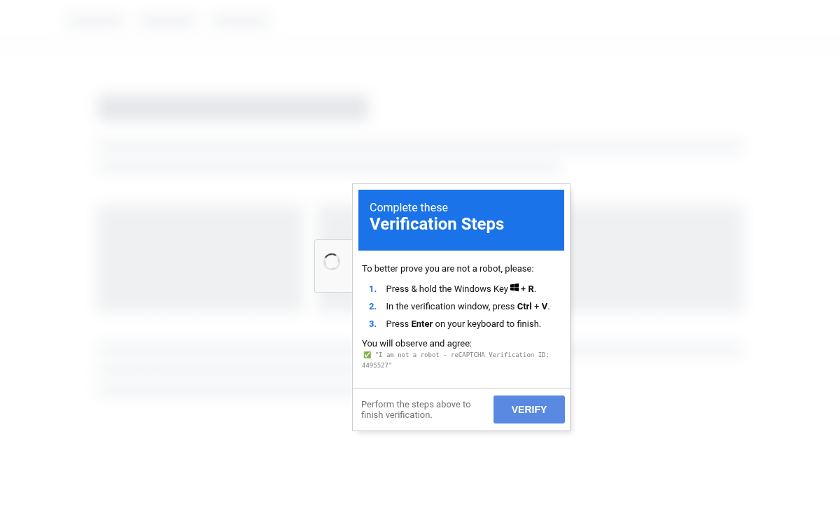
The page instructs victims to press Windows+R, paste clipboard content and execute it. This ClickFix technique turns the victim into the execution mechanism, bypassing many conventional drive-by protections.
The clipboard command opens a WebDAV UNC path hosted on a randomized subdomain of leaguejazire[.]com, then launches the pf.ch loader through rundll32.exe using export ordinal #1.
The original “verification.google” sample used the same WebDAV, disguised filename and ordinal-based execution pattern, indicating that the chains are likely closely related.
Both loaders ultimately deploy Amatera, also known as ACR Stealer, a credential and cryptocurrency-focused malware family.
The pf.ch loader uses exception-driven control flow, API hashing, XOR decryption, LZNT1 decompression and Windows fibers to unpack its payload in memory.
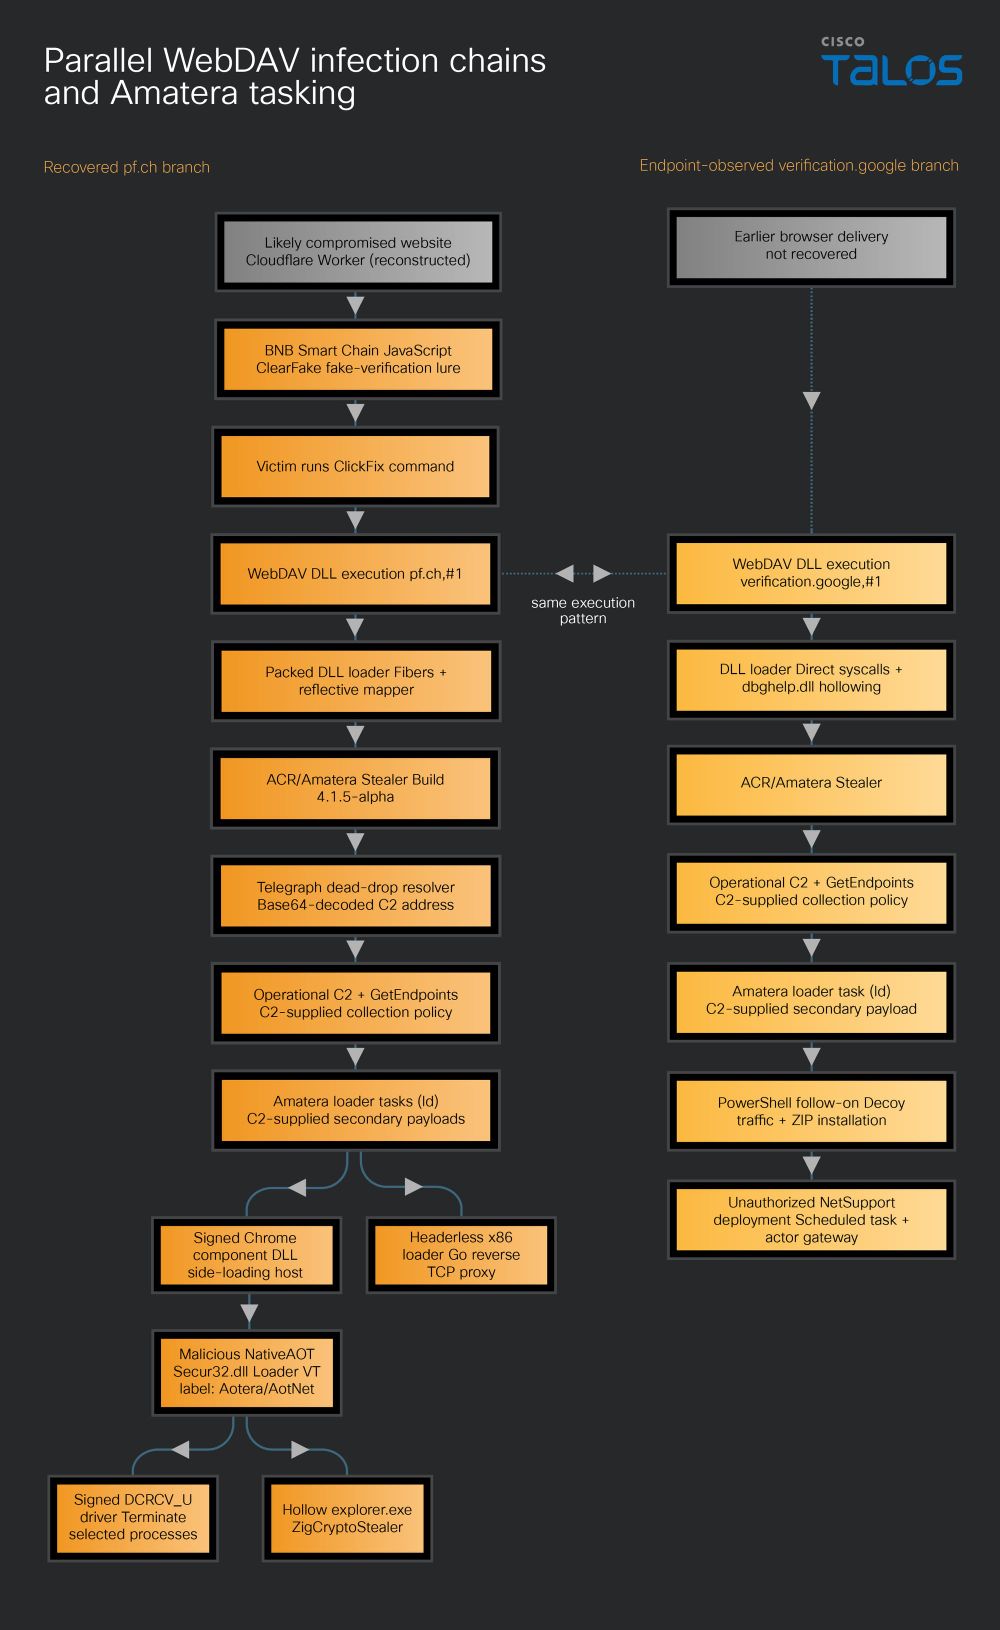
The “verification.google” variant instead uses direct WoW64 syscalls and DLL hollowing, mapping a clean dbghelp.dll image before overwriting its executable code with malicious instructions.
Google CAPTCHA Abuse
The malware’s collection scope is extensive. Talos found that the “verification.google” Amatera configuration contained more than 400 collection entries targeting browser data, browser extensions, messaging applications, cryptocurrency wallets, password managers, authenticator software, FTP tools, email clients, VPN clients and remote-access tools.
Telegram, Signal, WhatsApp, KeePass, Bitwarden, 1Password, FileZilla, NordVPN and AnyDesk were among the targeted applications.
Cisco Talos Researchers said that, For Windows visitors, the script performs headless-browser checks, assigns a victim identifier and overlays a fraudulent Google CAPTCHA-style verification prompt.
The stealer also searches Desktop, Downloads, Documents and Recent Items for private keys, wallet backups, API tokens, OAuth material, password databases and certificate files, including .kdbx, .p12, .pfx and .pem files.
This makes the campaign particularly dangerous for cryptocurrency users, developers and enterprise administrators.
The two branches diverge after Amatera establishes command-and-control communications.
The pf.ch branch downloads a ZIP archive containing a legitimate Google Chrome component that sideloads a malicious NativeAOT secur32.dll.
That DLL launches ZigCryptoStealer, which monitors the clipboard and replaces cryptocurrency wallet addresses with attacker-controlled addresses.
It also deploys a signed but vulnerable driver that can terminate EDR and other security processes through a kernel-mode process-termination primitive.
A separate memory-resident payload turns infected Windows systems into Go-based reverse TCP proxies using WebSocket Secure and HashiCorp Yamux multiplexing.
That capability can provide attackers with covert network relay infrastructure and post-compromise access.
Meanwhile, the “verification.google” branch retrieves a PowerShell payload that installs an unauthorized NetSupport Manager remote-access instance.
Its configuration pointed to infrastructure using a Russia-based IP address, supporting Talos’ assessment of possible Russian actor involvement.
Defenders should investigate executions of rundll32.exe from WebDAV UNC paths, particularly where non-DLL filenames such as pf.ch or verification.google are invoked by ordinal.
Organizations should also restrict unnecessary WebClient service usage, monitor suspicious pushd and WebDAV activity, and train users that legitimate CAPTCHA pages never require pasting commands into Windows Run or Terminal.
Security teams should further hunt for suspicious Cloudflare Worker modifications on owned websites, connections to BNB Smart Chain RPC endpoints from browser processes, unsigned or unexpected secur32.dll files loaded by Chrome-related executables, and unauthorized NetSupport Manager installations.
The campaign demonstrates how social engineering, decentralized infrastructure and living-off-the-land Windows execution can be combined into a resilient credential-theft pipeline.
★ Learn 7 Metric-Gated AI SOC Deployment Phases – Download Free AI SOC Deployment Playbook 2026.
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.
Text extracted automatically; images, tables and formatting may be missing. Original: https://gbhackers.com/google-captcha-abuse/