Microsoft shares one-click ProxyLogon mitigation tool for Exchange servers
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
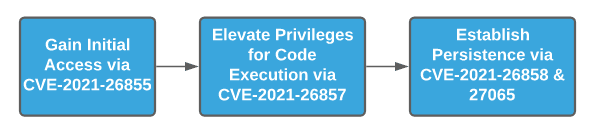
| CVE-2021-26855 | Unauthenticated SSRF/RCE in Microsoft Exchange Server (ProxyLogon) CVE-2021-26855 is a server-side request forgery flaw (CWE-918) in Microsoft Exchange Server that allows an unauthenticated remote attacker to send specially crafted HTTP requests and have the Exchange server process them as itself, disclosing sensitive session information. When chained with sibling Exchange flaws (the 'ProxyLogon' chain), it yields authentication bypass and arbitrary file write, escalating to full remote code execution with SYSTEM-level privileges on the on-premises Exchange server. Any organization running an affected on-premises Exchange server reachable over HTTP/HTTPS (typically outbound webmail) is exposed; Exchange Online was not affected. Exploitation is confirmed in the wild at large scale: the flaw was mass-exploited beginning in early 2021 (notably by the HAFNIUM group), is on the CISA KEV with documented ransomware use, and has a maximum EPSS score of 100% (100th percentile), despite no public PoC listing. Do: Apply the vendor's March 2021 Exchange security updates (or later cumulative updates) immediately, per the CISA required action; until patched, limit Exchange (ECP/OWA) exposure to the internet via firewall/VPN rules. Hunt for compromise: review IIS logs for unrecognized authenticated activity against FrontEnd HttpProxy endpoints, and check for malicious files or webshells under inetpub\wwwroot\aspnet_client, given the known ransomware use. | 9.1 | 100% | KEV ransomware PoC ×4 |
| masshundreds of thousands of on-premises deployments; tens of thousands of internet-exposed Exchange servers |
Full article463 words · extracted from therecord.media · click to collapse
Microsoft has published today a one-click software application that applies all the necessary mitigations for the ProxyLogon vulnerabilities to Microsoft Exchange servers that can't be updated for the time being. The new tool is named EOMT (or the Exchange On-premises Mitigation Tool), is written in PowerShell, and available for download via Microsoft's official GitHub account. Microsoft said it released the tool to help companies that don't have dedicated IT or security teams to handle updating their on-premises Exchange servers. The OS maker hopes that any company's employee would be able to download the tool on a Windows system running an Exchange mail server and execute the EOMT.ps1 PowerShell script by double-clicking on it. EOMT script also removes web shells Once started, the script will install a URL Rewrite configuration on the server, which is enough to mitigate CVE-2021-26855, the initial entry point in a series of four bugs known as ProxyLogon. But the tool also includes a copy of the Microsoft Safety Scanner app that will scan the Exchange server for known web shells that have been seen deployed in past ProxyLogon attacks. Once a web shell is discovered, the Microsoft Safety Scanner app will remove the backdoor and cut off the attacker's access. Microsoft says the tool can be used to both apply mitigations but also as a way to ensure that past mitigations applied by hand have been installed correctly. Users who installed patches released on March 2 do not need to run the tool, as the patches provide much better coverage for ProxyLogon attacks. This also includes an additional set of patches released on March 9 to cover Exchange server versions that have reached end-of-life status. Attacks on Microsoft have reached a fever pitch after Microsoft disclosed that a group of Chinese state-sponsored hackers known as Hafnium was abusing the four bugs to install backdoors on Exchange servers across the world. Since the initial disclosure, nine state-sponsored groups have been seen abusing the ProxyLogon vulnerabilities, two crypto-mining groups, and a ransomware gang. Attacks also intensified after the release of a free proof-of-concept exploit. Last week, Microsoft said that of the roughly 400,000 Exchange servers deployed across the internet, 318,000 appear to have been patched against the ProxyLogon vulnerabilities. Microsoft has released a new, one-click mitigation tool, the Microsoft Exchange On-Premises Mitigation Tool, to help customers who do not have dedicated security or IT teams to apply security updates for Microsoft Exchange Server. Learn more: https://t.co/IfChAqpcEH pic.twitter.com/xD94M8Czg5— Microsoft Security Intelligence (@MsftSecIntel) March 15, 2021
No previous article
No new articles
Catalin Cimpanu
is a cybersecurity reporter who previously worked at ZDNet and Bleeping Computer, where he became a well-known name in the industry for his constant scoops on new vulnerabilities, cyberattacks, and law enforcement actions against hackers.
Text extracted automatically; images, tables and formatting may be missing. Original: https://therecord.media/microsoft-shares-one-click-mitigation-tool-for-exchange-servers