Chaotic Eclipse Releases Kaspersky Zero
Researcher Chaotic Eclipse released HardBreacher, a PoC privilege-escalation exploit for Kaspersky Endpoint Security on fully patched Windows 11 25H2.
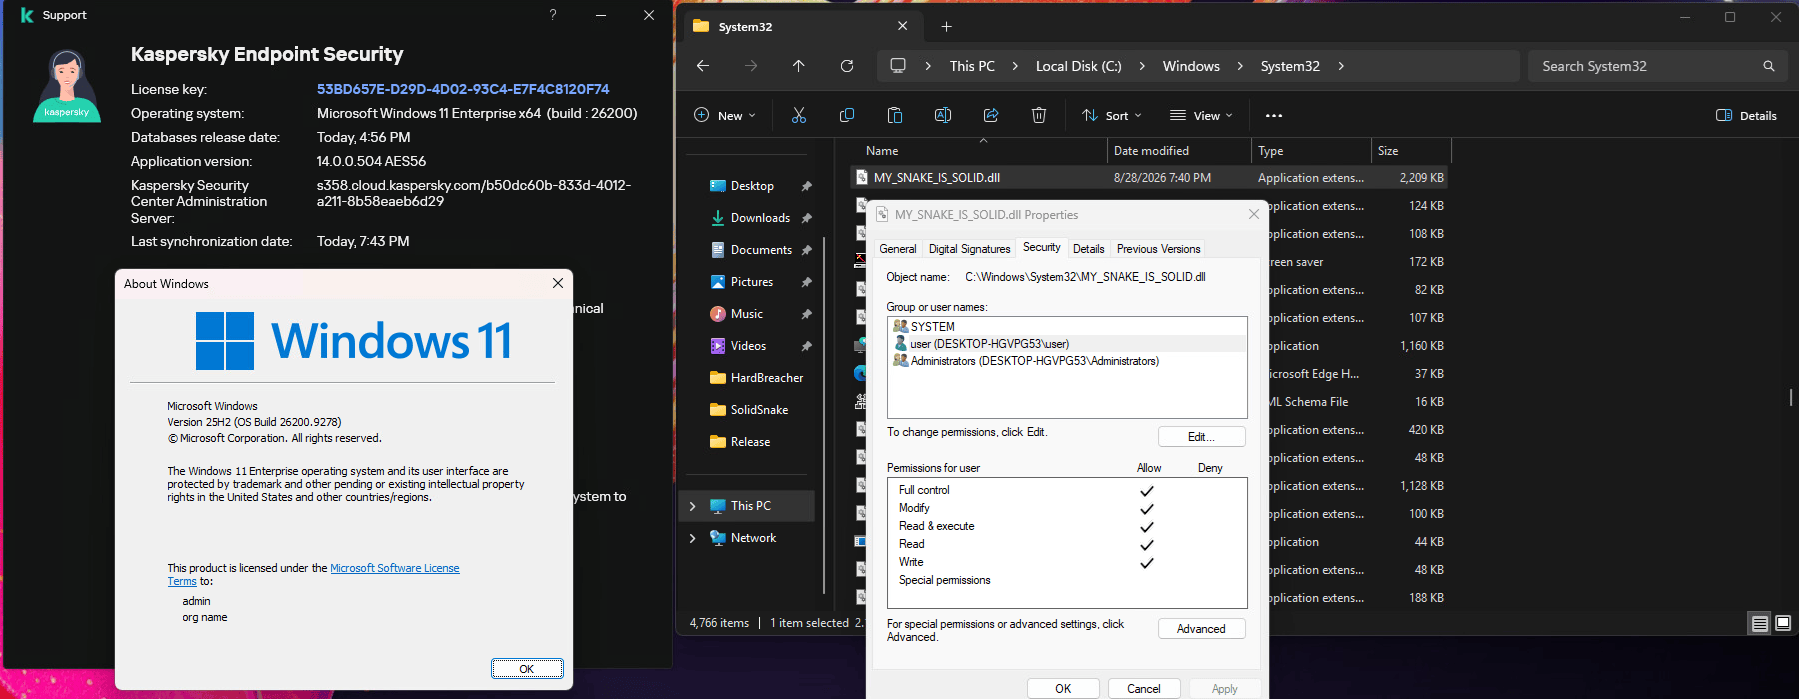
Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE and Nightmare-Eclipse, released a PoC zero-day exploit named HardBreacher targeting Kaspersky Endpoint Security v14.0.0.504. The exploit achieves privilege escalation on fully patched Windows 11 25H2, creating a DLL in System32 with full user permissions and potentially disrupting Kaspersky's UI process and file-access controls. The PoC is unstable and may require repeated attempts; Kaspersky claims it has already addressed the vulnerability.
- PoC creates MY_SNAKE_IS_SOLID.dll in System32 on success
- Exploit may disrupt Kaspersky UI and file-access controls
- PoC is unstable and requires repeated runs
- Researcher known for prior Microsoft Defender zero-days
Full article344 words · extracted from securityaffairs.com · click to collapse
 Pierluigi Paganini
 September 01, 2026

Chaotic Eclipse released HardBreacher, a PoC exploit for a Kaspersky Endpoint Security privilege escalation flaw, adding another zero-day to his list.
Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Kaspersky Endpoint Security. The researcher named the exploit HardBreacher, it triggers a privilege escalation flaw.
Nightmare Eclipse says the Kaspersky Endpoint Security zero-day allows privilege escalation on a fully patched Windows 11 25H2 system running Kaspersky Endpoint v14.0.0.504.
The researcher pointed out that the PoC is unstable and may require repeated attempts, but when successful, it creates a DLL in System32 with full user permissions.
The researcher also claims taking control of Kaspersky’s UI process can disrupt the antivirus and interfere with file-access controls, potentially leaving the system in an unstable state.
“The PoC is not in the best shape at all, it is basically duct tapped, I just managed to make it work and that’s all. It will fail to run with error so you just have to keep rerunning it. If it succeeds, it will create a file in C:\Windows\System32\MY_SNAKE_IS_SOLID.dll will full permissions for current user.” states Chaotic Eclipse. “The interesting part about this is the Kaspersky completely loses it when you take control over the UI process, you can cause it to stop functioning, grant/block access to files its not supposed to, if the PoC succeeds, the entire operating system becomes a hot mess.”
At this time, Kaspersky claimed it had already addressed the vulnerability.
Chaotic Eclipse, also known as Nightmare Eclipse, is a researcher known for publicly releasing PoC exploits for zero-day vulnerabilities, often after criticizing vendors’ handling of vulnerability reports. His releases have mainly targeted Microsoft products, including Windows and Microsoft Defender, with some later exploited in the wild. Among the most notable are the Undefend and RedSun Defender zero-days.
His work has fueled debate over responsible disclosure and the risks of publishing working exploits.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Zero-Day HardBreacher)
Text extracted automatically; images, tables and formatting may be missing. Original: https://securityaffairs.com/198214/hacking/chaotic-eclipse-releases-kaspersky-zero-day-hardbreacher.html