Chaotic Eclipse Releases Crowdstrike Falcon ZeroDay FalconFlank
Researcher Chaotic Eclipse released FalconFlank, a PoC zero-day privilege escalation exploit against CrowdStrike Falcon's Microsoft Office macro removal feature.
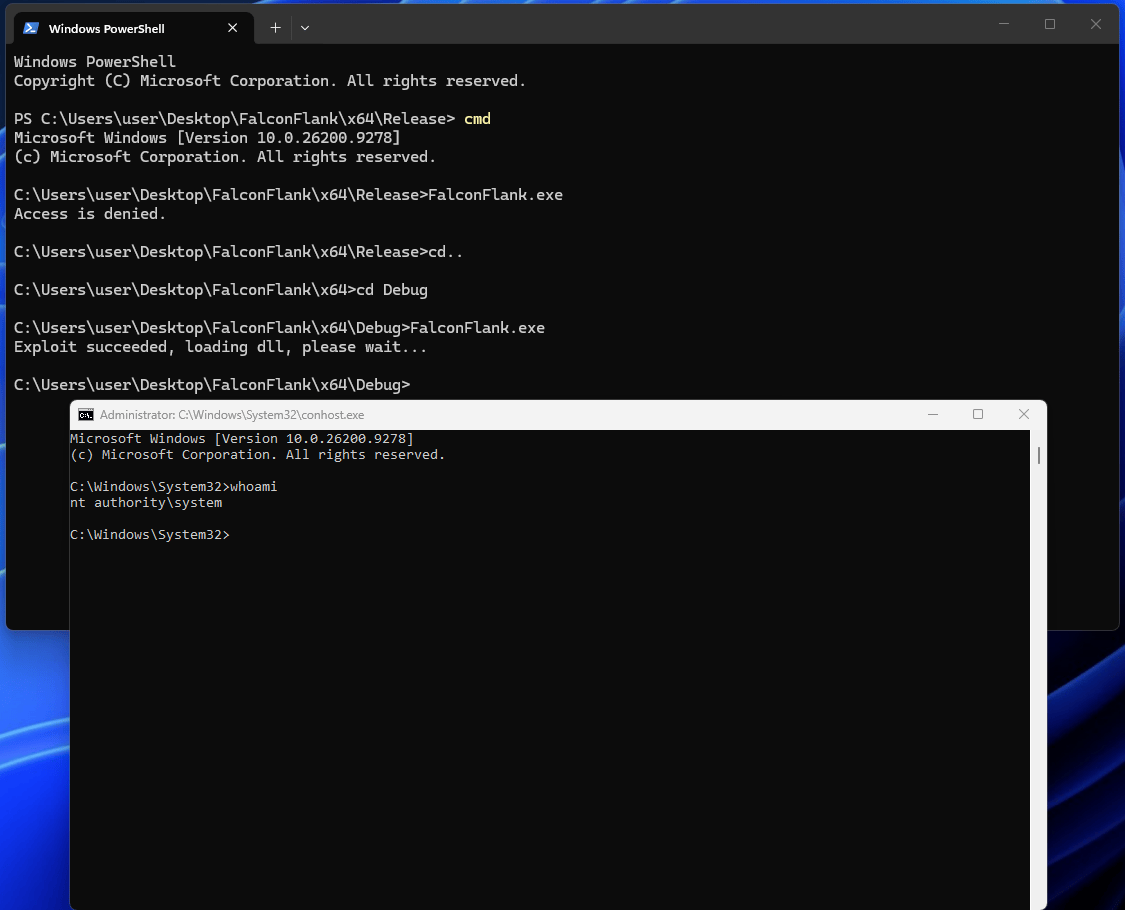
Security researcher Chaotic Eclipse (also known as Nightmare Eclipse) published FalconFlank, a proof-of-concept zero-day exploit for a privilege escalation flaw in CrowdStrike Falcon Sensor. It abuses the Microsoft Office file malicious macro removal remediation feature, which runs with high privileges, and works on fully updated Windows 11 25H2 and Windows Server 2025 with Falcon Phase 3 Optimal Protection. CrowdStrike says it is investigating and advises customers to disable the Microsoft Office File Suspicious Macro Removal Windows policy. The same researcher recently released zero-day PoCs against Kaspersky Endpoint Security (HardBreacher) and Avast Antivirus (PrettyPrague), the latter dumping the SAM database for a SYSTEM shell.
- FalconFlank abuses Falcon's Microsoft Office file malicious macro removal feature, which operates with high privileges
- PoC requires Falcon Phase 3 Optimal Protection with the malicious macro removal feature enabled on patched Windows 11 25H2 or Server 2025
- CrowdStrike advises disabling the Microsoft Office File Suspicious Macro Removal policy while customers stay protected by Cloud Anti-malware for Microsoft Office Files
- Researcher also published Kaspersky HardBreacher and Avast PrettyPrague zero-day privilege escalation PoCs, with Avast flaw possibly extending to AVG and Norton
- Highlights broader issue that EDR elevated privileges can become a local privilege escalation attack surface
Full article657 words · extracted from securityaffairs.com · click to collapse
 Pierluigi Paganini
 September 03, 2026

Chaotic Eclipse released FalconFlank, a PoC exploit for a Crowdstrike Falcon ZeroDay Elevation of Privileges Vulnerability
Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Crowdstrike Falcon cybersecurity platform. The researcher named the exploit FalconFlank, it triggers a privilege escalation flaw.
According to the researcher, FalconFlank abuses Falcon’s “Microsoft Office file malicious macro removal” feature. The function is part of Falcon’s remediation capabilities and operates with high privileges. The researcher claims that this behavior can be abused to escalate privileges from a low-privileged local user to a more powerful context.
“FalconFlank is a 0day privilege escalation that abuses the office malicious macros remediation in Crowdstrike Falcon Sensor, obviously by the time I drop this Crowdstrike would already have detections for it so if you want to test you either have to add it to the exclusions or obfuscate the PoC and change the dll load technique.” reads the announcement. “As of now it works in a fully updated windows 11 25H2 / Windows Server 2025 with Crowdstrike Falcon – Phase 3 Optimal Protection + needs “Microsoft Office file malicious macro removal””
The proof of concept works on fully updated Windows 11 25H2 and Windows Server 2025 systems running CrowdStrike Falcon with Phase 3 – Optimal Protection and the malicious macro removal feature enabled.
An interesting part of the announcement is the researcher’s warning that CrowdStrike may already have detections for the published PoC. In other words, the underlying vulnerability could still exist even if Falcon detects and blocks the specific exploit technique used in the PoC.
The case is particularly interesting because it highlights a broader security issue: EDR products need elevated privileges to protect a system, but those same privileges can become an attack surface. An attacker who gains limited local access may try to abuse the security software itself to obtain higher privileges.
Recently, Chaotic Eclipse released exploits targeting other anti-malware solutions.
Chaotic Eclipse released a zero-day exploit targeting Kaspersky Endpoint Security he named HardBreacher, which triggers a privilege escalation flaw. The researcher pointed out that the PoC is unstable and may require repeated attempts, but when successful, it creates a DLL in System32 with full user permissions. The researcher also claims taking control of Kaspersky’s UI process can disrupt the antivirus and interfere with file-access controls, potentially leaving the system in an unstable state.
Nightmare Eclipse says the Kaspersky Endpoint Security zero-day allows privilege escalation on a fully patched Windows 11 25H2 system running Kaspersky Endpoint v14.0.0.504.
The researcher also released a zero-day exploit targeting GenDigital Avast Antivirus, named PrettyPrague. The exploit triggers a privilege escalation flaw.
The researcher claims to have found another zero-day in an antimalware product, this time targeting Avast Antivirus. The PoC exploits a flaw in Avast Sandbox to dump the Windows SAM database and gain a SYSTEM-level shell. It reportedly works even on fully patched Avast Antivirus and Windows 11 25H2. The researcher also suspects the flaw may affect other Gen Digital products, including AVG and Norton.
Chaotic Eclipse, also known as Nightmare Eclipse, is a researcher known for publicly releasing PoC exploits for zero-day vulnerabilities, often after criticizing vendors’ handling of vulnerability reports. His releases have mainly targeted Microsoft products, including Windows and Microsoft Defender, with some later exploited in the wild. Among the most notable are the Undefend and RedSun Defender zero-days.
His work has fueled debate over responsible disclosure and the risks of publishing working exploits.
Update with a statement from CrowdStrike:
“We are actively investigating these claims and advise customers to disable the Microsoft Office File Suspicious Macro Removal Windows policy setting. Customers remain protected through the Cloud Anti-malware for Microsoft Office Files settings. We refer customers to the FalconFlank Tech Alert in the CrowdStrike support portal.” – CrowdStrike spokesperson
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Crowdstrike Falcon)
Text extracted automatically; images, tables and formatting may be missing. Original: https://securityaffairs.com/198342/hacking/chaotic-eclipse-releases-crowdstrike-falcon-zeroday-falconflank.html