Korean Air discloses data breach after the hack of its catering and duty
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2023-0669 | Pre-Authentication Deserialization RCE in Fortra GoAnywhere MFT Fortra (formerly HelpSystems) GoAnywhere MFT is vulnerable to pre-authentication remote code execution (CWE-502) in the License Response Servlet, which deserializes an attacker-controlled object without validating it. An unauthenticated attacker who can reach the exposed administrative interface can send a crafted serialized object to the servlet and trigger code execution on the server. Successful exploitation gives the attacker the ability to run arbitrary code in the context of the application, which has been leveraged for ransomware operations. All organizations running GoAnywhere MFT with the affected component reachable by untrusted networks are in scope. The flaw is being actively exploited: CISA added it to the Known Exploited Vulnerabilities catalog on 2023-02-10, ransomware use is confirmed, and EPSS puts the 30-day exploitation probability at 100%. Do: Apply the vendor's updates for GoAnywhere MFT immediately, per Fortra's instructions, as required by the CISA KEV catalog. Until patched, restrict or block untrusted/internet access to the administrative interface hosting the License Response Servlet, and review logs for signs of exploitation given confirmed in-the-wild and ransomware use. | 7.2 | 100% | KEV ransomware PoC ×3 |
| moderate≈1,000–10,000 internet-exposed GoAnywhere MFT instances (public internet scans of the exposed administrative interface) | |
| CVE-2023-34362 | Unauthenticated SQL Injection in Progress MOVEit Transfer CVE-2023-34362 is an unauthenticated SQL injection flaw (CWE-89) in Progress MOVEit Transfer that allows an attacker with no credentials to gain unauthorized access to the product's database. It is triggered remotely via crafted input submitted to the MOVEit Transfer web application, with the impact varying by the backend database engine in use (MySQL, Microsoft SQL Server, or Azure SQL). A successful attacker can infer the structure and contents of the database and, depending on the engine, execute SQL statements that alter or delete database elements, exposing data handled by the file-transfer service. Any organization running an internet-reachable MOVEit Transfer instance is affected; public internet-exposure scans around disclosure identified on the order of a few thousand servers, each typically serving enterprise or government user bases. Exploitation is confirmed in the wild: the flaw was added to CISA KEV on 2023-06-02 with known ransomware use and an EPSS exploitation probability of 99.9% (100th percentile), while no public PoC is known. Do: Apply the vendor's updates immediately, per Progress instructions and CISA's required action. Until patched, restrict internet exposure of MOVEit Transfer and check the backend database for unexpected structure or content changes and deletions. Because in-the-wild exploitation and ransomware use are confirmed, treat any unpatched, internet-facing instance as potentially compromised and review stored transfer data and access logs for anomalies. | 9.8 | 100% | KEV ransomware PoC |
| large≈2,000-3,000 internet-exposed MOVEit Transfer servers (public internet-exposure scans) | |
| CVE-2025-61882 | Unauthenticated Takeover of Oracle E-Business Suite Concurrent Processing CVE-2025-61882 is a critical (CVSS 9.8) authentication flaw (CWE-287) in the BI Publisher Integration component of the Oracle Concurrent Processing product within Oracle E-Business Suite. An unauthenticated attacker with network access over HTTP can exploit it remotely with no credentials and no user interaction, achieving a takeover of Oracle Concurrent Processing with high confidentiality, integrity, and availability impact. Any organization running Oracle E-Business Suite 12.2.3 through 12.2.14 is affected, especially instances reachable from the internet. The flaw is being actively exploited in the wild: the Cl0p data-theft group has used it to breach dozens of organizations (including Harvard University, with 1.3 TB of data leaked), CISA added it to the Known Exploited Vulnerabilities catalog on 2025-10-06 with known ransomware use, and EPSS puts its 30-day exploitation probability at 99.7%. Do: Apply Oracle's released patch or mitigations for CVE-2025-61882 to affected E-Business Suite 12.2.3-12.2.14 deployments as instructed by the vendor; per CISA KEV requirements, federal agencies must follow BOD 22-01 guidance or discontinue use if mitigations are unavailable. Until patched, limit internet exposure of EBS and its BI Publisher/Concurrent Processing HTTP endpoints, and review web and application logs for unauthenticated access and signs of Cl0p-style data theft or follow-on ransomware. | 9.8 | 100% | KEV ransomware |
| largetens of thousands of EBS environments worldwide across an estimated ~5,000+ customer organizations (est.) |
Full article748 words · extracted from securityaffairs.com · click to collapse
 Pierluigi Paganini
 December 29, 2025

Korean Air employee discloses a data breach after a hack of its catering and duty-free supplier, KC&D, affecting thousands of staff.
Korean Air suffered a data breach after its in-flight catering supplier Korean Air Catering & Duty-Free (KC&D) was hacked, exposing personal data of ~30,000 employees of Korean Air employees.
Korean Air is South Korea’s flag carrier and one of the largest airlines in Asia, operating passenger and cargo services worldwide. It employs around 18,000–20,000 people globally and serves destinations across multiple continents. In 2024 it carried over 23 million passengers, and in 2025 it has transported more than 16 million passengers so far. The airline operates a large modern fleet and has hubs at Seoul’s major airports, connecting numerous international and domestic routes.
The company posted an internal notice stating that KC&D had informed them of a security breach involving personal data belonging to the airline’s employees, according to sources cited by Korea JoongAng Daily.
Korean Air pointed out that no customer data appears to have been compromised by the cyber incident.

“”KC&D Service (KC&D)*,” an in-flight meal and in-flight sales company that was spun off from our company in 2020 and operates as a separate entity, was recently attacked by an external hacker group. It is understood that during this process, the personal information (names, account numbers) of our employees stored on that company’s ERP server was leaked.” reads the notice. “Our company recently learned of this after receiving the information from KC&D Service. Although this incident occurred within the management scope of an external partner company that was spun off and sold, the company takes this matter very seriously as our employees’ information is involved.”
Korean Air stated that, upon learning of the breach, it implemented emergency security measures, reported the incident to authorities, and is working to identify the scope and affected employees. The airline confirmed no additional employee data has leaked but warned staff to watch for suspicious messages. Further guidance and support will be provided, and security protocols with partners will be fully reviewed to prevent recurrence.
“Korean Air takes this incident very seriously, especially since it involves employee data, even if it originated from a third-party vendor that was sold off,” said Woo Kee-hong, vice chairman of Korean Air, in a message to employees. “We are currently focusing all our efforts on identifying the full scope of the breach and who was affected.”
Korean Air notified the relevant authorities and is investigating the incident to determine the precise scope and targets of the leak.
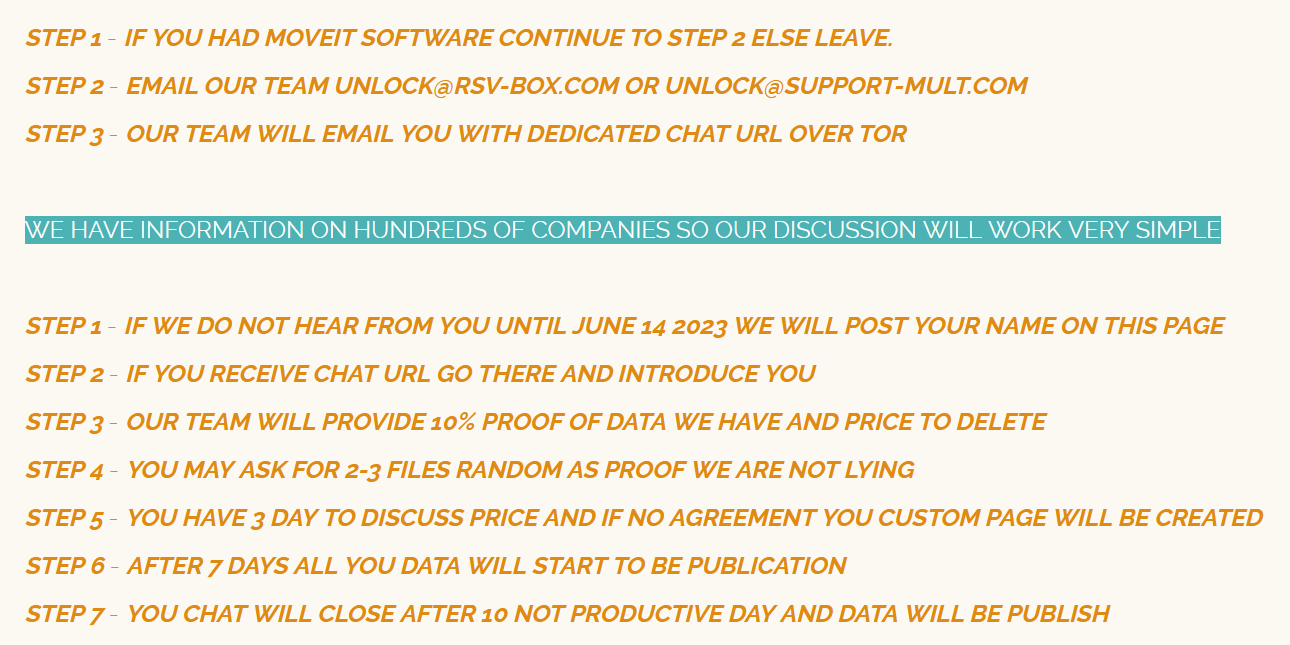
Korean Air did not attribute the attack to a specific threat actor, however, the Clop ransomware group has claimed responsibility for the KC&D attack in November. The group added KC&D to its Tor data leak site and already leaked the allegedly stolen data.

The Clop ransomware gang has been exploiting the critical Oracle EBS zero-day CVE-2025-61882 since early August, stealing sensitive data from numerous organizations worldwide, including Envoy Air, Harvard University, Washington Post, Logitech, University of Pennsylvania, and University of Phoenix.
Clop (aka Cl0p) is a prolific Russian-speaking ransomware-as-a-service group specializing in big-game hunting and double-extortion.
The Clop ransomware group first appeared on the threat landscape around February 2019, emerging from the TA505 cybercrime group, a financially motivated gang active since at least 2014.
Like other Russia-based threat actors, Clop avoids targets in former Soviet countries and its malware can’t be activated on a computer that operates primarily in Russian.
Operators and affiliates identify high-value targets, steal sensitive data, encrypt networks, then publish stolen files on data-leak sites to pressure victims into paying. Clop exploits zero-days and vulnerable third-party software (e.g., MOVEit, GoAnywhere, Oracle EBS), leverages initial-access brokers and automation, and uses sophisticated evasion and lateral-movement techniques to maximize impact and monetization.
Clop’s victims include Shell, British Airways, Bombardier, University of Colorado, PwC, and the BBC.
The group conducted major campaigns including:
- Accellion FTA (2020–2021): Exploited a zero-day in the file-transfer appliance to steal data from ~100 organizations.
- GoAnywhere MFT (2023): Targeted a flaw (CVE-2023-0669) to compromise over 130 organizations.
- MOVEit Transfer (2023): One of the largest ransomware campaigns in history, impacting hundreds of companies worldwide, including US and European firms, through an SQL injection zero-day (CVE-2023-34362).
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, data breach)
Text extracted automatically; images, tables and formatting may be missing. Original: https://securityaffairs.com/186275/data-breach/korean-air-discloses-data-breach-after-the-hack-of-its-catering-and-duty-free-supplier.html