Cyber Command alerts US firms of 'ongoing' hacks targeting Atlassian enterprise software
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2021-26084 | Atlassian Confluence Server and Data Center Object-Graph Navigation Language (OGNL) Injection Vulnerability CVE-2021-26084 is an OGNL injection vulnerability (CWE-917) in Atlassian Confluence Server and Data Center that may allow an unauthenticated attacker to execute arbitrary code. Any organization running Confluence Server or Data Center is potentially affected. It is significant because it is listed in CISA's Known Exploited Vulnerabilities catalog with known ransomware use, and EPSS assigns a 100.0% probability of exploitation within 30 days (100th percentile). Do: Apply updates to Confluence Server and Data Center per Atlassian's instructions, which is the required action in the CISA KEV listing. Prioritize remediation given confirmed in-the-wild exploitation and known ransomware use. | 9.8 | 100% | KEV ransomware PoC |
| — |
Full article717 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The warning comes after a similar advisory from the FBI and the Department of Homeland Security.
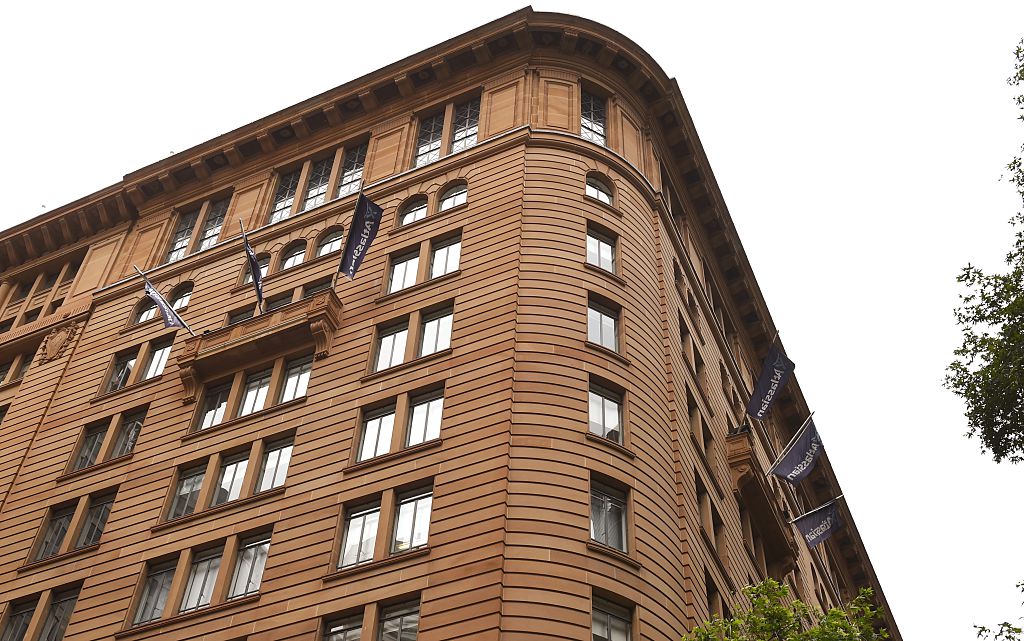
U.S. Cyber Command is warning American organizations that hackers are exploiting software flaws in a popular project management tool, an indication that attackers could be preparing for a larger campaign that creates headaches throughout the private sector.
Cyber Command — the Defense Department’s cyber unit — said in a tweet Friday that “mass exploitation” of the issue “is ongoing and expected to accelerate.” The issue exists in Atlassian Confluence, an enterprise application marketed as a means of enabling remote work in corporate environments. Atlassian, an Australian corporation, warned clients on Aug. 25 to update their systems to the latest version of Confluence.
“Please patch immediately if you haven’t already — this cannot wait until after the weekend,” the Cyber Command warning stated.
The message comes after the Department of Homeland Security’s cyber division, along with the FBI, warned firms to be on guard for ransomware attacks ahead of Labor Day, a holiday weekend in the U.S.
The ransomware attack at Colonial Pipeline that resulted in delayed fuel transportation occurred near Mother’s Day in May, followed shortly after by the breach at the food production corporation JBS, near Memorial Day. Another attack targeting Kaseya, a global IT firm, was timed roughly with Independence Day in the U.S.
“Ransomware continues to be a national security threat and a critical challenge, but it is not insurmountable,” Eric Goldstein, executive assistant director for cybersecurity at DHS’ Cybersecurity and Infrastructure Security Agency, said in a statement.
Specific details about the flaw in Atlassian’s Confluence software are sparse. The company said the issue, categorized as CVE-2021-26084, is an “injection vulnerability” that “would allow an authenticated user, and in some instances unauthenticated user, to execute arbitrary code on a Confluence Server or Data Center instance.”
The flaw is rated a 9.8 out of a possible 10 points on the Common Vulnerability Scoring System.
More Scoops
Iranian hackers launching disruptive attacks at U.S. energy, water targets, feds warn
Iranian government hackers are launching disruptive cyberattacks on American energy and water infrastructure, U.S. government agencies “urgently” warned Tuesday. The hackers are taking aim at devices and…
Top Senate Intel Dem warns of ‘catastrophic’ cyber consequences of Trump admin national security firings, politicization
Details emerge on BlackSuit ransomware takedown
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/atlassian-confluence-ransomware-cyber-command/