Earth Sirrush Espionage Activity May Support Sandworm Operations Against Ukraine
Earth Sirrush has spear-phished Ukrainian government and logistics since 2022, possibly feeding Sandworm.
TrendAI says Russia-aligned Earth Sirrush, also tracked as SHADOW-EARTH-065 and CERT-UA's UAC-0099, has spear-phished Ukrainian government, defense, border, and logistics targets since at least 2022 through July 2026. Early intrusions used archives, HTA files, and WinRAR flaw CVE-2023-38831; later chains added C# tools such as MATCHBOIL and the ASHVEIN stealer-RAT, image steganography in CINDERBLOT, and the LUNCHPOKE Notepad++ plugin. Shared signatures, XOR routines, and Regery-plus-Cloudflare infrastructure tie the clusters together. ESET's view that UAC-0099 may have given Sandworm initial access is presented as a hypothesis, not confirmed control.
- Spear-phishing of Ukrainian government, defense, border, and logistics since 2022.
- More than 10 families, including new stealer-RAT ASHVEIN (TelemetryBrowser).
- 2026 activity used PNG steganography and malicious Notepad++ plugin LUNCHPOKE.
- ESET hypothesis that UAC-0099 supplied Sandworm access remains unproven.
- C2 often used Regery domains, Cloudflare, and BL Networks AS399629.
Vulnerabilities mentionedAll →
- CVE-2023-388317.8100%Code Execution in RARLAB WinRAR via Crafted ZIP File/Folder Name Confusionpublished · RARLAB WinRAR KEV ransomware PoC ×4
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | cyberflysystems.com | istence, and deployment of the MeowMeow backdoor. The order.cyberflysystems[.]com download page with a fake antivirus badge (Source : Trend |
| domain | regery.com | onnections. Most confirmed command-and-control domains used Regery.com registration, Cloudflare fronting, and backend systems conc |
Full article605 words · extracted from gbhackers.com · click to collapse
Russia-aligned threat actor Earth Sirrush has sustained spear-phishing operations against Ukrainian government, defense, border security, and logistics organizations since at least 2022.
TrendAI Research’s analysis, covering activity through July 2026, identifies an evolving espionage toolkit whose persistent development and infrastructure patterns connect seemingly separate campaigns.
Previously tracked as SHADOW-EARTH-065, the intrusion set overlaps with CERT-UA’s UAC-0099 designation.
Early operations deployed LONEPAGE, SEAGLOW, and OVERJAM through malicious archives, HTA files, and exploitation of CVE-2023-38831.
Deep Instinct’s investigation documented fabricated court summons, disguised shortcuts, and scheduled tasks that repeatedly executed malicious scripts. Initial command-and-control communications frequently used plain HTTP over high-numbered ports.
During 2024 and 2025, Earth Sirrush increasingly adopted compiled C# tooling, introducing MATCHBOIL, MATCHWOK, and DRAGSTARE.
These components supported payload loading, encrypted task execution, credential collection, and reconnaissance. FortiGuard Labs’ related NordDragonScan analysis documented browser-profile theft, screenshot capture, document harvesting, and WMI-based system discovery.
ASHVEIN combines browser credential theft with GDI screenshot capture, file retrieval, PowerShell remote execution, and WMI fingerprinting.
It encrypts communications, detects analysis utilities, and conceals tasking inside invisible HTML elements. Some variants use GitHub-based dead-drop resolution for fallback connectivity.
Delivery mechanisms include DLL sideloading, VHD containers, and dedicated .NET droppers.
One component, AnswerFromPolice, displays a document impersonating Ukraine’s National Police while installing the implant, pairing credible institutional branding with background execution.
TrendAI Researchers identified more than 10 malware families, spanning PowerShell, Go, and .NET, including ASHVEIN, a previously undocumented information stealer and remote access trojan internally named “TelemetryBrowser.”
Earth Sirrush Espionage Activity
In 2026, the actor expanded image-based steganography. The CINDERBLOT campaign, also known as BadPaw, impersonated Ukraine’s State Border Guard Service.
ClearSky’s March report described malicious code extracted from an image, scheduled-task persistence, and deployment of the MeowMeow backdoor.

A subsequent campaign impersonated a drone-parts supplier, directing recipients to a polished website displaying a fraudulent “Verified by antivirus” badge.
Weaponized ZIP archives carried PNG-hidden payloads, including KittyCat.png. Different chains extracted executable data appended to images or reconstructed payloads from pixel data using PowerShell.
July activity introduced LUNCHPOKE, a malicious Notepad++ plugin using DLL proxying, alongside BURNYBEAR and MATCHBOIL.V2.
The chain staged payloads in randomized, user-writable directories and abused renamed schtasks.exe binaries. Parallel infections combined PNG extraction with Registry Run-key persistence.
Campaign continuity rests on several independent indicators: a reused PKCS #7 signature file, recurring developer artifacts, matching XOR routines, identical WMI queries, “TelemetryUP” branding, and shared staging conventions.
Infrastructure reinforces those connections. Most confirmed command-and-control domains used Regery.com registration, Cloudflare fronting, and backend systems concentrated in AS399629, operated by BL Networks one backend address connected ASHVEIN and CINDERBLOT domains.
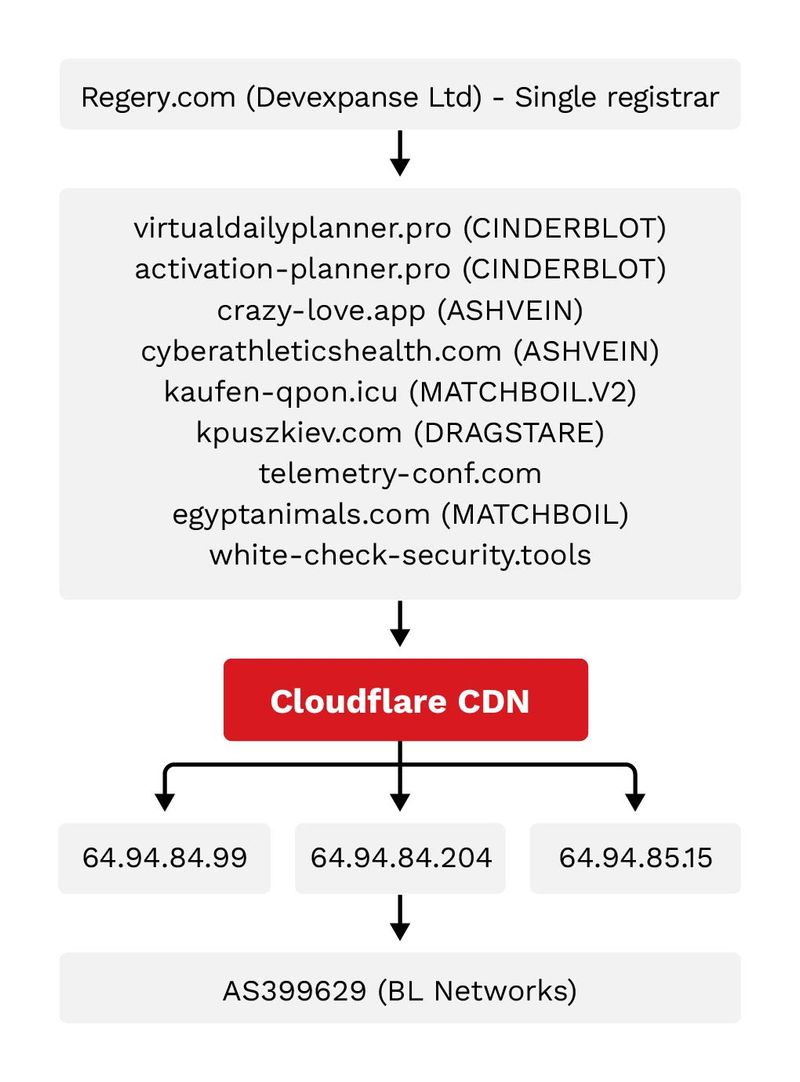
The supplied analysis cites ESET’s APT activity report as assessing that UAC-0099 might have provided Sandworm with initial access.
That remains a hypothesis, not proof of operational control. ESET separately documented Sandworm’s destructive targeting of Ukrainian government, energy, logistics, and grain organizations.
Defenders should prioritize suspicious Notepad++ plugin loading, renamed scheduling utilities, executable creation under public library directories, and payload-bearing images.
Browser-data access monitoring and PowerShell logging can expose collection activity.
Infrastructure matches should support behavioral investigation, not justify indiscriminate blocking of shared cloud services.
The operational risk is durable access: changing malware names does not erase the recurring behaviors connecting these espionage campaigns across Ukraine’s wartime supply chains.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.