Jenkins project discloses security breach following Confluence server hack
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2021-26084 | Atlassian Confluence Server and Data Center Object-Graph Navigation Language (OGNL) Injection Vulnerability CVE-2021-26084 is an OGNL injection vulnerability (CWE-917) in Atlassian Confluence Server and Data Center that may allow an unauthenticated attacker to execute arbitrary code. Any organization running Confluence Server or Data Center is potentially affected. It is significant because it is listed in CISA's Known Exploited Vulnerabilities catalog with known ransomware use, and EPSS assigns a 100.0% probability of exploitation within 30 days (100th percentile). Do: Apply updates to Confluence Server and Data Center per Atlassian's instructions, which is the required action in the CISA KEV listing. Prioritize remediation given confirmed in-the-wild exploitation and known ransomware use. | 9.8 | 100% | KEV ransomware PoC |
| — |
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | wiki.jenkins.io | d server, which hosted the now-defunct Jenkins wiki portal (wiki.jenkins.io), had already been deprecated since October 2019 when the p |
Full article383 words · extracted from therecord.media · click to collapse
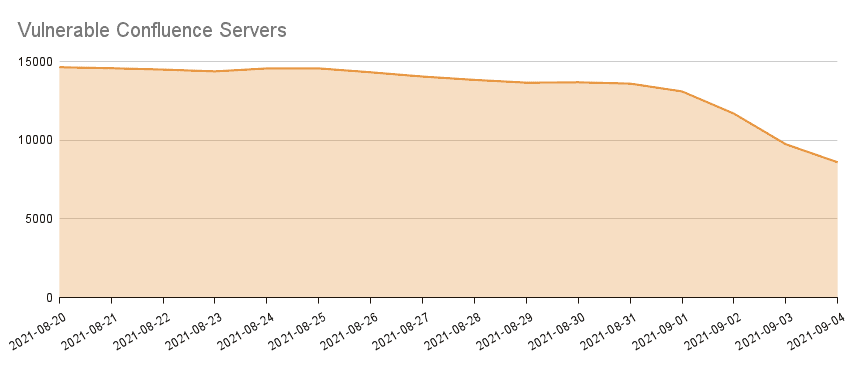
The developers of the Jenkins server, one of the most widely used open-source automation systems, said they suffered a security breach after hackers gained access to one of their internal servers and deployed a cryptocurrency miner. Despite the intrusion and malware deployment, the Jenkins team downplayed the severity of the breach in a statement published on Saturday. Jenkins admins said the hacked server, which hosted the now-defunct Jenkins wiki portal (wiki.jenkins.io), had already been deprecated since October 2019 when the project moved its wiki and team collaboration systems from a self-hosted Atlassian Confluence server to the GitHub platform. "At this time we have no reason to believe that any Jenkins releases, plugins, or source code have been affected," the Jenkins team said over the weekend. Following the discovery of the hack, Jenkins developers said they permanently took down the hacked Confluence server, rotated privileged credentials, and reset passwords for developer accounts. Breach part of the larger Confluence attack wave The Jenkins breach is part of a recent wave of attacks exploiting CVE-2021-26084 (also nicknamed Confluenza), an authentication bypass and command injection bug in Atlassian's Confluence server. As The Record first reported last Wednesday, attacks against Confluence servers began last week and ramped up after security researchers published a proof-of-concept exploit on GitHub. Attacks exploded throughout the week, prompting US Cyber Command to issue a public warning on Friday, urging administrators to patch affected systems before they left for the US Labor Day extended weekend. The attacks, which most deployed cryptocurrency miners, according to security firms Bad Packets and Rapid7, are still ongoing. According to internet monitoring project Censys, there are currently around 15,000 Atlassian Confluence servers that can be reached over the internet. According to Censys, on Sunday, September 5, there were 8,597 Confluence servers connected online and still vulnerable to CVE-2021-26084. Image: Censys Mass exploitation of Atlassian Confluence CVE-2021-26084 is ongoing and expected to accelerate. Please patch immediately if you haven’t already— this cannot wait until after the weekend.— USCYBERCOM Cybersecurity Alert (@CNMF_CyberAlert) September 3, 2021
No previous article
No new articles
Catalin Cimpanu
is a cybersecurity reporter who previously worked at ZDNet and Bleeping Computer, where he became a well-known name in the industry for his constant scoops on new vulnerabilities, cyberattacks, and law enforcement actions against hackers.
Text extracted automatically; images, tables and formatting may be missing. Original: https://therecord.media/jenkins-project-discloses-security-breach-following-confluence-server-hack