Critical ScreenConnect flaw now actively exploited in attacks
CISA confirms active exploitation of critical ConnectWise ScreenConnect flaw CVE-2026-84869, ordering federal agencies to mitigate within three days.
ConnectWise's ScreenConnect flaw CVE-2026-84869, an improper privilege management and missing authorization bug, lets attackers with basic privileges transfer or execute files through active remote sessions in low-complexity attacks without user interaction. It is patched in ScreenConnect 26.6.5; CISA added it to the KEV catalog and ordered US federal agencies to secure systems within three days. Shadowserver tracks over 1,000 unpatched exposed instances, mostly in North America (758) and Europe (180). This is the fourth actively exploited ScreenConnect flaw since 2024; earlier issues were abused by Kimsuky and ransomware gangs.
- CVE-2026-84869 allows unauthorized file transfer and execution without user interaction
- Patched in ScreenConnect 26.6.5; mitigation disables TransferFiles permissions
- CISA KEV addition with three-day deadline for federal agencies
- Over 1,000 unpatched instances exposed, mostly in North America
- Prior ScreenConnect flaws exploited by Kimsuky and ransomware gangs
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2024-1709 | Authentication Bypass in ConnectWise ScreenConnect Creates Rogue Admin Accounts ConnectWise ScreenConnect (ConnectWise Control), a widely used remote-access and remote-monitoring tool, contains an authentication bypass (CWE-288) in its management interface. An attacker needs only network access to the management interface to trigger the flaw, with no valid credentials or user interaction required. A successful attacker gains administrative control of the ScreenConnect server by creating a new administrator-level account, providing a foothold that has already been used in ransomware campaigns against downstream managed environments. Any organization running ConnectWise ScreenConnect is affected, especially managed service providers and IT teams whose management interface is reachable from the internet; the source data specifies affected products but no version ranges. Exploitation is confirmed and urgent: CISA added the flaw to the KEV on 2024-02-22 with known ransomware use, EPSS assigns a 100% probability of exploitation within 30 days, and ConnectWise warned that no patch was available at the time of disclosure. Do: Follow ConnectWise's instructions immediately: no patch existed at disclosure, so apply the vendor's mitigations or, per the CISA KEV required action, restrict internet exposure of the management interface or discontinue use until mitigations are available, then upgrade to the vendor's patched release as soon as it ships. Audit ScreenConnect servers for unexpectedly created administrator-level accounts and unusual remote sessions, which are the attack's artifacts. Prioritize any instance whose management interface is reachable from the internet, given confirmed in-the-wild exploitation and known ransomware use. | 10.0 | 100% | KEV ransomware PoC ×3 |
| masstens of thousands of internet-exposed ScreenConnect servers (on the order of 10,000-30,000 instances in public internet scans at disclosure), managing millions… | |
| CVE-2025-3935 | ViewState Code Injection in ConnectWise ScreenConnect May Lead to RCE ConnectWise ScreenConnect versions 25.2.3 and earlier rely on ASP.NET Web Forms ViewState, whose integrity depends on machine keys; if an attacker with privileged system-level access obtains those keys, they can craft and send a malicious ViewState that the server deserializes, potentially resulting in remote code execution. The risk stems from platform-level ASP.NET behavior rather than a defect introduced by ScreenConnect, and the ScreenConnect Client is not directly impacted, though the CVSS vector (PR:H) confirms exploitation requires already having high privileges on the host. An attacker who achieves this gains code execution on the server with the confidentiality, integrity, and availability impact reflected in the 7.2 High score. ScreenConnect 2025.4 mitigates the issue by disabling ViewState entirely and removing any dependency on it. The flaw was added to CISA's Known Exploited Vulnerabilities catalog on 2025-06-02, indicating confirmed exploitation in the wild, with EPSS estimating a 3.4% chance of exploitation in the next 30 days (88th percentile). Do: Upgrade to ScreenConnect 2025.4, which disables ViewState and removes any dependency on it, per vendor instructions and CISA BOD 22-01 requirements; if an upgrade is not immediately possible, apply vendor mitigations or discontinue use of the affected product. Because exploitation requires compromised machine keys, administrators who suspect prior privileged compromise should also review and rotate ASP.NET machine keys and investigate for signs of system-level access. Note ConnectWise is separately rotating ScreenConnect code signing certificates following a nation-state intrusion, so check vendor advisories for related hardening steps. | 7.2 | 3% | KEV |
| largetens of thousands of internet-exposed ScreenConnect servers (≈40,000+ in public scans), serving millions of managed endpoints | |
| CVE-2026-3564 | A condition in the ScreenConnect server component may allow an actor with access to server-level cryptographic material used for authentication to obtain unauth A condition in the ScreenConnect server component may allow an actor with access to server-level cryptographic material used for authentication to obtain unauthorized access, including elevated privileges, in certain scenarios. ScreenConnect host and guest client agents are not independently affected by this CVE. NVD description · AI analysis pending | 9.0 | <1% | — | — | ||
| CVE-2026-84869 | Missing authorization in ScreenConnect client allows unauthorized file execution CVE-2026-84869 is a critical authorization flaw (CWE-862 missing authorization, CWE-269 improper privilege management) in the ScreenConnect client, the endpoint-side agent of ConnectWise's widely used remote access and remote support platform, in which files can be transferred to a machine and executed during an active remote session without the expected authorization or without confirmation by the Host (technician). It is triggered in certain circumstances during an active session, with a network attack vector, low attack complexity, low privileges required, and no user interaction per the CVSS 3.1 vector. An actor who obtains or already holds access to a session context could thereby push and run files on the managed endpoint, potentially achieving code execution with high confidentiality, integrity, and availability impact (CVSS 3.1 score 9.9, scope changed). Only endpoints running the ScreenConnect client are affected; ScreenConnect servers are not impacted, and the affected client version ranges are governed by ConnectWise security advisory AV26-903 (not enumerated in the available data). The flaw is not currently known to be exploited: it is not in CISA KEV, no public proof of concept is known, and EPSS assigns a modest 0.4% probability of exploitation within the next 30 days (32nd percentile). Do: Follow ConnectWise security advisory AV26-903 and update ScreenConnect clients to the patched version it specifies, noting that ScreenConnect servers do not require remediation. Until patching is complete, monitor active remote sessions, require Host confirmation for file transfers, and review recent sessions on high-value endpoints for unexpected transferred or executed files; given no known exploitation and the active-session prerequisite, prioritize endpoints routinely accessed remotely. | 9.9 | <1% | KEV |
| massplausibly millions of managed endpoints running the ScreenConnect client agent |
Full article390 words · extracted from bleepingcomputer.com · click to collapse
Attackers now exploit a critical-severity ConnectWise ScreenConnect vulnerability in the wild, according to the U.S. Cybersecurity and Infrastructure Security Agency (CISA).
ConnectWise shared temporary mitigation measures for this missing-authorization flaw on September 7, advising security teams to disable TransferFiles permissions to block potential attacks.
The vulnerability (now tracked as CVE-2026-84869 and patched in ScreenConnect 26.6.5 and later) affects ScreenConnect clients and can let threat actors with basic privileges transfer or execute files in low-complexity attacks that don't require user interaction.
CISA added the security flaw to its catalog of actively exploited flaws on Friday and ordered U.S. federal agencies to secure their systems against ongoing attacks within three days.
"ConnectWise ScreenConnect contains both an improper privilege management and missing authorization vulnerability that may allow an attacker to file transfer and execution through an active remote sessions without authorization or host confirmation," CISA said. "These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the federal enterprise."
Since 2024, CISA has flagged four ScreenConnect security issues as actively exploited, two of which have also been abused in ransomware attacks.
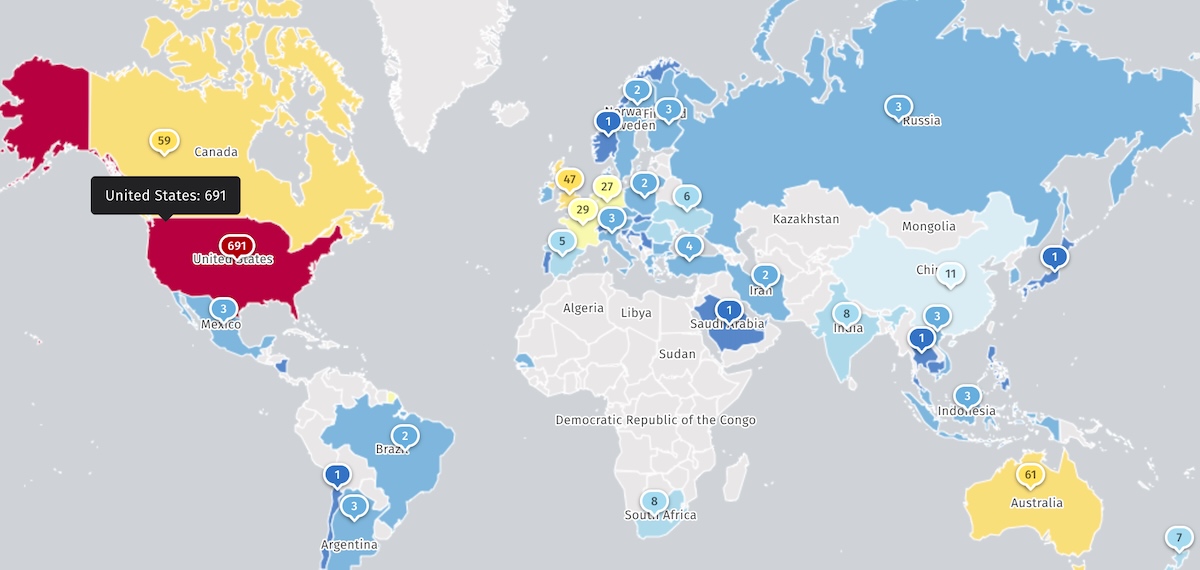
Internet threat watchdog Shadowserver now tracks over 1,000 ScreenConnect instances still unpatched and exposed to attacks online, most of them from North America (758) and Europe (180).
ScreenConnect vulnerabilities are often targeted in the wild by both financially-motivated and state-backed hacking groups.
For instance, the North Korean-backed Kimsuky hacking group and several ransomware gangs exploited another ScreenConnect flaw (CVE-2024-1709) in 2024.
Last year, ConnectWise also rotated digital code-signing certificates after disclosing that suspected state-sponsored hackers breached its systems through code injection attacks that exploited a ViewState flaw (CVE-2025-3935) and accessed the cloud-based instances of a limited number of customers.
More recently, in March, ConnectWise addressed a cryptographic signature verification vulnerability (CVE-2026-3564) that could allow attackers to hijack unpatched ScreenConnect servers.
ConnectWise provides services to more than 100,000 IT providers worldwide, with many managed service providers (MSPs) and IT teams using its ScreenConnect remote access platform for troubleshooting, patching, and system maintenance.
Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.bleepingcomputer.com/news/security/cisa-warns-of-hackers-exploiting-critical-screenconnect-flaw/