MATCHBOIL Malware Adds Sandbox Checks, .NET Reactor Obfuscation and Persistent C2
UAC-0099's MATCHBOIL downloader evolved with sandbox checks, .NET Reactor obfuscation, scheduled-task persistence, and recurring C2, hitting Ukrainian transport and energy firms.
ESET documents MATCHBOIL's evolution from a basic C# downloader into an evasive implant operated by UAC-0099, a group assessed with medium confidence as Russian-aligned that targets Ukrainian government, financial, and media organizations and can provide initial access for Sandworm. Samples from April 2024 to April 2026 added uptime checks via Windows event ID 6013, Debugger.IsAttached checks, Eziriz .NET Reactor obfuscation, decoy planner GUIs, and recurring two-minute C2 polling over a three-HTTPS-request protocol. The April 2026 MATCHBOIL.V2 variant ships as a DLL with a custom loader, installs SMTPClientApplication.exe, and persists via the MailClient\Checker scheduled task; C2 runs on VPS behind Cloudflare with Let's Encrypt certificates. Observed victims include Ukrainian transportation companies, a manufacturer, and an energy-sector organization.
- Sandbox evasion via Windows event ID 6013 uptime checks and Debugger.IsAttached.
- Delivered via spearphishing links dropping VBScript archives; deploys MATCHWOK backdoor.
- Persistence via DailyPlanner (7-minute) and MailClient\Checker scheduled tasks.
- C2 behind Cloudflare with Let's Encrypt; indicators include virtualdailyplanner[.]pro and telemetry-conf[.]com.
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | flycloud-service.com | lude virtualdailyplanner[.]pro , telemetry-conf[.]com , and flycloud-service[.]com . These network indicators, recurring HTTPS activity, une |
| domain | telemetry-conf.com | s. Published indicators include virtualdailyplanner[.]pro , telemetry-conf[.]com , and flycloud-service[.]com . These network indicators, |
| domain | virtualdailyplanner.pro | th Let’s Encrypt certificates. Published indicators include virtualdailyplanner[.]pro , telemetry-conf[.]com , and flycloud-service[.]com . The |
| sha1 | 026f892630d0a4fe854a75984695ba99af0022c4 | AnimalUpdater.exe MSIL/Agent_AGen.DGX MATCHBOIL downloader. 026F892630D0A4FE854A75984695BA99AF0022C4 bootloader.exe MSIL/Agent.XPZ MATCHBOIL downloader. Note: I |
| sha1 | a926889bab31f3c34663d18c05c4e862ef367028 | t.XXC MATCHBOIL DLL with C&C and payload persistence logic. A926889BAB31F3C34663D18C05C4E862EF367028 AnimalUpdater.exe MSIL/Agent_AGen.DGX MATCHBOIL downloader. |
| sha1 | b6569b0050b864c4a0d32326954bc2d3852a3958 |
Full article696 words · extracted from gbhackers.com · click to collapse
MATCHBOIL’s evolution from a basic C# downloader into a more evasive implant supporting recurring command-and-control communication.
Operated by UAC-0099, the malware now incorporates sandbox checks, commercial .NET obfuscation, deceptive interfaces, and revised persistence mechanisms, reflecting sustained development across samples spanning April 2024 through April 2026.
Compilation timestamps suggest earlier development, although timestamps alone do not establish deployment dates.
Observed infections affected Ukrainian transportation companies, a manufacturer, and an energy-sector organization.
UAC-0099 targets Ukrainian government organizations, financial institutions, and media. ESET assesses its alignment with Russian interests with medium confidence and notes that it can provide initial access for Sandworm.
The group also deploys LONEPAGE, a separate PowerShell downloader.
The downloader checks its installation location and collects machine identifiers, including processor information and BIOS serial numbers, to identify victims during C2 exchanges.
Its delivery protocol uses three HTTPS requests. The first retrieves a numeric value subsequently supplied through a custom HTTP header.
The second returns HTML containing a hexadecimal-encoded payload, which MATCHBOIL extracts using regular expressions and decodes into executable bytes. The third retrieves a string that can serve as configuration.
ESET’s investigation extends MATCHBOIL’s suspected development history beyond its first public documentation by CERT-UA in August 2025.
ESET Researchers said that, MATCHBOIL typically arrives through spearphishing links that deliver archives containing VBScript. Infection requires the recipient to execute the script, which downloads and launches the malware.
MATCHBOIL Malware
The downloaded executable is usually MATCHWOK, a C# backdoor associated exclusively with UAC-0099 in ESET’s reporting.
MATCHBOIL establishes persistence for that payload through scheduled tasks or registry entries; persistence for the downloader itself is handled separately by its delivery script or loader.
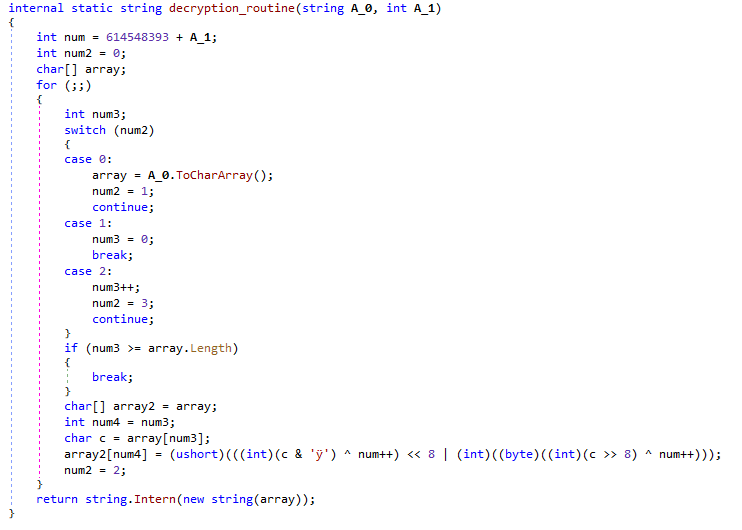
Early samples concealed class and method names with unprintable Unicode characters and encrypted strings using XOR operations and bitwise shifts.
By November and December 2025, the operators had switched to Eziriz .NET Reactor, whose protection features complicate reverse engineering.
Those later variants inspect Windows System event ID 6013, parsing English and Russian uptime messages.
One such change is an adjustment to the check of whether MATCHBOIL should run its malicious code: the operators have added the argument ‑plans that is executed along with the previous one, ‑auto.
MATCHBOIL treats the environment as suitable when it finds at least three events reporting uptime of 7,200 seconds or longer.
It also checks Debugger.IsAttached before starting a timer that executes C2 logic every two minutes.
This replaces the original one-shot delivery model with recurring retrieval, enabling subsequent download attempts and access to updated payloads.
Payload persistence also shifted: late-2025 samples created the UpdateCheckers\DailyPlanner scheduled task, configured to run every seven minutes.
Execution arguments separate malicious activity from decoy interfaces. Variants used -auto, later supplemented by -plans, while another adopted -renew.
Without the expected argument, users saw a daily planner or text-search utility instead.
The April 2026 variant, also described by CERT-UA as MATCHBOIL.V2, packages the downloader as a DLL executed by a custom C# loader.
It adds an operating-system installation-age check and installs its payload as SMTPClientApplication.exe under %LOCALAPPDATA%\SMTPClient, using the MailClient\Checker scheduled task for persistence.
ESET reports C2 infrastructure hosted on virtual private servers and concealed behind Cloudflare, with Let’s Encrypt certificates.
Published indicators include virtualdailyplanner[.]pro, telemetry-conf[.]com, and flycloud-service[.]com.
These network indicators, recurring HTTPS activity, unexpected scheduled tasks, and script-driven loader execution provide concrete investigation pivots across the documented variants.
The changes show an emphasis on resisting automated analysis while maintaining payload delivery rather than replacing the downloader’s core operational purpose.
IOCs
| SHA-1 | Filename | Detection | Description |
| B6569B0050B864C4A0D32326954BC2D3852A3958 | PlannerLibrary.dll | MSIL/Agent.XXC | MATCHBOIL DLL with C&C and payload persistence logic. |
| A926889BAB31F3C34663D18C05C4E862EF367028 | AnimalUpdater.exe | MSIL/Agent_AGen.DGX | MATCHBOIL downloader. |
| 026F892630D0A4FE854A75984695BA99AF0022C4 | bootloader.exe | MSIL/Agent.XPZ | MATCHBOIL downloader. |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.