Threat Advisory: Atlassian Confluence zero-day vulnerability under active exploitation
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2022-26134 | Unauthenticated OGNL Injection RCE in Atlassian Confluence Server/Data Center Atlassian Confluence Server and Data Center contain an unauthenticated remote code execution flaw caused by improper neutralization of expression-language (OGNL) input (CWE-917): an attacker with network access to the application can submit a crafted request that is evaluated as an expression and executed by the server. Successful exploitation lets a remote, unauthenticated attacker run arbitrary code with the privileges of the Confluence process, without any credentials. All organizations running self-managed Confluence Server or Data Center are affected, particularly instances exposed to the internet; Confluence Cloud is not listed among the affected products. Exploitation is confirmed in the wild: the flaw was added to CISA's KEV on 2022-06-02 with ransomware use marked as known, and EPSS assigns a 100% probability of exploitation within 30 days (100th percentile). CVSS has not yet been scored in this data, but the KEV listing and known ransomware use make unpatched, internet-facing instances a top-priority patching target. Do: Immediately upgrade to the patched Confluence release specified in Atlassian's 2022-06-02 security advisory, and until patched follow the CISA required action to block all internet traffic to and from affected instances. Because in-the-wild exploitation and ransomware use are confirmed, also hunt for compromise indicators on both patched and unpatched hosts, such as webshells, unexpected child processes of the Confluence service, and unusual outbound connections. | 9.8 | 100% | KEV ransomware PoC ×2 |
| largetens of thousands of internet-exposed instances (public scan counts of roughly 60,000-90,000 Confluence Server/Data Center hosts around the June 2022… |
Full article527 words · extracted from blog.talosintelligence.com · click to collapse
Friday, June 3, 2022 20:08
Cisco Talos is monitoring reports of an actively exploited zero-day vulnerability in Confluence Data Center and Server. Confluence is a Java-based corporate Wiki employed by numerous enterprises. At this time, it is confirmed that all supported versions of Confluence are affected by this vulnerability.
Vulnerability Details
The vulnerability, CVE-2022-26134, is reportedly associated with command injection. An attacker could exploit this vulnerability to execute remote code and, per reports, is being actively exploited in the wild. The attacks delivered several payloads, including the in-memory BEHINDER implant as well as webshells, including China Chopper. In addition to the initial attacks outlined in the report, researchers confirmed additional, continued exploitation is ongoing. There is now a Proof of Concept (PoC) available so exploitation could increase in the near term.
The vulnerability itself appears to be an OGNL injection vulnerability specifically impacting the web server and can be exploited via an HTTP request. It appears that all HTTP methods are vulnerable as well. The exploitation appears to be relatively straightforward and should be resolved immediately either through patching or other mitigations.
Mitigations
Atlassian has released a set of patches to mitigate the vulnerability. Enterprises are encouraged to test and apply the patch immediately to mitigate the ongoing attacks, patched versions include: 7.4.17, 7.13.7, 7.14.3, 7.15.2, 7.16.4, 7.17.4 and 7.18.1. Additionally, they have provided a series of steps to be performed to help mitigate the risk if the patches cannot be applied for any reason.
Coverage
Ways our customers can detect and block this threat are listed below.
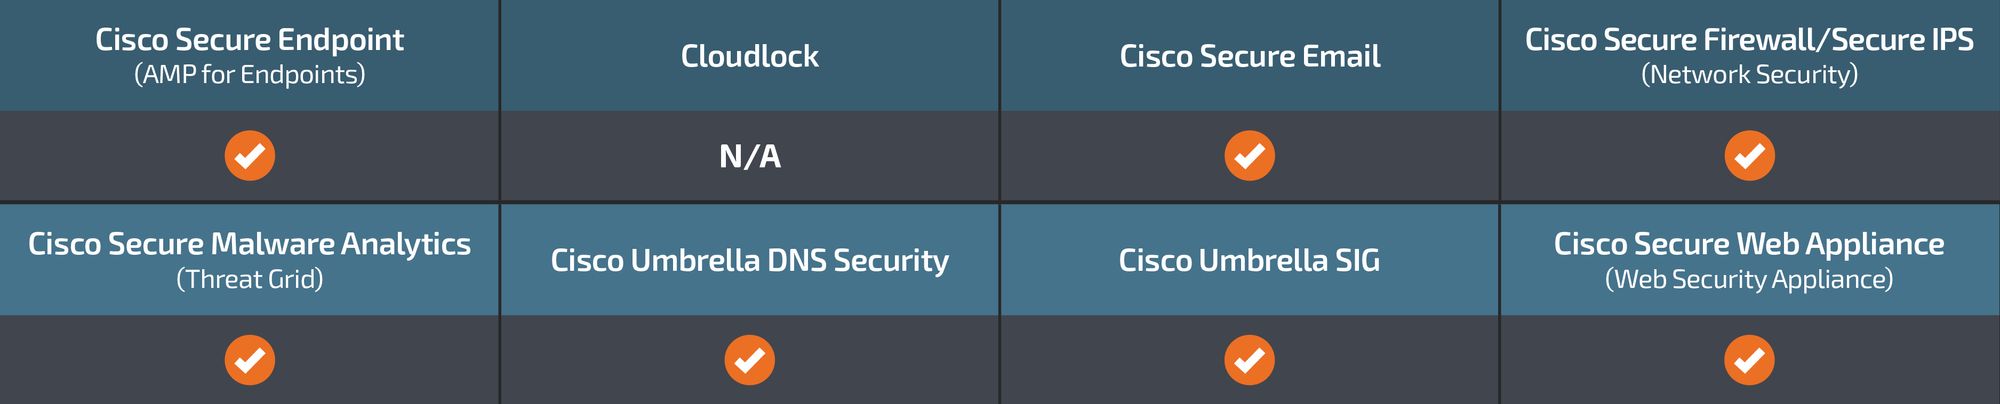
Cisco Secure Endpoint (formerly AMP for Endpoints) is ideally suited to prevent the execution of the malware detailed in this post. Try Secure Endpoint for free here.
Cisco Secure Web Appliance web scanning prevents access to malicious websites and detects malware used in these attacks.
Cisco Secure Email (formerly Cisco Email Security) can block malicious emails sent by threat actors as part of their campaign. You can try Secure Email for free here.
Cisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.
Cisco Secure Network/Cloud Analytics (Stealthwatch/Stealthwatch Cloud) analyzes network traffic automatically and alerts users of potentially unwanted activity on every connected device.
Cisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products.
Umbrella, Cisco's secure internet gateway (SIG), blocks users from connecting to malicious domains, IPs and URLs, whether users are on or off the corporate network. Sign up for a free trial of Umbrella here.
Cisco Secure Web Appliance (formerly Web Security Appliance) automatically blocks potentially dangerous sites and tests suspicious sites before users access them.
Additional protections with context to your specific environment and threat data are available from the Firewall Management Center.
Cisco Duo provides multi-factor authentication for users to ensure only those authorized are accessing your network.
Open-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org.
Talos created the following Snort coverage for CVE-2022-26134:
SIDs: 59925-59934
Text extracted automatically; images, tables and formatting may be missing. Original: https://blog.talosintelligence.com/atlassian-confluence-0day/