Over 61% of Exchange servers vulnerable to CVE-2020-0688 attacks
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2020-0688 | RCE in Microsoft Exchange Server from Shared Install-Time Validation Keys CVE-2020-0688 is a remote code execution vulnerability in Microsoft Exchange Server caused by the validation key not being uniquely created at install time, leaving deployments with a predictable, shared key (CWE-287, improper authentication). A remote attacker who can reach an affected Exchange server and knows the common install-time key can supply maliciously crafted, cryptographically signed payloads that the server trusts, triggering code execution without needing per-server secrets. Successful exploitation gives the attacker code execution on the Exchange server, which can be used to access mail data, move laterally, and stage follow-on activity; CISA notes known use in ransomware campaigns. All organizations running the affected on-premises Microsoft Exchange Server are in scope per CISA's listing, though the affected version range is not specified in the source data. Exploitation is confirmed in the wild: the flaw was added to CISA's KEV on 2021-11-03 with known ransomware use, and EPSS rates 30-day exploitation probability at 100% (top percentile). Do: Apply Microsoft's Exchange security updates addressing CVE-2020-0688 (released in February 2020) to every on-premises Exchange server, per CISA's required action. As an interim mitigation, configure a unique ASP.NET machineKey in each Exchange server's web.config instead of the default shared install-time key, and hunt for indicators of exploitation given the known ransomware use. | 8.8 | 100% | KEV ransomware PoC ×2 |
| masshundreds of thousands of on-premises Exchange servers (≈500,000) |
Full article504 words · extracted from securityaffairs.com · click to collapse
 Pierluigi Paganini
 September 30, 2020

More than 247,000 Microsoft Exchange servers are still vulnerable to attacks exploiting the CVE-2020-0688 RCE issue impacting Exchange Server.
The CVE-2020-0688 vulnerability resides in the Exchange Control Panel (ECP) component, the root cause of the problem is that Exchange servers fail to properly create unique keys at install time.
“Knowledge of a the validation key allows an authenticated user with a mailbox to pass arbitrary objects to be deserialized by the web application, which runs as SYSTEM.” reads the advisory published by Microsoft.
A remote, authenticated attacker could exploit the CVE-2020-0688 vulnerability to execute arbitrary code with SYSTEM privileges on a server and take full control.
Security experts Simon Zuckerbraun from Zero Day Initiative published technical details on how to exploit the Microsoft Exchange CVE-2020-0688 along with a video PoC.
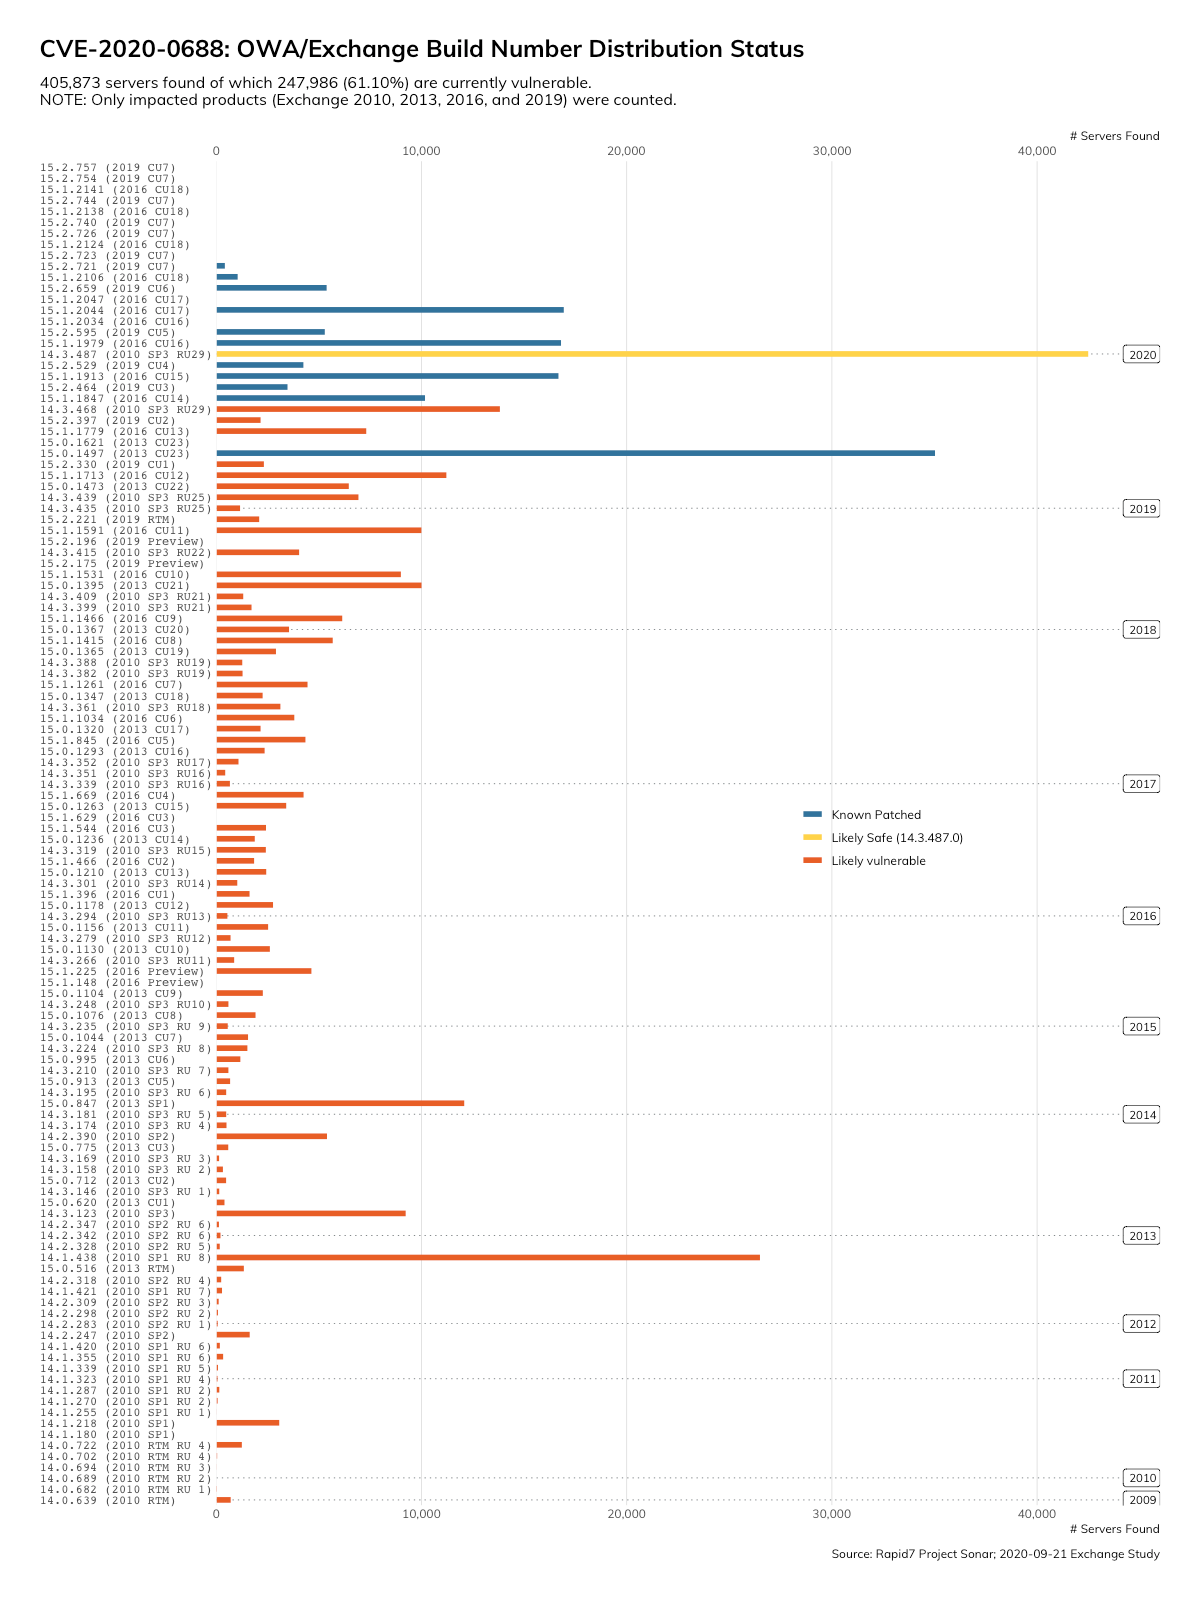
Microsoft addressed the vulnerability with the release of the Microsoft February Patch Tuesday updates, but more than 247,000 Microsoft Exchange servers (61% percent of Exchange servers installs) are yet to be fixed.
Rapid7 reported that 87% of almost 138,000 Exchange 2016 servers and 77% of around 25,000 Exchange 2019 servers are still vulnerable to CVE-2020-0688 attacks, and roughly 54,000 Exchange 2010 servers have not been updated in six years.
After Microsoft addressed the flaw experts reportedly observed that APT actors exploiting the flaw.
Researchers from Rapid7 reported that 61 percent of Exchange 2010, 2013, 2016 and 2019 servers are still vulnerable to the vulnerability.
“It’s been just under eight months since Microsoft released the patches to address CVE-2020-0688, so we thought it would be a good time to revisit patch deployment to see whether organizations have addressed this particular risk.” explained Tom Sellers with Rapid7 in a blog post. “Unfortunately, as of our study on Sept. 21, 2020, it appears that 61% of the target population (Exchange 2010, 2013, 2016, and 2019) is still vulnerable to exploitation.”
In March researchers from the cybersecurity firm Volexity warned of nation-state actors that were attempting to exploit the CVE-2020-0688 flaw.
Experts reccoments to determine whether Exchange has been updated and to install the update on any server with the Exchange Control Panel (ECP) enabled.
“The most reliable method to determine whether the update is installed is by checking patch management software, vulnerability management tools, or the hosts themselves to determine whether the appropriate update has been installed.” continues the post.”Note that these tools will likely not indicate that the update is missing if the Exchange Server isn’t running a current version of the Exchange Cumulative Update or Rollup. These servers are still vulnerable.”
According to the experts, admins could check the presence of compromised accounts used in attacks against Exchange servers by reviewing Windows Event and IIS logs for parts of encoded payloads including the “Invalid viewstate” text or the __VIEWSTATE and __VIEWSTATEGENERATOR strings for requests to a path under /ecp (usually /ecp/default.aspx).
Don’t waste time, check if your install is up to date.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Microsoft Exchange)
[adrotate banner=”5″]
[adrotate banner=”13″]
Text extracted automatically; images, tables and formatting may be missing. Original: https://securityaffairs.com/108946/hacking/vulnerable-exchange-servers.html