North Korean Lazarus Group Uses Windows Zero
Check Point links Lazarus Group's Operation Dream Job to a new Windows zero-day, CVE-2026-68820, targeting defense workers with fake Lockheed Martin job offers.
Check Point Research documented a new wave of Operation Dream Job, a North Korean Lazarus Group campaign targeting defense and aerospace professionals in France, Germany, Brazil, and India with fake Lockheed Martin job offers. The attacks chain a previously unknown Windows privilege escalation flaw in AFD.sys, CVE-2026-68820, which Microsoft patched on August 11, 2026, to deploy the MISTPEN downloader, ForestTiger backdoor, and updated FudModule 3.1 kernel rootkit. Check Point also discovered a new Troy backdoor DLL with 17 operator commands and a RelayShell PHP webshell deployed on compromised Roundcube and WordPress servers used as command relays, some infected via CVE-2025-49113 or leaked credentials. Defenders are urged to apply the August 2026 Patch Tuesday update and review Check Point's indicators of compromise.
- Lazarus used CVE-2026-68820, a privilege escalation flaw in AFD.sys, to gain SYSTEM and evade EDR visibility.
- Two infection chains deliver MISTPEN, ForestTiger, the FudModule 3.1 rootkit, and the new Troy backdoor.
- Troy is a single DLL implant supporting 17 operator commands including shell access and in-memory DLL injection.
- C2 relays run on compromised Roundcube webmail and WordPress sites infected via leaked credentials and CVE-2025-49113.
- Targets confirmed in France, Germany, Brazil, and India; applying the August Patch Tuesday fix is the priority.
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2025-49113 | Authenticated PHP Object Deserialization RCE in Roundcube Webmail Roundcube Webmail before 1.5.10 and 1.6.x before 1.6.11 contains a PHP object deserialization flaw (CWE-502) that allows remote code execution by authenticated users. The bug is in program/actions/settings/upload.php, where the _from URL parameter is not validated before deserialization, so any logged-in user can trigger it with a crafted URL to the settings upload action, with no user interaction required. Successful exploitation gives the attacker code execution on the web server with high confidentiality, integrity, and availability impact (CVSS 3.1 8.8). All deployments running affected versions are exposed, including Roundcube packages shipped with Debian Linux. The flaw reportedly existed for roughly a decade before disclosure, carries a 98.9% EPSS score (top percentile), and was added to CISA's KEV catalog on 2026-02-20, confirming exploitation in the wild. Do: Upgrade to Roundcube 1.6.11 or 1.5.10 (or later); Debian administrators should install the fixed roundcube package via security updates. Hunt for compromise by reviewing web access logs for requests to the settings upload action with unusual or crafted _from parameters, and check the web server runtime for unexpected processes, files, or webshells. Federal agencies must apply mitigations per vendor instructions under BOD 22-01 or discontinue use of the product if mitigations are unavailable. | 8.8 | 99% | KEV PoC ×2 |
| masslikely tens of thousands of internet-exposed Roundcube instances serving millions of mailboxes | |
| CVE-2026-68820 | Use-After-Free Local Privilege Escalation in Microsoft Windows WinSock AFD Driver CVE-2026-68820 is a use-after-free (CWE-416) in the Windows Ancillary Function Driver for WinSock (afd.sys), the kernel component that handles Winsock socket operations. A local, authenticated attacker can trigger the memory corruption through crafted socket activity, and the high attack-complexity score (AV:L/AC:H/PR:L) indicates exploitation requires a specific, likely race-sensitive sequence of operations. Successful exploitation elevates privileges to SYSTEM, giving the attacker full control of the host, and public reporting describes deployment of a backdoor after privilege escalation. Virtually every Windows 10, Windows 11, and Windows Server (2012-2022) installation ships this driver, so the affected population is essentially the entire supported Windows installed base. The flaw is being exploited in the wild: CISA added it to the KEV on 2026-08-11, Microsoft fixed it in the August 2026 Patch Tuesday release, and reporting ties active exploitation to North Korea's Lazarus group, who paired the zero-day with fake job-offer lures. Do: Apply Microsoft's August 2026 security updates for all listed Windows 10, Windows 11, and Windows Server versions as a priority; CISA KEV (added 2026-08-11) requires federal agencies to patch within two weeks in accordance with BOD 26-04. Because observed attacks used fake job-offer social engineering to reach local code execution, prioritize user workstations and review endpoints for unexplained SYSTEM-level process activity, newly installed services, or backdoor persistence artifacts. Where patching is deferred, restrict execution of untrusted local code on affected hosts and monitor for privilege-escalation events. | 7.0 | 6% | KEV |
| masshundreds of millions to over 1 billion Windows devices and servers (essentially all endpoints running the listed Windows 10/11/Server versions) |
Full article754 words · extracted from securityaffairs.com · click to collapse

Lazarus targets defense professionals with fake Lockheed Martin jobs, exploiting a Windows zero-day to deploy backdoors and evade security controls.
Check Point Research has uncovered a new wave of Operation Dream Job, the long-running North Korean campaign that lures defense and aerospace professionals with convincing fake job offers. This iteration is more dangerous than previous versions: it includes a previously unknown Windows vulnerability now patched as CVE-2026-68820, a newly documented backdoor called Troy, and command infrastructure built almost entirely from legitimate servers the attackers didn’t build, they hijacked them. Targets confirmed in France, Germany, Brazil, and India.
“The attackers used a previously unknown vulnerability in Windows (CVE-2026-68820) to gain full control of infected computers and evade EDR visibility. Check Point reported the issue to Microsoft, which released a fix before this research was published” reads the report published by Check Point Research. “Rather than running their own servers, the attackers are hijacking legitimate but compromised websites and webmail servers to relay commands, making the malicious traffic harder to distinguish from normal activity”
The vulnerability, CVE-2026-68820, is the same actively exploited zero-day that Microsoft patched on August 11 as part of Patch Tuesday, a privilege escalation flaw in AFD.sys, the kernel driver underlying Windows Sockets. Check Point reported the issue to Microsoft on July 28, Microsoft confirmed it three days later, and the fix shipped two weeks after that. The zero-day in this campaign and the zero-day under active exploitation are the same bug.
The attack runs through two parallel infection chains. In the first, victims download an encrypted archive containing a legitimate signed PDF viewer and a malicious DLL. The DLL displays a convincing Lockheed Martin job description while silently loading MISTPEN, a lightweight downloader that communicates through Microsoft Graph API and OneDrive. MISTPEN then runs reconnaissance modules, triggers the AFD.sys exploit to achieve SYSTEM privileges, and deploys ForestTiger, a well-documented Lazarus backdoor, along with an updated version of the group’s kernel-mode rootkit, FudModule 3.1, which can now tamper with Windows Smart App Control to bypass software verification.
“The second chain is more recent and shares several characteristics with a campaign described by ESET against the UAV sector in 2025. Victims are instructed to download SecurityPDF, a trojanized PDF viewer, from one of several websites impersonating Enveil, a legitimate privacy technology company with no actual connection to the attack. Once installed, the modified viewer inspects any PDF opened through it for a hidden marker.” continues the report. “When the marker is present, the application decrypts and launches an embedded payload that loads the Troy backdoor directly into memory.”
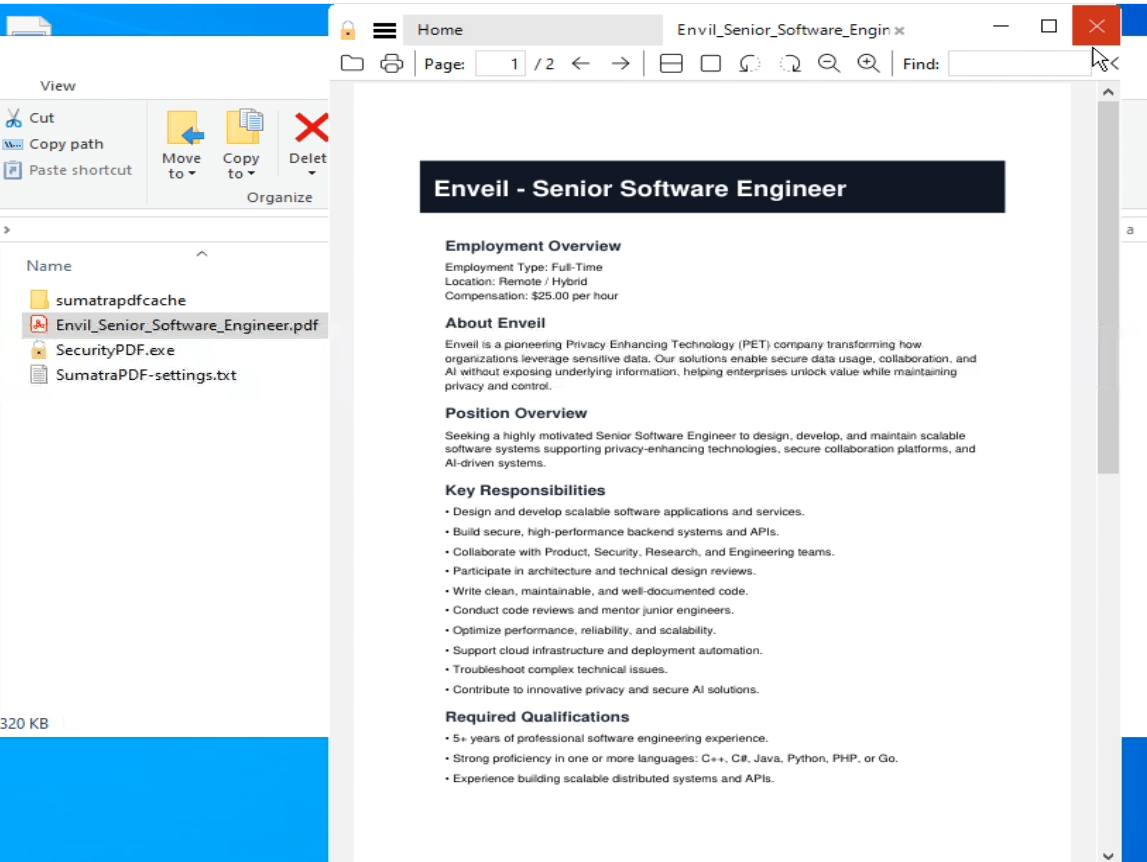
Troy is a single DLL implant that supports 17 operator commands covering file operations, shell access, process termination, in-memory DLL injection, and configuration updates. Its name comes from a PDB path embedded in the binary that Check Point also observed in earlier Lazarus samples. Enveil has no connection to the campaign; its brand was simply borrowed because it sounds credible to defense sector professionals.
The C2 infrastructure is built from compromised Roundcube webmail installations and WordPress sites, many vulnerable to CVE-2025-49113, infected with a previously undocumented PHP webshell called RelayShell. RelayShell functions as a relay rather than a traditional backdoor, exchanging commands and responses through simple text files. In at least one confirmed case, an already-breached French organization was used to send phishing messages to new victims — the attackers borrowed the company’s reputation to get past filters. Check Point identified at least 17 unique server identifiers in this relay network, with operators connecting through commercial VPNs to further obscure their location.
The most urgent action is applying the August 2026 Patch Tuesday update, which contains the CVE-2026-68820 fix. For organizations running public-facing Roundcube or CMS installations, the secondary risk is becoming part of the relay infrastructure rather than the intended target: the servers used in this campaign were compromised through leaked credentials and a known unpatched vulnerability, not anything exotic. The full indicators of compromise are in Check Point’s report.
“Given the combination of a zero day vulnerability that now have a patch, a new modular backdoor, and web based infrastructure designed to resemble legitimate traffic, security teams in these sectors should prioritize the August Patch Tuesday update, review the indicators of compromise published in Check Point Research publication, and apply the same level of scrutiny to unsolicited recruiting outreach that they would apply to any unverified download request.” concludes the report.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Lazarus)
Text extracted automatically; images, tables and formatting may be missing. Original: https://securityaffairs.com/197098/uncategorized/north-korean-lazarus-group-uses-windows-zero-day-in-operation-dream-job.html