New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads
Forescout identified ROMULUS, a six-server ClickFix platform delivering trojanized Stardock installers and LegionLoader.
Forescout described ROMULUS as a reusable ClickFix backend across six servers that serves PowerShell staging scripts and trojanized MSI installers. Huntress previously tied one node to attackers abusing ChatGPT Custom GPTs, fake verification pages, and Canon and Stardock apps for DLL sideloading. One route silently installs IconEdit2Turb.msi, which sideloads a malicious DLL through DeElevate64.exe and later stages a remote access trojan. A second route expands a heavily padded archive into LegionLoader, also known as Satacom, using smashshape.com with RC4 and Base64. Attribution remains unresolved and is distinct from Proofpoint’s RomulusLoader.
- Six ROMULUS servers expose matching panels and tokenized delivery routes.
- Stardock route uses decimal-IP downloads and silent msiexec DLL sideloading.
- LegionLoader route inflates a padded binary and calls smashshape.com with RC4.
- ClickFix PowerShell stages rebuild code, then delete themselves.
- No evidence links this platform to Proofpoint’s separate RomulusLoader.
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | orbitflownetwork.lol | rojan. The second route retrieved an encrypted archive from orbitflownetwork[.]lol and downloaded legitimate 7zr.exe from GitHub. Two passwo |
| domain | smashshape.com | Dropper. The analyzed LegionLoader configuration identified smashshape[.]com as its command server, using /nfront.php for registration |
| url | http://86.109.75[ | S node serving the Stardock-based package and LegionLoader. hxxp://86.109.75[.]7/s/19481b28bd67 Stage route paired with the Stardock-base |
Full article654 words · extracted from gbhackers.com · click to collapse
ROMULUS, a shared ClickFix delivery platform operating across six identified servers, with confirmed routes distributing a trojanized Stardock package and LegionLoader.
The discovery connects infrastructure from a recently documented ChatGPT Custom GPT abuse campaign to an independently investigated incident, exposing a reusable backend capable of delivering different malicious payloads.
The investigation began after researchers found malware on 86.109.75[.]7 matching samples previously delivered through 96.62.224[.]81.
Huntress linked the latter server to attackers abusing Custom GPTs to direct victims toward fake verification pages, where ClickFix instructions persuaded users to execute malicious PowerShell commands.
Its September 28 report documented Canon and Stardock applications abused for DLL sideloading.
VirusTotal and Shodan searches identified six IP addresses exposing matching ROMULUS authentication panels.
Their login pages submitted credentials to /api/login, stored returned tokens, and redirected authenticated users to the dashboard.
One server also exposed /stats.htm, displaying unique installations, total executions, historical activity, and geographic distribution.
Forescout said in a report shared with GBhackers, ROMULUS separates delivery through /s/<token> for PowerShell staging scripts and /app/<token> for trojanized MSI installers.
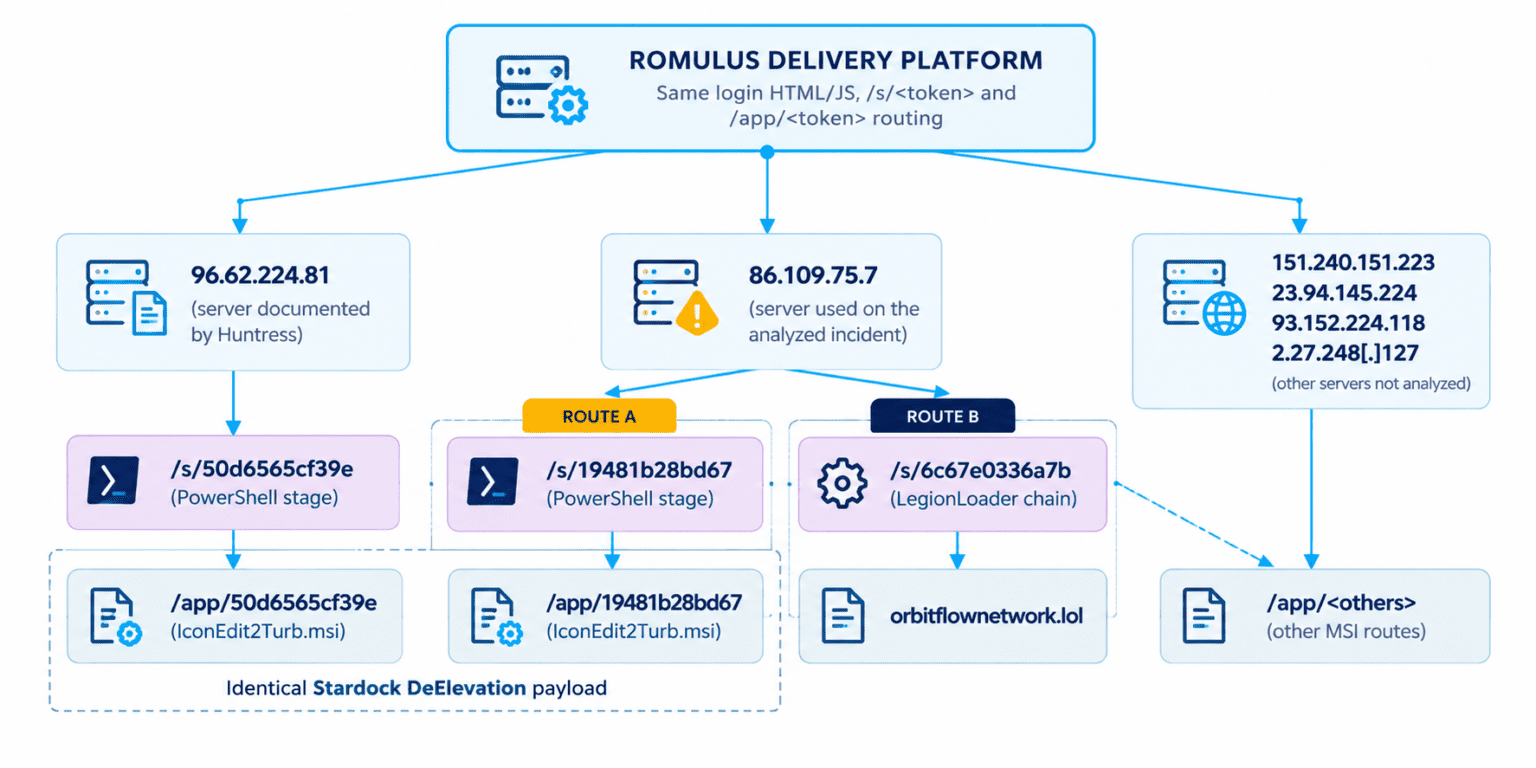
Observed tokens contain 12 hexadecimal characters, although their precise purpose remains unresolved.
ROMULUS Malware Platform
Different tokens selected different payload routes, indicating configurable delivery infrastructure rather than a server dedicated to one malware family.
Recovered scripts shared layered integer-array obfuscation, reconstructed executable code through [scriptblock]::Create, and deleted themselves after execution.
Payload-specific logic differed while the underlying staging template remained consistent.
The Stardock route downloaded IconEdit2Turb.msi using decimal IPv4 notation, representing 86.109.75[.]7 as 1450003207.
The script saved a GUID-prefixed installer in %TEMP%, removed its download-blocking marker, and invoked msiexec.exe silently with /qn and /norestart.
Installation launched legitimate DeElevate64.exe, which loaded a patched DeElevator64.dll. An added dependency redirected execution into malicious I++u.dll.
Huntress documented the same components, with subsequent loader stages using Build.dat and encrypted payload storage to deploy a remote access trojan.
The second route retrieved an encrypted archive from orbitflownetwork[.]lol and downloaded legitimate 7zr.exe from GitHub.
Two password-protected archive layers ultimately revealed five high-entropy binary files and an executable measuring 882,716,672 bytes.
Most of that executable consisted of repetitive padding inside its .reloc section. This allowed an archive smaller than one megabyte to expand into a file potentially exceeding scanning limits, sandbox budgets, or upload thresholds.
The meaningful executable content decrypted embedded shellcode using AES-256, reversed decrypted buffers, and manually mapped the final LegionLoader payload.
Malpedia also tracks LegionLoader as Satacom, CurlyGate, and RobotDropper.
The analyzed LegionLoader configuration identified smashshape[.]com as its command server, using /nfront.php for registration and tasking and /nback.php for results.
Messages used RC4 encryption followed by Base64 encoding, despite declaring application/x-www-form-urlencoded. AhnLab previously documented these endpoint roles, encryption patterns, and Chrome data collection capabilities.
Defenders should prioritize long PowerShell scripts executing from %TEMP%, decimal-IP downloads, hidden execution flags, silent MSI installation, and form-urlencoded POST requests containing a single Base64 blob.
Correlating these behaviors with process ancestry offers stronger coverage than filenames alone.
Operator attribution remains unresolved. Shared infrastructure does not establish common ownership of delivered malware, and investigators found no evidence connecting this platform to Proofpoint’s separately documented RomulusLoader.
That distinction prevents a shared name from becoming an unsupported attribution claim across otherwise separate investigations.
IOCs
| Indicator | Context |
|---|---|
96.62.224[.]81 / 1614733393 | Huntress-documented ClickFix delivery node. ROMULUS frontend observed. |
86.109.75[.]7 / 1450003207 | ROMULUS node serving the Stardock-based package and LegionLoader. |
hxxp://86.109.75[.]7/s/19481b28bd67 | Stage route paired with the Stardock-based IconEdit2Turb.msi. |
hxxp://86.109.75[.]7/app/19481b28bd67/IconEdit2Turb.msi | IconEdit2Turb.msi |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.