Fake ChatGPT, Claude and Gemini Ads Use Browser-in-the-Browser Phishing to Steal Accounts
Phishers impersonate ChatGPT, Claude, and Gemini ad tools, using fake browser windows to steal passwords and MFA approvals.
Island researchers documented a human-operated phishing platform that impersonates AI advertising products, including ChatGPT, Claude, Gemini, and Meta’s Muse, to steal advertising credentials. Clicking Connect opens a browser-in-the-browser window that fakes accounts.google.com or Okta while the real browser stays on the phishing site. Operators store up to three passwords and can request SMS codes, authenticator codes, Google prompts, or Okta push approvals over Socket.IO. Hundreds of submissions were seen, one Railway backend appeared across 25 domains, and hijacked manager accounts can expose multiple clients.
- Fake ChatGPT, Claude, Gemini, and Muse Ads pages target advertising staff.
- Browser-in-the-browser windows spoof Google and Okta sign-in.
- Operators capture three password attempts and live MFA challenges.
- Hundreds of submissions; one backend linked to 25 domains.
- Stolen manager accounts can add admins and divert ad spend.
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | account-sync-data.com | olled partner access intact. IOCs No. Category Domain 1 Ads account-sync-data.com 2 Ads ads-claude-beta.com 3 Ads ads-claude.com 4 Ads ads-te |
| domain | ads-claude-beta.com | IOCs No. Category Domain 1 Ads account-sync-data.com 2 Ads ads-claude-beta.com 3 Ads ads-claude.com 4 Ads ads-team-openai.com 5 Ads adsmis |
| domain | advertising-chatgpt.com | de.com 4 Ads ads-team-openai.com 5 Ads adsmistral.com 6 Ads advertising-chatgpt.com 7 Ads advertising-gemini.com Note: IP addresses and domains |
| domain | advertising-gemini.com | om 5 Ads adsmistral.com 6 Ads advertising-chatgpt.com 7 Ads advertising-gemini.com Note: IP addresses and domains are intentionally defanged ( |
| domain | socket.io | t another attempt, and preserve every submitted credential. Socket.IO carries victim submissions and commands through events incl |
Full article645 words · extracted from gbhackers.com · click to collapse
A human-operated phishing platform impersonating AI advertising products to steal credentials and manipulate multifactor authentication workflows.
The operation targets advertising professionals through convincing account-connection pages, with researchers observing hundreds of victim submissions and continued activity during their investigation.
Rather than presenting an obvious password request, the attackers sell a plausible business workflow: campaign optimization, spending audits, weekly performance briefings, or advertising integrations.
The newest lure, Muse Ads, appeared by September 16, eight days after Meta announced its Muse personal AI agent.
The fraudulent service described itself as an AI advertising manager and encouraged visitors to connect advertising accounts. Meta’s announcement described a personal agent, not this advertising product.
Other frontends tailor their language to agency workflows. ChatGPT-themed pages promise Monday Google Ads briefs, while Gemini-themed pages reference manager accounts and linked clients.
Terms such as MCC and ROAS make account connection appear operationally routine.
Related IRONSCALES research documented Gemini Ads invitations targeting paid-media personnel.
The messages passed SPF, DKIM, and DMARC checks and included functioning unsubscribe mechanisms, demonstrating how attacker-owned infrastructure can satisfy email authentication without establishing legitimacy.
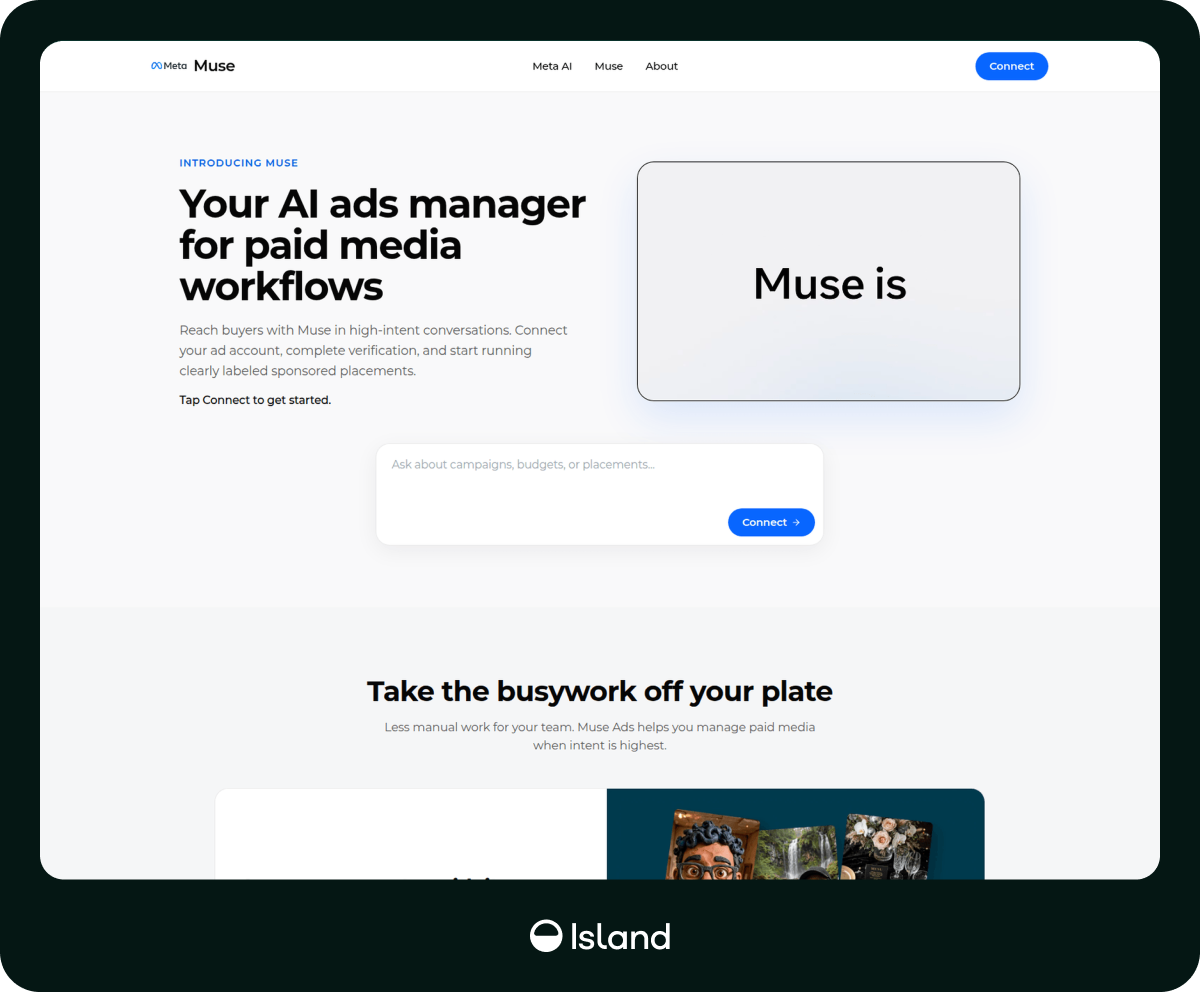
Island security Researchers uncovered that, Fake products borrow branding from ChatGPT, Claude, Gemini, Perplexity, Manus, and, most recently, Meta’s Muse.
AI Brand Phishing Campaign
Clicking Connect launches a Browser-in-the-Browser interface: a simulated browser window rendered within the malicious webpage.
Its fabricated address bar displays trusted origins, including accounts.google.com or an Okta tenant, while the real browser remains on the phishing domain.
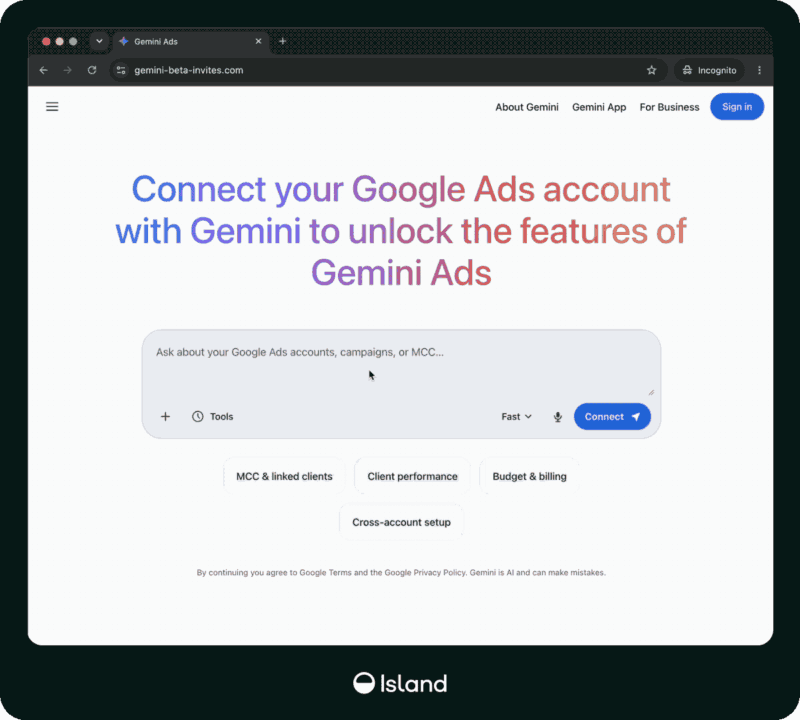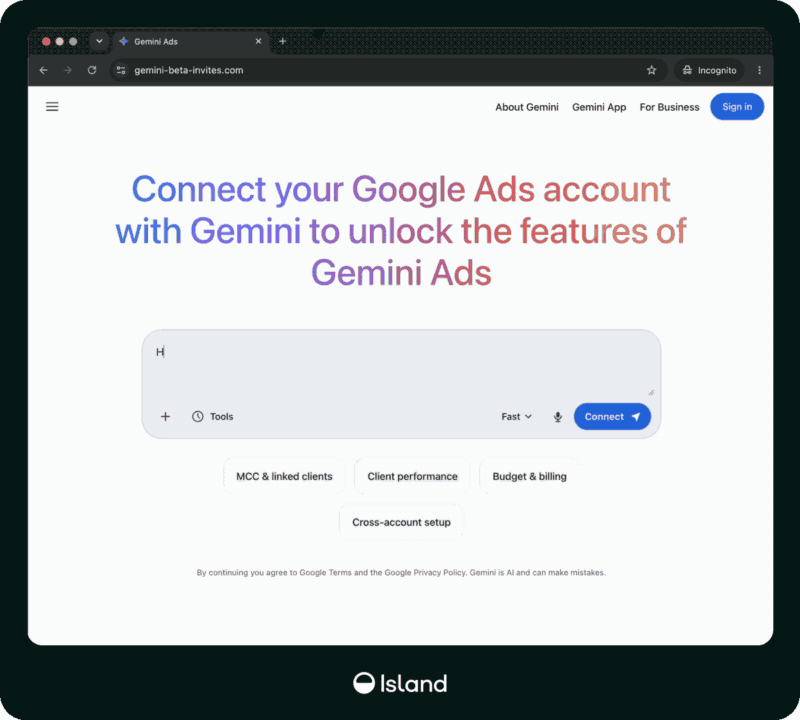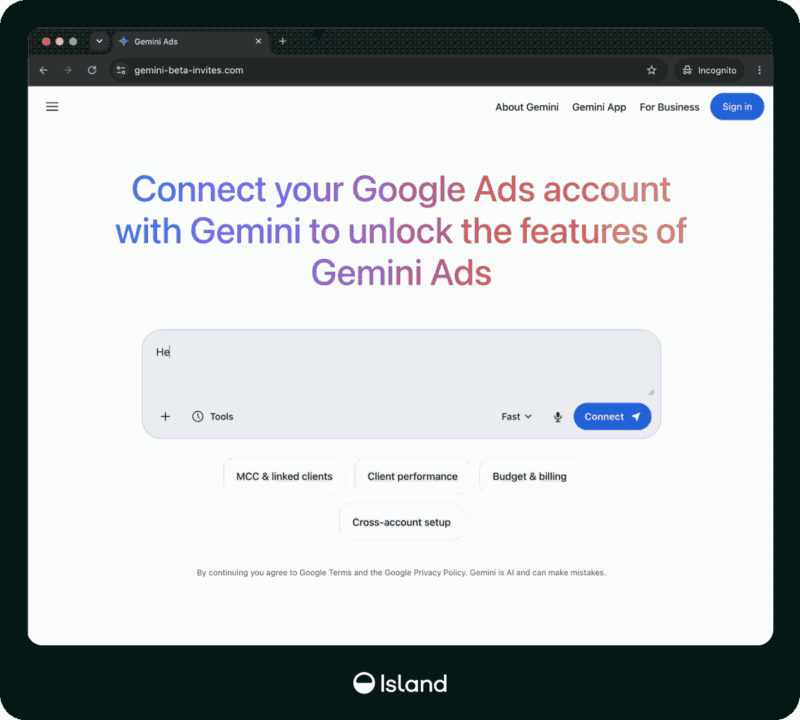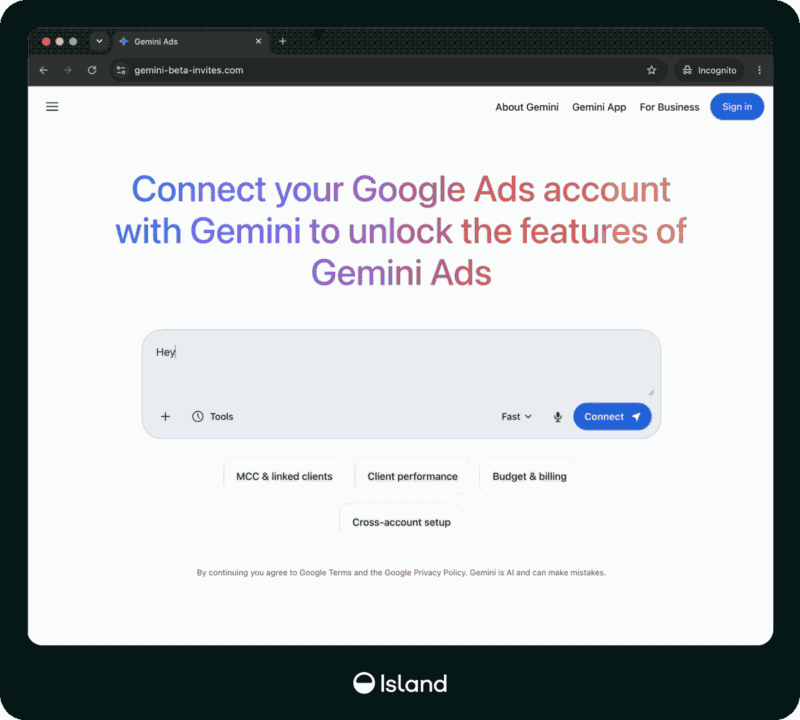
The interface adapts to Windows, macOS, iOS, and Android. Newer builds reproduce Safari address-bar styling, Chrome custom tabs, dark mode, and translucent toolbars to reduce visual inconsistencies.
Behind this presentation, the client creates a victim record through /api/create/user and submits device information through /api/send/ip. Collected attributes include IP address, location, screen dimensions, and WebGL characteristics.
The platform retains three separate password attempts under password_one, password_two, and password_three.
Operators can reject an entry, request another attempt, and preserve every submitted credential.
Socket.IO carries victim submissions and commands through events including operator-command and telegram-command.
Human operators can hold victims on waiting screens while attempting authentication against legitimate services.
Commands request SMS codes, authenticator codes, Google approval prompts, QR verification, numbered approval challenges, and Okta push authentication. Operators can reject codes, complete the interaction, or suppress the page.
Unlike a transparent reverse-proxy phishing kit, this platform reconstructs identity-provider interfaces locally and collects authentication data through its own APIs.
Its effectiveness depends on victims supplying credentials or approving attacker-triggered challenges; the fake window itself does not compromise the provider.
Island linked AI advertising, refund, and recruitment lures through a common Next.js and Socket.IO architecture.
One Railway backend appeared in 73 archived scans across 25 domains between May 27 and June 20.
Advertising identities are valuable because manager accounts can expose multiple clients. Mimecast research describes attackers adding administrators, hijacking spending, and reselling established accounts, with recovery sometimes taking months.
That recovery gap makes persistent administrative access especially consequential.
Mimecast recommends reviewing sessions, removing unfamiliar users and partners, pausing unauthorized campaigns, and auditing connected assets after suspected compromise. Password changes alone may leave attacker-controlled partner access intact.
IOCs
| No. | Category | Domain |
|---|---|---|
| 1 | Ads | account-sync-data.com |
| 2 | Ads | ads-claude-beta.com |
| 3 | Ads | ads-claude.com |
| 4 | Ads | ads-team-openai.com |
| 5 | Ads | adsmistral.com |
| 6 | Ads | advertising-chatgpt.com |
| 7 | Ads | advertising-gemini.com |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.