Citrix Urges Immediate Patching for Critical NetScaler Vulnerabilities
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
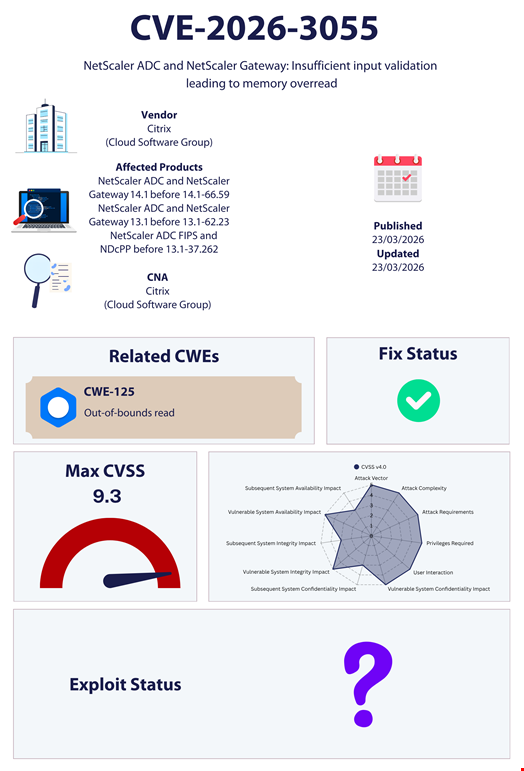
| CVE-2026-3055 | Out-of-Bounds Read in Citrix NetScaler ADC and Gateway When Used as SAML IDP CVE-2026-3055 is an out-of-bounds read (CWE-125) in Citrix NetScaler ADC and NetScaler Gateway caused by insufficient input validation when the appliance is configured as a SAML Identity Provider (IDP). An unauthenticated remote attacker can trigger the flaw by sending crafted input to the SAML IDP functionality, causing the appliance to read beyond the bounds of allocated memory and potentially disclose sensitive information from it. The CVSS 4.0 base score of 9.3 (critical) reflects a network-vector flaw requiring no privileges or user interaction. Only organizations running NetScaler ADC or NetScaler Gateway appliances with SAML IDP configured are affected, according to the available data. The flaw was added to CISA's Known Exploited Vulnerabilities catalog on 2026-03-30, carries an 87.2% EPSS probability of exploitation within 30 days, has a public proof-of-concept, and headlines indicate active reconnaissance and exploitation against NetScaler deployments, including federal patch directives. Do: Apply the patched NetScaler ADC and NetScaler Gateway releases from Citrix's advisory as soon as possible, prioritizing internet-facing appliances (exact fixed version numbers are not in this data; check the vendor bulletin). Determine whether SAML IDP is configured on your appliances and, if it is not needed, disable or unbind it as an interim mitigation while reviewing appliance logs for suspicious authentication or reconnaissance traffic. Federal agencies must follow the CISA required action and BOD 22-01 guidance, with CISA directing patching by the stated Thursday deadline. | 9.3 | 87% | KEV PoC |
| largetens of thousands of internet-exposed NetScaler ADC/Gateway appliances, with the directly exposed subset limited to those configured as SAML IDPs | |
| CVE-2026-4368 | Race Condition in NetScaler ADC and NetScaler Gateway when appliance is configured as Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA virtual server leadin Race Condition in NetScaler ADC and NetScaler Gateway when appliance is configured as Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA virtual server leading to User Session Mixup NVD description · AI analysis pending | 7.7 | 4% | — | — |
Full article563 words · extracted from infosecurity-magazine.com · click to collapse
Citrix has released a new critical security bulletin addressing two new vulnerabilities in its NetScaler Application Delivery Controller (ADC) and NetScaler Gateway.
The two products, formerly known as Citrix ADC and Citrix Gateway, are networking and security solutions used by enterprises to manage, optimize and secure application delivery and remote access.
CVE-2026-3055: Critical Out-of-Bounds Read
The first vulnerability, tracked as CVE-2026-3055 is a critical out-of-bounds read with a severity score (CVSS v4.0) of 9.3.
Identified internally by Citrix’s parent company, the Cloud Software Group, the flaw is due to insufficient input validation leading to memory overread. If exploited, it can enable an unauthenticated remote attacker to leak potentially sensitive information from the appliance's memory.
The products affected by CVE-2026-3055 include:
- NetScaler ADC and NetScaler Gateway versions 14.1 before 14.1-66.59
- NetScaler ADC and NetScaler Gateway 13.1 before 13.1-62.23
- NetScaler ADC FIPS and NDcPP before 13.1-37.262
However, according to Citrix’s advisory, published on March 23, these vulnerabilities only affect NetScaler systems explicitly configured as a SAML Identity Provider (SAML IDP). Default or standard configurations remain unaffected.
Additionally, Citrix noted that only customer-managed instances are affected, not cloud instances managed by Citrix.
Customers can determine if they have an appliance configured as a SAML IDP Profile by inspecting their NetScaler Configuration for the specified string: “add authentication samlIdPProfile .*.”
Cloud Software Group strongly urges affected customers to install the relevant updated versions as soon as possible, which include:
- NetScaler ADC and NetScaler Gateway 14.1-66.59 and later releases
- NetScaler ADC and NetScaler Gateway 13.1-62.23 and later releases of 13.1
- NetScaler ADC 13.1-FIPS and 13.1-NDcPP 13.1.37.262 and later releases of 13.1-FIPS and 13.1-NDcPP
NetScaler introduced the Global Deny List feature in its 14.1.60.52 versions. This new feature provides a method of adopting an instant-on patch to a running NetScaler without requiring a reboot.
Cloud Software Group has released Global Deny List signatures for mitigating CVE 2026-3055.
“Please note that to receive signatures meant for the Global Deny List, you must use NetScaler Console (Console On-prem with Cloud Connect or Console Service). Additionally, mitigation via Global Deny List signatures for CVE 2026-3055 is applicable only on 14.1-60.52 and 14.1-60.57 firmware builds,” the company noted.
“We recommend that you adopt fully patched builds as explained above. The Global Deny List feature is meant to be a method of quickly protecting your NetScaler so that upgrades can be done during a scheduled outage window.”
There is no known in-the-wild exploitation and no public proof-of-concept (PoC) exploit available at the time of writing.
CVE-2026-4368: High-Severity Race Condition Flaw
A second vulnerability, tracked as CVE-2026-4368 is a race condition flaw with a severity score (CVSS v4.0) of 7.7.
If exploited, CVE-2026-4368 can cause session mix up.
It affects NetScaler ADC and NetScaler Gateway version 14.1-66.54 if NetScaler is configured as Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA virtual server.
Customers can determine if they have an appliance configured as one of the following by inspecting their NetScaler Configuration for the specified strings
- An Auth Server (AAA Vserver): “add authentication vserver .*”
- A Gateway (VPN Vserver, ICA Proxy, CVPN, RDP Proxy): “add vpn vserver .*”
Affected customers are advised to install NetScaler ADC and NetScaler Gateway version 14.1-66.59 to apply the patch for CVE-2026-4368.
Image credits: JHVEPhoto / viewimage / Shutterstock.com
Read now: Salt Typhoon Uses Citrix Flaw in Global Cyber-Attack
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.infosecurity-magazine.com/news/citrix-patch-netscaler/