Chinese hacker used DeepSeek to launch autonomous cyberattacks on vulnerable servers
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2025-68613 | Authenticated RCE in n8n Workflow Automation Expression Evaluation n8n, an open source workflow automation platform, contains a critical remote code execution vulnerability (CVE-2025-68613, CWE-913) in its workflow expression evaluation system, affecting versions starting at 0.211.0 and prior to 1.120.4, 1.121.1, and 1.122.0. The flaw is triggered when expressions supplied by authenticated users during workflow configuration are evaluated in an execution context that is not sufficiently isolated from the underlying runtime, allowing the attacker to execute arbitrary code with the privileges of the n8n process. Successful exploitation can result in full compromise of the affected instance, including unauthorized access to sensitive data, modification of workflows, and execution of system-level operations. Any self-hosted or cloud n8n deployment running an affected version is exposed, with public scans indicating roughly 24,700 instances remain exposed on the internet. The flaw was added to CISA's Known Exploited Vulnerabilities catalog on 2026-03-11, EPSS places the 30-day exploitation probability at 99.1% (100th percentile), and Akamai has documented a ZeroBot malware campaign targeting n8n instances. Do: Upgrade immediately to n8n 1.120.4, 1.121.1, or 1.122.0 (or later), as the flaw is in CISA KEV and actively exploited by the ZeroBot malware campaign documented by Akamai. If immediate upgrade is not possible, restrict workflow creation and editing permissions to fully trusted users and run n8n in a hardened environment with restricted OS privileges and network access, keeping in mind these mitigations do not fully eliminate the risk. Review instances for signs of compromise, including unexpected workflow changes and suspicious process activity, and apply BOD 22-01 requirements if the product is used in federal cloud services. | 8.8 | 99% | KEV PoC |
| large≈24,700 internet-exposed n8n instances (public internet scan counts cited in exploit reporting) | |
| CVE-2026-21858 | Unauthenticated RCE in n8n Workflow Automation (Ni8mare) n8n versions 1.65.0 through below 1.121.0 contain an input-validation flaw (CWE-20) in the handling of certain form-based workflows, allowing an unauthenticated remote attacker to reach the underlying server through form endpoints. By triggering a vulnerable form workflow, the attacker can access files on the host and expose sensitive information stored there; the Cyera research team (which named the bug "Ni8mare") and the CVSS 10.0 score with high integrity impact indicate this yields unauthenticated remote code execution and potential full takeover. Any self-hosted n8n instance running an affected version that exposes form-based workflows over the network is at risk, with blast radius amplified by n8n's typical access to credentials, secrets, and connected internal systems. The issue is fixed in version 1.121.0; the flaw is not yet in CISA's KEV, but a public proof-of-concept is available and EPSS assigns a 78.4% probability of exploitation within 30 days, so defenders should treat exploitation as likely and imminent. Do: Upgrade n8n to version 1.121.0 or later immediately. If you cannot upgrade right away, check whether any workflows use form triggers and remove those form endpoints from untrusted network exposure — place them behind authentication, a reverse proxy, or an IP allowlist. Review instance logs for unexpected requests to form/webhook paths and unusual file access, given the high EPSS score and public proof-of-concept. | 10.0 | 78% | PoC ×2 |
| large≈50,000–100,000 internet-exposed n8n servers (self-hosted automation platform, affected range spans roughly a year of releases) | |
| CVE-2026-3055 | Out-of-Bounds Read in Citrix NetScaler ADC and Gateway When Used as SAML IDP CVE-2026-3055 is an out-of-bounds read (CWE-125) in Citrix NetScaler ADC and NetScaler Gateway caused by insufficient input validation when the appliance is configured as a SAML Identity Provider (IDP). An unauthenticated remote attacker can trigger the flaw by sending crafted input to the SAML IDP functionality, causing the appliance to read beyond the bounds of allocated memory and potentially disclose sensitive information from it. The CVSS 4.0 base score of 9.3 (critical) reflects a network-vector flaw requiring no privileges or user interaction. Only organizations running NetScaler ADC or NetScaler Gateway appliances with SAML IDP configured are affected, according to the available data. The flaw was added to CISA's Known Exploited Vulnerabilities catalog on 2026-03-30, carries an 87.2% EPSS probability of exploitation within 30 days, has a public proof-of-concept, and headlines indicate active reconnaissance and exploitation against NetScaler deployments, including federal patch directives. Do: Apply the patched NetScaler ADC and NetScaler Gateway releases from Citrix's advisory as soon as possible, prioritizing internet-facing appliances (exact fixed version numbers are not in this data; check the vendor bulletin). Determine whether SAML IDP is configured on your appliances and, if it is not needed, disable or unbind it as an interim mitigation while reviewing appliance logs for suspicious authentication or reconnaissance traffic. Federal agencies must follow the CISA required action and BOD 22-01 guidance, with CISA directing patching by the stated Thursday deadline. | 9.3 | 87% | KEV PoC |
| largetens of thousands of internet-exposed NetScaler ADC/Gateway appliances, with the directly exposed subset limited to those configured as SAML IDPs | |
| CVE-2026-33017 | Unauthenticated RCE in Langflow AI Workflow Builder CVE-2026-33017 is an unauthenticated remote code execution flaw in Langflow, an open-source tool for building and deploying AI-powered agents and workflows. The POST /api/v1/build_public_tmp/{flow_id}/flow endpoint, which by design requires no authentication for building public flows, accepts an optional data parameter; when present, attacker-controlled flow data — including arbitrary Python code embedded in node definitions — is used instead of the flow stored in the database and passed to exec() with no sandboxing. An attacker who can reach this endpoint on an affected instance can therefore execute arbitrary Python code without any credentials, typically yielding full compromise of the underlying server. All Langflow versions prior to 1.9.0 are affected; the issue was fixed in 1.9.0 and is distinct from CVE-2025-3248, which only added authentication to the /api/v1/validate/code endpoint. The flaw was added to CISA's KEV catalog on 2026-03-25 (confirming exploitation in the wild), carries a 96.2% EPSS probability of exploitation within 30 days, and related reporting describes Langflow RCE attacks, including ransomware activity targeting AI model files. Do: Upgrade all Langflow deployments to 1.9.0 or later. If immediate patching is not possible, keep Langflow off direct internet exposure (place it behind an authenticating reverse proxy or firewall) and review logs for unauthenticated POST requests to /api/v1/build_public_tmp/{flow_id}/flow that include a data parameter, which would indicate exploitation attempts. As a KEV entry, federal agencies must apply mitigations per vendor guidance and BOD 22-01, or discontinue use of the product if mitigations are unavailable. | 9.3 | 96% | KEV PoC ×4 |
| moderateon the order of several thousand internet-exposed Langflow instances (estimate) |
Full article583 words · extracted from helpnetsecurity.com · click to collapse
A Chinese threat actor operating under the aliases “knaithe” and “KnYuan” used multiple LLMs to automate cyberattacks against internet-facing systems with limited human intervention.
Researchers at Palo Alto Networks’ Unit 42 uncovered the operation after the threat actor’s AI agent misconfigured a file server, inadvertently exposing the entire infrastructure.
“This visibility enabled us to understand their full tool set, how the attackers orchestrated multiple AI platforms and gave us a peek into their targeting,” Unit 42 wrote.
“Based on our analysis of their session logs and configuration files, the actor primarily used the Hermes Agent with DeepSeek as its reasoning agent for the attack phase of this campaign. Their Hermes Agent conducted autonomous vulnerability enumeration, downloaded public exploit code from the internet and attempted exploits against targets,” the researchers explained.
After receiving instructions over Telegram, the agent worked autonomously. It searched internet-facing systems through the FOFA search engine, downloaded exploit code from GitHub, and launched attacks without requiring further operator input.
Beyond DeepSeek, the threat actor deployed several other LLMs, including Qwen, GLM, Kimi, and MiniMax. Researchers also found evidence of limited testing of Western AI tools. Claude Code appeared only in connectivity checks and proxy tests, while Codex artifacts were found in exploit development directories.
“This limited usage is consistent with evaluating the AI-market to identify their preferred tool set.”
AI agent prioritized and tested exploits
In one recovered session, the AI agent targeted a Langflow vulnerability tracked as CVE-2026-33017, rated 9.8 in severity. It downloaded a public exploit from GitHub, identified 84 exposed Langflow servers through FOFA, and assessed them for exploitation. Only one appeared potentially vulnerable, but the attack ultimately failed because the required configuration was not enabled.
“The exploitation attempts failed because the vulnerability requires either auto_login enabled or a public flow ID and the target had neither. DeepSeek assessed the entire product as a low-value target,” Unit 42 said.
The AI agent then analyzed public exploit repositories, weighing vulnerability severity against deployment scale before selecting n8n, a workflow automation platform that FOFA identified on more than 647,000 internet-exposed servers worldwide, including more than 25,000 in China.
It selected an exploit chaining two vulnerabilities: CVE-2026-21858, an arbitrary file read flaw with a CVSS score of 10.0, and CVE-2025-68613, a sandbox escape vulnerability leading to remote code execution with a CVSS score of 9.9.
Although both flaws had already been patched in newer n8n releases, the AI agent determined that version 1.117.3 predated both fixes and was therefore vulnerable to the exploit chain.
“This autonomous process of target identification, sampling and narrowing of scope is notable because the system executed hundreds of hours of manual targeting analysis in mere minutes, while also managing its own compute resources,” the researchers noted.
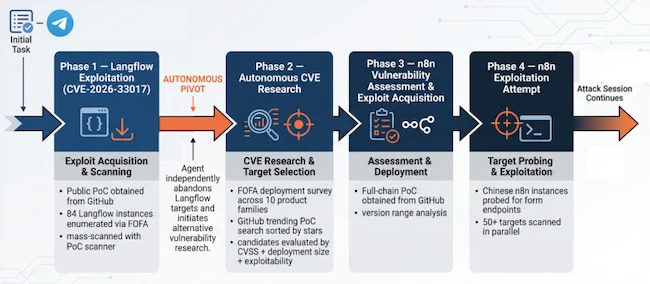
Autonomous attack flow observed in Hermes Agent session (Source: Palo Alto Networks)
Although none of the autonomous attacks resulted in a successful compromise, Unit 42 described the workflow as “a functional, end-to-end autonomous offensive capability.”
Manual attacks delivered the results
Outside the AI-driven sessions, the threat actor also conducted hands-on attacks against more than 460 systems, targeting known vulnerabilities in Citrix NetScaler, Apache Tomcat, Marimo Notebook, and Windows IKE VPN, among others.
Three of the manual attacks succeeded, all exploiting CVE-2026-3055 in Citrix NetScaler appliances. The attackers extracted data directly from device memory and searched it for authentication cookies that could be be used to hijack active user sessions.
“The technical barrier to AI-augmented offensive operations is low and continues to decrease,” the researchers concluded.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.helpnetsecurity.com/2026/08/03/deepseek-ai-autonomous-cyberattacks-hermes-agent/