CVE-2026-9586 | Sangoma Switchvox Unauthenticated SQL Injection Remote Code Execution Vulnerability
CVE-2026-9586, a critical unauthenticated SQL injection to RCE in Sangoma Switchvox, is being actively exploited against internet-facing systems per honeypot observations.
CVE-2026-9586 (CVSS 4.0: 9.3) is an unauthenticated SQL injection in the /pa endpoint of Sangoma Switchvox SMB Edition, where the unsanitized PhoneIP value in XML phone notification requests reaches the PostgreSQL database. Horizon3 demonstrated escalation to OS command execution, and honeypots run with Defused Cyber observed exploitation attempts on August 30, 2026, using PostgreSQL commands with nc and curl. Fixed in Switchvox 8.4.0.2 released July 14, 2026; one attacker IP (176.65.148.184) was documented.
- Unauthenticated network RCE via SQL injection in Polycom notification handling
- Exploitation attempts observed on honeypots starting August 30, 2026
- Fix shipped in Switchvox 8.4.0.2 on July 14, 2026
- db-quirks.log can show injected PostgreSQL statements for investigators
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2026-9586 | Unauthenticated SQL Injection RCE in Sangoma Switchvox SMB Edition Sangoma Switchvox SMB Edition 8.3 (build 104997) contains an unauthenticated SQL injection flaw (CWE-89) in its /pa endpoint, where the user-controlled PhoneIP value from XML input is concatenated directly into PostgreSQL queries without sanitization or parameterization. A single crafted request lets a remote, unauthenticated attacker execute arbitrary SQL statements against the backend PostgreSQL database, which can be escalated to remote code execution on the server. Any organization running the affected Switchvox SMB Edition build is exposed, especially appliances reachable from the internet. Exploitation is confirmed in the wild: the flaw was added to CISA's KEV catalog on 2026-09-02, and researchers have observed attackers using it without credentials to deploy reverse shells and cryptocurrency miners. Do: Identify all Switchvox SMB Edition deployments and verify the running build (affected: 8.3, build 104997), then upgrade to the patched release specified in Sangoma's advisory. If patching is delayed, restrict or remove internet exposure of the Switchvox web interface, including the /pa endpoint. Hunt for indicators of compromise such as unexpected reverse shells, new processes, or crypto-miner activity, as active exploitation is confirmed and the flaw is on CISA's KEV catalog, making it subject to BOD 26-04 patching guidance for federal stakeholders. | 9.3 | 12% | KEV PoC |
| moderatelikely on the order of thousands of on-prem PBX deployments (est.) |
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| ipv4 | 176.65.148.184 | pts originating from: Indicator Type Description IP Address 176.65.148.184 was observed targeting the vulnerable Switchvox /pa endpoin |
| ipv4 | 8.2.2.1 | release notes describe CVE-2026-9586 as affecting Switchvox 8.2.2.1, while the CNA record specifies 8.3 (104997). Organizations |
| ipv4 | 8.4.0.2 | goma Switchvox SMB Edition 8.3 (104997), versions less than 8.4.0.2 The available public sources contain some inconsistency reg |
Full article664 words · extracted from horizon3.ai · click to collapse
Sangoma Switchvox Unauthenticated SQL Injection Remote Code Execution Vulnerability
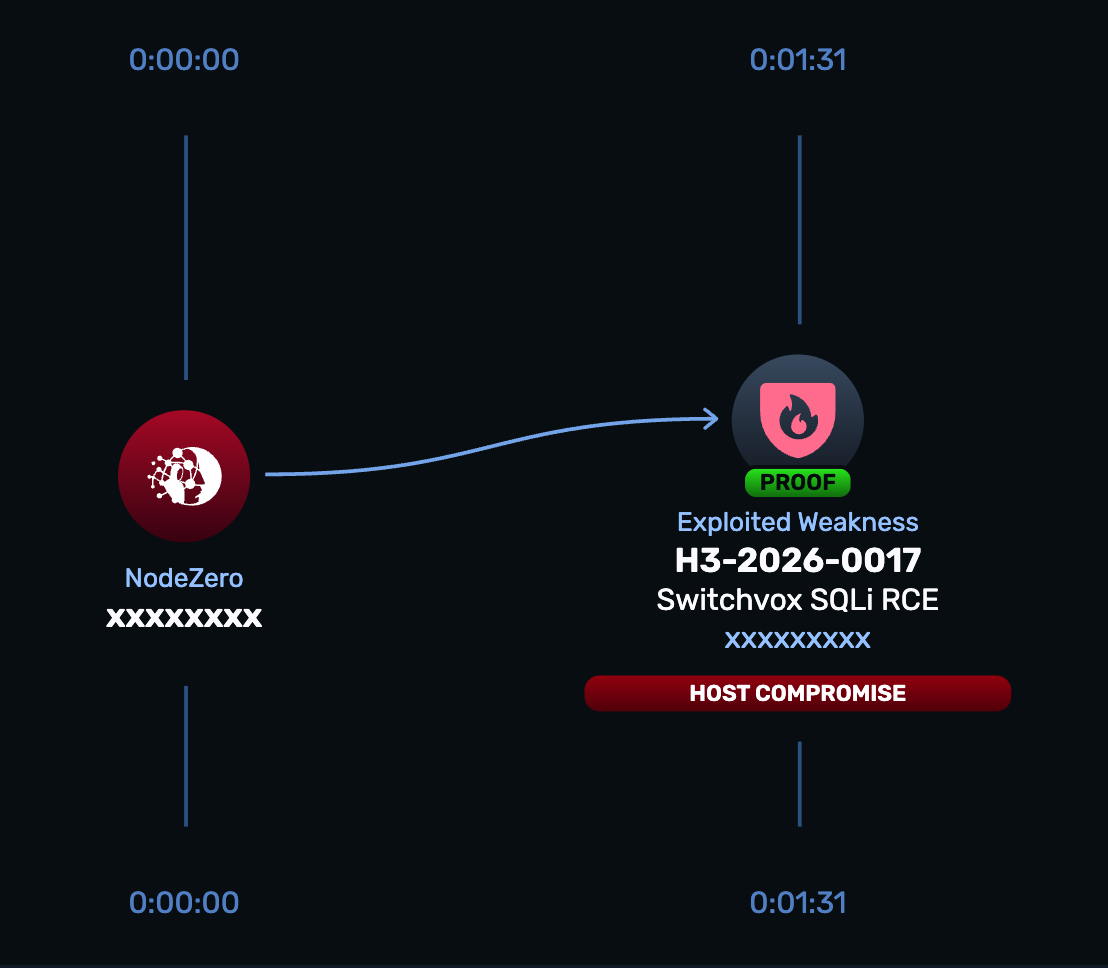
CVE-2026-9586 is a critical unauthenticated SQL injection vulnerability in Sangoma Switchvox SMB Edition that allows a remote attacker to execute arbitrary SQL statements against the backend PostgreSQL database and achieve remote code execution without authentication or user interaction. The vulnerability has a CVSS 4.0 score of 9.3 Critical . Horizon3 independently discovered the vulnerability while researching the Sangoma ecosystem and has since observed valid exploitation attempts targeting the vulnerability in the wild.
Technical Details
CVE-2026-9586 exists in the unauthenticated /pa HTTP endpoint used by Switchvox to process phone notification requests. The endpoint accepts XML content beginning with <PolycomIPPhone> and extracts the user-controlled PhoneIP value from the request.
The vulnerable PhoneAppsHandler.pm component concatenates the PhoneIP value directly into a PostgreSQL query without sanitization or parameterization. An unauthenticated remote attacker can therefore inject arbitrary SQL through a single crafted request. Horizon3 demonstrated that exploitation can reach operating-system command execution through PostgreSQL, resulting in remote code execution on the Switchvox system.
Key characteristics include:
Attack vector: Network
Attack complexity: Low
Attack requirements: None
Privileges required: None
User interaction: None
Weakness: CWE-89, Improper Neutralization of Special Elements used in an SQL Command
Impact: Arbitrary SQL execution and remote code execution
CVSS 4.0: 9.3 Critical
The published CVSS vector is CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N.
Horizon3 and Defused Cyber subsequently observed exploitation attempts against multiple internet-facing Switchvox honeypots using the vulnerable /pa endpoint. The activity included attempts to execute operating-system commands and enumerate processes on the targeted system.
Stop Guessing, Start Proving
NodeZero® Proactive Security Platform — Rapid Response
A NodeZero Rapid Response test has been developed to safely validate whether this vulnerability can be exploited in your environment. The test executes real attack techniques without causing damage, giving teams immediate clarity on exposure.
Run the Rapid Response test: Launch from the NodeZero platform to determine whether CVE-2026-9586 can be exploited
Patch immediately: Upgrade affected Switchvox systems to version 8.4.0.2 or later
Re-run the test: Confirm the vulnerability is no longer exploitable after remediation
Indicators of Compromise
Horizon3 and Defused Cyber observed exploitation attempts originating from:
Indicator Type Description
IP Address 176.65.148.184 was observed targeting the vulnerable Switchvox /pa endpoint
Organizations with SSH access to a Switchvox system can inspect /var/log/switchvox/db-quirks.log for evidence of injected SQL statements. In the activity observed by Horizon3 and Defused Cyber, the attacker attempted to use PostgreSQL command execution to invoke nc and later used curl to send process information to attacker-controlled infrastructure.
The presence of these utilities alone should not be treated as evidence of compromise. Investigators should correlate suspicious commands with requests targeting /pa, injected PostgreSQL statements, outbound connections, and other host or network telemetry.
Affected versions & patch
Affected
The published CVE record identifies:
Sangoma Switchvox SMB Edition 8.3 (104997), versions less than 8.4.0.2
The available public sources contain some inconsistency regarding earlier versions. Sangoma’s 8.4.0.2 release notes describe CVE-2026-9586 as affecting Switchvox 8.2.2.1, while the CNA record specifies 8.3 (104997). Organizations running earlier Switchvox releases should therefore upgrade to the fixed release rather than relying on an assumption that an older version is unaffected.
Fixed
Switchvox 8.4.0.2 , released July 14, 2026, contains the fix for CVE-2026-9586.
Timeline
April 10, 2026: Horizon3 reported vulnerabilities in Switchvox to Sangoma via GitHub Issues.
April 10, 2026: Sangoma acknowledged receipt of the report.
April 21, 2026: Sangoma provided a pre-release build containing fixes for Horizon3 to validate.
May 8, 2026: Horizon3 deployed internet honeypots in coordination with Defused Cyber to monitor for exploitation.
May 11, 2026: Security Risk Advisors independently reported Switchvox vulnerabilities.
July 14, 2026: Sangoma released Switchvox 8.4.0.2 containing the fix for CVE-2026-9586.
July 17, 2026: CVE-2026-9586 was publicly published, and Security Risk Advisors released its independent Switchvox vulnerability research.
August 30, 2026: Defused Cyber honeypots detected valid exploitation attempts targeting CVE-2026-9586.
September 1, 2026: Horizon3 published research detailing CVE-2026-9586 and the observed exploitation activity.
References
Sangoma Switchvox 8.4.0.2 Release Notes
CVE.org Record – CVE-2026-9586
NIST NVD – CVE-2026-9586
Security Risk Advisors: Sangoma Switchvox Vulnerability Disclosure
Text extracted automatically; images, tables and formatting may be missing. Original: https://horizon3.ai/attack-research/vulnerabilities/cve-2026-9586/