RemControl Android Malware Targets 30+ Banking Apps to Steal PINs and Credentials
RemControl Android trojan overlays 30-plus banking apps, stealing PINs and streaming screens through accessibility abuse.
Group-IB reports RemControl, an Android banking trojan operated as malware-as-a-service since at least May 2026, with the earliest operator tracked as UNKK. Campaigns use fake Google Play pages impersonating TVTap, geolocation and User-Agent checks, and malvertising to deliver a dropper that blocks Play Protect connectivity and signs each payload uniquely. After Accessibility Service access, it overlays more than 30 banking apps across Europe, the Middle East, and Canada to steal PINs and credentials, while streaming screenshots and the accessibility tree. Telegram channels act as a dead-drop resolver for WebSocket command-and-control, and researchers noted a possible link to the Medusa affiliate ecosystem.
- RemControl is an Android banking MaaS trojan active since at least May 2026.
- Fake TVTap Google Play pages and malvertising deliver the dropper APK.
- Accessibility overlays steal PINs and credentials from more than 30 banking apps.
- Operators stream screenshots and the accessibility tree over WebSocket.
- Telegram channels serve as a dead-drop resolver for rotating C2 addresses.
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | cdn.dlmafi.top | [.]com/ Distribution – fake TVTAP download website hxxp[:]//cdn[.]dlmafi[.]top/ Distribution – fake TVTAP download website Note: IP ad |
| domain | ff-de.shutgpt.ir | .]site/ Distribution – fake TVTAP download website hxxp[:]//ff-de[.]shutgpt[.]ir/ Distribution – fake TVTAP download website hxxp[:]//vp |
| domain | tvtap-hd.app | sa UNKN affiliate ecosystem. IOCs IOC Description hxxps[:]//tvtap-hd[.]app/ Distribution – fake TVTAP download website hxxp[:]//vpn[ |
| domain | vpn.askarzadeh.com | t[.]ir/ Distribution – fake TVTAP download website hxxp[:]//vpn[.]askarzadeh[.]com/ Distribution – fake TVTAP download website hxxp[:]//cd |
| domain | vpn.doneplay.site | [.]app/ Distribution – fake TVTAP download website hxxp[:]//vpn[.]doneplay[.]site/ Distribution – fake TVTAP download website hxxp[:]//ff |
| url | http://cdn[ | skarzadeh[.]com/ Distribution – fake TVTAP download website hxxp[:]//cdn[.]dlmafi[.]top/ Distribution – fake TVTAP download website |
Full article879 words · extracted from gbhackers.com · click to collapse
A newly uncovered Android banking trojan dubbed RemControl is targeting customers of more than 30 financial institutions across Europe, the Middle East, and Canada.
The malware combines fake Google Play pages, Android Accessibility Service abuse, credential-stealing overlays, real-time screen streaming, and remote-control functions to compromise mobile banking sessions.
The company tracks the operator behind the earliest campaigns as UNKK, based on hardcoded affiliate and campaign identifiers recovered from analyzed samples.
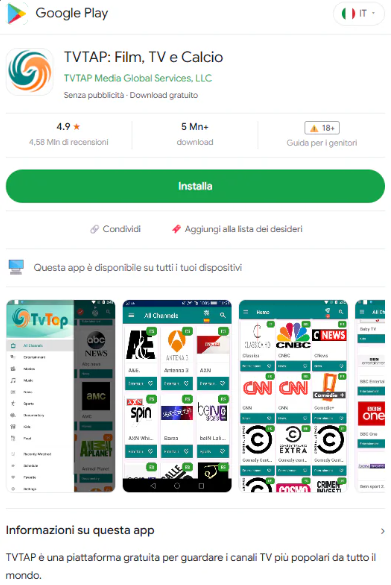
The campaign begins with fake Google Play Store pages impersonating TVTap, a third-party IPTV application commonly sought from unofficial download sites.
The malicious pages are designed to appear legitimate and, in at least one Italy-focused operation, checked visitors’ IP geolocation and mobile User-Agent before delivering the APK.
Researchers also identified Meta Pixel tracking IDs on the pages, indicating that malvertising likely drove victims to the fraudulent downloads.
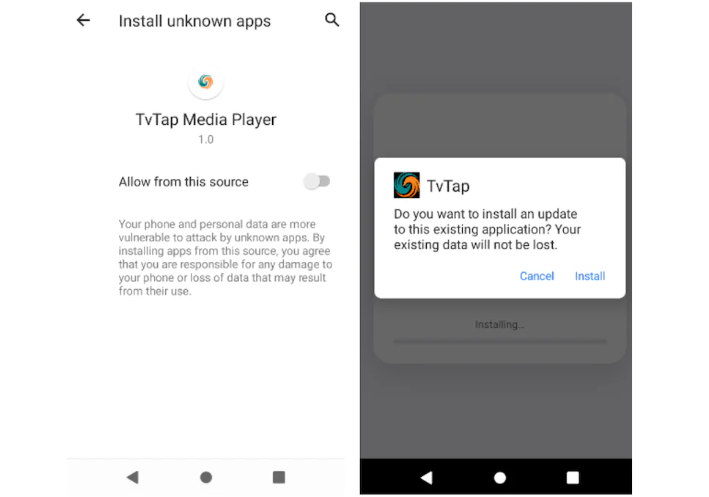
After installation, the RemControl dropper presents a WebView-based interface disguised as a TVTap update prompt.
It then abuses Android’s VPN functionality to block network traffic associated with com.android.vending, the Google Play Store package.
This effectively interferes with Google Play Protect connectivity during installation, limiting real-time scanning at a critical stage of the attack.
The dropper also generates a fresh signing certificate for every installation using Android Keystore functionality. As a result, each payload carries a different certificate and hash, complicating conventional hash- and certificate-based detection.
Newer variants further protect their code with a custom DEX packer that derives its decryption key from the APK signing certificate, binding the protected payload to an individual build.
Once the victim grants Accessibility Service permissions, RemControl gains the capabilities needed to hijack banking activity.
Group-IB researchers said that, RemControl operates as a Malware-as-a-Service platform and has been active since at least May 2026, while the first identified samples appeared in July.
RemControl Android Malware
The malware monitors foreground applications and fetches a dynamic target list from its command-and-control infrastructure.
The strings in both the dropper and payload are obfuscated by Base64 encoding followed by XOR decryption against a hardcoded key, thus hiding the strings from simple string inspection.
When a targeted banking app opens, RemControl places a full-screen WebView overlay over the legitimate application, collecting data such as PINs, banking codes, card-expiry dates, and other login credentials.
The overlay content is not embedded in the APK. Instead, it is retrieved dynamically from the C2 server, enabling operators to change phishing templates or retarget infected devices without requiring a new malware installation.
Group-IB confirmed overlays targeting banks in Italy, France, Spain, Poland, Portugal, Canada, and Gulf Cooperation Council member states, with Italy and France appearing to be major initial targets.
The malware fetches one of two hardcoded Telegram channel URLs in round-robin. It then searches the page HTML for a marker string appearing twice, extracts the content between the two occurrences, Base64-URL decodes it, and decrypts it with AES-128-CBC.
RemControl extends beyond overlay fraud. It can capture device screenshots through AccessibilityService.takeScreenshot(), encode them as WEBP images, and stream them over WebSocket connections.
It also transmits the Android accessibility tree as structured JSON, exposing visible text, UI elements, coordinates, and interaction states.
This gives operators both a visual and machine-readable representation of a victim’s device.
The malware can additionally log clicks, text changes, focus events, and selections across applications. Its remote-control toolkit supports taps, long presses, swipes, scrolling, gesture actions, and direct text injection.
Researchers also found functions that identify pattern-lock interfaces on major Android implementations, including Samsung One UI, Xiaomi MIUI, Huawei, OPPO ColorOS, OnePlus, and stock Android variants.
For C2 resilience, RemControl uses Telegram as a dead-drop resolver.
A notable operational mistake linked the campaign to AI-assisted development: researchers found a complete AI assistant response accidentally appended to a live banking-phishing overlay.
The malware retrieves encrypted configuration data from hardcoded Telegram channels, decodes the concealed C2 address, and then communicates primarily over WebSocket, with HTTP POST as a fallback.
This architecture allows operators to rotate infrastructure without recompiling the malware.
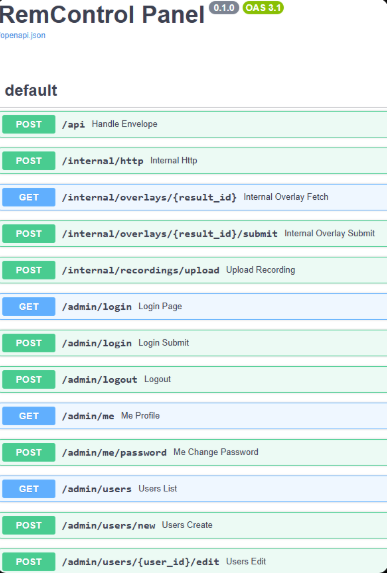
Group-IB also found publicly exposed API documentation for infrastructure labeled “RemControl Proxy” and the operator panel.
The panel exposed bot management, overlay editing, credential-result viewing, macro automation, VNC session replay, and per-affiliate APK build capabilities, reinforcing the assessment that RemControl is a MaaS operation.
Russian-language comments in overlay code provide a limited clue about the developer’s language background, while campaign-tag overlaps and delivery similarities suggest a possible connection to the Medusa UNKN affiliate ecosystem.
IOCs
| IOC | Description |
| hxxps[:]//tvtap-hd[.]app/ | Distribution – fake TVTAP download website |
| hxxp[:]//vpn[.]doneplay[.]site/ | Distribution – fake TVTAP download website |
| hxxp[:]//ff-de[.]shutgpt[.]ir/ | Distribution – fake TVTAP download website |
| hxxp[:]//vpn[.]askarzadeh[.]com/ | Distribution – fake TVTAP download website |
| hxxp[:]//cdn[.]dlmafi[.]top/ | Distribution – fake TVTAP download website |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Cut every SOC alert investigation by 21 min. Power your SOC with instant IOC context for immediate response: Integrate TI Lookup in your SOC
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.