New Check Point flaw lets hackers execute code with root privileges
Check Point patched CVE-2026-91843, a stack-based buffer overflow in Security Management Server logins enabling unauthenticated root remote code execution.
Check Point fixed CVE-2026-91843, a stack-based buffer overflow in the Security Management Server and Log Server login process that allows unauthenticated, low-complexity root RCE without user interaction. All Security Management Server deployments are vulnerable regardless of configuration. Fixes ship via LivePatch, with mitigation limiting SmartConsole Trusted Clients to trusted IPs, and attacks are detectable via 'Administrator failed to log in: Username too long' alerts. The new flaw is not yet flagged as exploited, though Check Point zero-days CVE-2026-50751 and CVE-2026-16232 are actively abused, including by a Qilin ransomware affiliate, and NCSC-NL urged fast patching of CVE-2026-85102 and CVE-2026-85103.
- Stack-based buffer overflow in Security Management Server and Log Server login process.
- Exploitation is low-complexity, needs no privileges or user interaction, and yields root RCE.
- All Security Management Server deployments are vulnerable regardless of configuration.
- Mitigations include LivePatch updates and restricting SmartConsole Trusted Clients to trusted IPs.
- Detect attempts via 'Administrator failed to log in: Username too long' audit alerts.
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2026-16232 | Authentication Bypass in Check Point SmartConsole Grants Full Admin Access Check Point SmartConsole, the administrative client used to manage Quantum Security Management and Multi-Domain Security Management, contains an authentication bypass (CWE-287) in its login process that allows an unauthenticated remote attacker to obtain an application login token and authenticate with full administrative privileges. Exploitation is possible when the Management Server IP address is reachable from the internet and the configuration does not restrict Trusted Clients. A successful attacker can modify security policies and security configurations, effectively taking control of firewall management. Any organization running an internet-exposed Check Point management server without Trusted Client restrictions is affected, though Check Point reports exploitation has impacted only a very small number of customers. The flaw was added to CISA's KEV on 2026-07-22, is actively exploited, and press reports indicate public proof-of-concept code has been released. Do: Apply the fix released in Check Point's advisory for CVE-2026-16232 by updating SmartConsole and the associated Quantum/MDS management software; no fixed version numbers were provided in this data, so confirm them against the vendor bulletin. As an interim mitigation, restrict internet access to the Management Server IP address and configure Trusted Clients so SmartConsole connections are accepted only from known administrator addresses. Review management logs for unexpected logins, unauthenticated token issuance, or unfamiliar administrator sessions, and complete remediation per CISA BOD 26-04 given the KEV listing. | 9.3 | 72% | KEV |
| largeplausibly tens of thousands of Check Point management deployments, though the vulnerable subset is only those with an internet-exposed Management Server and no… | |
| CVE-2026-50751 | Unauthenticated IKEv1 VPN Auth Bypass in Check Point Security Gateways Check Point has disclosed CVE-2026-50751, a critical (CVSS 9.3) improper authentication flaw (CWE-287) in the certificate validation logic for Remote Access and Mobile Access VPN when the deprecated IKEv1 key exchange is used. An unauthenticated remote attacker can exploit this logic flow weakness during IKEv1 negotiation to bypass user authentication entirely. Successful exploitation lets the attacker establish a remote access VPN connection without a valid user password, gaining access to the organization's internal network resources (high confidentiality impact per the CVSS score). Any organization running a Check Point Security Gateway on Gaia OS or Gaia Embedded with IKEv1-based Remote Access/Mobile Access configured is affected; specific affected and fixed versions are in Check Point's advisory. The flaw is being exploited in the wild — it was added to CISA's Known Exploited Vulnerabilities catalog on 2026-06-08 with known ransomware use and an EPSS of 83.8% — and it was disclosed alongside other critical Check Point VPN certificate flaws per recent headlines. Do: Upgrade affected Security Gateways to the fixed releases identified in Check Point's advisory (version numbers are not specified in the source data), prioritizing internet-facing VPN gateways; as an interim mitigation, move Remote Access/Mobile Access clients to IKEv2 or disable IKEv1. Review VPN authentication logs for sessions established without valid credentials, given known in-the-wild and ransomware exploitation. Federal agencies must apply mitigations per BOD 22-01, and defenders should beware of fake 'public PoC' repositories spreading malware (ChocoPoC RAT), since no legitimate public PoC is known. | 9.3 | 84% | KEV ransomware PoC |
| massplausibly on the order of 100,000+ internet-exposed Check Point gateways, with the IKEv1-affected subset likely tens of thousands of sites (estimate) | |
| CVE-2026-85102 | Unauthenticated RCE in Check Point Quantum Security Gateway via certificate flaw CVE-2026-85102 is an improper certificate trust-validation flaw (CWE-295) in the VPN negotiation code of Check Point Quantum Security Gateways. An unauthenticated remote attacker who can reach the gateway's VPN service can trigger the flaw during VPN negotiation, where certificates involved in the exchange are not properly validated, and achieve code execution on the gateway. Successful exploitation yields arbitrary code execution on the gateway with high impact on confidentiality, integrity, and availability (CVSS 9.8), amounting to full compromise of the security gateway. The affected population is organizations running Quantum Security Gateways with VPN services reachable from untrusted networks. As of the available reporting there is no public proof-of-concept, the flaw is not in CISA's Known Exploited Vulnerabilities catalog, and no in-the-wild exploitation is confirmed; the issue was disclosed alongside a second, similarly rated (9.8) Check Point VPN certificate-validation RCE flaw. Do: Upgrade Quantum Security Gateways to the fixed versions listed in Check Point's advisory (AV26-902) as soon as they are published, prioritizing internet-facing VPN gateways. Until patched, restrict exposure of VPN negotiation endpoints to trusted networks and monitor VPN services for anomalous handshake activity. Inventory which gateways in your estate expose VPN services publicly and treat those as the highest-priority targets. | 9.8 | — |
| largetens of thousands of internet-exposed Quantum VPN gateways (est.); total Check Point installed base plausibly in the hundreds of thousands of appliances/sites | ||
| CVE-2026-85103 | Unauthenticated RCE in Check Point Quantum VPN Certificate ASN.1 Decoding CVE-2026-85103 is a heap-based buffer overflow (CWE-122) in the ASN.1 certificate-decoding code used by Check Point's VPN implementation, rated 9.8 Critical with a network-exploitable, unauthenticated, low-complexity vector. An unauthenticated remote attacker can trigger the flaw by sending crafted certificate data that the VPN service parses during connection handling, causing heap corruption that allows arbitrary code execution on the target system. Successful exploitation grants the attacker code execution with high confidentiality, integrity, and availability impact, which on security gateways and management servers could mean control of the security infrastructure itself. Any organization running Check Point Quantum Security Management or Quantum Security Gateway systems that process VPN certificate traffic is potentially affected, and the advisory set indicates this flaw was disclosed alongside a second, similarly rated 9.8 VPN certificate vulnerability (Check Point advisory AV26-902). There is no evidence of exploitation so far: the flaw is not in CISA's Known Exploited Vulnerabilities catalog and no public proof-of-concept is known. Do: Patch promptly: because this is an unauthenticated, network-reachable 9.8-rated RCE in the VPN path, upgrade Quantum Security Management and Quantum Security Gateway deployments per Check Point's advisory (referenced as AV26-902), and check your current software versions against the affected/fixed ranges listed there, which are not specified in the data available here. Until patched, restrict access to exposed VPN and management interfaces to trusted source IPs where possible and monitor VPN endpoints for anomalous connection or crash behavior. Inventory all Quantum appliances and management servers, since the flaw affects both product lines and was disclosed together with a second 9.8 VPN certificate flaw. | 9.8 | — |
| largelikely tens of thousands (order of magnitude 10k–100k) of deployed Quantum gateways/management servers, of which a substantial share expose VPN endpoints to… | ||
| CVE-2026-91843 | Unauthenticated stack overflow gives root RCE in Check Point login process CVE-2026-91843 is a stack-based buffer overflow (CWE-121) in the unauthenticated login process of a Check Point product, as Check Point Software ([email protected]) is the assigning CNA and its CVE scope covers Check Point products. An attacker can trigger the flaw remotely by sending crafted input to the login interface before authenticating, with no user interaction or credentials required. Successful exploitation allows arbitrary code execution with root privileges, the highest level of control on the affected system. The vulnerability is rated 9.8 Critical (AV:N/AC:L/PR:N/UI:N, all impacts high), reflecting trivial network exploitability. No public proof-of-concept or confirmed in-the-wild exploitation is known at this time, and the source data does not name the specific product line or affected version ranges. Do: Monitor Check Point's official advisory channels for the affected product/version list and patch release, and upgrade as soon as fixed versions are published. In the interim, restrict the login/management interface of Check Point appliances to trusted management networks and remove any direct internet exposure, and review perimeter logs for anomalous pre-authentication traffic against that interface. | 9.8 | — |
| — |
Full article427 words · extracted from bleepingcomputer.com · click to collapse
Check Point Software has released security updates to address a critical vulnerability that can let attackers execute code with root privileges on management systems.
Tracked as CVE-2026-91843, this flaw stems from a stack-based buffer overflow weakness in the login process for Security Management Server instances, which manage Security Gateways (firewalls) and monitor network security events.
The security issue also affects the company's Log Server, a dedicated server that collects and stores logs generated by Check Point firewalls.
Successful exploitation lets threat actors without privileges gain root remote code execution in low-complexity attacks that don't require user interaction.
Check Point also provided temporary mitigation measures for customers who can't deploy the latest LivePatch, including hardening vulnerable systems against attacks and limiting access to trusted IP addresses/subnets by editing the entries under Manage & Settings > Permissions & Administrators > Trusted Clients in the SmartConsole dashboard.
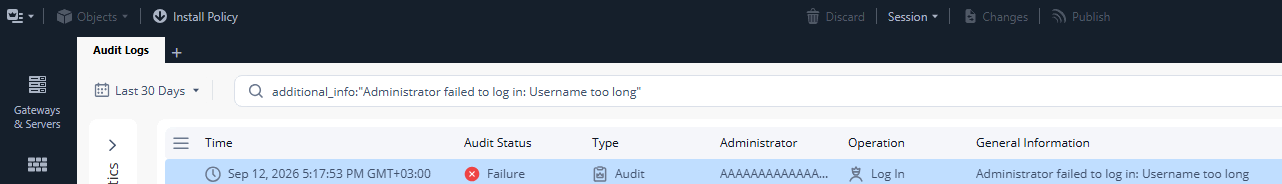
While the company has not yet flagged this security flaw as actively exploited, it said security teams can identify CVE-2026-91843 attacks by looking for "Administrator failed to log in: Username too long" alerts in the Audit and Admin login logs.
Last week, it patched another critical remote code execution flaw (CVE-2026-85103) stemming from a heap overflow in the VPN certificate ASN.1 decoding flow that affects Check Point firewalls and management systems.
"All Security Management Server deployments are vulnerable, regardless of configuration," Check Point warned. "The vulnerability is not dependent on any specific management configuration. The management is vulnerable even when VPN in not in use or configured."
The same day, it patched a second critical flaw (CVE-2026-85102) that lets unauthenticated hackers bypass authentication and execute code remotely on vulnerable firewalls.
Although these vulnerabilities are not yet exploited in the wild, Check Point flagged other flaws as actively exploited in recent months.
The first, an authentication bypass (CVE-2026-50751) zero-day, was abused by a Qilin ransomware affiliate since June, while a second authentication bypass zero-day (CVE-2026-16232) has been exploited since at least July to authenticate with administrator privileges to SmartConsole admin panels.
More recently, the Dutch National Cyber Security Centre (NCSC-NL) warned organizations to prioritize patching two critical Check Point VPN flaws tracked as CVE-2026-85102 and CVE-2026-85103 because it "expects exploitation attempts to occur soon."
Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.bleepingcomputer.com/news/security/check-point-warns-critical-flaw-lets-hackers-execute-code-as-root/