Hackers Exploit WordPress CVE-2026-63030 and CVE-2026-60137 to Steal Government Data
A Chinese threat actor exploited critical WordPress vulnerabilities to steal 18,566 sensitive records from a Western government organization across 29 countries.
A Chinese-speaking threat actor exploited the critical WordPress wp2shell vulnerability chain to compromise government and small-business targets across 29 countries, stealing at least 18,566 sensitive records from a Western government organization.
- Chinese-speaking threat actor exploited WordPress critical vulnerability chain to compromise government and small-business targets across 29 countries
- At least 18,566 sensitive records were stolen from a Western government organization
- Attack chain involves two critical vulnerabilities tracked as CVE-2026-63030 and CVE-2026-60137
- Both CVEs were added to CISA's Known Exploited Vulnerabilities catalog
Vulnerabilities mentionedAll →
- CVE-2026-630309.810%WordPress Core Route Confusion (wp2shell) Enables SQL Injection to RCEpublished · WordPress Core KEV PoC ×3+1 related
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| ipv4 | 104.225.153.141 | *.981666.xyz C2 74.48.66.73 Staging <REDACTED> Exploitation 104.225.153.141 C2 Note: IP addresses and domains are intentionally defange |
| ipv4 | 74.48.66.73 | 539e162a516466c0de682dbf9f8a4000b1 Backdoor *.981666.xyz C2 74.48.66.73 Staging <REDACTED> Exploitation 104.225.153.141 C2 Note: IP |
| sha256 | 0e81d80b40eaacbf6cb1e817fb1824c30a824af5cb4faca4aa9b03fd506d480f | es. Indicators of Compromise Indicator of Compromise Note 0e81d80b40eaacbf6cb1e817fb1824c30a824af5cb4faca4aa9b03fd506d480f Backdoor 0f6e757e82c4d91df5bd249f775b9970b59dee42cc0dfe40f8 |
| sha256 | 0f6e757e82c4d91df5bd249f775b9970b59dee42cc0dfe40f879d77fc16821c6 | bf6cb1e817fb1824c30a824af5cb4faca4aa9b03fd506d480f Backdoor 0f6e757e82c4d91df5bd249f775b9970b59dee42cc0dfe40f879d77fc16821c6 Backdoor 2ff2945b13a4cd0e9a65c85af29ea1539e162a516466c0de68 |
| sha256 | 2ff2945b13a4cd0e9a65c85af29ea1539e162a516466c0de682dbf9f8a4000b1 | 1df5bd249f775b9970b59dee42cc0dfe40f879d77fc16821c6 Backdoor 2ff2945b13a4cd0e9a65c85af29ea1539e162a516466c0de682dbf9f8a4000b1 Backdoor *.981666.xyz C2 74.48.66.73 Staging <REDACTED> Exp |
Full article800 words · extracted from gbhackers.com · click to collapse
A suspected Chinese-speaking threat actor has exploited the critical WordPress “wp2shell” vulnerability chain to compromise government and small-business targets across 29 countries, stealing at least 18,566 sensitive records from one Western government organization.
GreyNoise linked the activity to a malicious cyber actor (MCA) it has tracked through its Global Observation Grid since early June.
The attack chain, known as wp2shell, combines a route-confusion flaw in the WordPress REST API batch endpoint, tracked as CVE-2026-63030, with a SQL injection flaw in the WP_Query component’s author__not_in parameter, CVE-2026-60137.
Together, the flaws allow an unauthenticated attacker to execute arbitrary code on vulnerable WordPress deployments without requiring plugins, valid credentials, or prior access.
Affected releases include WordPress 6.8.x before 6.8.6, 6.9.x before 6.9.5, and 7.0.x before 7.0.2.
The issues were patched in WordPress 6.8.6, 6.9.5, and 7.0.2, while both CVEs were added to CISA’s Known Exploited Vulnerabilities catalog on July 21 following confirmation of active exploitation.
GreyNoise observed the actor successfully compromise at least 49 organizations, including government entities, in countries such as Germany, Colombia, Switzerland, Brazil, Japan, the United Kingdom, India, the United States, and Ukraine.
The campaign also reportedly affected a Russian state entity in Russian-occupied Ukraine.
In the most serious incident, the actor targeted a Western government organization on July 22.
The intrusion began with exploitation of WordPress bugs and deployment of a custom web shell. Within roughly 11 minutes, the attacker had dumped the WordPress user table and stolen 13 administrator accounts.
The operator then logged into the victim’s WordPress administration panel, created a fraudulent account impersonating a legitimate organization email address, and backdated its registration timestamp to 2025 in an apparent effort to blend into normal account history.
The attacker later uploaded a custom WordPress plugin for host and application enumeration, then used the web shell to inspect Microsoft Defender settings, local users, running services, MySQL installations, IIS sites, network listeners, WordPress configuration files, and Windows registry locations.
WordPress Vulnerability Exploitation
GreyNoise said the adversary used at least 17 script variants to evade Microsoft’s Antimalware Scan Interface, test privilege-escalation paths, conduct token theft attempts, and search for credentials embedded in readable files.
GreyNoise Researchers observed that, the actor began targeting WordPress environments around July 20, weaponizing CVE-2026-63030 and CVE-2026-60137 to gain unauthenticated remote code execution and establish persistent access.
The code included extensive Chinese-language comments, while its rapid iteration and superficial changes between variants led GreyNoise to assess that a large language model may have helped generate the tooling.
The credential-hunting activity uncovered working database credentials from configuration files.
The actor then staged stolen files into a ZIP archive in a web-accessible location and downloaded the archive, which contained source code, credentials, and other sensitive information.
Using the harvested credentials, the operator carried out password spraying against internal resources and successfully accessed an internal SQL database.
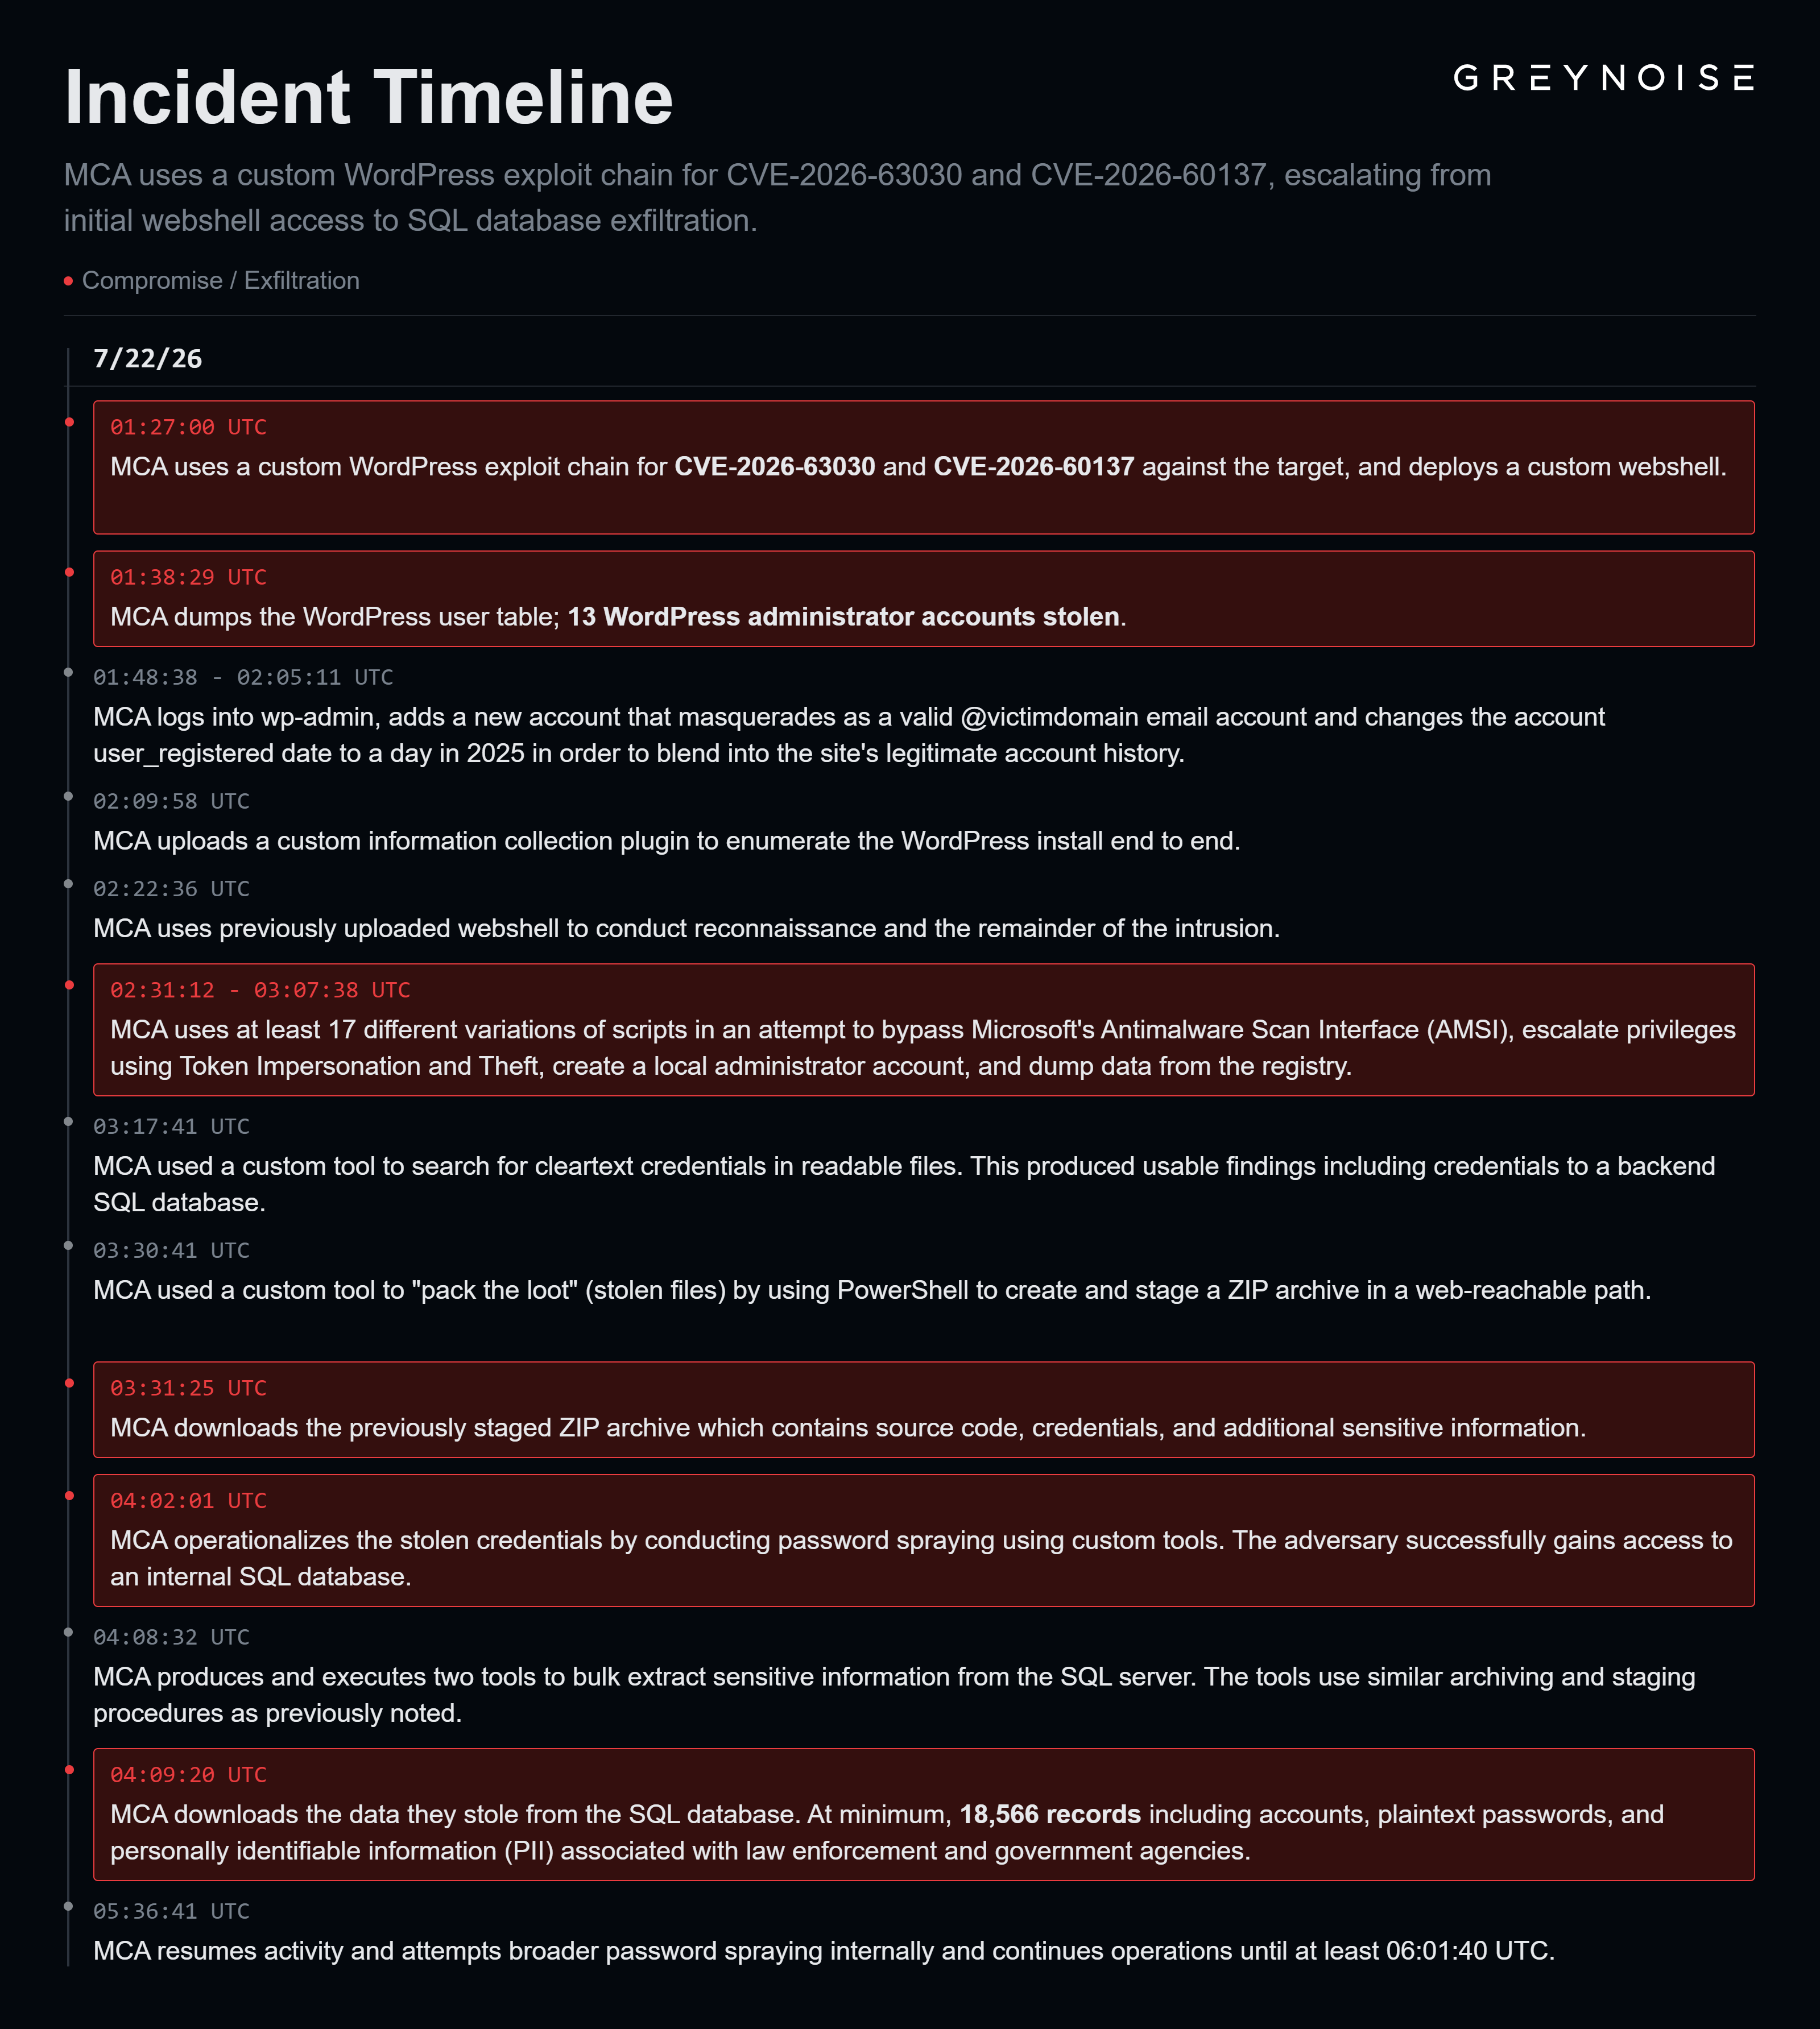
Two custom collection tools were subsequently used to bulk-extract data from the server.
At least 18,566 records containing accounts, plaintext passwords, and personally identifiable information tied to law-enforcement and government agencies were exfiltrated.
GreyNoise assesses that the operator is the same as, or related to, the “Red Heron” activity documented by Acronis, citing overlap in command-and-control infrastructure, malware, Gitea exploitation, and broader tradecraft.
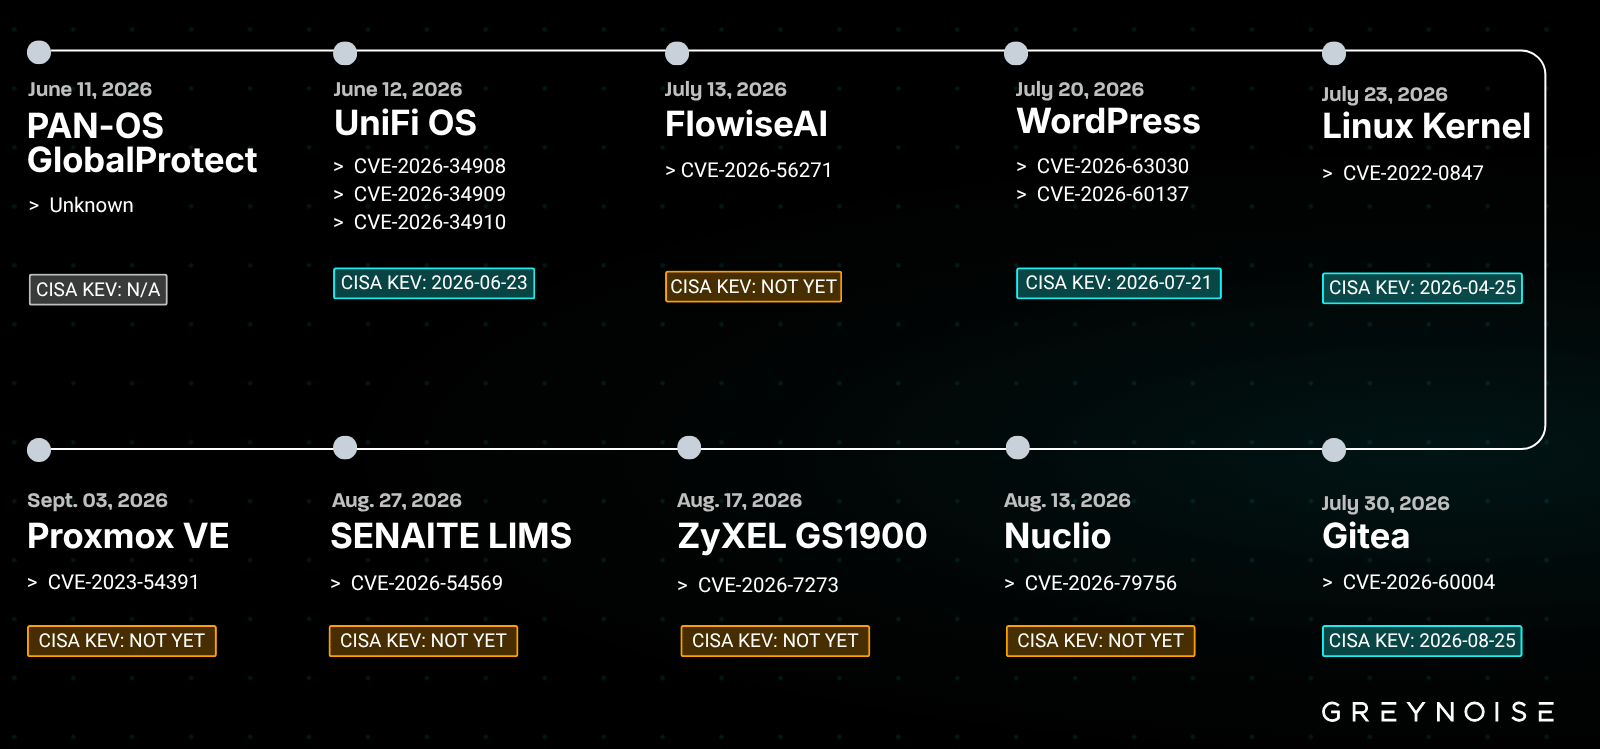
The campaign has also targeted Ubiquiti UniFi OS, FlowiseAI, Gitea, Nuclio, SENAITE LIMS, Proxmox VE, PAN-OS GlobalProtect, and ZyXEL GS1900 switches.
Notably, the actor allegedly exploited CVE-2026-7273 against 996 ZyXEL GS1900 switches in 48 countries, stealing device configurations, hashed root credentials, and network information.
GreyNoise described this as the first publicly documented exploitation of that vulnerability in the wild.
Organizations running WordPress should immediately upgrade to the fixed releases and investigate for indicators of compromise, including unauthorized administrator accounts, unfamiliar plugins, modified web-root files, suspicious archives in web-accessible directories, and unusual access to /wp-json/batch/v1.
Where emergency patching is impossible, defenders should restrict anonymous access to the REST batch endpoint through a web application firewall and closely review web-server, WordPress, endpoint, and database logs.threatprotect.qualys+1
The campaign demonstrates how quickly a public, pre-authentication WordPress RCE can become an enterprise and government-data theft issue when exposed applications are connected to Windows servers, internal credentials, and backend databases.
Indicators of Compromise
| Indicator of Compromise | Note |
|---|---|
| 0e81d80b40eaacbf6cb1e817fb1824c30a824af5cb4faca4aa9b03fd506d480f | Backdoor |
| 0f6e757e82c4d91df5bd249f775b9970b59dee42cc0dfe40f879d77fc16821c6 | Backdoor |
| 2ff2945b13a4cd0e9a65c85af29ea1539e162a516466c0de682dbf9f8a4000b1 | Backdoor |
| *.981666.xyz | C2 |
| 74.48.66.73 | Staging |
| <REDACTED> | Exploitation |
| 104.225.153.141 | C2 |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Cut every SOC alert investigation by 21 min. Power your SOC with instant IOC context for immediate response: Integrate TI Lookup in your SOC
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.