Critical N-able N-central Vulnerability and Active Exploitation
N-able N-central pre-auth RCE zero-day CVE-2026-86218 (CVSS 10.0) is exploited in the wild; on-prem admins must upgrade to 2026.3 HF4.
N-able disclosed a third N-central vulnerability, CVE-2026-86218, a pre-authentication RCE rated CVSS 10.0, and released hotfix 2026.3 HF4 superseding build 2026.3.1.13. Huntress reproduced an exploit chain involving an authentication bypass (CVE-2026-86206/CVE-2026-86207) after a fully patched customer's N-central production server was compromised on September 4. Attackers appended strings like .invalid to account names and probed the /remoteControlAction.do?method=getPierDetails endpoint; Huntress worked with Cloudflare to disable adversary tunnel infrastructure. Hosted N-central instances are already patched; on-prem administrators must upgrade immediately.
- CVE-2026-86218: pre-auth RCE, CVSS 10.0, observed exploited in the wild
- Exploit chain uses auth bypass CVE-2026-86206/CVE-2026-86207 against patched 2026.3.1.10
- Attackers manipulate account names and probe getPierDetails endpoint for recon
- Huntress coordinated with Cloudflare to disrupt adversary tunnel infrastructure
- On-prem admins urged to upgrade to 2026.3 HF4 immediately
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2026-18556 | Authentication Bypass (Alternate Path/Channel) in N-able N-central N-able's N-central RMM platform contains an authentication bypass (CWE-288) in which an alternate path or channel allows requests to skip the normal authentication check. An unauthenticated attacker can trigger it by sending requests through that alternate path without valid credentials, gaining unauthorized access to the N-central management interface; because N-central is remote monitoring and management software run by managed service providers, such access can expose management functions across downstream customer environments. N-able N-central deployments are affected; the available data does not specify affected version ranges or fixed builds. The flaw was added to CISA's Known Exploited Vulnerabilities catalog on 2026-08-04, confirming exploitation in the wild, with a high EPSS of 40.2% (99th percentile), no CVSS score yet, no public PoC, and undetermined ransomware use; related reporting describes a recent string of N-central hotfixes, including fixes for unauthenticated remote code execution. Do: Apply N-able's hotfix for N-central immediately per the vendor's instructions, since the flaw is in CISA KEV and BOD 26-04 applies (for cloud-hosted N-central, apply mitigations per BOD 26-04 or discontinue use if mitigations are unavailable). Until patched, restrict internet exposure of the N-central server to trusted management networks and review authentication logs for unexpected access, following CISA's forensics triage guidance. Check the vendor advisory for the exact fixed build, as the available data does not list affected or fixed version numbers. | 8.2 | 40% | KEV |
| largeon the order of tens of thousands of N-central server instances (estimate; exact counts not in available data) | |
| CVE-2026-18577 | Authentication Bypass and Account Takeover in N-able N-central (Incomplete Patch) CVE-2026-18577 is an authentication bypass (CWE-288) in N-able's N-central RMM platform caused by an incomplete patch for the earlier vulnerability CVE-2026-18556. Because the original fix can be bypassed via an alternate path or channel, a remote, unauthenticated attacker needs no privileges or user interaction, though the attack requires meeting exploit-specific conditions (high attack complexity, CVSS 4.0: 8.2 High). Successful exploitation lets the attacker bypass authentication and take over N-central accounts, gaining high-impact access to the management console with limited direct effects on downstream services. All N-central versions through 2026.3.1 are affected. Exploitation is confirmed in the wild: the flaw was added to CISA's KEV on 2026-08-03, EPSS estimates a 54.1% chance of exploitation within 30 days (99th percentile), and news reports say attackers kept exploiting it even as N-able shipped successive hotfixes; ransomware use is currently unknown. Do: Upgrade N-central to a fixed release or hotfix newer than 2026.3.1 following N-able's advisory — the vendor has issued multiple successive hotfixes for this and related N-central flaws, so verify you are on the latest build. Because the flaw is on CISA's KEV, federal and BOD 26-04-bound organizations must apply vendor mitigations promptly or discontinue use of the product if patching is unavailable. Limit internet exposure of N-central portals and review accounts for signs of takeover or unauthorized access. | 8.2 | 54% | KEV |
| moderate≈1,000–10,000 internet-exposed N-central server instances (estimate from public internet scans; total on-prem deployments likely higher, with millions of… | |
| CVE-2026-86206 | Access Control Filter Bypass in N-able N-central Exposes Internal APIs N-able N-central contains a flaw in the access-control filter that protects its internal API (CWE-791, incomplete filtering), allowing requests to bypass the filter and reach internal APIs without authorization. The issue is exploitable over the network with no privileges and no user interaction, per the CVSS 4.0 vector (AV:N/PR:N/UI:N). An attacker gains unauthorized, low-impact access to internal APIs (VC:L); the vector indicates no integrity or availability impact and no evidence of code execution from this flaw. Any organization running an affected N-central release — a remote monitoring and management (RMM) platform operated by managed service providers — is affected, and the fix is available in N-central 2026.3 HF3 and 2026.4. The flaw is not on the CISA KEV list and has no known public PoC or confirmed in-the-wild exploitation, though it was disclosed in the same patching cycle as actively exploited N-central unauthenticated RCE flaws. Do: Upgrade N-central to 2026.3 HF3 or 2026.4 as soon as practical. While patching, limit direct internet exposure of the N-central API and check logs for unauthenticated requests to internal API endpoints. Note this release cycle included several recent N-central hotfixes, including an actively exploited unauthenticated RCE, so ensure all outstanding patches are applied. | 6.9 | <1% |
| large≈ tens of thousands of N-central server deployments (MSP RMM installs), with only the internet-exposed subset directly reachable | ||
| CVE-2026-86207 | Authentication bypass in N-able N-central internal APIs before 2026.3 HF 3 CVE-2026-86207 is an authentication bypass (CWE-305) in N-able's N-central remote monitoring and management (RMM) platform that allows unauthorized access to APIs that are supposed to be internal-only. It is triggered over the network by sending requests to these internal API endpoints under specific conditions (the CVSS vector indicates some attack prerequisites and a low-privilege foothold are required). An attacker who exploits it gains highly privileged access to the N-central server's data and functions, with high impact on confidentiality, integrity and availability of the server itself. Organizations running any N-central release before version 2026.3 Hotfix 3 are affected — primarily managed service providers hosting N-central for their own operations. There is no public proof of concept, the flaw is not in CISA's KEV catalog, and EPSS puts 30-day exploitation risk at just 0.7%; note that the recent news headlines about actively exploited 'unauthenticated RCE' flaws in N-central describe separate vulnerabilities in the same product, which is why multiple hotfixes have shipped in quick succession. Do: Upgrade all N-central servers to version 2026.3 HF 3 or later, or apply the vendor's hotfix to your current release. Restrict network access to the N-central web/API interface to trusted networks and review logs for unexpected access to internal API endpoints. Given the recent string of N-central fixes — including the separately exploited pre-auth RCE — verify that every recent hotfix has been applied to each N-central instance you operate. | 7.7 | <1% |
| moderate≈ several thousand to low tens of thousands of N-central server deployments (typically one internet-exposed server per MSP) | ||
| CVE-2026-86218 | Pre-Auth Static Code Injection RCE in N-able N-central (Exploited in the Wild) CVE-2026-86218 is a static code injection flaw (CWE-96) in N-able's N-central on-premises remote monitoring and management (RMM) platform, carrying a maximum CVSS 4.0 score of 10.0. An unauthenticated, remote attacker triggers it by sending crafted network input to the N-central server that is improperly neutralized and persisted into application-managed code, which the server then executes — no privileges (PR:N) or user interaction (UI:N) are required. Successful exploitation yields full server compromise with high impact on confidentiality, integrity, and availability, and because N-central acts as the management hub for downstream customer endpoints, compromise can expose the entire managed estate. Any organization running an affected N-central release (before 2026.3.1.14) — primarily MSPs and corporate IT departments using N-able RMM — is affected. The flaw is confirmed exploited in the wild: N-able patched it as a zero-day, CISA added it to the KEV catalog on 2026-09-08, and it is the fourth N-central hotfix in five weeks, though no public PoC is known and ransomware use is unknown. Do: Upgrade N-central to 2026.3.1.14 or later (or apply N-able's hotfix) immediately, as the flaw is in CISA's KEV catalog and BOD 26-04 timelines apply to federal stakeholders. Until patched, remove direct internet exposure of the N-central server (restrict to VPN/management networks via firewall allowlists) since no authentication is needed for exploitation. Because in-the-wild exploitation is confirmed, review internet-facing N-central servers for indicators of compromise such as unexpected processes, unusual child processes of the web service, and new or suspicious accounts. | 10.0 | <1% | KEV PoC |
| large≈ tens of thousands of deployed/internet-exposed N-central servers (order of magnitude ~10k+), each managing many downstream customer endpoints |
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| md5 | 5568cd69c754b392121f1dbb8f900fda | r IPv4 (Tzulo VPN) 23.234.97[.]68 Intruder IPv4 (Tzulo VPN) 5568cd69c754b392121f1dbb8f900fda Malicious Cloudflare tunnel account tag Update: 8/6/26 @ 5: |
Full article2,899 words · extracted from huntress.com · click to collapse
Acknowledgments: Special thanks to Aaron Deal, Chris Bisnett, Aaron Bennett, Sharon Martin, Dave Kleinatland, James Northey, Josh Kiriakoff, Kamal Bennoune, Susannah Matt, and Michael Tigges for their contributions to this investigation and write-up.
Update: 9/6/26 @ 7:30 AM ET
In the early morning hours (U.S. time) of 9/6/2026, Huntress was alerted to a new CVE (CVE-2026-86218) and fourth hotfix via a Discord post on MSPGeek. Notably, this third CVE is an N-central pre-auth remote code execution vulnerability rated with a 10.0 CVSS score, which is the maximum allowable rating and higher than the previous two CVEs published on 9/5.
N-able also said that this release supersedes N-central 2026.3 Hotfix 3 (build 2026.3.1.13).
Here's the full notes from Jason Murphy with N-able in that MSPGeek Discord thread:
We recently communicated about two security vulnerabilities within N-central that were responsibly disclosed by a third party through our voluntary security disclosure program and we issued a hotfix. Since the disclosures, a third, independent researcher alerted us to a new vulnerability that has been exploited in the wild that is unrelated to the previously disclosed CVEs.
This critical zero-day vulnerability, if exploited, could allow for pre-authenticated access to the N-central server.
What You Need to Do
• N-central On-Premises Environments: Upgrade to 2026.3 HF4 immediately. Hotfix link: [2026.3 HF4 Release Notes]
• If you've already upgraded to 2026.3 HF3, you will need to upgrade to 2026.3 HF4 to protect against this newly discovered vulnerability.
• N-central Hosted Environments: No action is needed on your part; your instances have already been patched.
• N-able's HF4 release notes include supported upgrade paths and installation guidance.
In follow up conversation to the above message, Jason explicitly mentioned "this one is a Zero day."
The vulnerability has also been detailed in an Active N-able Incident page with the details here: https://uptime.n-able.com/event/201814/
Exploited in the Wild?
Notably, in both the MSPGeek post above and on N-able's Active Incident post they said the vulnerability has been observed being exploited in the wild.
However, N-able's Release Notes said: "At this time, we have no confirmations that this vulnerability has been exploited in production environments, but unpatched systems remain at risk".
In our 9/5/26 update (below), we had said we could not rule out whether the two previous vulnerabilities released (CVE-2026-86206 and CVE-2026-86207) were the ones that were exploited in the instance seen in the patched production environment of one of our customers. Because logs on the compromised N-central server had already rotated, we are also unable to say whether this new CVE was the vulnerability exploited in that case.
Detection opportunities
Given the ongoing exploitation N-central described above, we recommend checking for evidence of API manipulation in the appliance logs, and auditing your user accounts to verify no unauthorized changes have been made to your users or their permissions.
Huntress continues to monitor related activity and will update this post as more information becomes available.
Update: 9/5/26 @ 5 PM ET
Huntress is actively investigating a newly discovered authentication bypass affecting N-able N-central environments. Through rapid analysis of recent telemetry and partner-shared logs, our researchers have successfully reproduced and validated a proof of concept (PoC) that works against the latest N-Central version 2026.3.1.10. Following our discovery, we worked directly with N-able leadership and their security team to share our findings and tradecraft analysis, accelerating the development of an official fix. N-able has now released a security advisory and corresponding hotfix (2026.3.1.13), which we strongly urge all N-central administrators to apply immediately.
This activity represents a net new exploit chain that potentially leverages one or both of two newly designated vulnerabilities (CVE-2026-86206 and CVE-2026-86207), completely distinct from the flaws addressed by N-able's August hotfixes (CVE-2026-18556 and CVE-2026-18577).
To be clear on our observations: Huntress' investigation began on September 4 after a customer's fully patched N-central production environment was compromised. While analyzing the intrusion, we successfully recreated an exploit chain that explains the observed adversarial activity. However, due to limited historical logging available directly on the appliance, we cannot definitively confirm which specific exploit the threat actor used to achieve their compromise, nor can we rule out the use of alternative vulnerabilities.
Key tradecraft observations:
Account name anomalies: We have observed attackers manipulating account names by appending unexpected strings (such as
.invalid) to known N-able email addresses during user creation attempts. Administrators should also watch for login names and email addresses with subtle character swaps or spoofed domains designed to pass casual inspection.Reconnaissance probes: Initial staging activity shows threat actors probing the
/remoteControlAction.do?method=getPierDetailsendpoint with specific appliance IDs to map the environment and gather details prior to exploitation.
Disrupting adversary infrastructure
In addition to our collaboration with N-able on the hotfix, Huntress has initiated direct communications with Cloudflare to proactively disable the adversary's existing tunnels. We assess that any exploitation activity that predates our discovery likely utilizes the same account token. By working with Cloudflare to take down this infrastructure, we aim to simultaneously shut these unauthorized backdoors across all affected environments.
Detection opportunities
Unlike the August campaign, which heavily abused the Take Control feature, this new activity targets the underlying API and appliance logs. Defenders should pivot their hunting efforts to the following files on their N-central servers:
envoy_proxy_HTTPS.logsyslog ncentraldms
What to look for:
API manipulation: Filter these logs for URL-encoded endpoint anomalies—specifically successful requests to internal API routes using URL-encoded values such as
%2F.Account quirks: Audit newly created user accounts for unusual naming conventions, specifically email addresses appended with
.invalidor similar unexpected string manipulations.
Recommendations for N-central customers
N-able has released a security advisory and a corresponding hotfix to address these vulnerabilities. Because this exploit chain grants full administrative control over user management, organizations must act immediately.
Execute a rapid patching plan: Apply the latest N-central hotfix provided by N-able immediately. Refer to their official release notes and instructions to ensure your appliance is fully updated and no longer vulnerable.
Hunt for anomalous user creation: Actively audit your user lists and access controls. Because this exploit chain grants full control over user management, you should hunt for any anomalous user creation or unexpected role modifications, including the
.invalidaccount anomalies detailed above.Enforce strict perimeter controls: Even after patching, we strongly urge you to restrict all inbound access to your N-central console. Ensure it is not directly exposed to the public internet by enforcing strict IP allowlisting or a mandatory VPN.
Huntress will continue to update this post as the landscape evolves.
NEW Indicators of Compromise
See the table at the end of this post for a complete list of indicators from the August incidents.
Item | Description |
|---|---|
| Intruder IPv4 (Tzulo VPN) |
| Intruder IPv4 (Tzulo VPN) |
| Malicious Cloudflare tunnel account tag |
Update: 8/6/26 @ 5:40 PM ET
N-able has released a second hotfix for N-central that supersedes its original hotfix to provide additional hardening measures. Hotfix 2 (2026.3.1.10) is required for organizations running N-central on-premises even if they've applied Hotfix 1 (2026.3.1.7). Organizations are advised to upgrade immediately, following N-able's upgrade instructions. N-able says organizations using hosted N-central (NCOD) do not need to take action, as mitigations have already been applied.
N-able has also published an additional security update with four more malicious IPs, which we have added to the IoC section at the end of this blog.
173.249.252[.]176185.156.46[.]15023.234.94[.]4368.235.46[.]235
We continue to monitor activity tied to this vulnerability and will add details to this blog as new information becomes available.
Update: 8/3/26 @ 2:15 PM ET
Huntress continues to investigate activity targeting N-able's critical vulnerability. We are now seeing threat actors targeting the flaw across multiple organizations, though we are not yet seeing evidence that this has become a broad, indiscriminate campaign across our partner base.
The good news is that organizations are actively applying the hotfix provided by N-able. In our last update at 12:45 AM ET, we reported that more than half (55.6%) of our partners' and customers' reachable cloud servers were still unpatched. As of publication of this latest update, almost all of the cloud-hosted servers are now patched. Overall, we see about 13.6% reachable servers overall are still unpatched (including both cloud and self-hosted reachable servers). Notably, the majority of the remaining unpatched servers are self-hosted: 28.6% of the reachable N-central self-hosted servers are still unpatched.
Across the attacks we've observed, we have seen the same pattern of behavior:
Threat actors are conducting high-level reconnaissance in order to target key servers, typically Domain Controllers. This indicates that threat actors are being strategic enough to prioritize their efforts.
After exploitation, we have seen the attackers request a process list, to enumerate processes running on a compromised system, before disconnecting.
Post compromise, threat actors moved quickly across multiple hosts in impacted organizations' environments after gaining initial access, as seen in Figure 1a.
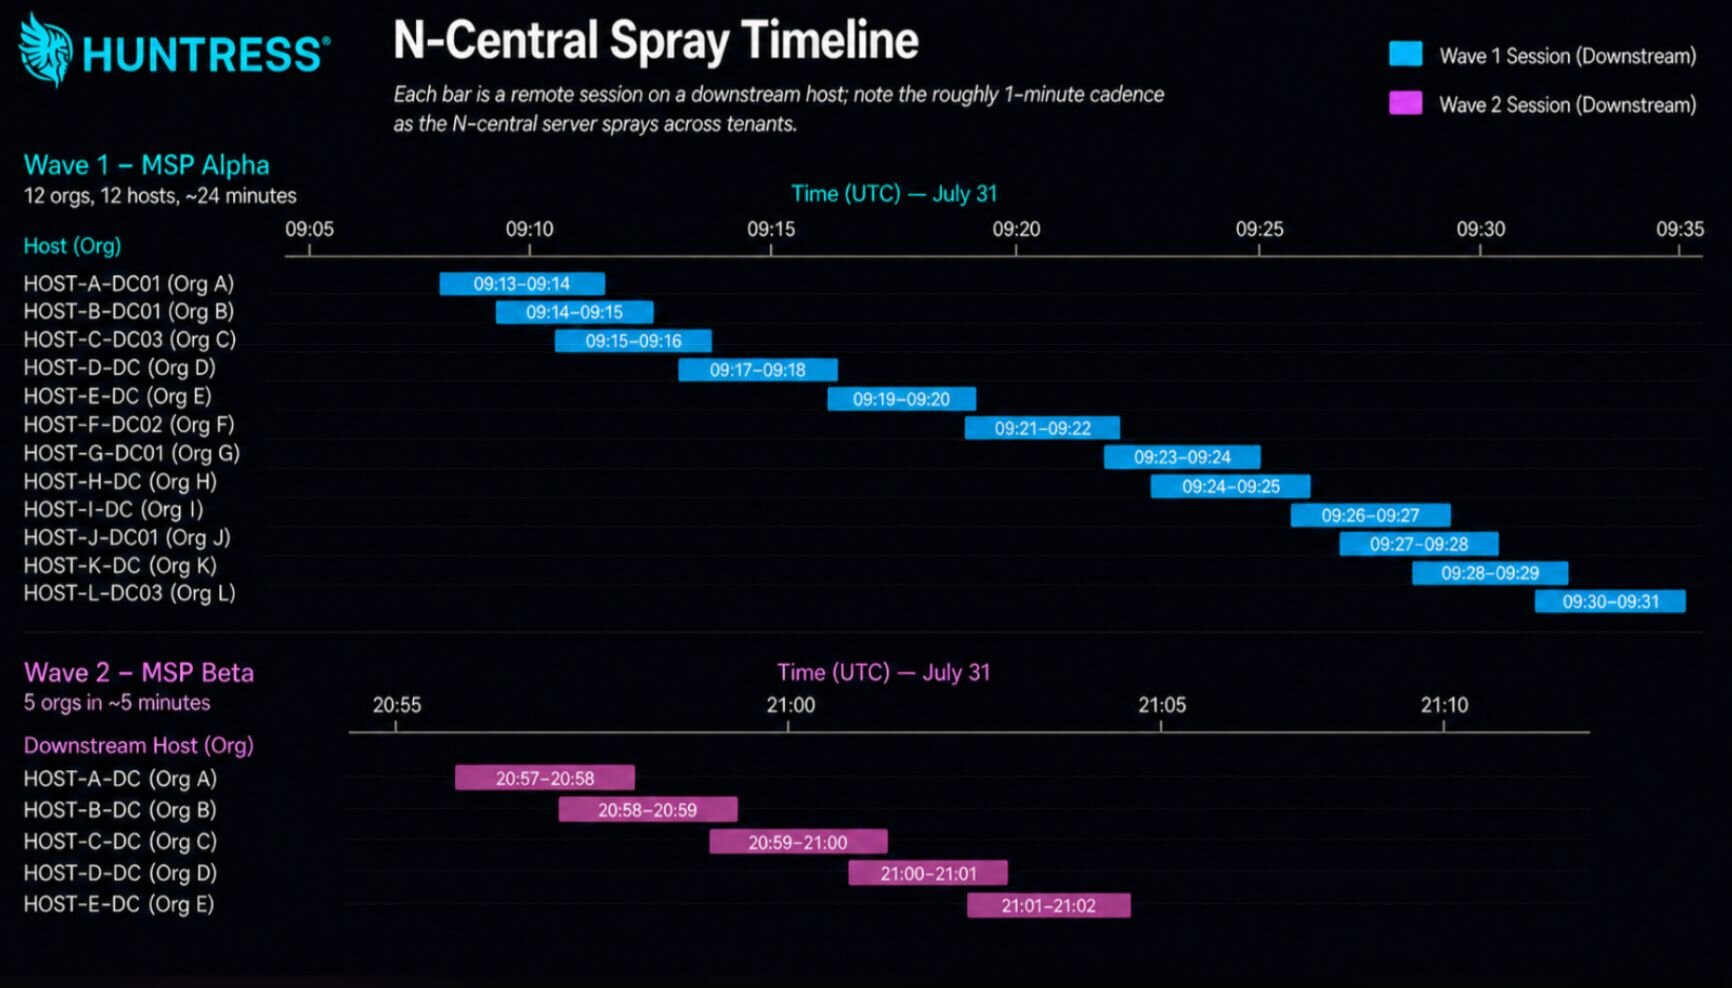
Figure 1a: Timeline of threat actors tearing through downstream hosts on two impacted organizations
Below are the Windows Application Event Logs reflecting Event IDs 4102, 8192, and 8193 for a compromised organization. These show the threat actor first making the malicious connection via "MSP Support" from 173.249.252[.]200 (one of the IP addresses listed as an IoC by N-able). "MSP Support" is the default username tied to legitimate N-Central Take Control sessions. Event IDs 8192 and 8193 then show the actor abusing the built-in Take Control feature.
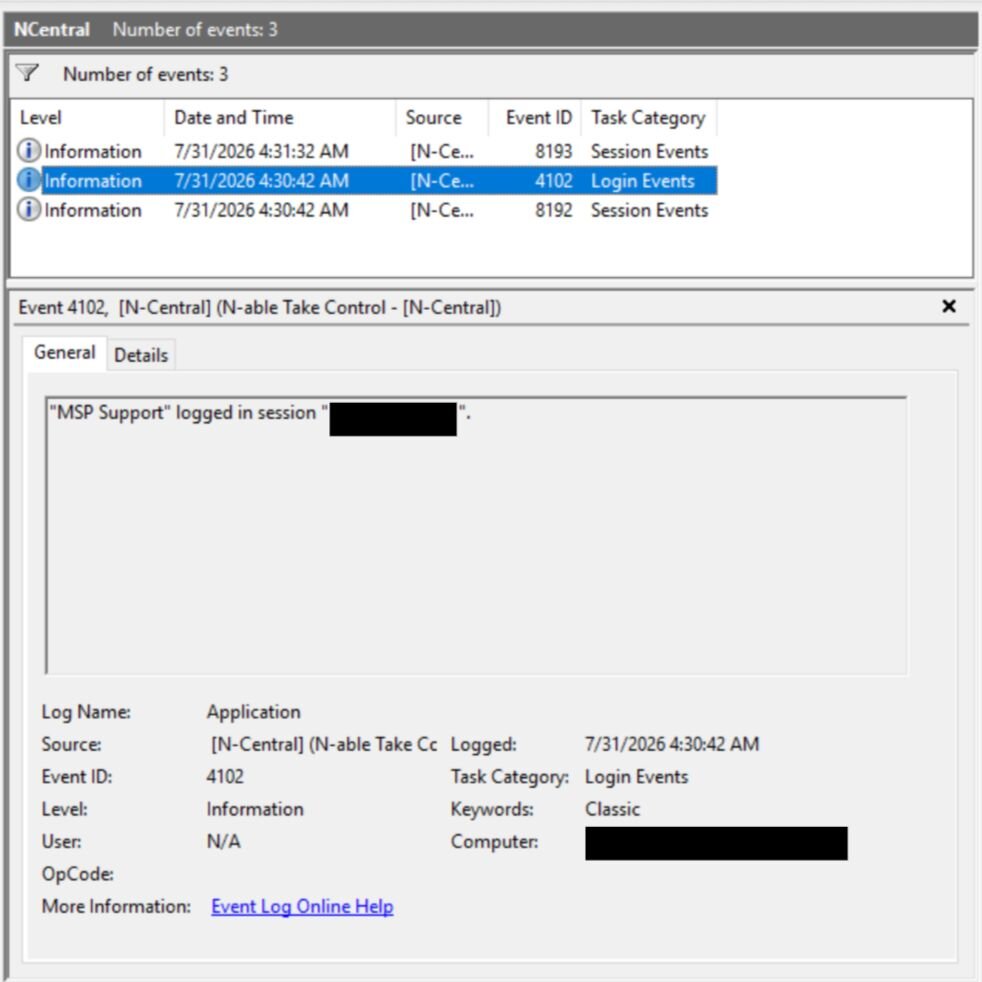
Figure 1b: Windows Event Logs reflecting "MSP Support" account session login
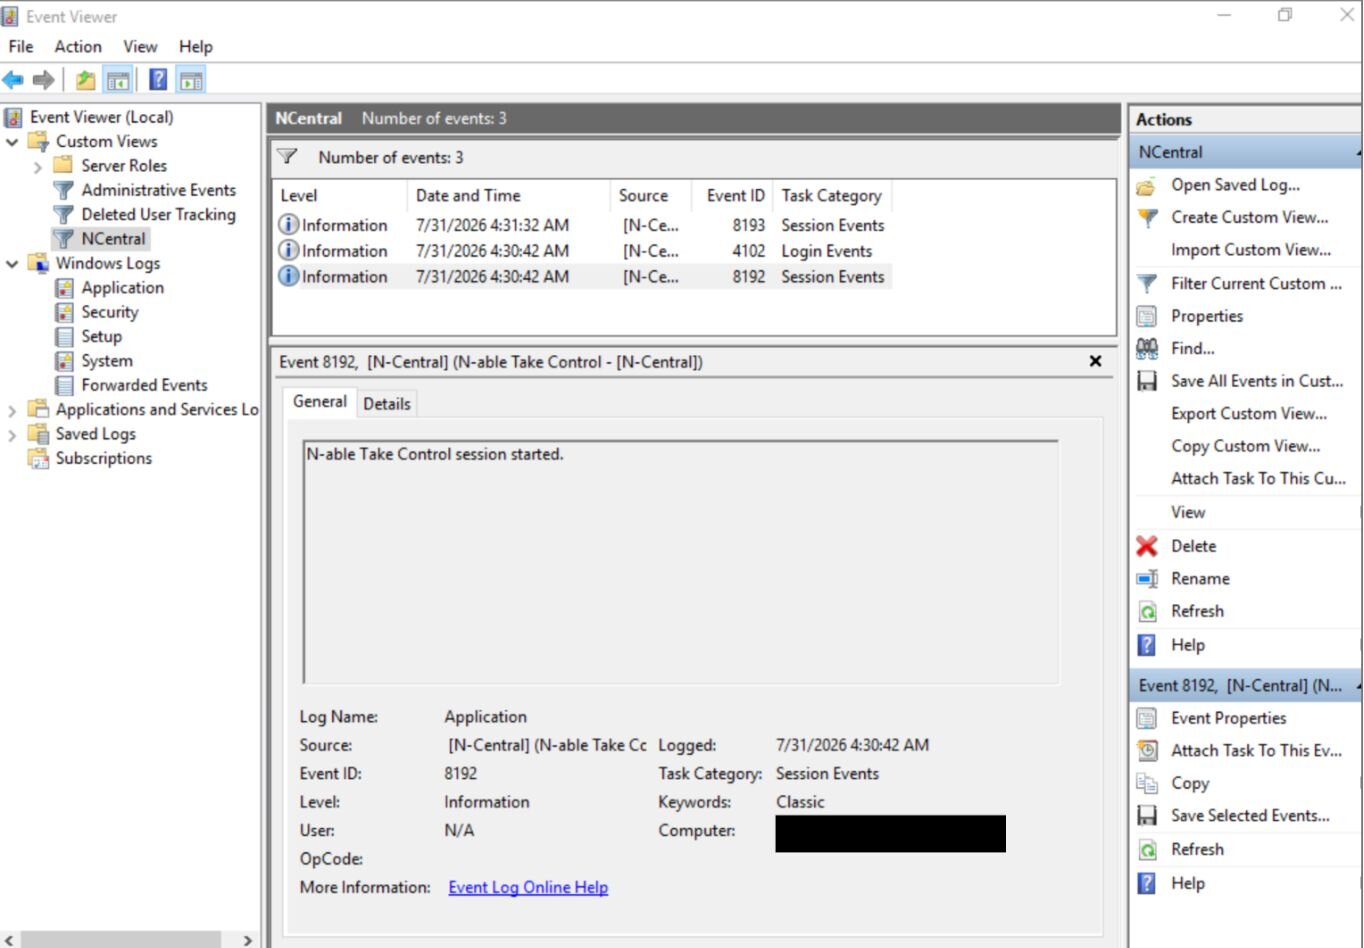
Figure 1c: Windows Event Logs reflecting Take Control session starting
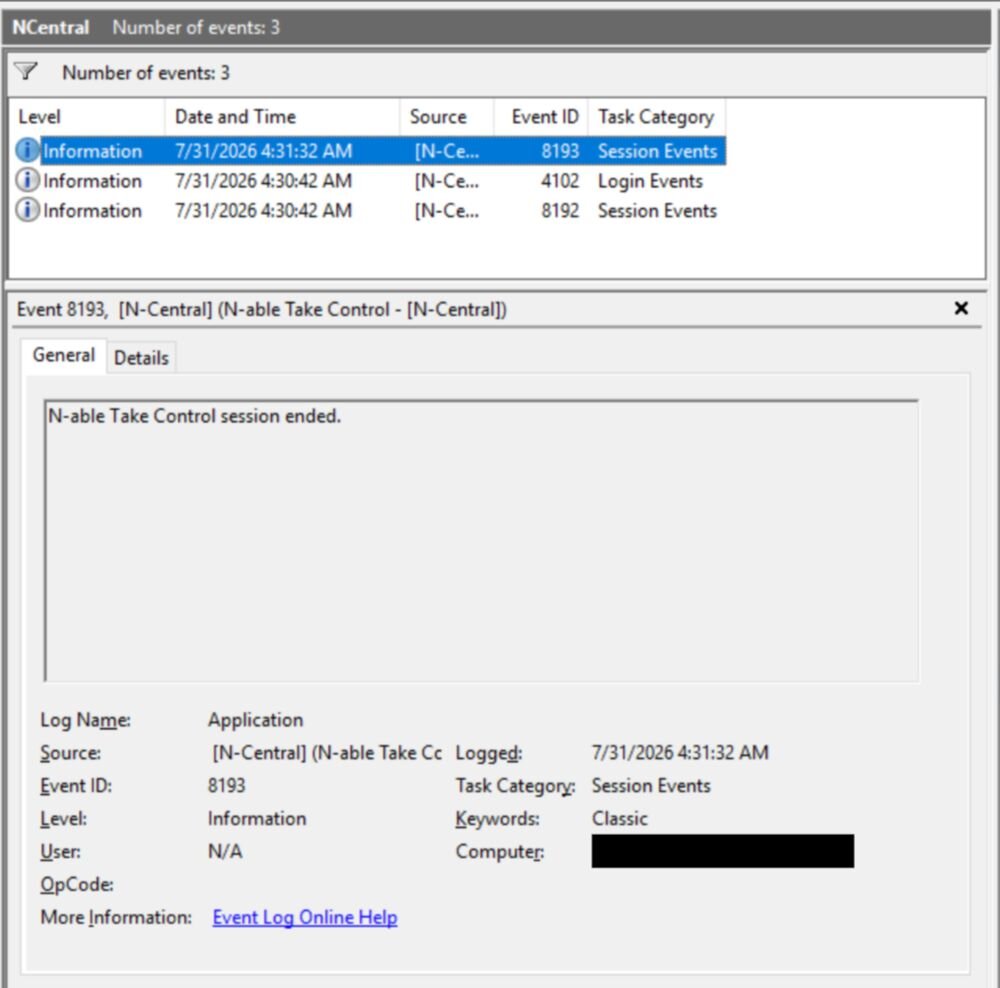
Figure 1d: Windows Event Logs reflecting Take Control session ending
As our recommendations below outline, it is important for organizations to apply the hotfix and review N-central Take Control activity in their environment. In its release notes, N-able has also said to review users' documents folder for files called svchost.exe and look for registered service names called Cloudflared. We have not seen either of these indicators across our telemetry as of this update.
Huntress continues to investigate the activity associated with exploitation of this N-able flaw, and will update our blog accordingly.
Update: 8/3/26 @ 12:45 AM ET
As Huntress continues our investigation and analysis of activity targeting vulnerable N-able N-central environments, we discovered that the four IPs N-able initially flagged as malicious are actually Mullvad or NordVPN VPN exit nodes. Notably, among the original IPs, we have seen substantial traffic with 87.249.138[.]34 directly attributed to NordVPN, as well as substantial traffic with 37.19.210[.]32 directly attributed to Mullvad VPN. 37.19.210[.]32 has been previously abused for bruteforcing, spam, and other nefarious activity prior to this incident.
In parallel, Huntress technology and teammates are rapidly identifying unpatched N-able server instances and contacting at-risk partners and customers about the imminent threat.
Beyond this specific vulnerability, we are seeing many environments where the N-central Server has yet to be updated to the 2026.3.1.7 hotfix needed to prevent exploitation of the vulnerability. At the time of posting this update, more than half (55.6%) of our partners' and customers' reachable cloud servers were still unpatched. That is especially concerning because the N-able server runs a custom distribution of AlmaLinux 9, and does not often have EDR software deployed on it due to running as an appliance.
N-able has since published an additional security update with two more malicious IPs, 37.153.90[.]88 and 92.118.112[.]181, which we have incorporated into our hunting and guidance below.
We will continue to investigate this activity and update this post as we learn more.
Background and Vulnerability Overview
On August 1–2, 2026, N-able disclosed a critical vulnerability in N-central, its flagship remote monitoring and management (RMM) platform used by MSPs to centrally monitor, patch, and remotely access servers and endpoints across all of their customers. N-able published a security update on the N-central vulnerability (which is currently down as of publication of this blog) and corresponding incident entries on their uptime / status page, describing this issue and confirming active exploitation in the wild. On August 2, N-able released a hotfix and urged all customers to upgrade to the 2026.3.1.7 hotfix version immediately.
N-able's initial security advisory linked this critical vulnerability to CVE-2026-18556; while the subsequent hotfix pointed to CVE-2026-18577. The CVE's description for CVE-2026-18577 said: "an incomplete patch for CVE-2026-18556 allows for authentication bypass and account takeover in N-central Versions through 2026.3.1."
Based on N-able's advisory and the logs we and our partners have reviewed so far, we know that remote attackers can gain administrative access to vulnerable N-central servers and then abuse the built-in Take Control feature to pivot into managed endpoints and deploy Cloudflare-based tunnels for persistence. N-able has not yet published full technical root-cause details for this vulnerability, so our understanding is limited to the behavior they have described and what we have observed in affected environments, and may evolve as more information is released.
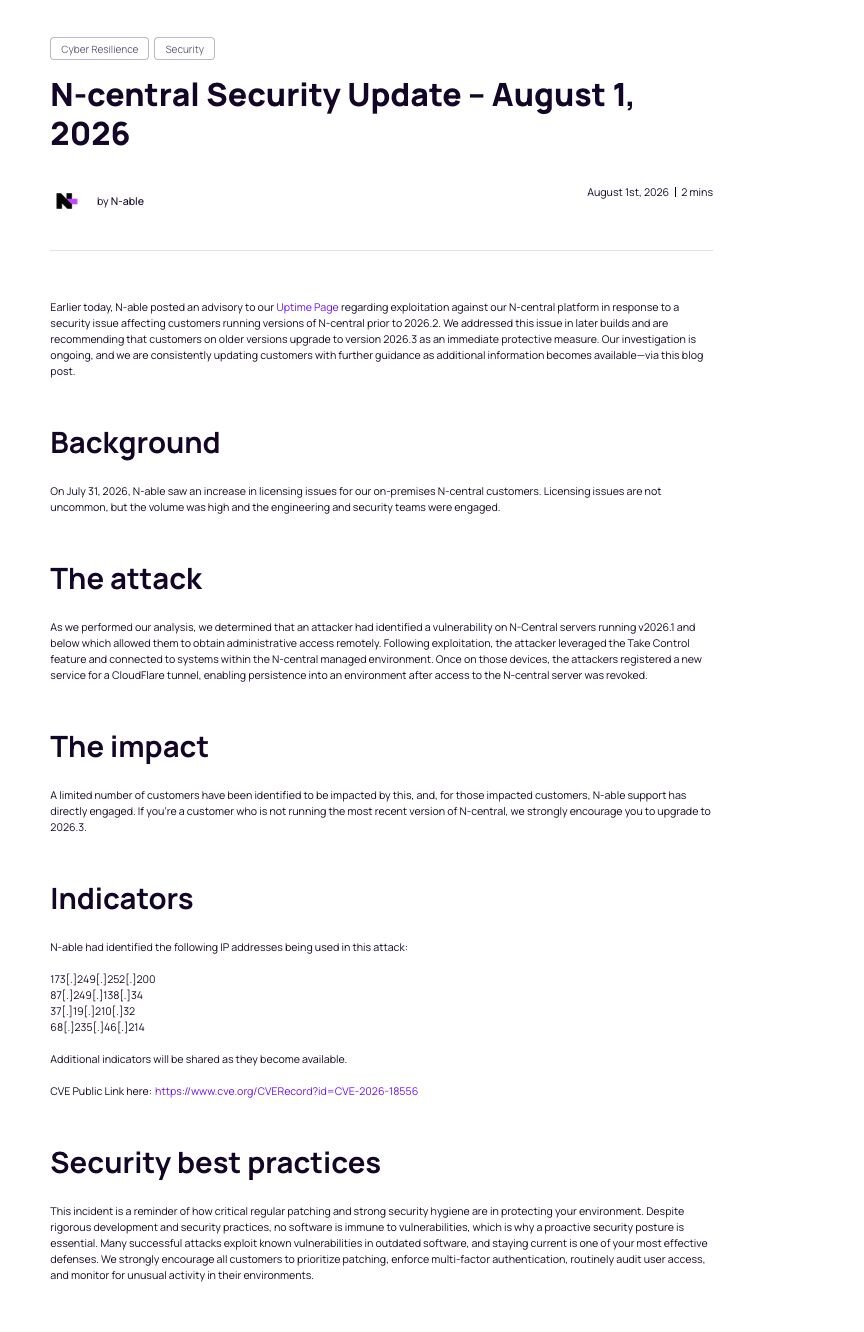
Figure 1: N-able's security advisory
Key points from N-able's communications:
The vulnerability affects all currently supported versions of N-central, including builds that were initially believed to be safe.
N-able has confirmed active exploitation of N-central.
Both cloud‑hosted and on‑premises N-central deployments are impacted.
From an MSP perspective, exploitation of this flaw can grant an attacker full administrative access to an N-central console — the same level of control normally reserved for trusted NOC and engineering staff.
Once inside the console, a threat actor can:
Push new scripts and jobs to many or all managed endpoints.
Deploy and run dual‑use tools (for example, remote tunnels or discovery utilities) via the N-able agent.
Initiate remote‑control sessions into servers and workstations, including domain controllers and other critical systems.
Modify security‑relevant configuration such as roles, accounts, and policies to pave the way for follow‑on activity.
Useful N-able resources to monitor:
Detection Opportunities
Below are concrete places defenders can look today for evidence that this tradecraft has been used against their environments.
1. N‑central UI / Remote-Access Logs
On your N-central servers, review UI and remote-control logs (for example, ui_access_control.log or equivalent in the N-central web application) and:
Filter for sessions where the viewer IP is one of N-able's published IOC IPs (see the Indicators section below).
Pay special attention to viewer accounts that appear to be N-able support identities (for example,
[email protected]).Flag for investigation any sessions that:
Target domain controllers, file servers, or other critical systems.
Occur at unusual times for your team.
Do not line up with a ticket or expected support work.
This combination — a session originating from an IOC IP, associated with a support account, and targeting a high-value host — should be treated as high priority for review.
2. Endpoint Breadcrumbs from N‑central Take Control (Windows)
On N-central–managed Windows hosts, suspicious Take Control activity we have reviewed created log files under:
Directory:
C:\ProgramData\GetSupportService_N-Central\Logs\Example filenames:
BASupSrvc_*.log.gz
What to do with this:
On Windows endpoints managed by N-central, look for:
The directory
C:\ProgramData\GetSupportService_N-Central\Logs\BASupSrvc_*.log.gzfiles, whose creation times align with suspicious N-able sessions
Important caveat: these logs are also created during legitimate Take Control usage, so:
Presence alone is not proof of compromise.
Treat them as a pivot and validate against:
Viewer IP (one of the IOC IPs below).
Viewer identity (support account vs your own technicians).
Target host criticality and time‑of‑day.
Taken together, N-central UI logs, network indicators, and endpoint Take Control logs can help you reconstruct whether this tradecraft has been used against your environment.
3. Network and Server-Side Indicators
We recommend that MSPs:
Search N-central server, firewall, proxy, and WAF logs for traffic involving the IOC IPs and hostnames listed below, particularly where those indicators:
Connect to N-central web consoles or APIs.
Appear as the source of remote-control viewer traffic.
As a short‑term mitigation, consider blocking the IOC IPs at the perimeter of N-central servers, with clear internal messaging that:
This is a temporary, partial control, not a complete fix.
Attackers can and will rotate infrastructure, so blocking the initial IOC set should not create a false sense of security.
Recommendations for N‑central Customers
The following guidance is intended for MSPs and organizations currently using N-able N-central.
1. Patch and Harden Your N‑central Environment
Apply N-able's hotfixes and updates as soon as they are available for your version, following the latest guidance on the N-central security update blog and uptime / status page.
Restrict who and what can reach the N-central console:
Ensure the console is not directly exposed to the public internet—restrict access with firewall/IP rules and/or VPN, and front it with SSO where available.
Enforce multi‑factor authentication (MFA) on all N-central accounts.
Limit inbound access to known IP ranges (for example, office networks, admin VPNs).
2. Review N‑central Logins, Accounts, and Configuration
Focus on changes and events that do not match your normal operational patterns:
Unusual logins
New or unexpected IP ranges or geolocations.
Access at odd hours compared to your team's normal schedule.
Activity from accounts that should no longer exist (departed staff, test accounts).
Account and permission changes
Newly created administrative users.
Sudden promotion of existing accounts to higher‑privilege roles.
Security‑relevant settings being loosened (for example, MFA removed, IP restrictions broadened).
Jobs and automation
New or modified jobs that touch a large number of customers or endpoints at once.
Scripts that you do not recognize, particularly those targeting domain controllers, DC‑adjacent infrastructure, or making broad configuration changes.
3. Evaluate whether temporarily disabling N‑central is appropriate
Turning off N-central is a significant decision, and it should be made based on risk, not panic. On one side, a compromised RMM can be used as a force multiplier against every downstream client you manage; on the other, taking N-central offline means losing central visibility, patching, and remote access when they may be needed most. Our goal is not to tell every N-able customer to shut down their RMM, but to make sure you consciously weigh this option: for higher-risk environments, or where you cannot meaningfully reduce exposure, temporarily disabling N-central until you are able to apply N-able's hotfix may be the safer choice.
4. Review Remote-Control Activity
N-central's remote‑control features are powerful — and attractive to attackers.
Review recent remote‑control / Take Control sessions for:
Connections into domain controllers, file servers, and other high‑value systems.
Viewer IPs that do not line up with your help‑desk or NOC networks.
Sessions launched at unusual times or that do not match expected customer tickets.
If you find sessions you cannot explain, treat them as high‑priority for investigation and cross‑reference them with the IOC list and endpoint breadcrumbs above.
What Huntress Is Doing for Our Customers
Huntress is taking the following actions as this situation unfolds:
Active hunting across telemetry
We are actively hunting in our telemetry for behaviors consistent with N-able's guidance and partner‑shared logs, with a focus on customers running N-central.Prioritization of at‑risk partners
Partners with N-central deployments are being treated as a priority cohort for:Deeper hunting and signal review.
Faster escalation paths when suspicious N-able‑related activity is observed.
Detection refinement
We are tuning relevant detections to better distinguish between:Normal MSP use of N-central (legitimate scripts and support sessions), and
Abnormal, high‑risk RMM abuse patterns.
Incident reporting and communication
As we confirm N-central abuse in specific customer environments, we will publish dedicated incident reports in the Huntress portal and work directly with those partners through our managed response workflows.
For Huntress Customers: Review Managed Response Settings
Because this vulnerability sits in a central piece of your tooling, fast containment and remediation matter.
For Huntress Managed EDR customers, we strongly recommend:
Confirm that Managed Response isolation is enabled wherever possible, so Huntress can quickly contain endpoints if we detect malicious activity.
Ensure active remediation is turned on so our analysts can assist with removing malicious tools or persistence that may have been deployed via N-central.
For step‑by‑step guidance, review our KB: Huntress Managed Response – Automated Remediation of Incident Reports.
If you are unsure of your current settings, work with your internal team or Huntress support to review and update them.
Huntress is fully engaged on this issue: we are hunting for abuse patterns across our telemetry, prioritizing partners where N-central is present, and standing ready to respond. We'll continue to update this post as we learn more and as the community uncovers additional details.
Indicators of Compromise (IOCs)
How to use these IOCs:
Review N-central server access logs, firewall/WAF/proxy logs, and any upstream logging for connections involving these IPs/hostnames.
Treat confirmed interaction between these indicators and N-central servers as high‑priority for investigation, and then:
Pull corresponding N-central UI / remote‑access logs to identify which accounts and endpoints were touched.
Use endpoint Take Control logs (
GetSupportService_N-Central\Logs/BASupTSHelper_*and related files) as pivots to confirm activity on specific hosts.
Item | Description |
|---|---|
| Known malicious IP addresses identified by N-able (shared in August 1 security update). Note: These are all IP addresses known to be associated with either Mullvad VPN or Nord VPN |
| Known malicious IP addresses identified by N-able (shared in August 2 security update) |
| Known malicious IP addresses identified by N-able (shared in August 6 security update). |
| Known malicious domain |
| Intruder IPv4 (Tzulo VPN) |
| Intruder IPv4 (Tzulo VPN) |
| Malicious Cloudflare tunnel account tag |
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.huntress.com/blog/n-able-vulnerability-exploitation