Google plans to give Private AI Compute a memory that follows users across devices
Google plans encrypted, device-keyed server-side memory so Private AI Compute assistants retain context across devices.
Google plans to add persistent, server-side memory to Private AI Compute so Gemini-powered assistants can keep context across sessions and devices. The platform currently processes sensitive data in a hardware-isolated cloud environment and discards context when a task ends. Under the proposed design, assistance data would be stored encrypted, with decryption keys held only on the user's devices, and a secure enclave would temporarily decrypt it over an authenticated end-to-end channel. Google published an updated technical brief, a tamper-proof record of server software, and independent audit results, and says devices can verify the software before sending personal data.
- Private AI Compute has been stateless, erasing context when each task ends.
- Planned memory would sit in storage encrypted with keys held only on user devices.
- A secure enclave decrypts data temporarily, processes the request, then re-encrypts it.
- Google released a technical brief, tamper-proof software record, and audit results.
- Cross-device scenarios are described as future possibilities, not current features.
Full article380 words · extracted from helpnetsecurity.com · click to collapse
Google plans to add private, server-side memory to Private AI Compute, enabling AI assistants to maintain continuity across devices while providing privacy protections normally associated with on-device processing.
Private AI Compute is Google’s cloud platform for processing sensitive data with Gemini models in a hardware-isolated environment. It gives AI features access to greater computing power and is designed to prevent anyone other than the user, including Google, from accessing the data being processed.
Until now, the platform has been stateless, erasing all context when a task ends. Google says workarounds such as maintaining lists of personal facts and preferences do not provide the context required for continuous assistance. The new system will allow cloud-based AI to retain context across sessions and devices.
“With this new technical capability, a new persistent memory layer will be able to function like a secure digital vault in the cloud,” the Google Private AI Compute team said.
Securing AI memory
Information needed to provide assistance will be stored in dedicated, encrypted storage. The cryptographic keys required to unlock it will be held exclusively on users’ devices, which Google says will make the data inaccessible to anyone else, including the company itself.
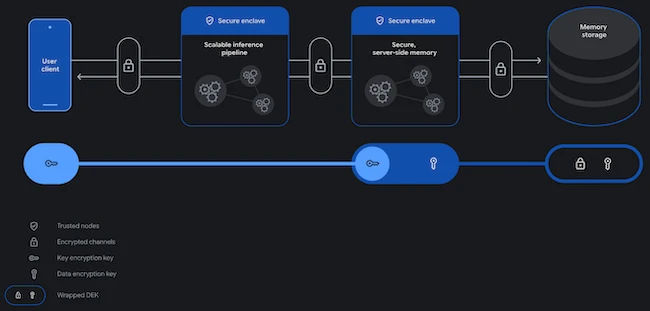
By combining hardware-enforced secure enclaves, encrypted channels, and per-user databases shielded by device-derived encryption keys, this architecture ensures your data stays fully private and under your control. (Source: Google)
When an AI model needs the information, an authenticated, end-to-end encrypted channel will connect the user’s device to a secure cloud enclave. The enclave will temporarily decrypt the data in isolated memory, process the request, save any new context and encrypt the information again.
Transparency and oversight
Google says the technology could eventually let users pull up assembly instructions on a laptop after viewing them through smart glasses or resume conversations across mobile and web platforms. The company presents these scenarios as examples of the architecture’s potential, not as currently available product features.
Google has published an updated technical brief, a tamper-proof public record of its server software and results from an independent audit. Devices using Private AI Compute will be able to verify that the software is authentic and unaltered before sending personal data.
The company has invited the privacy community to review the platform’s architecture, protections, security proofs and verification protocols.