HBO Max’s verified Reddit account hijacked to spread malware
Cybercriminals hijacked HBO Max's verified Reddit account to run 108 ClickFix ads pushing AMOS and Amatera infostealers via fake HBO app sites.
Hudson Rock found that hijackers used HBO Max's verified Reddit account to run 108 malicious ads over roughly 48 hours promoting fake AI tools and macOS utilities. The ads led to HBO lookalike sites instructing victims to paste commands into Terminal or PowerShell, a ClickFix social-engineering technique ADAMnetworks dubbed PasteSwitch. macOS payloads included MacSync and AMOS infostealers targeting browser credentials, Telegram data, Apple Notes, passwords, and crypto recovery phrases; Windows users received the in-memory Amatera infostealer. The operation is also linked to cryptocurrency clipboard hijackers, and Reddit admins paused the ads and opened an investigation.
- 108 malicious ads run from verified HBO Max Reddit account in 48 hours
- ClickFix lures trick users into pasting commands into Terminal or PowerShell
- AMOS/MacSync steal credentials, Telegram data, and crypto seed phrases on macOS
- PasteSwitch infrastructure tailors payload per device; linked to clipboard hijackers
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | ember-bridge.com | lution with a web protection component. Malwarebytes blocks ember-bridge.com, which is part of the PasteSwitch infrastructure. Educate y |
Full article623 words · extracted from malwarebytes.com · click to collapse
Researchers at Hudson Rock found that cybercriminals hijacked HBO Max’s verified Reddit account and used it to run 108 malicious ads over roughly 48 hours.
The ads used HBO Max’s trusted corporate account to promote fake AI tools, developer software, and macOS utilities, lowering potential victims’ guards.
Some ads directed users to convincing HBO lookalike sites that claimed to offer a native HBO Max app for macOS or a promotional download. But instead of providing an installer, the sites instructed visitors to open Terminal on their Mac or, on Windows, the Run dialog or PowerShell, and paste in a command.
This is the hallmark of a growing social engineering technique known as ClickFix.
ClickFix attacks disguise malicious instructions as a routine technical step, such as fixing an error, completing a CAPTCHA, verifying that you are human, or installing software. A web page may silently copy a command to the clipboard, then guide the victim through pasting and running it, by which they will infect their own device.
Researchers at ADAMnetworks have dubbed the operation behind the HBO Max ads “PasteSwitch.” Its infrastructure appears to tailor the next stage to the visitor’s device and the lure being used.
Observed macOS payloads included MacSync and AMOS infostealers designed to steal browser credentials and profiles, Telegram data, Apple Notes, saved passwords, and cryptocurrency wallet recovery phrases.
Windows users could end up with the Amatera infostealer, which runs in memory. The operation has also been linked to cryptocurrency clipboard hijackers, which monitor copied wallet addresses and replace them with an attacker-controlled address before a transaction is sent.
How to stay safe
Reddit admins paused the ads and opened a security investigation after reports came in, but it is important to remain vigilant. Reportedly, ClickFix was responsible for more than half of all malware loader activity in 2025.
One reason for its success is that campaigns continue to add new methods for tricking users and different commands for avoiding detection.
Users of macOS Tahoe 26.4 or later may be warned when pasting text into Terminal, but it doesn’t appear for everyone, so you shouldn’t rely on that alone.
Malwarebytes can provide additional protection at several stages of a ClickFix attack. Browser Guard warns when a website tries to copy something to your clipboard, web protection blocks known malicious sites, and real-time protection can detect malware delivered by the campaign.
With ClickFix running rampant and inventing new methods all the time, it’s important to be aware, careful, and protected:
- Treat ads with caution. A verified account does not guarantee that an ad is safe. Visit the company’s official website directly instead of downloading software through an advertisement.
- Slow down. Don’t rush to follow instructions on a webpage or prompt, especially if it asks you to run commands on your device or copy-paste code. Attackers may use countdowns, user counters, or other pressure tactics to make you act quickly.
- Don’t run commands from untrusted sources. Never run code or commands copied from websites, emails, ads, or messages unless you trust the source and understand what the command does. Check the instructions against official documentation or contact the company’s support team.
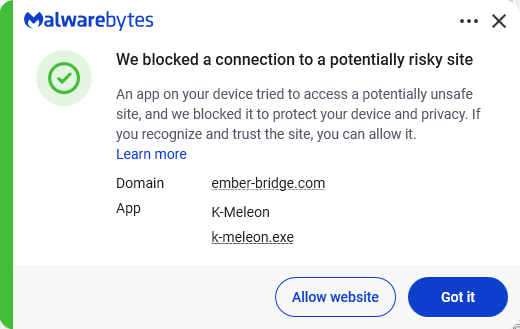
- Secure your devices. Use an up-to-date, real-time anti-malware solution with a web protection component. Malwarebytes blocks ember-bridge.com, which is part of the PasteSwitch infrastructure.
- Educate yourself on evolving attack techniques. Understanding that attacks may come from unexpected vectors and evolve helps maintain vigilance. Keep reading our blog!
From reporting threats to removing them.
Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.
About the author
Was a Microsoft MVP in consumer security for 12 years running. Can speak four languages. Smells of rich mahogany and leather-bound books.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.malwarebytes.com/blog/news/2026/09/hbo-maxs-verified-reddit-account-hijacked-to-spread-malware