HBO Max Reddit account compromised to serve ClickFix attacks
Attackers hijacked HBO Max's verified Reddit account to run 108 ClickFix malvertising ads delivering infostealers, loaders, and crypto clippers to Windows and macOS users.
Attackers compromised the verified HBO Max Reddit account (u/hbomax) to push 108 malicious ads in a 48-hour malvertising blitz named PasteSwitch, analyzed by Hudson Rock and ADAMnetworks. The ClickFix lures directed victims to fake landing pages instructing them to paste commands into Terminal, delivering OS-targeted infostealers, malware loaders, and cryptocurrency clippers. Lures included 46 HBO Max ads, 36 fake OpenAI Codex ads, 15 fake macOS disk utilities, and 11 developer-tool ads. The AnimateClipper and ZigClipper payloads use Binance Smart Chain contracts as resilient C2 fallback, with 36 mainnet changes observed between March and July 2026; Reddit paused the ads three days after discovery and is investigating.
- HBO Max's verified Reddit account pushed 108 malicious ClickFix ads within 48 hours
- PasteSwitch campaign served OS-targeted infostealers, loaders, and crypto clippers
- AnimateClipper and ZigClipper use Binance Smart Chain contracts for resilient C2 rotation
- Lures included fake OpenAI Codex and macOS disk-utility apps across 108 ads
- Reddit paused the ads three days after a user reported them on September 6
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | clean-disk-guide.com | Of the rest: 15 purported to be a macOS disk utility (apple.clean-disk-guide[.]com) and 11 used other developer tools as lures (code-desktop |
| domain | code-desktop.com | sk-guide[.]com) and 11 used other developer tools as lures (code-desktop[.]com). “The campaign proves once again why trusted distributio |
| domain | codex-craft.com | trick prospective victims via an OpenAI Codex theme (with a codex-craft[.]com) landing page. Of the rest: 15 purported to be a macOS di |
| domain | hbomax-macos.com | Max lure, directing app seekers to either hbomaxx[.]app or hbomax-macos[.]com. Another 36 tried to trick prospective victims via an Ope |
| domain | hbomaxx.app | s, 46 used an HBO Max lure, directing app seekers to either hbomaxx[.]app or hbomax-macos[.]com. Another 36 tried to trick prospect |
| domain | hbomaxx.us | n be taken to a “somewhat-legitimate” looking landing page (hbomaxx[.]us) that includes a join/download button. REG AD Clicking th |
Full article566 words · extracted from theregister.com · click to collapse
cyber-crime
Part of a 'massive 48-hour malvertising blitz' targeting macOS and Windows machines with malware
Someone compromised the official HBO Max Reddit account and used it to push more than 100 malicious ads serving up ClickFix attacks targeting both Windows and macOS devices with information-stealing malware.
A Reddit user uncovered the infostealer ads on September 6, noting that the ad showed u/hbomax as the author — this is the verified HBO Max account — and advertised a macOS app for HBO Max. The streaming service does not offer a native client for the Mac.
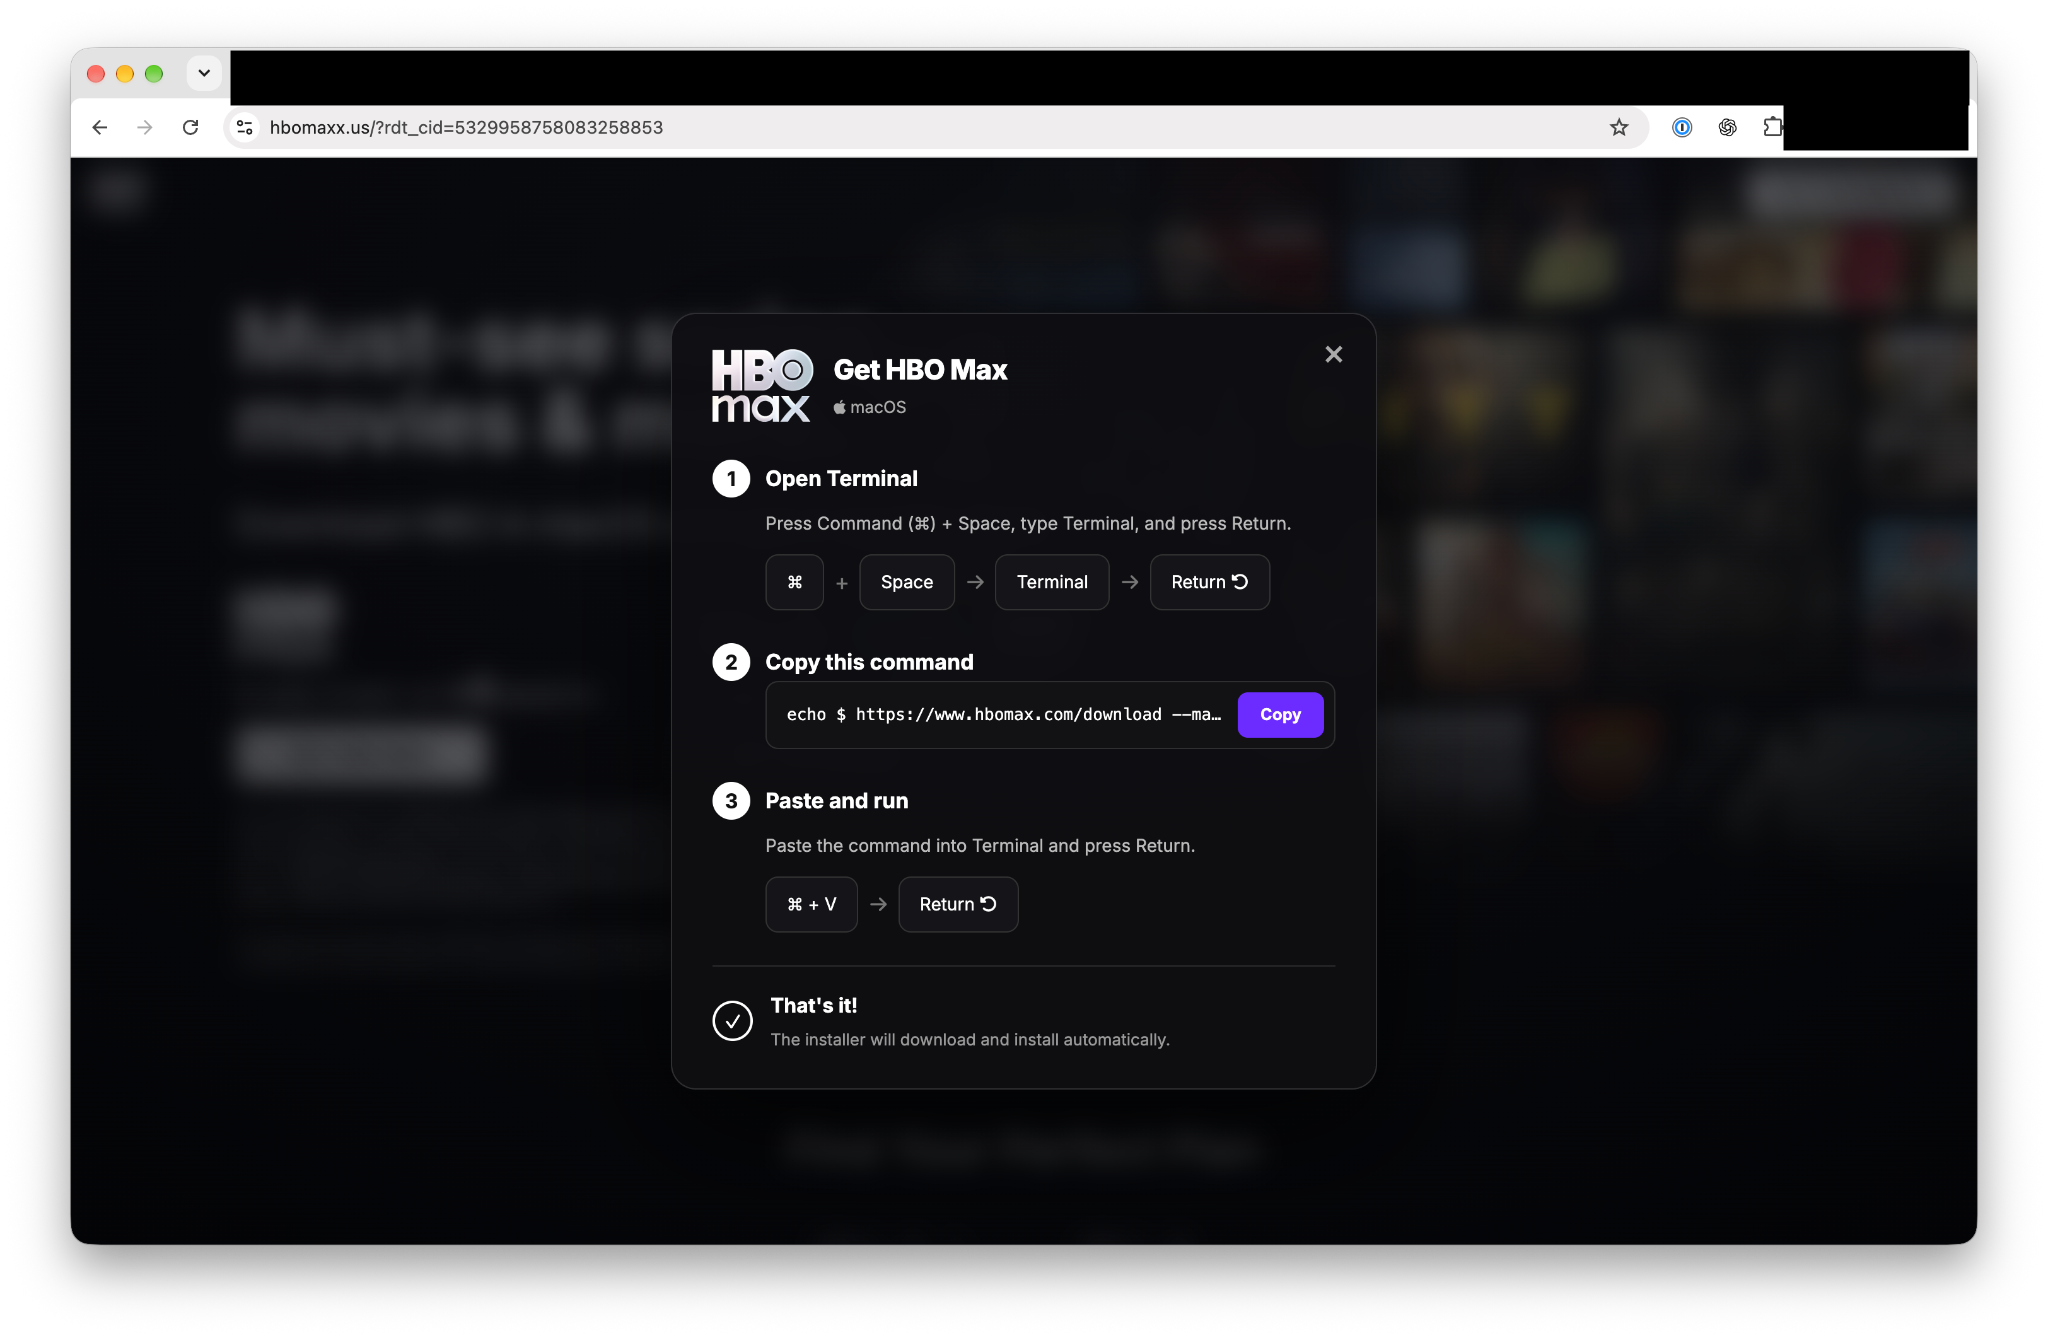
Anyone who clicked on the malicious ad would then be taken to a “somewhat-legitimate” looking landing page (hbomaxx[.]us) that includes a join/download button.
REG AD
Clicking the button produced instructions telling the user to copy and paste a command into Terminal on macOS.
REG AD
The Reddit security sleuth described that as “the classic infostealer/clickfix paste this command to download,” noting that they tested all of this in a sandboxed environment, and didn’t actually run the executable on their machine. “My guess is that the Reddit account is compromised,” they concluded.
Three days later, Reddit paused the infostealer-dropping ads, and an admin said the social media platform’s safety and security teams were investigating what happened.
HBO Max’s parent company Warner Bros. Discovery didn’t immediately respond to The Register’s inquiries about the account takeover - including who hijacked the streaming service’s Reddit account and how they did it. Maybe someone who didn’t like the House of the Dragon season 3 finale? We will update this story if and when we hear back.
Researchers at Hudson Rock and ADAMnetworks analyzed the ads, and in a couple of reports said the HBO Max account hijacking was part of a “massive 48-hour malvertising blitz” that pushed 108 distinct ads using multiple software lures.
They named the campaign PasteSwitch, and said it serves up targeted malware aimed at victims’ operating system - either macOS or Windows. The payloads include infostealers, malware loaders, cryptocurrency clippers, and fake cryptocurrency wallet applications.
The cryptocurrency clippers - PasteSwitch delivers either AnimateClipper or ZigClipper - also provide blockchain-based command-and-control fallbacks for the attackers. They use Binance Smart Chain (BSC) contracts to dynamically fetch whatever C2 domain the crooks are using at any given time.
“Between March and July 2026, researchers observed 36 mainnet changes executed by the same attacker controller address,” Hudson Rock said. “Because the C2 domain is hosted directly on the blockchain, the infrastructure demonstrates dynamic resilience, allowing the threat actors to easily rotate burned domains.”
In addition to HBO Max, the attackers used developer-tool, disk-cleaner, and AI-themed lures, including fake OpenAI Codex ads, which crims have previously used to push Mac malware.
REG AD
Of the 108 ads, 46 used an HBO Max lure, directing app seekers to either hbomaxx[.]app or hbomax-macos[.]com. Another 36 tried to trick prospective victims via an OpenAI Codex theme (with a codex-craft[.]com) landing page. Of the rest: 15 purported to be a macOS disk utility (apple.clean-disk-guide[.]com) and 11 used other developer tools as lures (code-desktop[.]com).
“The campaign proves once again why trusted distribution channels are becoming prime targets for infostealer delivery,” Hudson Rock co-founder and CTO Alon Gal said in a LinkedIn post.
It also shows that miscreants continue to make heavy use of ClickFix attacks, so there’s little sign this social engineering method is going away anytime soon.®
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.theregister.com/cyber-crime/2026/09/14/hbo-max-reddit-account-compromised-to-serve-clickfix-attacks/5296408