Attackers hijack HBO Max’s Reddit account for 48-hour malvertising blitz
Attackers hijacked HBO Max's verified Reddit account to push 108 ClickFix infostealer ads delivering AMOS, MacSync, and crypto clippers.
Threat actors compromised the verified u/hbomax Reddit account and ran 108 ClickFix malvertising ads in 48 hours as part of the PasteSwitch operation, analyzed by Hudson Rock and ADAMnetworks. macOS victims received curl-to-zsh payloads (MacSync, AMOS Helper, fake Ledger/Trezor/Exodus wallets harvesting BIP39 seed phrases); Windows users got Amatera via mshta and PowerShell loaders. Clipper C2 addresses are stored in Binance Smart Chain smart contracts, with 36 mainnet changes observed between March and July 2026.
- Compromised verified HBO Max Reddit account pushed 108 ClickFix ads in 48 hours
- Cross-platform operation spans MacSync, AMOS, Amatera, fake wallets, and crypto clippers
- Wallet apps harvest 12/24-word BIP39 recovery phrases for direct crypto theft
- C2 hosted on Binance Smart Chain contracts, rotating 36 times March-July 2026
- Reddit has paused the ads and secured the account
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | clean-disk-guide.com | oke down into 15 ads for a fake macOS disk utility at apple.clean-disk-guide[.]com and 11 for other developer tools at code-desktop[.]com. O |
| domain | code-desktop.com | .clean-disk-guide[.]com and 11 for other developer tools at code-desktop[.]com. One entry point into a larger system The HBO Max ads wer |
| domain | codex-craft.com | -macos[.]com. Another 36 posed as OpenAI Codex, pointing to codex-craft[.]com. The rest broke down into 15 ads for a fake macOS disk ut |
| domain | hbomax-macos.com | s, 46 used an HBO Max lure, split between hbomaxx[.]app and hbomax-macos[.]com. Another 36 posed as OpenAI Codex, pointing to codex-craf |
| domain | hbomaxx.app | id . Of the 108 ads, 46 used an HBO Max lure, split between hbomaxx[.]app and hbomax-macos[.]com. Another 36 posed as OpenAI Codex, |
| domain | hbomaxx.us | HBO Max subreddits,” wrote the user. Clicking the ad led to hbomaxx[.]us, “which looks somewhat legitimate, and has a join button |
Full article724 words · extracted from helpnetsecurity.com · click to collapse
Attackers compromised the verified official HBO Max Reddit account, u/hbomax, and used its trusted advertising status to launch a ClickFix campaign targeting macOS and Windows devices with information-stealing malware.
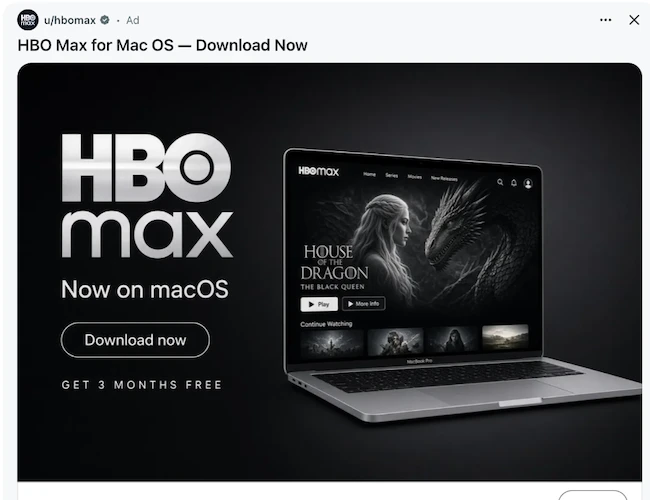
Screenshot of the fraudulent ad (Source: Alex Cutts)
ClickFix has been rising in popularity among cybercriminals. It’s a social engineering technique that cons victims into running malicious commands on their own machine, usually by pretending the commands are needed to fix a problem or perform routine upkeep.
A Reddit user spots the fake ad
Security researchers at Hudson Rock and ADAMnetworks analyzed the campaign after a Reddit user reported the infostealer ads on September 6.
“I was browsing Reddit and saw an ad displaying u/hbomax as the author – this advertised a macOS HBO Max app which I’d not heard of and was interested in. The user is verified and appears to have posted many times in the official HBO Max subreddits,” wrote the user.
Clicking the ad led to hbomaxx[.]us, “which looks somewhat legitimate, and has a join button / download.” According to the user, “clicking these opens up the classic infostealer/clickfix paste this command to download.” They added: “Having checked, this downloads an executable with other capabilities for account compromise,” done in a sandbox, “inspecting the output only, not running anything.”
“My guess is that the reddit account is compromised,” warned the user.
108 ads in 48 hours
Over a 48-hour period, the compromised account pushed 108 distinct ClickFix ads to Reddit users, part of a large operation researchers named PasteSwitch.
“The threat actors squeezed as much value as possible out of the verified account’s status, pivoting quickly when domains were burned,” Hudson Rock said.
Of the 108 ads, 46 used an HBO Max lure, split between hbomaxx[.]app and hbomax-macos[.]com. Another 36 posed as OpenAI Codex, pointing to codex-craft[.]com. The rest broke down into 15 ads for a fake macOS disk utility at apple.clean-disk-guide[.]com and 11 for other developer tools at code-desktop[.]com.
One entry point into a larger system
The HBO Max ads were one entry point into that operation. The same delivery system had already turned up behind fake Claude, Codex, Alfred, Homebrew, GitHub, utility, and wallet applications.
ADAMnetworks described following the copied command into “a cross-platform delivery operation spanning MacSync, AMOS, Amatera, fake wallet apps, and contract-controlled cryptocurrency clippers.”
Visitors were checked before anything malicious was shown to them. Depending on browser, screen, and device signals, some got the lure and a malicious command. Others saw a blank page, a redirect to a legitimate vendor site, or unrelated content, which kept automated scans from catching the pattern consistently.
Different malware for macOS and Windows
On macOS, PasteSwitch relied on commands that pipe curl output into zsh, running attacker code without a separate download step. Researchers identified three main payloads.
MacSync used transaction tokens to track infected machines and moved stolen data out in chunks to avoid detection. It collected browser credentials, Gecko profiles, Telegram data, Apple Notes, and macOS passwords, staging everything in a hidden zip file before exfiltration.
AMOS Helper installed itself as a persistent background process disguised as a macOS system service, then checked in with attacker infrastructure for ongoing tasks.
Fake wallet apps mimicking Ledger, Trezor Suite, and Exodus were built to collect 12- and 24-word BIP39 recovery phrases, giving attackers direct access to victims’ cryptocurrency.
Windows visitors went through a separate chain using mshta and PowerShell, ending with a loader that ran in memory and installed Amatera, malware that fingerprints the host, takes screenshots, and decrypts stored browser credentials.
Blockchain-hosted command and control
The clipper malware in the operation, AnimateClipper and ZigClipper, replaces a victim’s copied cryptocurrency wallet address with one owned by the attacker. Instead of a fixed command-and-control domain, the operators stored that address inside smart contracts on the Binance Smart Chain, letting them rotate infrastructure by updating the contract instead of registering new domains.
“Between March and July 2026, researchers observed 36 mainnet changes executed by the same attacker controller address. Because the C2 domain is hosted directly on the blockchain, the infrastructure demonstrates dynamic resilience, allowing the threat actors to easily rotate burned domains,” Hudson Rock added.
Reddit has since paused the ads and secured the account, “but the campaign proves once again why trusted distribution channels are becoming prime targets for infostealer delivery,” Alon Gal, Hudson Rock CTO, wrote on LinkedIn.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.helpnetsecurity.com/2026/09/15/hbo-max-reddit-account-clickfix-infostealer-malware/