F5 patches BIG-IP APM zero-day flaw exploited in RCE attacks
F5 patched actively exploited BIG-IP APM zero-day CVE-2026-94127 enabling remote code execution; CISA added it to KEV with a federal patch deadline.
F5 released updates for critical BIG-IP APM zero-day CVE-2026-94127, which is exploited in remote code execution attacks against instances configured as an OAuth Authorization Server. CISA added the flaw to its Known Exploited Vulnerabilities catalog and ordered federal agencies to patch by Friday. Shadowserver tracks over 14,700 internet-exposed BIG-IP APM IPs, and admins unable to patch immediately can apply an F5-provided iRule mitigation. F5 advises checking for multiple OAuth authentication failures followed by suspicious commands and a TMM SIGABRT as indicators of compromise.
- Zero-day CVE-2026-94127 exploited in RCE attacks on BIG-IP APM OAuth Authorization Server setups
- CISA added the flaw to KEV and set a federal patch deadline for Friday
- Over 14,700 BIG-IP APM instances exposed online per Shadowserver
- Mitigation iRule available for admins who cannot patch immediately
Vulnerabilities mentionedAll →
- CVE-2026-941279.32%Unauthenticated Heap-Overflow RCE in F5 BIG-IP APM with OAuth Profilepublished · F5 BIG-IP (Access Policy Manager) KEV PoC ×2
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
Full article454 words · extracted from bleepingcomputer.com · click to collapse
F5 has released security updates to address a critical BIG-IP APM zero-day vulnerability being exploited in remote code execution attacks.
BIG-IP APM (short for Access Policy Manager) is the company's centralized access management proxy solution that helps admins secure access to their organizations' networks, applications, cloud, and application programming interfaces (APIs).
Tracked as CVE-2026-94127, the flaw affects instances configured as an OAuth Authorization Server when a BIG-IP APM access policy and an OAuth profile are configured on a virtual server.
"We have learned that this vulnerability has been exploited," F5 warned in a security advisory published on Tuesday. "Deployments using APM strictly as an OAuth Client / Resource Server (without OAuth authorization server profiles configured) are not affected by this vulnerability."
The company advised customers to review systems for indicators of compromise if they detect a combination of multiple OAuth authentication failures and suspicious commands, shortly followed by a TMM SIGABRT.
F5 also shared mitigation measures for admins who can't immediately install the security updates, which require applying an iRule (available from F5 Support) to the affected BIG-IP APM virtual server.
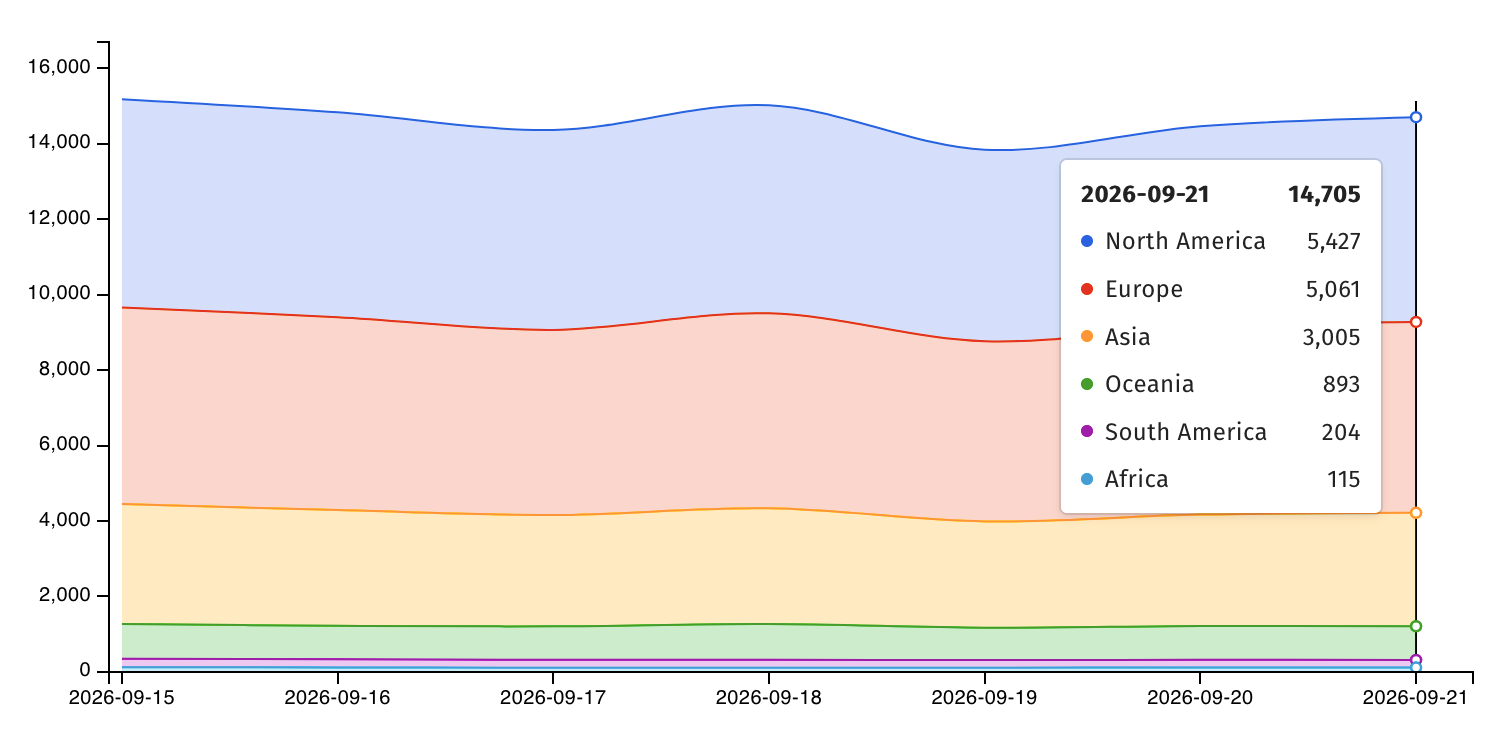
Internet threat monitoring non-profit Shadowserver currently tracks over 14,700 IP addresses with BIG-IP APM fingerprints. However, there is no information on how many have already been patched or are honeypots.
On Tuesday, the Cybersecurity and Infrastructure Security Agency (CISA) also added CVE-2026-94127 to its Known Exploited Vulnerabilities (KEV) Catalog and ordered U.S. federal agencies to secure their networks against this flaw by Friday.
"These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the federal enterprise," the cybersecurity agency warned.
Cybercrime and state-backed threat groups have often exploited F5 vulnerabilities in recent years. For instance, attackers have targeted security flaws in F5 products to breach corporate networks, hijack devices, map internal servers, deploy data-wiping malware, and steal sensitive documents.
F5 also disclosed in October 2025 that state-sponsored hackers breached its systems in August 2025 and stole undisclosed BIG-IP security source code and vulnerabilities.
Since November 2021, CISA has flagged eight actively exploited F5 vulnerabilities, four of which have also been abused in ransomware attacks.
F5 is a Fortune 500 company that provides cybersecurity, application delivery networking (ADN), and other services to more than 23,000 customers worldwide, including 48 of the Fortune 50 companies and 80% of the Fortune Global 500.
Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.